Azure AD vs Active Directory (Entra ID): Key Differences Explained

- Level
- Intermediate
- Reading time
- 12 min
- Concept
- Active Directory vs Microsoft Entra ID
- Last reviewed
- July 18, 2026
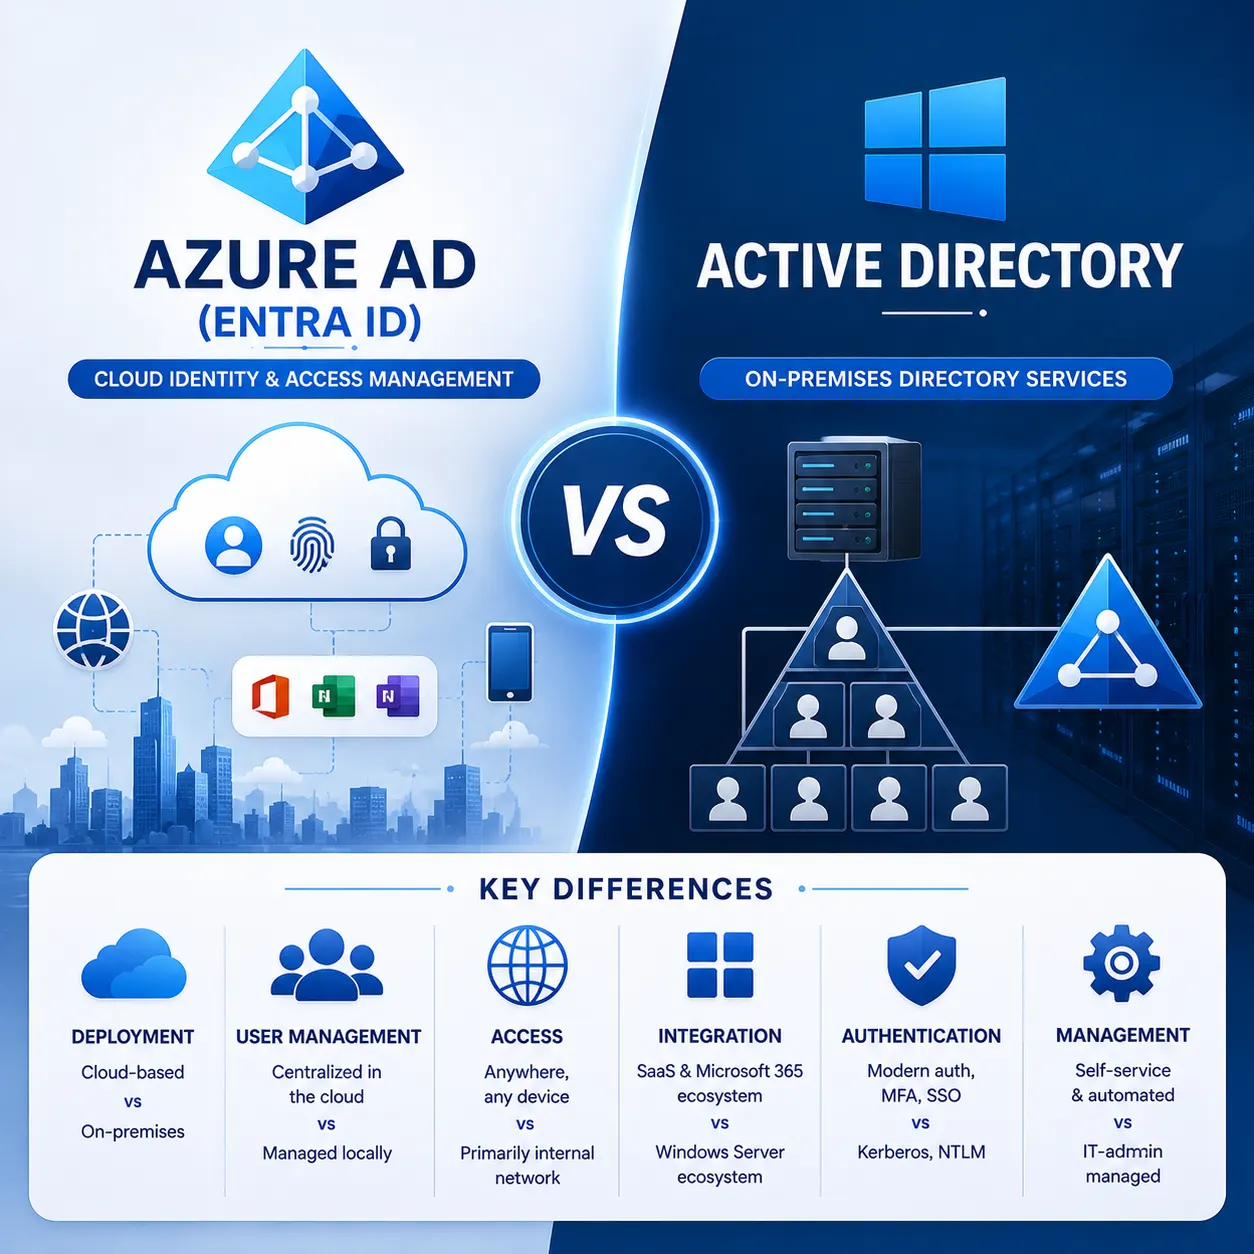
Table of contents
Active Directory Domain Services (AD DS) and Microsoft Entra ID (formerly Azure AD) both manage identity, but they were designed for different trust models. AD DS controls resources inside a corporate network perimeter. Entra ID controls access to cloud applications in a world where the network itself isn't trusted. Understanding this distinction prevents the most common architectural mistakes in hybrid environments.
Key takeaways
- AD DS secures infrastructure inside a trusted network. Entra ID secures access to applications in a zero-trust model.
- AD DS uses Kerberos/NTLM and LDAP. Entra ID uses OAuth 2.0, SAML, and OpenID Connect.
- Entra ID is not "Active Directory in the cloud." It's a fundamentally different identity platform.
- Most enterprises use both together in hybrid environments synced via Entra Connect.
- Azure AD was renamed to Microsoft Entra ID in July 2023. The product didn't change, only the branding.
Quick explanation
In simple terms
Active Directory manages users and devices inside your corporate network. Microsoft Entra ID manages identity and access to cloud applications like Microsoft 365 and Azure.
Technical definition
AD DS is an on-premises directory service using LDAP, Kerberos, and NTLM for authentication within a Windows domain trust boundary. Microsoft Entra ID is a cloud-native Identity-as-a-Service (IDaaS) platform using OAuth 2.0, SAML 2.0, and OpenID Connect for application-level authentication with policy-based Conditional Access.
Analogy
AD DS is like a building security desk that checks badges and grants access to floors and rooms inside the building. Entra ID is like a cloud-based access system that verifies your identity from anywhere and decides whether to unlock specific applications based on who you are, where you are, and what device you're using.
Definition
Active Directory Domain Services (AD DS) is an on-premises directory service for Windows domain networks. Microsoft Entra ID (formerly Azure AD) is a cloud-based identity platform for cloud and SaaS application access. They serve different trust models and often work together in hybrid deployments.
Active Directory Domain Services (AD DS) is Microsoft's on-premises directory service, released in 2000, that manages users, computers, groups, and policies within a Windows domain. It authenticates using Kerberos and NTLM protocols and organizes objects in a hierarchical structure of forests, domains, and organizational units (OUs). Group Policy Objects (GPOs) enforce configuration across domain-joined devices.
Microsoft Entra ID (formerly Azure Active Directory) is a cloud-native identity and access management platform launched in 2010. It authenticates using modern protocols: OAuth 2.0, SAML 2.0, and OpenID Connect. Instead of OUs and GPOs, it uses flat tenant structures, Conditional Access policies, and application registrations. Entra ID serves as the identity provider for Microsoft 365, Azure, and thousands of third-party SaaS applications.
The name changed from Azure AD to Microsoft Entra ID in July 2023, per Microsoft's official announcement. The product remained the same; the rebrand aligned it with the broader Entra identity product family.
Why it matters
Core concepts
Different Trust Models
AD DS assumes everything inside the network perimeter is trusted. Entra ID assumes nothing is trusted and evaluates every access request.
Active Directory was designed when corporate networks had clear boundaries: a firewall separated "inside" from "outside," and domain-joined devices were implicitly trusted. Entra ID was built for a world where users work from anywhere, on any device, accessing SaaS apps that live outside any corporate perimeter. This is why AD DS uses network-based trust (domain membership) while Entra ID uses policy-based trust (Conditional Access evaluating identity, device, location, and risk).
Example
A domain-joined laptop on the corporate LAN gets a Kerberos ticket automatically. An Entra ID user signing in from a coffee shop is evaluated by Conditional Access before getting an OAuth token.
Why it matters — Choosing the wrong trust model for your environment creates security gaps that attackers exploit.
Authentication Protocols
AD DS uses Kerberos and NTLM. Entra ID uses OAuth 2.0, SAML 2.0, and OpenID Connect.
Kerberos and NTLM were designed for internal network authentication between domain-joined devices and on-premises resources. They don't work natively across the internet. OAuth 2.0, SAML 2.0, and OpenID Connect were designed for web-based and API-based authentication, making them the standard for cloud and SaaS applications. Per Microsoft's documentation, Entra ID doesn't support LDAP queries or Kerberos authentication directly, which is why it's not a direct replacement for AD DS.
Example
Accessing a file share on a Windows Server uses Kerberos. Signing into Salesforce through SSO uses SAML tokens issued by Entra ID.
Why it matters — Understanding protocol differences explains why you can't just "move AD to the cloud" and expect everything to work.
Management and Control Plane Structure
AD DS uses forests, domains, OUs, and GPOs. Entra ID uses flat tenants, groups, app registrations, and Conditional Access policies.
AD DS organizes identity in a hierarchical tree: forests contain domains, domains contain OUs, and OUs hold user and computer objects. Group Policy Objects attach to OUs and push configuration to domain-joined devices. Entra ID is flat by design. There are no OUs, no nested domains, and no GPOs. Instead, you manage access through security groups, app registrations, Conditional Access policies, and (for device management) Microsoft Intune. Per Microsoft Learn, Entra ID Domain Services exists as a managed option when legacy apps need LDAP or Kerberos in the cloud, but it's a bridge solution, not a full AD DS replacement.
Example
In AD DS, you organize users into OUs and apply GPOs for configuration. In Entra ID, you use security groups and Conditional Access policies to control application access.
Why it matters — Trying to recreate OU hierarchies and GPO-based management in Entra ID leads to frustration and workarounds that weaken security.
Benefits
AD DS: Mature on-premises infrastructure control
Enterprise-grade identity for on-premises networks with deep Windows integration, GPO-based device management, and fine-grained delegation.
A hospital network using AD DS to manage thousands of domain-joined workstations, printers, and file shares across multiple sites.
Entra ID: Cloud-native security and SSO
SSO to thousands of SaaS apps, Conditional Access policies, MFA, Identity Protection, and Privileged Identity Management without on-premises infrastructure.
A remote-first company using Entra ID to authenticate employees into Microsoft 365, Salesforce, and AWS from any device, anywhere.
Hybrid: Best of both through Entra Connect
Entra Connect syncs on-premises AD identities to Entra ID, giving users a single identity for both on-prem resources and cloud apps.
An enterprise running AD DS for file servers and printers while using Entra ID for Microsoft 365 and third-party SaaS, with password hash sync keeping credentials unified.
Limitations
AD DS: No native cloud app integration
HighAD DS has no native support for modern authentication protocols (OAuth, SAML, OpenID Connect) and can't provide SSO to cloud/SaaS applications without Entra ID.
Workaround — Deploy Entra Connect to sync identities and use Entra ID as the cloud identity provider alongside AD DS.
Entra ID: No LDAP, GPO, or Kerberos support
HighEntra ID doesn't support LDAP queries, GPOs, Kerberos/NTLM authentication, or the hierarchical OU structure that legacy applications depend on.
Workaround — Use Entra ID Domain Services (managed domain) for legacy apps needing LDAP or Kerberos in Azure. Use Intune instead of GPOs for device management.
Hybrid: Operational complexity
MediumRunning both AD DS and Entra ID requires Entra Connect synchronization, careful password policy alignment, and ongoing operational overhead.
Workaround — Evaluate whether you can go cloud-only with Entra ID + Intune. Microsoft's 2026 strategic direction favors native Entra ID Join over Hybrid Join for new deployments.
Myths, corrected
Myth
Entra ID is just Active Directory in the cloud
Correction
They're fundamentally different systems. Entra ID has no forests, domains, OUs, LDAP, Kerberos, NTLM, or GPOs. It's a cloud-native identity platform built on REST APIs and modern authentication protocols. Per Microsoft's documentation, Entra ID Domain Services exists as a separate, managed service for legacy protocol support.
Why it happens: The original name "Azure Active Directory" implied it was a cloud version of AD DS. Microsoft acknowledged this confusion as a reason for the rebrand to Entra ID.
Myth
Entra ID replaces Active Directory
Correction
They complement each other. AD DS manages on-premises infrastructure. Entra ID manages cloud application access. Most enterprises run both in hybrid deployments synced via Entra Connect. Going fully cloud-only is possible but requires eliminating all on-premises resource dependencies.
Why it happens: Marketing messaging around cloud migration can suggest a complete replacement, but legacy apps, file shares, and print services still depend on AD DS.
Myth
The free tier of Entra ID is sufficient for enterprise use
Correction
The free tier covers basic authentication and SSO. Enterprise features like Conditional Access, Identity Protection, Privileged Identity Management, and access reviews require Entra ID P1 or P2 licenses (included in Microsoft 365 E3/E5 or available standalone).
Why it happens: Organizations start with the free tier and assume all features are included, then discover policy enforcement gaps when scaling.
Practical implications
For admins
Plan your hybrid identity architecture around which resources live where. AD DS for on-prem infrastructure, Entra ID for cloud apps, Entra Connect to bridge them. Don't try to force one system to do the other's job.
For MSPs
Most clients will run hybrid for years. Build expertise in both AD DS management and Entra ID Conditional Access. Position cloud-only Entra ID + Intune as the long-term target for new deployments.
For business
Hybrid identity enables employees to use a single set of credentials for all resources. This reduces help desk calls, improves productivity, and supports compliance requirements for access auditing.
For security
Entra ID's Conditional Access and Identity Protection provide stronger adaptive security than AD DS alone. For hybrid environments, ensure password hash sync is enabled so Entra ID can detect compromised credentials even for on-prem accounts.
Decision guide
Use when
- You manage cloud applications like Microsoft 365, Azure, or third-party SaaS (use Entra ID).
- You manage on-premises Windows infrastructure with file shares, printers, and legacy apps (use AD DS).
- You need single identity across on-prem and cloud resources (use both with Entra Connect).
Avoid when
- You need LDAP queries, Kerberos authentication, or GPO-based device management (use AD DS).
- All your apps and resources are on-premises with no cloud services (AD DS alone may suffice).
Requirements
- AD DS: Windows Server domain controllers, DNS infrastructure.
- Entra ID: Microsoft 365 or Azure subscription (free tier available).
- Hybrid: Entra Connect or Cloud Sync agent, network connectivity between DC and Azure.
Alternatives
- Entra ID Domain Services for legacy apps needing LDAP/Kerberos in Azure.
- Third-party IDaaS platforms (Okta, Ping Identity) as Entra ID alternatives.
- AD DS with ADFS for on-prem SSO without Entra ID.
Frequently asked questions
Is Microsoft Entra ID a replacement for Active Directory?
No. They're different systems designed for different environments. AD DS manages on-premises infrastructure using Kerberos, LDAP, and GPOs. Entra ID manages cloud application access using OAuth 2.0, SAML, and Conditional Access. Most organizations run both together in hybrid deployments.
What's the difference between Azure AD and Microsoft Entra ID?
Azure Active Directory was renamed to Microsoft Entra ID in July 2023. Per Microsoft, the product itself didn't change; the rebrand aligned it with the broader Entra identity product family (Entra ID, Entra Permissions Management, Entra Verified ID, etc.).
How do I sync Active Directory with Entra ID?
Use Entra Connect (formerly Azure AD Connect) or Entra Cloud Sync. Entra Connect is the traditional tool requiring a dedicated server. Cloud Sync uses lightweight agents and is Microsoft's recommended approach for new deployments. Both sync users, groups, and password hashes from AD DS to Entra ID.
What is Entra ID Domain Services?
Entra ID Domain Services is a managed service that provides domain join, Group Policy, LDAP, and Kerberos/NTLM authentication in Azure without deploying your own domain controllers. It's designed for legacy applications that need these protocols in the cloud, not as a full AD DS replacement.
Can I go fully cloud with Entra ID and drop AD DS entirely?
Yes, but it requires eliminating all dependencies on on-premises resources (file shares, printers, legacy apps using LDAP/Kerberos). Devices would use Entra ID Join instead of domain join, and Intune replaces Group Policy for device management. Microsoft's 2026 strategic direction favors this approach for new deployments.
Why can't Entra ID use Kerberos like Active Directory?
AD DS uses Kerberos and NTLM, which are designed for on-premises domain networks. Entra ID uses OAuth 2.0, SAML 2.0, and OpenID Connect, which are designed for web and API authentication. The protocol mismatch is why Entra ID can't directly replace AD DS for applications expecting LDAP or Kerberos.
Conclusion
Active Directory Domain Services and Microsoft Entra ID are not competing products. AD DS secures infrastructure inside a domain using Kerberos and GPOs. Entra ID secures application access from anywhere using OAuth and Conditional Access. Most enterprises run both in hybrid, synced via Entra Connect. New cloud-first deployments should evaluate whether native Entra ID Join with Intune can replace domain join entirely.
Main takeaway
Look into Entra Connect vs Cloud Sync for synchronization options, Conditional Access policy design, and Microsoft's hybrid identity architecture guidance on Microsoft Learn.