DMZ Network Explained: Architecture, Security, and Best Practices

- Level
- Beginner
- Reading time
- 16 min
- Concept
- DMZ (Demilitarized Zone) Network
- Last reviewed
- July 14, 2026
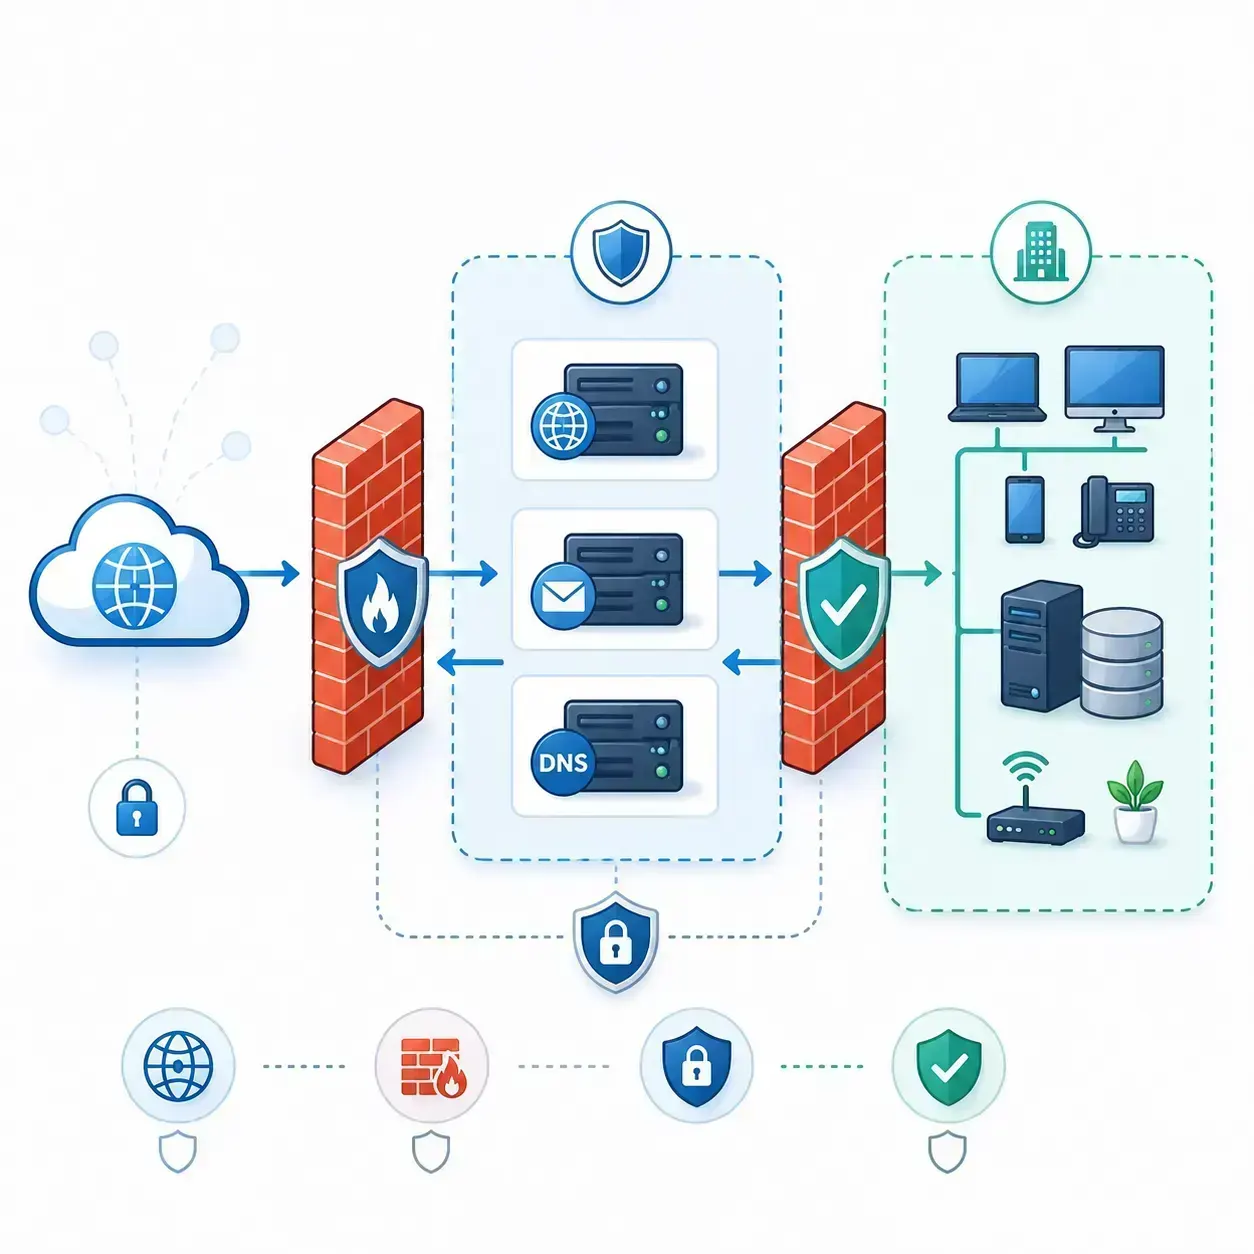
Table of contents
A DMZ (demilitarized zone) is a network segment that isolates public-facing services from your internal network. It sits between two firewall boundaries, letting external users reach web servers, email servers, and DNS while blocking direct access to the private LAN where sensitive data lives. If an attacker compromises a DMZ server, the internal firewall still protects core systems.
Key takeaways
- A DMZ isolates public-facing services (web, email, DNS) from the internal network using firewalls.
- Two main architectures exist: single-firewall (three interfaces) and dual-firewall (two separate firewalls).
- If a DMZ server is compromised, the internal firewall still protects the private LAN.
- DMZs are a baseline requirement in many compliance frameworks including PCI DSS and ISO 27001.
- In cloud environments, the DMZ concept maps to public/private subnets within a VPC.
Quick explanation
In simple terms
A DMZ is a fenced-off section of your network where you put servers that need to be accessible from the internet, keeping them separate from the rest of your internal systems.
Technical definition
A DMZ is a perimeter subnet isolated by one or more firewalls, hosting externally accessible services while enforcing strict ACLs that limit traffic flow between the public internet, the DMZ, and the internal trusted network.
Analogy
Think of a DMZ like the reception area in a secure office building. Visitors can enter the lobby and interact with the receptionist, but they can't walk through the locked door into the offices without authorization.
Definition
A DMZ is a perimeter network segment that sits between the public internet and an organization's internal LAN, isolated by firewalls. It hosts public-facing services like web servers, email servers, and DNS servers so that external users can reach those services without having direct access to internal systems.
A demilitarized zone (DMZ) is a physical or logical network segment that provides an isolation layer between an organization's public-facing services and its private internal network. The DMZ is separated from both the internet and the internal LAN by firewalls, which enforce strict access rules controlling what traffic can move between zones.
The term borrows from the military concept of a neutral buffer zone between opposing forces. In network security, the DMZ serves a similar purpose: it contains services that must be accessible from the internet (web servers, mail servers, DNS, FTP, VPN endpoints) while preventing external users and attackers from reaching the internal network where sensitive data and core business systems live.
If an attacker compromises a server in the DMZ, the internal firewall still stands between them and the private network. This containment strategy limits the blast radius of a breach and gives security teams time to detect and respond.
Why it matters
Core concepts
Network segmentation through firewall zones
Firewall zones divide a network into trust levels. The DMZ sits at a lower trust level than the internal LAN but higher than the untrusted internet.
Firewalls enforce access rules between zones. Traffic from the internet can reach the DMZ on specific ports (HTTP/443, SMTP/25, DNS/53). Traffic from the DMZ to the internal network is tightly restricted, typically limited to specific application connections like database queries on defined ports. Traffic from the internal network to the DMZ is more permissive, allowing admin access for management.
This layered approach means each zone has its own security posture. Even if the DMZ is compromised, the firewall rules between DMZ and internal network limit lateral movement.
Example
A web server in the DMZ accepts HTTPS on port 443. It queries a MySQL database on the internal network via port 3306 only. The firewall blocks all other DMZ-to-internal traffic.
Why it matters — Without zone-based segmentation, a compromised public server could directly access internal file shares, domain controllers, and databases.
Single-firewall DMZ architecture
A single firewall with at least three network interfaces creates the DMZ: one for internet, one for DMZ, one for internal network.
This is the simpler and cheaper design. One firewall device manages all traffic between the three zones using separate rulesets per interface. It works well for smaller organizations with moderate security requirements.
The tradeoff is a single point of failure. If the firewall is misconfigured or compromised, all three zones are affected. Per TechTarget, this design is common in small to mid-sized environments where cost and complexity matter more than maximum isolation.
Example
A pfSense appliance with three Ethernet ports: WAN (internet), DMZ (web server subnet), and LAN (internal network).
Why it matters — Single-firewall designs are accessible and cost-effective, but they concentrate risk on one device.
Dual-firewall DMZ architecture
Two separate firewalls flank the DMZ: an external firewall between internet and DMZ, an internal firewall between DMZ and private network.
The dual-firewall design offers stronger isolation. An attacker who compromises the external firewall still faces the internal firewall. Using firewalls from different vendors further reduces the risk of a single vulnerability affecting both devices.
This architecture is preferred for high-security environments, financial institutions, and healthcare organizations. Per Fortinet's documentation, the majority of modern enterprise DMZ architectures use the dual-firewall approach.
Example
A Palo Alto firewall faces the internet. A Cisco ASA sits between the DMZ and the internal network. An attacker must bypass both.
Why it matters — Dual-firewall designs eliminate the single point of failure and add a second barrier after a DMZ breach.
Services that belong in a DMZ
Any service that must be accessible from the public internet is a candidate for DMZ placement.
Common DMZ services include web servers, mail relays (SMTP), DNS servers, FTP servers, VPN concentrators, reverse proxies, and VoIP gateways. Per Fortinet, these services need public reachability but should never store or process sensitive data directly.
DMZ servers should be hardened: minimal software, unnecessary services disabled, logging enabled, regular patching. They act as intermediaries, passing requests to internal systems rather than hosting the data themselves.
Example
A reverse proxy in the DMZ terminates TLS and forwards requests to application servers on the internal network.
Why it matters — Placing the wrong services in the DMZ (like a database or domain controller) defeats its purpose.
DMZ in cloud environments
In cloud platforms, the DMZ concept maps to public subnets within a VPC, separated from private subnets by security groups and NACLs.
Cloud providers don't use the term DMZ explicitly, but the architecture is equivalent. Public subnets host load balancers and bastion hosts with internet-routable IPs. Private subnets hold application servers and databases with no direct internet access. Security groups and NACLs act as the firewall rules.
Per the Infosec Institute, virtual DMZ cloud architecture provides a similar security buffer using software-defined networking instead of physical firewalls. The principles are identical: isolate public-facing resources, control traffic between zones, and limit blast radius.
Example
In AWS, a VPC has a public subnet with an ALB and a private subnet with EC2 instances. A NAT gateway allows outbound access from the private subnet.
Why it matters — Understanding how DMZ concepts translate to cloud is essential for organizations migrating from on-premises infrastructure.
How it works
External request arrives
A user on the internet sends a request (e.g., HTTPS to a web server). The request reaches the external firewall.
Internet to External Firewall
Example — A browser requests https://company.com.
External firewall filters the request
The external firewall checks the request against its ruleset. Only allowed traffic types on specific ports to DMZ hosts pass through.
External Firewall to DMZ
Example — Firewall allows TCP/443 to the web server but drops port scans.
DMZ server processes the request
The server in the DMZ handles the request. If it needs data from an internal system, it opens a connection through the internal firewall.
DMZ Server to Internal Firewall
Example — Web server queries a MySQL database on the internal network via port 3306.
Internal firewall enforces strict rules
The internal firewall only permits specific predefined connections between DMZ hosts and internal systems. All other traffic is blocked.
Internal Firewall to Internal LAN
Example — Firewall allows port 3306 from the web server to the database, blocks everything else.
Response returns through the same path
The response travels back through the firewalls. Stateful firewalls track the connection and allow return traffic matching an established session.
Internal LAN to DMZ to Internet
Example — Database returns query results; web server renders the page and sends it to the user.
Use cases
Hosting public web applications on-premises
Network adminsPlace web servers in the DMZ so external users can access them without reaching internal databases.
Customer portal on a DMZ web server connecting to an internal database through the internal firewall.
Benefit — Compromising the web server doesn't give attackers direct database access.
Securing email infrastructure
Email administratorsPlace SMTP relays in the DMZ. Internal mail servers sit behind the internal firewall.
Exchange Edge Transport in the DMZ relaying mail to internal Exchange.
Benefit — Internal mail server never directly exposed to the internet.
VPN and remote access endpoints
Remote access adminsPlace VPN concentrators in the DMZ as controlled entry points.
VPN appliance in the DMZ terminates SSL VPN connections.
Benefit — VPN endpoint is exposed but internal network requires authentication and firewall rules.
Meeting compliance requirements
Compliance officersPCI DSS, HIPAA, and ISO 27001 require network segmentation for sensitive data systems.
Payment web frontend in DMZ, cardholder data environment on internal network.
Benefit — Reduces audit scope and demonstrates defense in depth.
Benefits
Limits blast radius of a compromise
A compromised DMZ server can't automatically access internal systems.
Attacker exploits DMZ web server but can't reach the internal database.
Provides defense in depth
Multiple firewall boundaries create layered defenses.
Breaching the external firewall only gets into the DMZ, not the LAN.
Simplifies firewall rule management
Separating public services into their own zone makes rules clearer.
Audit teams review DMZ-to-internal rules as a discrete set.
Supports compliance requirements
Many frameworks require segmentation between public and internal systems.
PCI DSS Requirement 1 calls for firewall-based segmentation.
Limitations
Adds complexity and cost
MediumRequires additional firewall hardware, licensing, and ongoing management.
Workaround — Single-firewall DMZ or cloud VPC subnets reduce cost while preserving the principle.
Doesn't protect against internal threats
MediumDMZ protects from external attacks but not insider threats or compromised endpoints.
Workaround — Combine with internal segmentation, endpoint detection, and zero-trust.
Misconfiguration negates all benefits
HighOverly permissive firewall rules between DMZ and internal network defeat the purpose.
Workaround — Regular firewall audits and least-privilege rules.
Less relevant for fully cloud-native environments
LowOrganizations with no on-premises public services may find cloud-native controls more practical.
Workaround — Apply the same principle using cloud VPC public/private subnets.
Architecture
A DMZ architecture creates three network zones: untrusted (internet), DMZ (semi-trusted, hosting public services), and trusted (internal LAN). Firewalls separate each zone and enforce traffic rules.
External firewall
Controls traffic between the internet and the DMZ. Allows only specific ports and protocols.
A Palo Alto NGFW allowing HTTPS, SMTP, and DNS inbound to DMZ hosts.
Internal firewall
Controls traffic between the DMZ and the internal network. Only permits specific application connections.
A Cisco ASA allowing the DMZ web server to reach the internal database on port 3306.
DMZ servers
Host public-facing services. Hardened with minimal software and full logging.
An Nginx reverse proxy terminating TLS and forwarding to internal app servers.
IDS/IPS
Monitors DMZ traffic for malicious patterns.
Suricata inspecting traffic between the internet and the DMZ.
Monitoring and logging
Collects logs from DMZ servers and firewalls for anomaly detection and incident response.
A SIEM collecting syslog from firewalls and DMZ servers.
Data flow
Internet > External Firewall > DMZ Server > Internal Firewall > Internal Server > reverse path.
Integrations: SIEM platforms, IDS/IPS, Vulnerability scanners, Cloud VPC subnets
Architecture limitations
Examples
Small business web hosting
A small business hosts a public website on the same network as its internal file server.
Placing the web server in a DMZ behind a firewall with three interfaces ensures the web server is reachable on port 443, but a compromise doesn't expose internal file shares or accounting data.
Enterprise email relay
A large organization receives thousands of emails daily with sensitive mailbox data on the internal Exchange server.
An SMTP relay in the DMZ filters spam and malware before forwarding clean messages to the internal Exchange server through the internal firewall.
Cloud VPC equivalent
An organization hosts its application in AWS with a web tier and a database tier.
The web tier runs in a public subnet (DMZ equivalent) with an ALB. The database tier runs in a private subnet with no internet-facing IP. Security groups control traffic.
Comparisons
DMZ vs Zero Trust Architecture vs Zero Trust
A DMZ creates trust zones. Zero trust eliminates implicit trust entirely, verifying every request regardless of network location.
| Criterion | DMZ vs Zero Trust Architecture | Zero Trust |
|---|---|---|
| Trust model | Zone-based: DMZ is semi-trusted, internal LAN is trusted | No implicit trust: every request verified regardless of origin |
| Focus | Perimeter defense between network zones | Identity and context-based access control at every layer |
| Maturity | Established, widely deployed for 20+ years | Emerging as the modern standard, per NIST SP 800-207 |
When to choose — DMZs remain useful for on-premises public services. Zero trust complements DMZ architecture. They're not mutually exclusive.
Myths, corrected
Myth
A DMZ makes internal systems completely safe from external attacks
Correction
A DMZ limits exposure but doesn't eliminate risk. Poorly configured rules or unpatched DMZ servers can still lead to internal compromise.
Why it happens: The term implies neutrality, which some interpret as safety.
Myth
DMZs are obsolete because of cloud and zero trust
Correction
The concept still applies wherever public services exist. Cloud VPCs implement the same principle. Zero trust complements rather than replaces DMZ architecture.
Why it happens: Marketing around zero trust sometimes positions it as a complete replacement.
Myth
You should put your database in the DMZ for performance
Correction
Databases should never be in the DMZ. They contain sensitive data and belong on the internal network, reachable only through specific firewall rules.
Why it happens: Some administrators place databases in the DMZ to avoid firewall latency.
Myth
A single firewall can't create a real DMZ
Correction
A single firewall with three interfaces creates a functional DMZ. The tradeoff is a single point of failure, not an architectural flaw.
Why it happens: Some security literature only discusses dual-firewall designs.
Practical implications
For admins
Maintain strict firewall rules, patch DMZ servers promptly, and monitor DMZ traffic for anomalies. Regular firewall audits prevent rule creep.
For MSPs
Standardize firewall templates, automate patch management for DMZ hosts, and include DMZ monitoring in managed service offerings.
For business
A DMZ demonstrates security maturity to customers and auditors. It's often a prerequisite for compliance certifications.
For security
Treat DMZ servers as high-risk targets. Include them in vulnerability scanning, penetration testing scope, and incident response plans.
Cost impact
Single-firewall DMZ adds minimal cost. Dual-firewall adds hardware and licensing overhead. Cloud equivalents incur no additional infrastructure cost.
Operational impact
DMZ maintenance is ongoing: firewall rule management, server patching, log monitoring, and periodic architecture reviews.
Decision guide
Use when
- You host public-facing services on-premises
- Compliance frameworks require network segmentation
- You need to limit blast radius of a server compromise
- External users need access to specific services but not your internal network
Avoid when
- No on-premises public-facing services (fully cloud-native)
- Network too small to justify complexity (no public servers)
- Looking for a replacement for internal segmentation (DMZ protects perimeter only)
Requirements
- At least one firewall with three or more interfaces (or two firewalls)
- Network addressing plan separating DMZ, internal, and external subnets
- Firewall rules following least-privilege principles
- Ongoing patch management for DMZ servers
Alternatives
- Cloud VPC with public/private subnets
- Reverse proxy or WAF in front of internal servers
- Zero trust network access (ZTNA) for internal access control
Related terms
Firewall
A network security device that monitors and controls traffic based on predefined rules.
Network segmentation
Dividing a network into smaller segments to improve security and control traffic between them.
Bastion host
A hardened server in the DMZ or public subnet designed to withstand attacks, often used as a jump box.
Reverse proxy
A server in front of backend servers that forwards client requests. Often placed in the DMZ to terminate TLS.
Zero trust architecture
A security model requiring strict identity verification for every access request, regardless of network location. Defined in NIST SP 800-207.
VPC (Virtual Private Cloud)
An isolated virtual network in a cloud provider where you define subnets, routing, and security rules. Public subnets serve the same function as a DMZ.
Frequently asked questions
What is a DMZ in networking?
A DMZ is a network segment isolated by firewalls that sits between the public internet and an organization's internal network. It hosts public-facing services so external users can reach them without direct access to the internal LAN.
What is the difference between single-firewall and dual-firewall DMZ?
A single-firewall DMZ uses one firewall with three interfaces. A dual-firewall DMZ uses two separate firewalls flanking the DMZ. Dual-firewall designs offer stronger isolation but cost more and are more complex.
Which services should be placed in a DMZ?
Services accessible from the public internet: web servers, email relays, DNS servers, FTP, VPN endpoints, and reverse proxies. Databases, domain controllers, and file servers should never be in the DMZ.
Is a DMZ still relevant with cloud and zero trust?
Yes. The concept translates to cloud environments as public/private subnets in a VPC. Zero trust complements DMZ architecture by adding identity-based access control. Most architectures use both.
Does a DMZ protect against internal threats?
No. A DMZ protects the internal network from external attacks through public-facing services. It doesn't address insider threats or compromised internal endpoints. Combine with internal segmentation and endpoint detection.
What compliance frameworks require a DMZ?
PCI DSS requires firewall segmentation between untrusted networks and cardholder data environments. HIPAA and ISO 27001 require controls isolating systems processing sensitive data. A DMZ directly satisfies these requirements.
Conclusion
A DMZ creates a controlled buffer between the public internet and your internal network. By placing public-facing services in an isolated segment protected by firewalls, you limit what an attacker can reach even if they compromise an exposed server. The concept is decades old but remains foundational, on-premises or in the cloud.
Main takeaway
If you're implementing a DMZ, explore firewall rule best practices and consider how zero trust architecture complements perimeter security.