TCP vs UDP Ports Explained: Key Differences and Use Cases

- Level
- Beginner
- Reading time
- 11 min
- Concept
- TCP vs UDP and network ports
- Last reviewed
- July 18, 2026
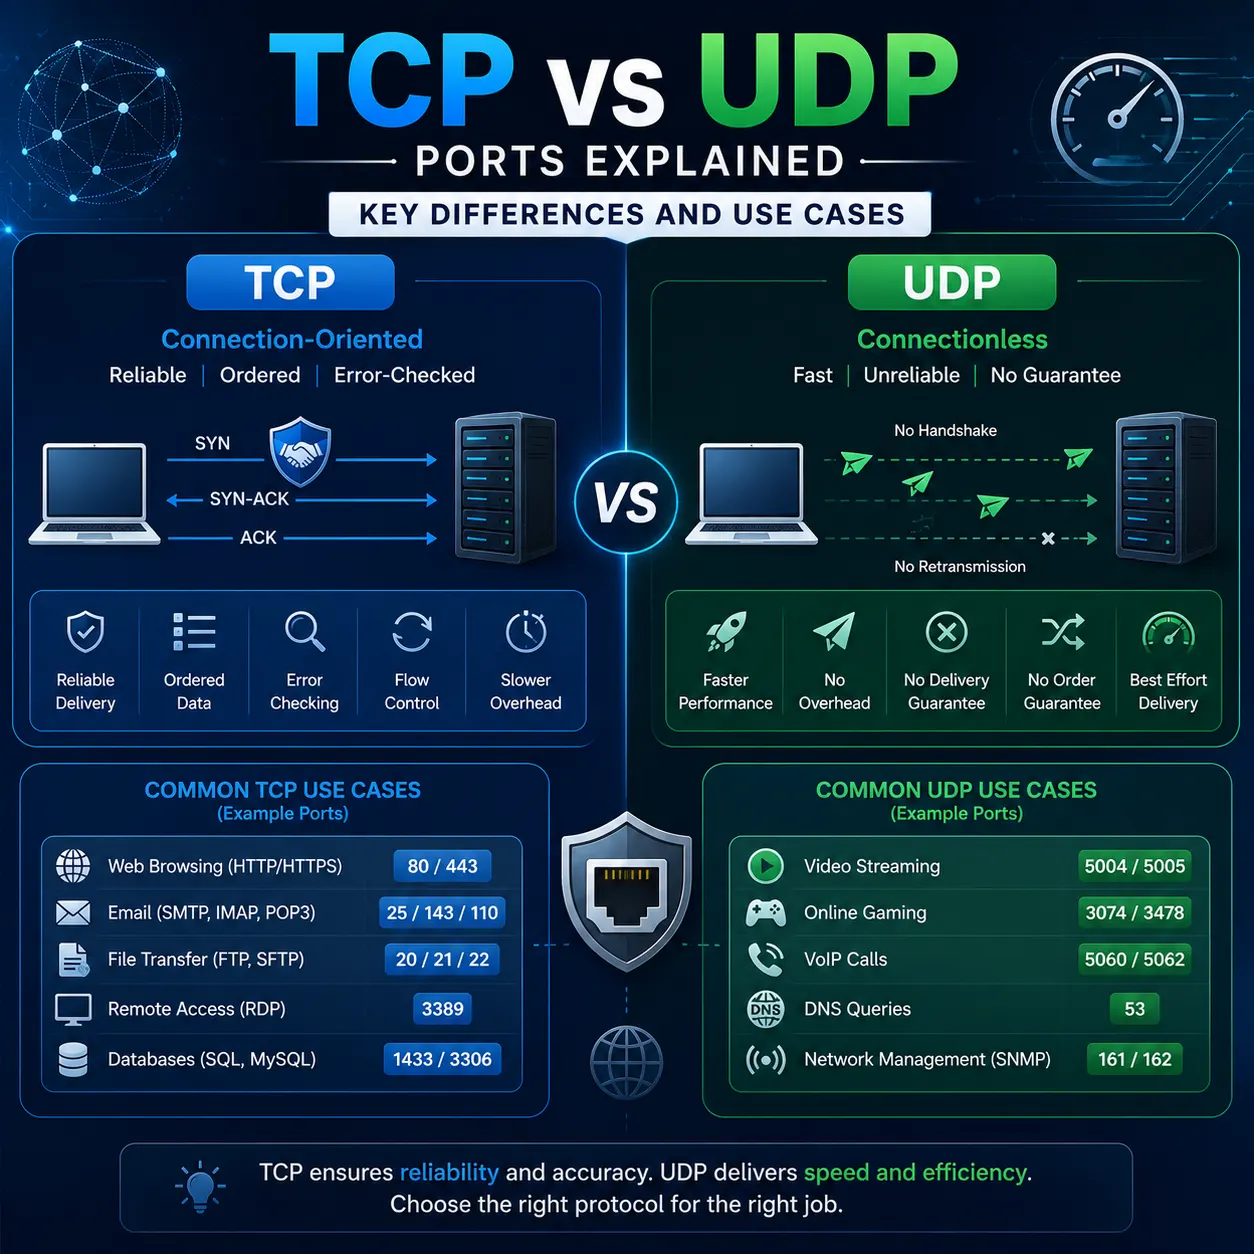
Table of contents
TCP and UDP are the two transport-layer protocols that carry data across IP networks. Both use port numbers to route traffic to the correct application, but they handle delivery in fundamentally different ways. TCP prioritizes reliability with connection setup and acknowledgments. UDP prioritizes speed by skipping those steps entirely.
Key takeaways
- TCP uses a three-way handshake to establish connections and guarantees ordered, reliable delivery.
- UDP sends datagrams without connection setup, acknowledgments, or delivery guarantees.
- Ports (0-65535) direct traffic to the right application on each device. Some are shared, some are protocol-specific.
- TCP suits web browsing, email, file transfers. UDP suits streaming, gaming, DNS, and VoIP.
- Open ports are attack surfaces. Firewalls, IDS/IPS, and port scanning are key security controls.
Quick explanation
In simple terms
TCP (Transmission Control Protocol) delivers data reliably by establishing a connection and confirming receipt. UDP (User Datagram Protocol) delivers data fast by skipping connection setup and not waiting for confirmation. Both use port numbers to direct traffic to specific applications.
Technical definition
TCP (RFC 793) is a connection-oriented, stateful transport protocol that uses a three-way handshake (SYN, SYN-ACK, ACK), sequence numbers, acknowledgments, flow control (sliding window), and congestion control (slow start, congestion avoidance) to guarantee ordered, reliable byte-stream delivery. UDP (RFC 768) is a connectionless, stateless protocol that sends datagrams with a minimal 8-byte header (source port, destination port, length, checksum) and provides no delivery guarantees, ordering, or flow control.
Analogy
TCP is like a phone call: you dial, the other side picks up, you confirm you can hear each other, then you talk. If a word gets lost, you ask "can you repeat that?" UDP is like shouting across a room: faster, but nobody confirms they heard you, and if a word gets lost, it's gone.
Definition
TCP (Transmission Control Protocol) and UDP (User Datagram Protocol) are transport-layer protocols that use port numbers to route data to applications. TCP ensures reliable, ordered delivery. UDP prioritizes speed over reliability.
Every network connection between two devices needs three things: a source IP, a destination IP, and port numbers to identify which application should handle the traffic. Ports range from 0 to 65535, divided into well-known ports (0-1023, assigned by IANA), registered ports (1024-49151), and dynamic/ephemeral ports (49152-65535).
The transport layer sits between the application layer and the network layer in the TCP/IP stack. Its job is to take data from an application, segment it, and hand it to IP for delivery. TCP and UDP are the two protocols that do this work, per the IETF standards (RFC 793 for TCP, RFC 768 for UDP).
TCP establishes a connection before sending data using a three-way handshake: the client sends a SYN packet, the server responds with SYN-ACK, and the client confirms with ACK. After that, every segment is numbered, acknowledged, and retransmitted if lost. This makes TCP reliable but adds latency overhead.
UDP skips all of that. It sends datagrams immediately with an 8-byte header (source port, destination port, length, checksum). No handshake, no acknowledgment, no retransmission. If a packet is lost, the application handles it or ignores the loss. This makes UDP faster but unreliable at the protocol level.
Why it matters
Core concepts
TCP Three-Way Handshake
A three-step process (SYN > SYN-ACK > ACK) that establishes a TCP connection before any data is sent.
The handshake ensures both sides are reachable and ready. It also synchronizes sequence numbers used to track every byte sent. If any of the three packets is lost, the connection doesn't establish. This is why TCP is called "connection-oriented," per RFC 793. The trade-off is latency: the handshake adds one full round-trip time (RTT) before data flows. For a server 100ms away, that's 100ms of pure overhead before the first byte of actual content.
Example
When you open https://example.com, your browser sends a SYN to port 443, the server replies SYN-ACK, your browser sends ACK, and only then does TLS negotiation begin.
Why it matters — The handshake is why TCP is reliable but slower. Every TCP connection starts with this overhead.
UDP Connectionless Delivery
UDP sends data as independent datagrams without establishing a connection or confirming receipt.
UDP's header is just 8 bytes: source port, destination port, length, and checksum. There's no sequence numbering, no acknowledgment, no retransmission, and no flow control. If a packet is lost, the sender doesn't know unless the application implements its own checks. Per RFC 768, this minimal design was intentional. UDP was built for applications where speed matters more than perfect delivery. Modern protocols like QUIC (used by HTTP/3) build reliability on top of UDP at the application layer, getting TCP-like guarantees with UDP-like performance.
Example
A DNS query to port 53: your device sends a single UDP packet with the domain name. The DNS server replies with the IP address. No handshake, no ACK.
Why it matters — UDP's simplicity is its strength. Missing one frame of a video call is better than waiting 200ms for a retransmission.
Port Numbers and Ranges
IANA assigns well-known ports (0-1023) to standard services. Registered ports (1024-49151) are for vendor applications. Ephemeral ports (49152-65535) are assigned dynamically to client connections.
A port number is a 16-bit unsigned integer (0-65535) that identifies a specific process or service on a device. Combined with an IP address, a port creates a socket: a unique endpoint for communication. The Internet Assigned Numbers Authority (IANA) maintains the official port registry. Some services use both TCP and UDP on the same port number: DNS uses UDP 53 for standard queries and TCP 53 for zone transfers. Open ports are potential attack vectors, which is why firewalls default to blocking all ports and only allowing specific ones.
Example
HTTP uses TCP 80, HTTPS uses TCP 443, DNS uses UDP 53, DHCP uses UDP 67-68, RDP uses TCP 3389, SSH uses TCP 22.
Why it matters — Knowing which ports your services need is the foundation of firewall rules and network security.
Benefits
TCP: Guaranteed reliable delivery
TCP's acknowledgments, retransmission, and ordering guarantee that every byte arrives intact and in sequence.
Downloading a 500 MB file over FTP (TCP 21/20): not a single byte is lost or out of order.
UDP: Minimal latency
UDP's 8-byte header and zero handshake overhead make it the fastest option for time-sensitive data.
A VoIP call on UDP 5060 (SIP) + RTP: voice packets arrive with minimal delay, keeping conversation natural.
TCP: Built-in flow and congestion control
TCP's sliding window and congestion avoidance (slow start, AIMD) prevent senders from overwhelming the network or the receiver.
A busy web server serving thousands of clients: TCP automatically throttles each connection to avoid packet loss.
Limitations
TCP: Latency overhead
MediumThe three-way handshake, acknowledgments, and retransmission add latency that makes TCP unsuitable for real-time applications.
Workaround — Use UDP for real-time apps. Or use QUIC (HTTP/3), which builds reliability on top of UDP with lower handshake cost.
UDP: No delivery guarantees
MediumUDP provides no guarantee that packets arrive, arrive in order, or arrive at all. The application must handle loss.
Workaround — Implement application-level reliability (e.g., QUIC, DTLS, custom ACK mechanisms) when some reliability is needed without full TCP overhead.
Both: Ports as attack surfaces
HighOpen TCP and UDP ports are potential entry points for attackers. Port scanning (e.g., Nmap) can map exposed services.
Workaround — Default-deny firewall policies, close unused ports, use IDS/IPS, and run regular port scans to detect exposure.
Myths, corrected
Myth
UDP is insecure and TCP is secure
Correction
Neither protocol provides encryption or authentication by itself. Security comes from upper-layer protocols: TLS for TCP, DTLS for UDP. A plaintext TCP connection is just as exposed as a plaintext UDP datagram.
Why it happens: People associate TCP's reliability mechanisms with security, but reliability and security are different properties.
Myth
UDP is only for streaming and gaming
Correction
UDP carries DNS (port 53), DHCP (ports 67-68), SNMP (port 161), TFTP (port 69), NTP (port 123), and modern web traffic via QUIC/HTTP/3 (port 443). It's used wherever low latency or simple request-response patterns matter more than guaranteed delivery.
Why it happens: Streaming and gaming are the most visible UDP use cases, but the protocol is foundational to many core network services.
Myth
TCP is always slower than UDP
Correction
On reliable, low-latency networks, TCP's overhead is negligible. Modern TCP optimizations (TCP Fast Open, window scaling, selective acknowledgments) close much of the performance gap. UDP's speed advantage is most significant on lossy or high-latency networks.
Why it happens: Textbooks emphasize the handshake overhead without noting that modern TCP implementations minimize it.
Practical implications
For admins
Know which ports your services use and build firewall rules accordingly. Default-deny inbound, allow only specific TCP/UDP ports. Run port scans (Nmap) against your own infrastructure regularly.
For MSPs
Document which ports each client application uses. Maintain port inventories for firewall audits. Use QUIC-aware firewalls and proxies as HTTP/3 adoption grows.
For business
Protocol choice affects user experience. A video conferencing platform on TCP would stutter under packet loss. A financial trading platform on UDP could silently lose orders. Match the protocol to the business requirement.
For security
Every open port is a potential attack vector. Monitor for unexpected listeners with netstat or ss. Use IDS/IPS to inspect traffic on allowed ports. Be aware that UDP is harder to firewall statefully than TCP because there's no handshake to track.
For end users
End users don't choose TCP or UDP directly, but they experience the consequences: smooth video calls (UDP), reliable file downloads (TCP), and fast web pages (QUIC over UDP).
Decision guide
Use when
- Use TCP for web browsing, email, file transfers, database connections, and any data that must arrive complete.
- Use UDP for live streaming, online gaming, VoIP, DNS queries, and time-sensitive broadcasts.
- Use QUIC/HTTP/3 for modern web applications that need low-latency reliable delivery.
Avoid when
- Don't use TCP for real-time voice/video where retransmission causes stutter.
- Don't use UDP for file transfers or database operations where data loss is unacceptable.
Requirements
- TCP: both endpoints must support connection establishment and maintain state.
- UDP: application must handle loss, ordering, and congestion if needed.
- Firewalls must allow the specific TCP/UDP port numbers your services use.
Alternatives
- QUIC (HTTP/3): reliability over UDP with lower latency than TCP.
- SCTP: multi-stream, multi-homed transport (used in telecom signaling).
- DCCP: congestion-controlled unreliable transport for streaming.
Frequently asked questions
What is the difference between TCP and UDP?
TCP guarantees reliable, ordered delivery using a three-way handshake and acknowledgments. UDP sends data immediately without connection setup or delivery confirmation. TCP suits file transfers and web browsing. UDP suits streaming, gaming, and DNS.
What is a port number?
A port is a 16-bit number (0-65535) that identifies a specific application on a device. Combined with an IP address, it creates a socket. Well-known ports (0-1023) are assigned by IANA: HTTP (80), HTTPS (443), SSH (22).
Can a service use both TCP and UDP?
Yes. DNS uses UDP 53 for standard queries and TCP 53 for zone transfers and large responses. Other services like NTP also listen on both protocols.
What are the most common port numbers?
TCP: 80 (HTTP), 443 (HTTPS), 22 (SSH), 21 (FTP), 25 (SMTP), 3389 (RDP). UDP: 53 (DNS), 67-68 (DHCP), 123 (NTP), 161 (SNMP), 5060 (SIP). QUIC/HTTP/3 uses UDP 443.
Are TCP and UDP secure?
Neither provides encryption by itself. TCP is secured with TLS. UDP uses DTLS or application-layer encryption. Open ports should be protected by default-deny firewall rules.
What is QUIC?
QUIC is a transport protocol built on UDP that provides TCP-like reliability with lower latency. It powers HTTP/3 and combines connection setup with TLS 1.3 in a single round trip on UDP port 443.
Conclusion
TCP and UDP are the two transport protocols that use port numbers to route data to applications. TCP guarantees reliable, ordered delivery through handshakes and acknowledgments, at the cost of latency. UDP sends datagrams immediately with no guarantees, trading reliability for speed. Ports (0-65535) identify services on each endpoint. Neither protocol provides encryption without TLS or DTLS.
Main takeaway
Look into QUIC (HTTP/3) for modern reliability-over-UDP, TLS/DTLS for transport security, and IANA's port registry for assigned port numbers.