What Is Event ID 4688? Windows Process Creation Audit Explained

- Level
- Beginner
- Reading time
- 6 min
- Concept
- Event ID 4688
- Last reviewed
- July 23, 2026
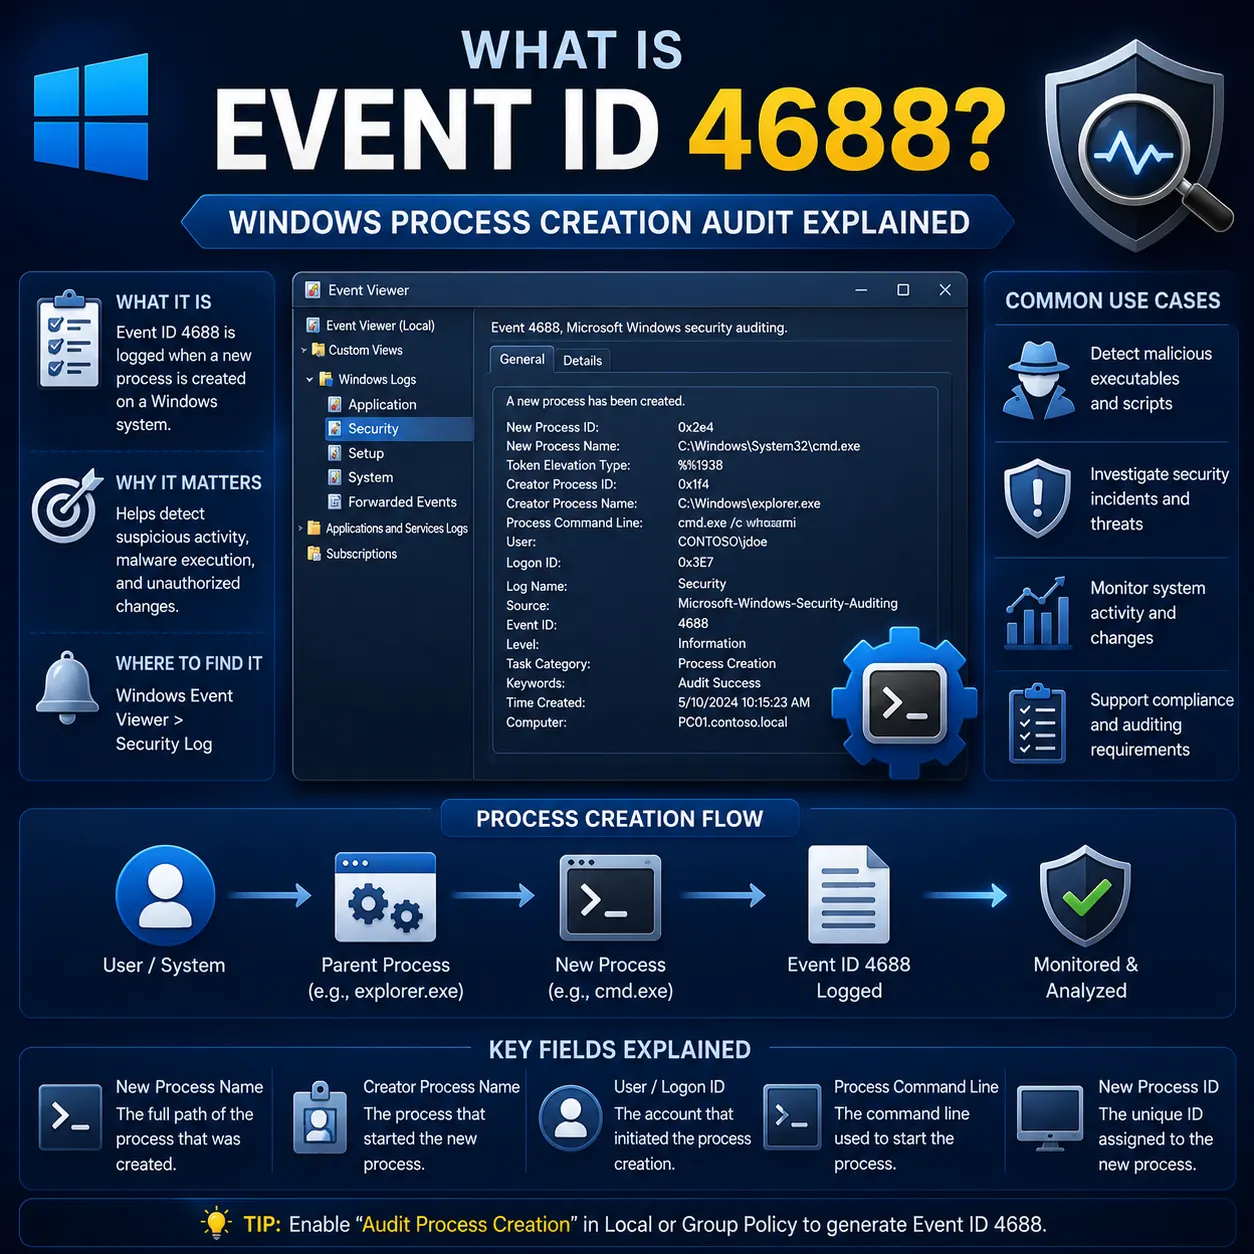
Table of contents
Event ID 4688 logs every process that starts on a Windows system when process creation auditing is enabled. It captures the executable path, command line, parent process, user context, and privilege level. Per Microsoft Learn, it is part of the Detailed Tracking audit category and requires explicit enablement.
Key takeaways
- Disabled by default. Enable via Group Policy > Audit Process Creation.
- Captures process name, PID, parent process, user, and Token Elevation Type.
- Command line logging requires a separate GPO setting.
- High volume on busy systems. Filtering and centralization are essential.
- Companion event: 4689 (process termination) for full lifecycle.
Quick explanation
In simple terms
A Windows log entry recording every time a program starts.
Technical definition
A Security log event from Microsoft-Windows-Security-Auditing capturing NewProcessName, NewProcessId, ParentProcessName, SubjectUserName, TokenElevationType, and ProcessCommandLine.
Analogy
Like a building security camera that records every time someone opens a door: who, which door, when, and who sent them.
Definition
A Windows Security log event that records every new process creation when Audit Process Creation is enabled.
Event ID 4688 is generated by Microsoft-Windows-Security-Auditing each time a process starts on a Windows system where Audit Process Creation is enabled. Per Microsoft Learn, it captures the new process name, PID, parent process, user account, Token Elevation Type, and optionally the full command line.
Why it matters
Core concepts
Audit Process Creation policy
The GPO setting that enables Event ID 4688.
Located at Advanced Audit Policy > Detailed Tracking > Audit Process Creation. When set to Success, Windows logs 4688 for every new process. Disabled by default.
Process Command Line logging
A separate GPO that adds the full command line to 4688 events.
Without this, you only see the executable path. The command line is critical for detecting LOLBin abuse and encoded PowerShell.
Token Elevation Type
A field showing the privilege level of the new process.
Type 1 (default, no elevation), Type 2 (elevated via UAC), Type 3 (admin running without elevation). Helps detect privilege escalation.
Parent-child process relationships
The link between the spawning process and the new process.
Unusual parent-child pairs like winword.exe spawning cmd.exe are strong indicators of macro attacks. Event ID 4688 records ParentProcessName and CreatorProcessId.
Event ID 4689 (process termination)
The companion event logging process exits.
Combined with 4688, provides complete process lifecycle: start time, duration, exit code.
How it works
Audit policy enables logging
An admin enables Audit Process Creation (Success) in Group Policy. Applied via gpupdate or next GP refresh.
Process starts on the system
Any process start (user app, service, scheduled task, child process) triggers the kernel audit event.
Event 4688 is created
The Security-Auditing provider writes Event 4688 to the Security log with all process details.
Event is consumed
SIEM, WEF, EDR, or PowerShell reads the event for detection and alerting.
Use cases
Security monitoring
SIEM platforms detect suspicious execution: encoded PowerShell, cmd from Office, executables from temp directories.
Incident response
Analysts reconstruct attack timelines using process creation chains.
Compliance auditing
PCI DSS, HIPAA, SOC 2, NIST 800-53 require system activity audit trails.
EDR integration
EDR solutions use 4688 as a primary data source for behavioral detection and ATT&CK mapping.
Software usage tracking
Identify what software actually runs on endpoints beyond installed programs.
Benefits
Visibility into every process that starts on the system
Captures user context, parent process, and privilege level
Command line logging reveals how programs are invoked
Built into Windows with no additional software
Integrates with all major SIEM and EDR platforms
Limitations
Disabled by default on all Windows editions
MediumHigh event volume can overwhelm log storage and SIEM
MediumDoes not capture file hashes, network, or registry changes
MediumCommand line logging requires a separate GPO
MediumLogs after execution, cannot prevent processes
MediumArchitecture
Generated by the Windows kernel audit subsystem and written to the Security log.
Audit Policy
Controls whether 4688 events are generated via Advanced Audit Policy.
LSA
Enforces audit policy and instructs the kernel to generate events.
Security Event Log
Stores events. Default max 20 MB with overwrite-oldest.
Event consumers
SIEM, WEF, EDR agents, and scripts that read events.
Data flow
Group Policy > LSA > Kernel audit > Security log > Consumers
Examples
Detecting encoded PowerShell
Tracking PsExec lateral movement
PCI DSS audit trail
Comparisons
Sysmon Event ID 1
Event ID 4689
Microsoft Defender for Endpoint
Myths, corrected
Myth
Event ID 4688 is enabled by default
Correction
Myth
4688 captures the command line automatically
Correction
Myth
Event ID 4688 can block malicious processes
Correction
Myth
Sysmon makes Event ID 4688 unnecessary
Correction
Practical implications
For admins
Enable via Group Policy. Set Security log to 1 GB on servers, 256 MB on workstations. Forward events centrally.
For MSPs
Include 4688 collection in standard SOC offerings. Alert on suspicious parent-child and LOLBin patterns.
For business
Provides audit trails for PCI DSS, HIPAA, SOC 2, NIST 800-53. Minimum viable process auditing.
For security
Build detection for encoded PowerShell, Office spawning shells, processes from temp directories, and unusual elevation types.
Operational impact
High volume on busy systems. Plan for increased log size and SIEM capacity.
Related terms
Event ID 4689
Process termination event. Companion to 4688.
Sysmon Event ID 1
Enhanced process creation event with hashes and network.
Audit Process Creation
The GPO that enables Event ID 4688.
Token Elevation Type
Field showing process privilege level.
LOLBins
Legitimate Windows tools abused by attackers.
Frequently asked questions
Is Event ID 4688 enabled by default?
No. You must enable Audit Process Creation through Group Policy (Advanced Audit Policy > Detailed Tracking > Success). Disabled on all editions by default.
How do I enable command line logging?
Enable a separate GPO: Administrative Templates > System > Audit Process Creation > Include command line in process creation events.
4688 vs Sysmon Event 1?
Sysmon Event 1 has file hashes and network info but needs separate installation. Event ID 4688 is built into Windows natively.
How to reduce 4688 noise?
Filter out common system processes (svchost, dwm, csrss) in your SIEM or WEF. Focus on user-initiated and suspicious parent-child relationships.
Can 4688 detect malware?
Yes, but only after execution. It records the event, not prevents it. Use AppLocker or WDAC for blocking.
Conclusion
Main takeaway