What Is SIEM? Definition, How It Works, and Use Cases

- Level
- Beginner
- Reading time
- 21 min
- Concept
- Security Information and Event Management (SIEM)
- Last reviewed
- July 12, 2026
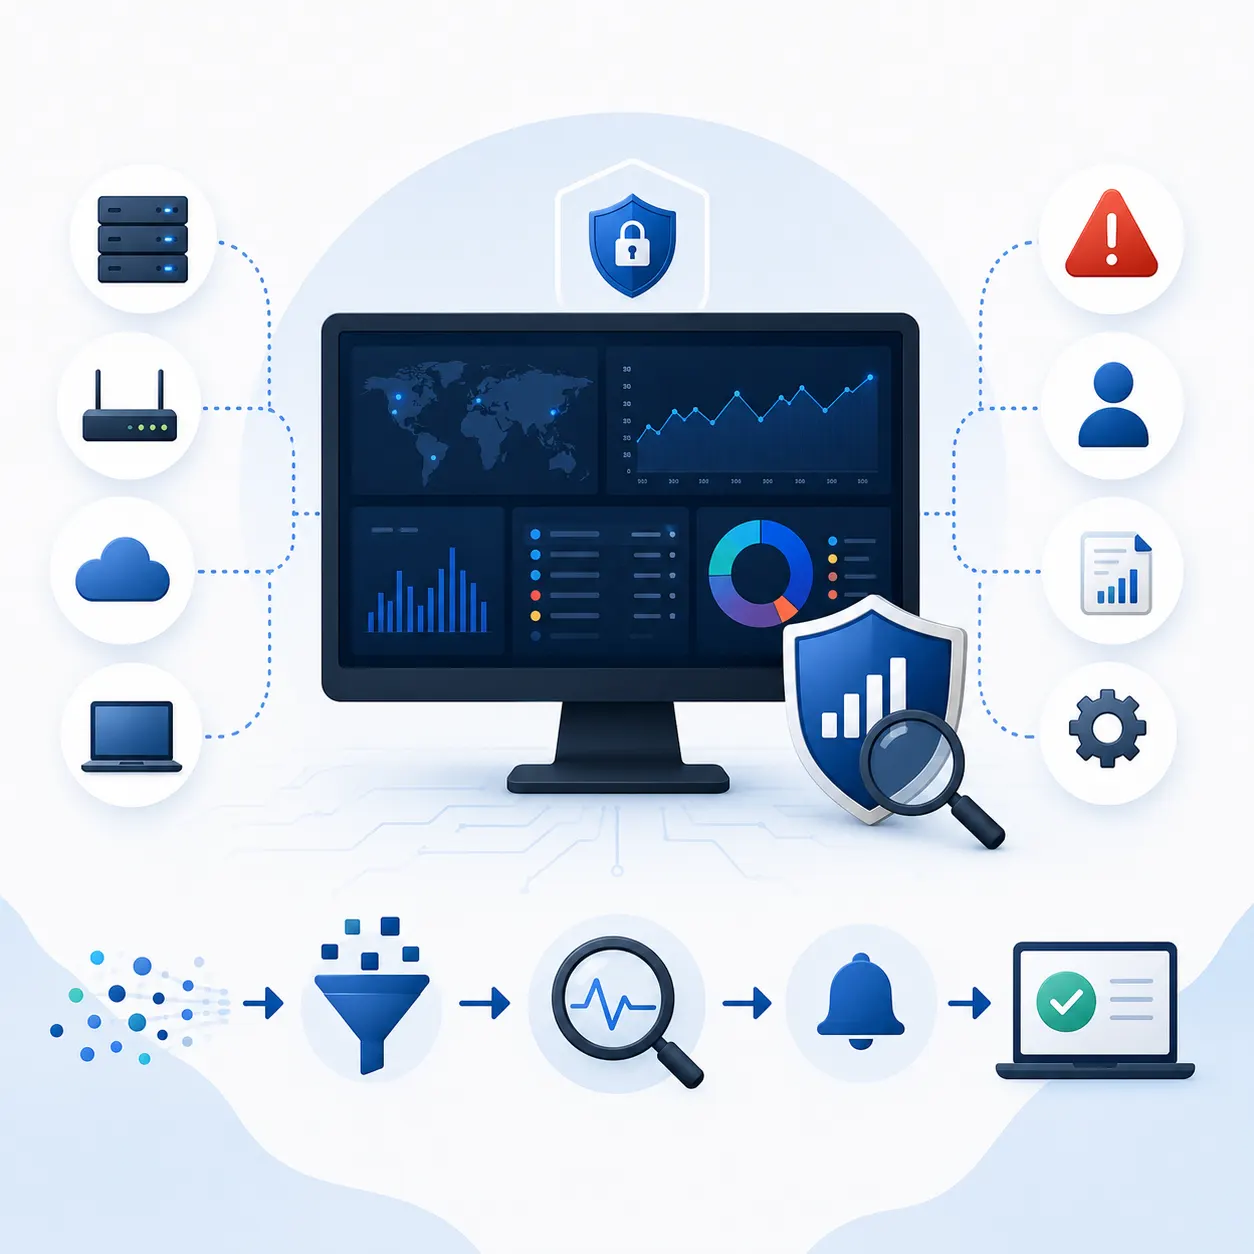
Table of contents
Security information and event management, or SIEM, is software that collects log and event data from across your IT environment, then correlates it in one place to spot security threats. It combines two older ideas: storing and searching security logs, and monitoring events in real time. Most security operations centers run a SIEM as the backbone that turns scattered, noisy log data into alerts an analyst can act on. This guide explains what SIEM is, how it works stage by stage, where teams use it, and the limits worth knowing before you buy.
Key takeaways
- SIEM stands for security information and event management; Gartner coined the term in 2005 by combining SIM and SEM.
- It works in stages: collect logs, normalize and enrich them, correlate and analyze, alert, then support investigation and response.
- Core value is centralized visibility and faster detection and response across firewalls, endpoints, identity, and cloud.
- Modern SIEMs add UEBA, SOAR integration, and machine learning to catch threats that static rules miss.
- SIEM isn't set-and-forget: it needs tuning, skilled staff, and a SOC process, and cost scales with data volume.
Quick explanation
In simple terms
SIEM is like a central security control room: it gathers reports from every system, watches for trouble, and rings an alarm when something looks wrong.
Technical definition
A SIEM is a platform that ingests, normalizes, and indexes log and event data from heterogeneous sources, applies correlation rules and analytics (including UEBA and ML) to detect indicators of compromise, and generates prioritized, enriched alerts plus compliance reporting.
Analogy
Think of it as an air traffic control tower for security: dozens of separate feeds come in, and the SIEM combines them into one screen so controllers can spot conflicts early.
Definition
SIEM is security software that collects log and event data from across an organization's IT environment, then normalizes and correlates it to detect, investigate, and report on security threats from a single interface.
Security information and event management (SIEM) is a security solution that gathers log and event data from across an organization's systems, then analyzes that data in one place to surface security threats.
The term dates to 2005, when Gartner named the pairing of two older technologies: security information management (SIM), which handles the collection and long-term storage of log data, and security event management (SEM), which handles real-time monitoring and correlation. A modern SIEM does both.
NIST defines a SIEM tool as an application that gathers security data from information system components and presents it as actionable information through a single interface. In practice, SIEM sits at the center of most security operations centers (SOCs), where analysts use it to detect, investigate, and respond to incidents.
Over time SIEM has grown beyond plain log management. Today's platforms add user and entity behavior analytics (UEBA), integrations with security orchestration, automation, and response (SOAR), and machine learning to spot patterns that simple rules miss.
Why it matters
Core concepts
Log collection and aggregation
Gathering event and log data from many sources into one central platform.
A SIEM ingests event data from across the environment: users, endpoints, applications, cloud workloads, and network devices, plus security tools like firewalls and antivirus. Collection runs in near real time so nothing important sits unseen.
This is the security information side of the original SIM plus SEM pairing. Without broad, reliable log sources, everything downstream suffers, because the SIEM can only analyze what it receives.
Example
A SIEM pulls sign-in logs from an identity provider, traffic logs from firewalls, and process logs from endpoints into one pipeline.
Why it matters — Coverage decides quality. Gaps in log sources create blind spots that attackers exploit.
Normalization and enrichment
Converting raw logs into a common schema and adding context.
Every device speaks its own log dialect. Normalization rewrites those records into a shared schema so events from a firewall and a cloud service can be compared side by side.
Enrichment then adds context: user and asset details, geolocation, threat intelligence, and vulnerability data. This extra context is what lets an analyst judge whether an event is routine or dangerous.
Example
A raw failed-login entry becomes a structured event tagged with the user's department, the device's risk score, and the source country.
Why it matters — Correlation only works when data is consistent. Good enrichment cuts investigation time and reduces false positives.
Correlation and analytics
Linking related events across sources to reveal a threat.
Correlation is the heart of a SIEM. It links events that look harmless alone but tell a story together. Rules, statistical baselines, and machine learning all play a part.
A classic example: repeated failed logins followed by a large outbound data transfer. Neither event alone is alarming, but the sequence points to a possible breach. This is the security event management side of SIEM.
Example
Ten failed logins, one success, then bulk file access from a new location triggers a single correlated incident instead of three unrelated logs.
Why it matters — Correlation is what separates a SIEM from plain log storage. It turns raw data into a lead worth chasing.
Alerting and incident management
Surfacing prioritized alerts and workflow on a central console.
When correlation finds something, the SIEM raises an alert. It de-duplicates noise, scores risk and confidence, and routes the alert to the right team through a central dashboard.
Good alerting is about focus. A SIEM that cries wolf trains analysts to ignore it, so tuning alerts to real risk is an ongoing job, not a one-time setup.
Example
A high-severity incident appears on the SOC dashboard with a risk score, affected users, and a timeline, ready for triage.
Why it matters — Alerts are where detection meets human action. Poor prioritization buries real threats under false alarms.
Compliance reporting and retention
Storing log data and generating audit reports for regulations.
SIEM keeps a searchable record of security events over time, which serves two goals. It supports forensic investigation after an incident, and it produces the audit trails regulators expect.
Many platforms ship with prebuilt reports for standards like PCI DSS, HIPAA, GDPR, and SOX. That automation cuts the manual work of proving controls are in place.
Example
A SIEM generates a quarterly PCI DSS report showing who accessed cardholder data and when, without an analyst pulling logs by hand.
Why it matters — Compliance is often the reason a SIEM gets funded. Retention also enables forensics and trend analysis.
Modern extensions: UEBA, SOAR, and threat intelligence
Analytics and automation layers added to classic SIEM.
Today's SIEMs go past rules. UEBA (user and entity behavior analytics) baselines normal behavior for each user and device, then flags deviations such as impossible travel or sudden privilege misuse.
SOAR integration adds automated playbooks that can enrich an alert, block an IP, or disable an account without waiting for a human. Threat intelligence feeds compare internal activity against known attack signatures. Together these layers cut mean time to respond.
Example
UEBA notices a user active in two countries at once and, through a SOAR playbook, forces re-authentication and disables the account pending review.
Why it matters — These layers catch threats static rules miss and reduce the manual load on stretched security teams.
How it works
Collect data from across the environment
The SIEM ingests logs and events from endpoints, servers, applications, cloud workloads, identity systems, and security tools like firewalls. Collection runs continuously so the platform has a live view of activity.
Collect
Example — Agents and connectors forward firewall, endpoint, and cloud sign-in logs into the SIEM pipeline.
Normalize and enrich the data
Raw logs arrive in dozens of formats. The SIEM rewrites them into a common schema and adds context such as user identity, asset criticality, geolocation, and threat intelligence, so unlike sources can be compared.
Normalize
Example — A firewall log and a cloud audit log both become structured events with shared fields for user, IP, and time.
Correlate and analyze
Correlation rules, statistical baselines, and machine learning link related events across sources. The SIEM scores risk and ties activity to specific users and hosts, turning scattered records into a single narrative.
Correlate
Example — Failed logins on one system plus data movement on another combine into one suspected account-compromise event.
Alert and prioritize
The platform de-duplicates noise, applies confidence and risk scoring, and raises prioritized alerts on a central dashboard. Playbooks and use-case logic decide who gets notified so the right analyst sees the right alert.
Alert
Example — A high-severity incident lands on the SOC queue while low-risk noise is suppressed.
Investigate and respond
Analysts pivot across timelines, entities, and lateral-movement paths to confirm scope. Where SOAR is integrated, playbooks can automate containment steps like blocking an IP or isolating a host.
Respond
Example — An analyst traces an alert back to a phishing email, then triggers a playbook to disable the affected account.
Report and retain
The SIEM stores normalized data for a defined retention period and generates compliance and forensic reports on demand. This record supports audits and post-incident review.
Report
Example — A monthly compliance report and a full event timeline are produced from stored data for auditors.
Use cases
Threat detection and monitoring
Security analysts, SOCContinuously watch activity across the environment and detect known and unknown threats by correlating signals from many sources.
Correlating identity, network, and endpoint logs to catch a phishing-driven account takeover in progress.
Benefit — Earlier detection of multi-stage attacks that single tools miss.
Incident investigation and forensics
Incident responders, DFIRReconstruct what happened during an incident by searching centralized, retained log data across systems.
Tracing an intrusion back through weeks of stored events to find the initial entry point.
Benefit — Faster, evidence-based investigation and clearer scope.
Compliance auditing and reporting
Compliance officers, businessAutomate the collection and reporting of security data needed for regulatory frameworks.
Generating PCI DSS, HIPAA, or GDPR reports on demand from stored events.
Benefit — Lower manual effort and reliable audit trails.
Insider threat and account-compromise detection
Security, MSPUse behavior analytics to spot misuse by authorized users or hijacked accounts.
UEBA flags impossible travel or unusual privilege use and raises a high-severity incident.
Benefit — Detection of threats that live inside the perimeter.
Log centralization and retention
IT admins, MSPConsolidate scattered logs into one searchable place and keep them for a defined period.
Bringing on-premises and multi-cloud logs into a single store for search and audit.
Benefit — One source of truth and simpler retention management.
Benefits
Centralized visibility
One console unifies alerts and data from across the whole environment, so teams stop stitching together separate tools by hand.
A single dashboard shows firewall, endpoint, and cloud events together.
Faster detection and response
Automated correlation and analytics cut mean time to detect (MTTD) and mean time to respond (MTTR) by offloading manual analysis.
A correlated alert replaces hours of manual log review.
Compliance support
Automated data collection and prebuilt reports help meet PCI DSS, HIPAA, GDPR, and SOX requirements with less effort.
On-demand audit reports generated from retained data.
Detection of advanced and unknown threats
Threat intelligence feeds and behavior analytics help surface insider threats, phishing, ransomware, and data exfiltration.
UEBA catches a compromised account that no static rule flagged.
Forensic and trend analysis
Retained, centralized data lets teams re-create past incidents and spot longer-term patterns.
Reviewing three months of events to find a slow, low-volume exfiltration.
Limitations
Cost scales with data volume
HighPricing is usually tied to how much data you ingest and store. High-volume environments can face large, hard-to-predict bills.
Workaround — Filter and route low-value logs, use tiered storage, and review ingestion regularly to control cost.
Tuning and false positives
HighOut of the box, a SIEM generates heavy noise. Without ongoing tuning, real threats get buried under false alarms.
Workaround — Invest in continuous rule tuning and use-case development; treat tuning as a permanent task.
Requires skilled staff and a process
HighA SIEM is only as good as the team using it. It needs analysts to review alerts and a SOC process to act on them.
Workaround — Staff a SOC, or use a managed security service provider (MSSP) to run the SIEM.
Detects, but doesn't prevent
MediumA SIEM raises alerts; it doesn't block attacks by itself. It complements, rather than replaces, endpoint and network defenses.
Workaround — Pair SIEM with EDR, firewalls, and SOAR for automated containment.
Deployment and integration complexity
MediumOnboarding sources, mapping data, and building correlation rules takes real time and expertise, especially in mixed environments.
Workaround — Phase the rollout by priority use cases and use prebuilt connectors and content packs.
Architecture
A SIEM is built as a pipeline. Data flows in from collectors, passes through ingestion and normalization, lands in storage, gets processed by a correlation and analytics engine, and surfaces on dashboards where analysts work. Response and automation sit alongside, often through SOAR. Deployments can be on-premises, cloud-native, or a managed service, but the logical stages stay the same.
Data collectors and connectors
Agents, forwarders, and APIs that pull logs and events from sources across the environment.
Syslog forwarders, cloud connectors, and endpoint agents.
Ingestion and normalization pipeline
Parses, timestamps, and rewrites raw records into a common schema, then enriches them with context.
Mapping a firewall log and an identity log to shared fields.
Storage and indexing
Holds normalized data in a searchable store for correlation, investigation, and retention.
A data lake or indexed log store sized for the retention window.
Correlation and analytics engine
Applies rules, baselines, UEBA, and machine learning to detect threats and score risk.
A rule that links failed logins to data exfiltration.
Dashboards and console
The central interface where analysts view alerts, triage incidents, and run queries.
A SOC dashboard with real-time visualizations and incident queues.
Response and automation (SOAR)
Runs playbooks to enrich, contain, or remediate, reducing manual effort and response time.
An automated playbook that blocks an IP range after a brute-force pattern.
Data flow
Log and event data moves left to right through the pipeline. Sources emit records that collectors forward into the SIEM. The ingestion layer normalizes and enriches each record, then writes it to storage. The correlation engine reads across stored events to detect patterns, scores them, and pushes prioritized alerts to the console. From there, analysts investigate, and response actions, manual or automated through SOAR, feed back into the environment.
Integrations: SOAR platforms for automated response, Threat intelligence feeds, EDR and XDR tools, Identity providers and directory services, Cloud platforms such as Azure, AWS, and GCP
Architecture limitations
Examples
Catching a brute-force attack through correlation
A SIEM receives thousands of failed inbound connection attempts on a remote-access port from a range of addresses.
Alone, each failed connection is noise. The SIEM correlates the volume and pattern into a single brute-force detection, enriches it with threat intelligence, and raises one incident instead of thousands of logs.
Spotting a compromised account with UEBA
A user appears to sign in from one country while also active locally moments later.
UEBA baselines normal behavior and flags the impossible-travel pattern as a deviation. The SIEM creates a high-severity incident and, through a SOAR playbook, forces re-authentication and disables the account pending review.
Producing a compliance report on demand
An auditor asks for evidence of who accessed sensitive data over the last quarter.
Because the SIEM retained and normalized access logs, it generates a prebuilt report from stored data rather than an analyst pulling logs from each system by hand.
Comparisons
SIEM vs SOAR vs SOAR
SIEM detects threats by collecting and correlating data; SOAR acts on them by automating response workflows. They're complementary, and modern SIEMs often integrate SOAR.
| Criterion | SIEM vs SOAR | SOAR |
|---|---|---|
| Primary job | Detection and analysis of security data | Orchestration and automation of response |
| Output | Prioritized alerts and reports | Automated playbooks and actions |
| Relationship | Feeds alerts into response | Consumes alerts to trigger response |
When to choose — Use both: SIEM for detection, SOAR for fast, consistent response.
SIEM vs XDR vs XDR
SIEM is source-agnostic and ingests almost any log for broad visibility and compliance. XDR is a more integrated stack focused on detection and response across endpoints, identity, email, and cloud, usually within one vendor's ecosystem.
| Criterion | SIEM vs XDR | XDR |
|---|---|---|
| Data scope | Any log source, very broad | Curated telemetry from integrated tools |
| Focus | Visibility, correlation, compliance | Detection and response depth |
| Setup | Flexible but more integration work | More turnkey within its ecosystem |
When to choose — Many organizations run both, with XDR feeding the SIEM for full-environment visibility.
SIEM vs plain log management vs Log management
Log management collects and stores logs. SIEM adds correlation, analytics, and real-time alerting on top of that data to detect threats.
| Criterion | SIEM vs plain log management | Log management |
|---|---|---|
| Goal | Threat detection and response | Collection, storage, and search |
| Analysis | Correlation, UEBA, and alerting | Basic search and retention |
When to choose — Choose SIEM when you need detection, not just storage; log management alone won't correlate threats.
Myths, corrected
Myth
A SIEM is a plug-and-play, set-and-forget solution.
Correction
A SIEM needs continuous tuning, use-case development, and staff to review alerts. Deployed with defaults, it produces heavy noise and misses real threats.
Why it happens: Marketing often implies instant value, and the setup wizard runs quickly, hiding the ongoing operational work.
Myth
A SIEM stops attacks on its own.
Correction
A SIEM detects and alerts; it doesn't block. Prevention still relies on firewalls, endpoint protection, and, for automated action, SOAR.
Why it happens: People conflate detection with prevention because both fall under 'security software'.
Myth
A SIEM replaces the SOC team.
Correction
A SIEM is a tool the team uses, not a substitute for analysts. Its output still needs human judgment to investigate and decide.
Why it happens: Automation and AI features get oversold as full replacements for people.
Myth
SIEM is only for large enterprises.
Correction
Cloud-native and managed SIEM options bring the technology within reach of smaller teams, often through an MSSP.
Why it happens: Early SIEMs were costly, on-premises deployments aimed at big organizations.
Practical implications
For admins
Expect real work onboarding log sources, mapping data, and tuning rules. Plan for ongoing maintenance, not a one-time install, and catalog your assets and log sources first.
For MSPs
SIEM is a common managed service. Running it well for clients means standardized use cases, tuned rules, and clear escalation, and it can be a strong recurring-revenue offering.
For business
SIEM supports risk reduction and compliance but carries real cost and staffing needs. Fund it as an ongoing program, not a product purchase.
For security
It's the backbone of the SOC, improving MTTD and MTTR when paired with good sources, tuning, and response processes. It complements EDR, XDR, and threat intelligence.
For end users
Mostly invisible, but SIEM-driven detection may trigger security actions like forced re-authentication or account lockout when behavior looks risky.
Cost impact
Cost is usually driven by data ingestion and storage volume, which can grow quickly. Budget for licensing plus the staff or MSSP needed to operate it.
Operational impact
SIEM centralizes detection but adds an operational commitment: continuous tuning, alert triage, and a response process are required to get value.
Decision guide
Use when
- You need centralized visibility across many systems and clouds
- You must meet compliance or audit reporting requirements
- You have, or can outsource, a team to review and act on alerts
- You want to detect multi-stage threats that span tools
Avoid when
- You have no capacity to review alerts or run a SOC process
- You only need log storage and search, not detection
- Your environment is tiny and adequately covered by simpler tools
Requirements
- Reliable log sources across the environment
- Skilled analysts or an MSSP to operate it
- Budget for ingestion, storage, and staffing
- A defined incident response process
Alternatives
- Managed SIEM through an MSSP for teams without a SOC
- XDR for integrated detection within one ecosystem
- Standalone log management when only storage and search are needed
Related terms
Security operations center (SOC)
The team and process, often running 24/7, that monitors and responds to security events, typically using a SIEM as its analytics backbone.
SOAR
Security orchestration, automation, and response: technology that automates response workflows through playbooks, often integrated with a SIEM.
UEBA
User and entity behavior analytics: baselines normal behavior and flags anomalies that may signal insider threats or compromised accounts.
XDR
Extended detection and response: an integrated stack that correlates telemetry across endpoints, identity, email, and cloud for detection and response.
Threat intelligence
External data about known threats and attack signatures that a SIEM uses to enrich and prioritize alerts.
MTTD and MTTR
Mean time to detect and mean time to respond: key metrics a SIEM aims to reduce.
Frequently asked questions
What does SIEM stand for?
SIEM stands for security information and event management. It combines security information management (SIM), which collects and stores log data, with security event management (SEM), which handles real-time monitoring and correlation. Gartner named the combined category in 2005.
What is the difference between SIEM and SOAR?
SIEM focuses on detection: it collects and correlates security data to raise alerts. SOAR focuses on response: it automates workflows to act on those alerts through playbooks. They're complementary, and many modern SIEMs include SOAR features.
Is SIEM the same as a SOC?
No. A SOC (security operations center) is the team and process that monitors and responds to threats. A SIEM is the main tool that SOC uses. The SIEM provides the analytics; the SOC provides the people and workflow.
Does a SIEM prevent cyberattacks?
Not by itself. A SIEM detects threats and raises alerts, but it doesn't block attacks. Prevention relies on controls like firewalls and endpoint protection, while automated containment usually comes from an integrated SOAR platform.
How does a SIEM work, in simple terms?
It collects logs from across your systems, translates them into a common format, correlates related events to find threats, and raises prioritized alerts. It also stores that data for investigation and compliance reporting.
Is SIEM only for large companies?
No. Early SIEMs were expensive on-premises deployments, but cloud-native and managed options now bring SIEM within reach of smaller teams, often delivered through a managed security service provider (MSSP).
What data sources does a SIEM collect from?
A SIEM ingests logs and events from endpoints, servers, applications, cloud workloads, identity systems, and network and security devices such as firewalls and antivirus. Broad coverage improves detection quality.
Why do SIEMs generate so many false positives?
Out of the box, correlation rules are generic and noisy. Reducing false positives takes continuous tuning, enrichment with context, and use-case development tailored to your environment. Tuning is an ongoing task, not a one-time step.
Conclusion
SIEM brings together log collection, normalization, correlation, alerting, and reporting so a security team can see and act on threats from one place. It grew from the pairing of SIM and SEM, and modern platforms add UEBA, SOAR, and machine learning. The payoff is centralized visibility and faster detection and response, but only if you tune it, staff it, and run a real process around it.
Main takeaway
If you're ready to act on SIEM alerts automatically, look at SOAR next. For hands-on setup, a tutorial on onboarding log sources or writing correlation rules is the logical follow-up.