What Is a VLAN (Virtual LAN)? Definition, How It Works, and Use Cases

- Level
- Beginner
- Reading time
- 19 min
- Concept
- Virtual LAN (VLAN)
- Last reviewed
- July 4, 2026
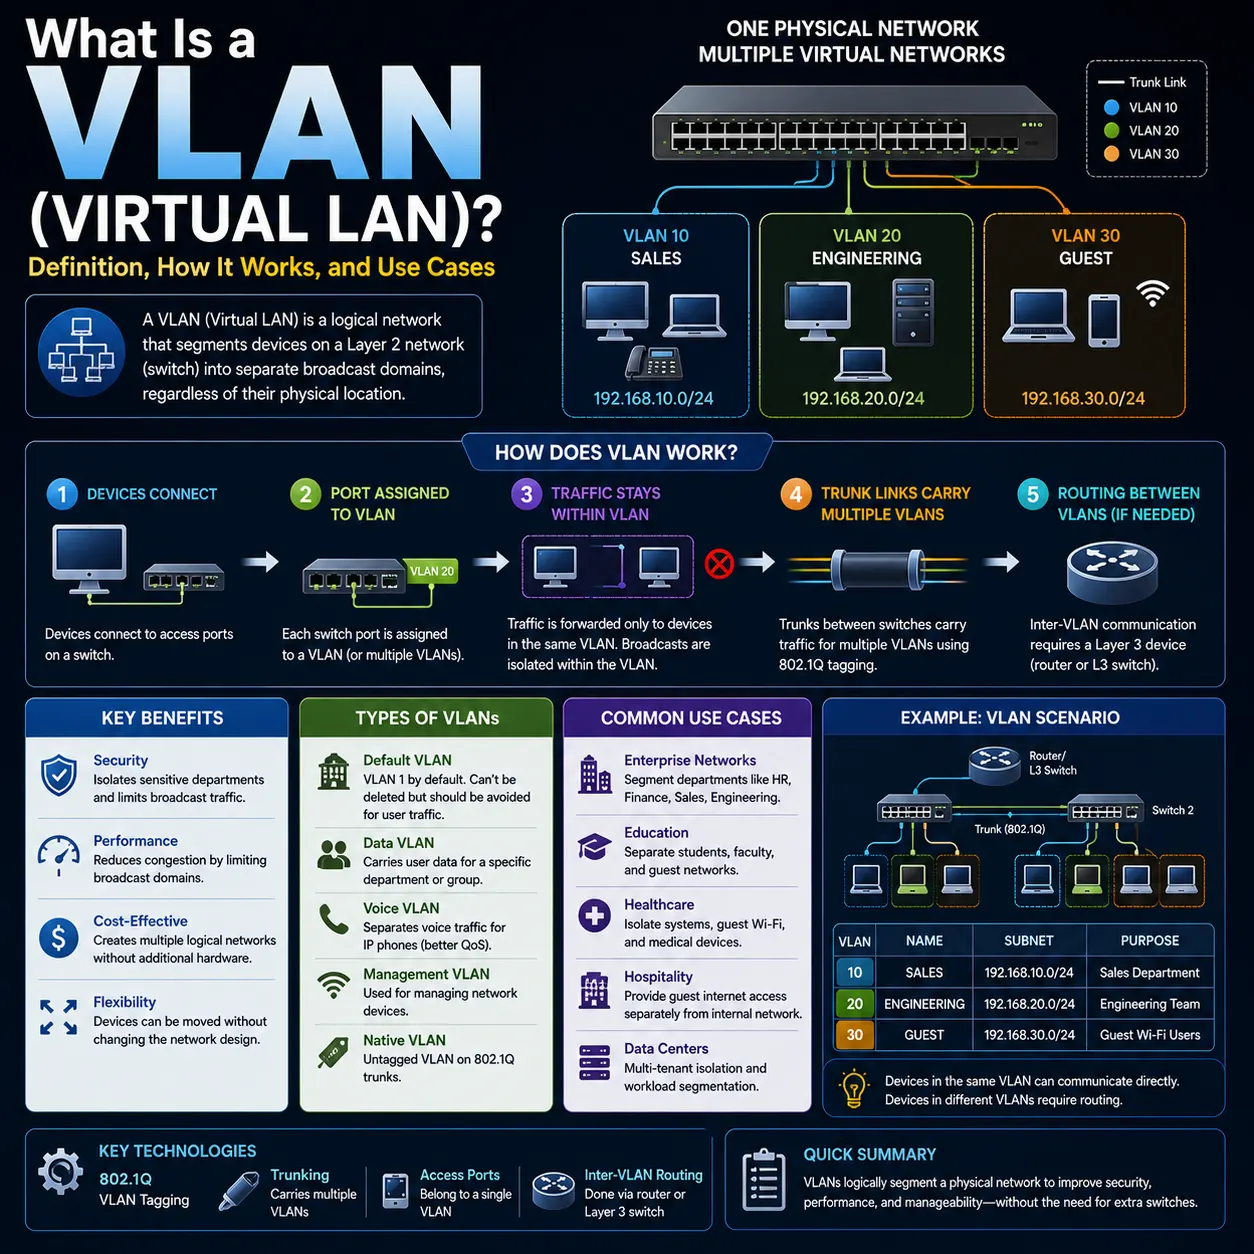
Table of contents
A VLAN (Virtual LAN) solves an everyday networking problem: how to create separate, secure network segments without rewiring the building. Rather than giving each department its own switches and cables, a VLAN uses software-defined boundaries to carve one physical network into multiple isolated broadcast domains. Standardized by IEEE 802.1Q in 1998, VLANs remain a cornerstone of network design - turning a single switch fabric into many logical networks, each with its own traffic scope and policies, spanning multiple switches or sites when needed.
Key takeaways
- A VLAN creates a separate broadcast domain in software on shared physical switches.
- IEEE 802.1Q adds a 4-byte tag with a 12-bit VLAN ID (up to 4,094 usable VLANs).
- Access ports carry one VLAN; trunk ports carry many tagged VLANs plus one untagged native VLAN.
- Devices in different VLANs communicate only via Layer 3 inter-VLAN routing.
- VLANs segment traffic but aren't a security boundary alone - VLAN hopping exploits weak defaults.
Quick explanation
In simple terms
A way to create separate networks in software on the same physical switches, so devices in one group can't directly talk to another group without a router.
Technical definition
A Layer 2 broadcast domain defined by IEEE 802.1Q VLAN tagging, where access ports carry a single untagged VLAN and trunk ports carry multiple tagged VLANs between switches, with inter-VLAN traffic requiring Layer 3 routing.
Analogy
A VLAN is like separate apartments in one building: each unit is a private space (broadcast domain), but they share the same building infrastructure (physical switches and cabling).
Definition
A VLAN (Virtual Local Area Network) is a logical grouping of network devices into a separate broadcast domain within shared physical switch infrastructure, created in software rather than by separate cabling.
A VLAN (Virtual Local Area Network) partitions a single physical switched network into multiple logical networks, each its own broadcast domain. Instead of using separate switches and cabling for each group, a VLAN uses switch configuration and frame tagging to keep traffic logically separate - and a VLAN can span multiple switches, floors, or sites. The mechanism is standardized by IEEE 802.1Q (ratified in 1998): a VLAN-aware switch inserts a 4-byte 802.1Q tag into the Ethernet frame carrying a 12-bit VLAN ID, which supports up to 4,094 usable VLANs. Frames stay within their VLAN unless a Layer 3 device explicitly routes between VLANs.
Why it matters
Core concepts
Broadcast domains and segmentation
A VLAN is a separate broadcast domain: broadcast/multicast/unknown-unicast traffic stays inside it.
In a flat network, every broadcast reaches every device, which wastes bandwidth and exposes traffic. A VLAN confines broadcast, multicast, and unknown-unicast flooding to the ports in that VLAN, so a broadcast storm or discovery traffic in one segment doesn't affect others. Segmentation is the core purpose of VLANs.
Example
A broadcast storm in the guest VLAN doesn't touch the server VLAN because they're separate broadcast domains.
Why it matters — Containing broadcast traffic is what improves performance and gives each segment its own scope.
IEEE 802.1Q tagging
A 4-byte tag inserted into the Ethernet frame identifies which VLAN it belongs to.
The 802.1Q tag is inserted after the source MAC address (before the EtherType field). It carries a 12-bit VLAN ID (allowing 4,094 usable VLANs) plus a 3-bit priority field (PCP) used for QoS. VLAN-aware switches add the tag on ingress and read it to keep frames within the correct VLAN; regular end-device frames are untagged.
Example
A frame entering the finance access port is tagged with VLAN 100 and only forwarded among VLAN 100 ports.
Why it matters — Tagging is the mechanism that lets a single physical link and switch fabric carry many separate VLANs.
Access ports vs trunk ports (and the native VLAN)
Access ports carry one VLAN untagged; trunk ports carry many VLANs tagged, with one untagged native VLAN.
An access port connects an end device and belongs to a single VLAN; frames on it are untagged. A trunk port connects switches (or switch-to-router/AP) and carries multiple VLANs, each tagged - except the native VLAN, which by convention travels untagged. On many switches the default native VLAN is VLAN 1, and leaving it that way is a security weakness (see misconceptions).
Example
A trunk between two switches carries VLANs 10, 20, and 30 tagged, with VLAN 99 as an unused native VLAN.
Why it matters — The access/trunk distinction and native-VLAN handling drive both connectivity and Layer 2 security.
VLAN table and forwarding
The switch tracks MAC-to-port mappings per VLAN and forwards only within the same VLAN.
A VLAN-aware switch maintains MAC address tables scoped per VLAN. It forwards a frame only to ports in the same VLAN as the source, and floods broadcast/unknown-unicast only within that VLAN. When a frame leaves through an access port to an end device, the tag is stripped.
Example
The switch forwards a VLAN 20 frame only among VLAN 20 ports, never leaking it into VLAN 10.
Why it matters — Per-VLAN forwarding is what enforces the logical separation at the hardware level.
Inter-VLAN routing
A Layer 3 device is required for devices in different VLANs to communicate.
Because VLANs are separate broadcast domains, traffic between them must pass through a Layer 3 device (a router or Layer 3 switch), which applies routing and can enforce access policies. Typically each VLAN maps to an IP subnet, and the L3 device provides the default gateway for each.
Example
A user VLAN reaches the server VLAN only through the core switch's routing, where an ACL controls what's allowed.
Why it matters — Inter-VLAN routing is where controlled connectivity and Layer 3 security policy are applied.
How it works
Assign ports to VLANs
Admins configure each switch port as an access port (one VLAN) or a trunk port (multiple VLANs).
Port assignment
Example — Port 5 is set as access VLAN 100 (finance).
Tag frames on ingress
When a frame enters an access port, the switch inserts an 802.1Q tag with that port's VLAN ID.
Tagging
Example — The finance PC's frame gets a VLAN 100 tag.
Look up the VLAN table
The switch consults its per-VLAN MAC table to decide where the frame may go, keeping it within the same VLAN.
Table lookup
Example — The switch finds the destination MAC on another VLAN 100 port.
Carry tagged frames across trunks
To reach another switch, frames traverse trunk ports that carry multiple VLANs, each keeping its tag (the native VLAN travels untagged).
Trunking
Example — VLAN 100 frames cross the inter-switch trunk still tagged.
Contain broadcasts, then strip the tag
Broadcast/unknown traffic floods only within the VLAN; when a frame exits to an end device via an access port, the tag is removed.
Contain + untag
Example — A VLAN 100 broadcast never reaches VLAN 200; the tag is stripped at delivery.
Route between VLANs at Layer 3
If devices in different VLANs must communicate, a Layer 3 device routes between them and can enforce policy.
Inter-VLAN routing
Example — The core switch routes and filters traffic from users to servers.
Use cases
Network segmentation and security zones
Security and network teamsIsolate sensitive systems from general traffic by placing them in dedicated VLANs, with routing/ACLs controlling access.
Separate VLANs for patient records, medical devices, guest WiFi, and admin systems in a hospital.
Benefit — Reduced exposure and clearer policy boundaries
Broadcast domain management
Network adminsSplit large networks so broadcast traffic stays local, improving performance.
A campus separates dorms, departments, and admin to contain broadcasts.
Benefit — Less congestion, better performance
QoS with voice VLANs
UC/network teamsPlace VoIP phones on a dedicated voice VLAN with higher priority so calls aren't degraded by data traffic.
Voice VLAN 150 prioritized over the data VLAN.
Benefit — Consistent call quality
Simplified moves, adds, and changes
IT operationsReassign a port's VLAN in software instead of recabling when people or devices move.
An employee relocates and their new port is set to their VLAN - no rewiring.
Benefit — Faster changes, lower cost
Multi-tenant isolation
Service providersGive each tenant dedicated VLANs on shared switching hardware.
A colo provider isolates customers with per-tenant VLANs.
Benefit — Isolation with shared infrastructure
Benefits
Segmentation without rewiring
Create isolated logical networks in software on existing physical infrastructure.
New department gets its own VLAN with no new cabling.
Better performance
Containing broadcast traffic per VLAN reduces congestion.
Broadcast storms stay within one segment.
Cost efficiency and flexibility
One physical network supports many logical ones, reconfigurable by software.
Reassign ports instead of buying separate switches.
Scalability
Up to 4,094 VLANs let networks grow without re-architecting the physical layer.
Add VLANs as the org grows.
Centralized, consistent management
Software-defined VLAN policies apply consistently across switches and sites.
Standard VLAN scheme pushed across the campus.
Limitations
Segmentation is not automatic security
HighVLANs isolate traffic but can be bypassed by VLAN hopping (switch spoofing via trunk negotiation, or double tagging via the native VLAN) when defaults aren't hardened.
Workaround — Disable dynamic trunk negotiation (DTP) and set unused ports to access mode, move the native VLAN off VLAN 1 to an unused ID, and specify explicit trunk VLAN lists.
Configuration complexity
MediumGood VLAN design needs planning; misconfiguration causes outages or security gaps.
Workaround — Standardize a numbering scheme, document port/VLAN/subnet maps, and use change control.
Inter-VLAN routing overhead
LowTraffic between VLANs must be routed, adding latency and a dependency on the L3 device.
Workaround — Use a capable Layer 3 switch and design VLAN/subnet boundaries around traffic patterns.
Trunk bottlenecks and single points of failure
MediumA trunk carrying many VLANs can become a chokepoint or failure point.
Workaround — Provide redundant trunks with LACP and STP for loop-free redundancy.
Troubleshooting complexity and limited mobility
LowIssues spanning VLANs and routing are harder to diagnose, and port-based VLANs limit device mobility.
Workaround — Use monitoring and, for mobility, dynamic VLAN assignment via 802.1X.
Architecture
A VLAN deployment consists of managed (VLAN-aware) switches with ports designated as access or trunk, the 802.1Q tag that identifies each frame's VLAN, per-VLAN forwarding tables, and a Layer 3 device for inter-VLAN routing. Optional pieces include dynamic VLAN assignment (802.1X), voice VLANs, and overlay technologies (VXLAN) for large-scale segmentation.
Managed switches
Create and enforce VLANs; tag/untag frames; forward per VLAN
Access-layer switches with 802.1Q support
Access and trunk ports
Access carries one VLAN to devices; trunk carries many VLANs between switches
Access VLAN 100 to a PC; trunk carrying 100/200/300
802.1Q tag
Identifies the VLAN (and priority) for each frame
12-bit VID + 3-bit PCP
Layer 3 device
Routes between VLANs and applies access policy
Core Layer 3 switch as default gateway per VLAN
Native VLAN and trunk config
Defines the untagged VLAN and permitted VLAN list on trunks
Native VLAN 99, explicit allowed list
Data flow
Frame enters an access port then the switch tags it with the VLAN ID; a per-VLAN table lookup forwards it within the VLAN (broadcasts contained); frames cross trunks between switches still tagged; the tag is stripped at the egress access port; and inter-VLAN traffic is routed by a Layer 3 device.
Integrations: 802.1X dynamic VLAN assignment, Voice VLAN for VoIP QoS, VXLAN overlay for large-scale/data-center segmentation
Architecture limitations
Examples
Separating finance from marketing
Finance and marketing share the same switches, and sensitive traffic shouldn't be visible across teams.
Placing each department in its own VLAN makes them separate broadcast domains; traffic only crosses via a routed boundary where ACLs apply.
Voice VLAN for VoIP quality
VoIP calls degrade when they compete with bulk data on the same segment.
A dedicated voice VLAN with higher 802.1p priority separates and prioritizes call traffic.
Comparisons
VLAN vs subnet vs IP subnet
A VLAN segments at Layer 2 (broadcast domains); a subnet divides Layer 3 IP address space. They're complementary - typically one VLAN maps to one subnet, with a Layer 3 device routing between them.
| Criterion | VLAN vs subnet | IP subnet |
|---|---|---|
| OSI layer | Layer 2 (data link) | Layer 3 (network) |
| What it divides | Broadcast domains | IP address space |
| Configured on | Switch ports (802.1Q) | Routers / L3 devices |
| Isolation type | Layer 2 separation | Layer 3 routing/policy |
When to choose — Use them together: a VLAN per subnet gives both Layer 2 isolation and Layer 3 control.
Learn moreVLAN vs VXLAN / SDN vs VXLAN / SDN overlay
Traditional VLANs are distributed, switch-configured, and capped at 4,094 segments; VXLAN/SDN overlays are centrally managed and scale to about 16 million segments across Layer 3, suited to large data centers and multi-tenant clouds.
| Criterion | VLAN vs VXLAN / SDN | VXLAN / SDN overlay |
|---|---|---|
| Scale | Up to 4,094 VLANs | ~16 million segments (24-bit VNI) |
| Control plane | Distributed, per-switch | Centralized controller/policy |
| Reach | Layer 2 domain | Overlay tunneled across Layer 3 |
| Best fit | Campus, branch, simple segmentation | Data center, cloud, multi-tenant |
When to choose — VLANs for campus/branch simplicity and proven reliability; VXLAN/SDN for data-center scale and mobility. Many networks use both.
Myths, corrected
Myth
A VLAN is a security boundary you can rely on by itself.
Correction
VLANs segment traffic but can be bypassed by VLAN hopping - switch spoofing (an attacker negotiating a trunk, e.g., via DTP) or double tagging (abusing an untagged native VLAN). Without hardening, Layer 2 isolation isn't guaranteed.
Why it happens: Segmentation looks like isolation, so people assume it enforces security on its own, overlooking insecure defaults.
Myth
A VLAN and a subnet are the same thing.
Correction
They operate at different layers: a VLAN is a Layer 2 broadcast domain, a subnet is a Layer 3 IP range. They usually map one-to-one but are configured and enforced differently.
Why it happens: Because a VLAN typically corresponds to a subnet, the two get conflated.
Myth
VLANs encrypt or protect the confidentiality of traffic.
Correction
VLANs provide separation, not encryption. Traffic on a trunk is still readable to anyone who can capture it; confidentiality requires encryption (e.g., MACsec/IPsec).
Why it happens: 'Isolation' is mistaken for 'protection,' but separation and encryption are different guarantees.
Myth
More VLANs always means a better, more secure network.
Correction
Over-segmentation adds management and troubleshooting overhead without proportional benefit. Each VLAN should serve a clear purpose and hold enough devices to justify it.
Why it happens: VLANs are cheap to create, so teams add them reflexively.
Practical implications
For admins
Plan a VLAN numbering scheme, use explicit trunk VLAN lists, harden the native VLAN, disable unused-port trunk negotiation, and document port/VLAN/subnet maps.
For MSPs
Standardize VLAN designs and Layer 2 hardening across clients, and monitor for misconfigurations and excessive broadcast.
For business
VLANs deliver segmentation and flexibility cheaply, but budget for design expertise and remember they support - not replace - a security strategy.
For security
Treat VLANs as one control among many: add DHCP snooping, dynamic ARP inspection, port security, and Layer 3 ACLs, and prevent VLAN hopping by hardening trunks and the native VLAN.
For end users
Impact is indirect: more reliable performance and appropriate access, with seamless moves when dynamic VLAN assignment is used.
Cost impact
VLANs themselves add no hardware cost on managed switches, but design, hardening, and Layer 3 routing capacity require investment in skills and equipment.
Operational impact
Introduces Layer 2 design and change-control practices (trunking, native VLAN, STP/LACP) that must be managed carefully.
Decision guide
Use when
- You need to segment departments, device types, or security zones
- You want to contain broadcast traffic or prioritize voice/critical traffic
- You need software-reconfigurable topology without recabling
Avoid when
- A tiny flat network where segmentation adds needless complexity
- You need massive multi-tenant overlays across data centers (use VXLAN)
- You expect VLANs alone to provide confidentiality or complete security
Requirements
- Managed switches supporting 802.1Q
- A Layer 3 device for inter-VLAN routing
- Layer 2 hardening (native VLAN, trunk config, DHCP snooping/DAI)
Alternatives
- Physical network separation (air-gapped)
- VXLAN / SDN overlays for large-scale segmentation
- Private VLANs for isolation within a VLAN
Related terms
The standard defining VLAN tagging on Ethernet.
Trunk port
A switch port carrying multiple tagged VLANs between switches.
Access port
A switch port carrying a single untagged VLAN to an end device.
Native VLAN
The one VLAN sent untagged on a trunk; a common hardening target.
Inter-VLAN routing
Layer 3 routing that lets different VLANs communicate.
VXLAN
An overlay that scales segmentation to ~16 million segments over Layer 3.
Frequently asked questions
What is a VLAN in simple terms?
A VLAN (Virtual LAN) is a way to create separate network groups in software on the same physical switches. Devices in different VLANs can't communicate directly without a router, even if they plug into the same switch.
What is a VLAN used for?
Mainly network segmentation and security zoning, broadcast-domain control for performance, QoS (like a dedicated voice VLAN), simplified moves/adds/changes, and multi-tenant isolation on shared hardware.
Is a VLAN the same as a subnet?
No. A VLAN is a Layer 2 broadcast domain; a subnet is a Layer 3 IP range. They usually map one-to-one and work together, with a Layer 3 device routing between VLANs/subnets.
How many VLANs can I create?
IEEE 802.1Q supports up to 4,094 usable VLANs (IDs 1-4094, some reserved). Practical limits depend on your switch hardware and design. For far larger scale, VXLAN supports about 16 million segments.
Do I need special equipment for VLANs?
Yes - managed switches that support 802.1Q. Unmanaged switches can't create or manage VLANs. Inter-VLAN communication also needs a router or Layer 3 switch.
Are VLANs secure?
VLANs segment traffic but aren't a security boundary by themselves. VLAN hopping (switch spoofing or double tagging) can bypass isolation if defaults aren't hardened. Disable trunk negotiation on access ports, move the native VLAN off VLAN 1, use explicit trunk VLAN lists, and add DHCP snooping and dynamic ARP inspection.
What's the difference between a VLAN and VXLAN?
VLANs are switch-configured Layer 2 segments capped at 4,094 and best for campus/branch. VXLAN is a centrally managed overlay tunneled over Layer 3 that scales to ~16 million segments, suited to data centers and multi-tenant clouds. Many networks use both.
Conclusion
A VLAN logically groups devices into separate broadcast domains on shared physical switches using IEEE 802.1Q tagging. Access ports carry one VLAN, trunk ports carry many (with one untagged native VLAN), forwarding stays within each VLAN, and a Layer 3 device routes between them. VLANs deliver segmentation, performance, flexibility, and scalability - differing from subnets (Layer 3) and VXLAN (large-scale overlay).
Main takeaway
Read an explainer on subnetting or VXLAN to go deeper, or a tutorial on configuring 802.1Q trunks and inter-VLAN routing for hands-on practice.