What Is Windows Event ID 4625? Failed Logon Monitoring and Attack Detection Explained

- Level
- Beginner
- Reading time
- 12 min
- Concept
- Windows Event ID 4625
- Last reviewed
- July 19, 2026
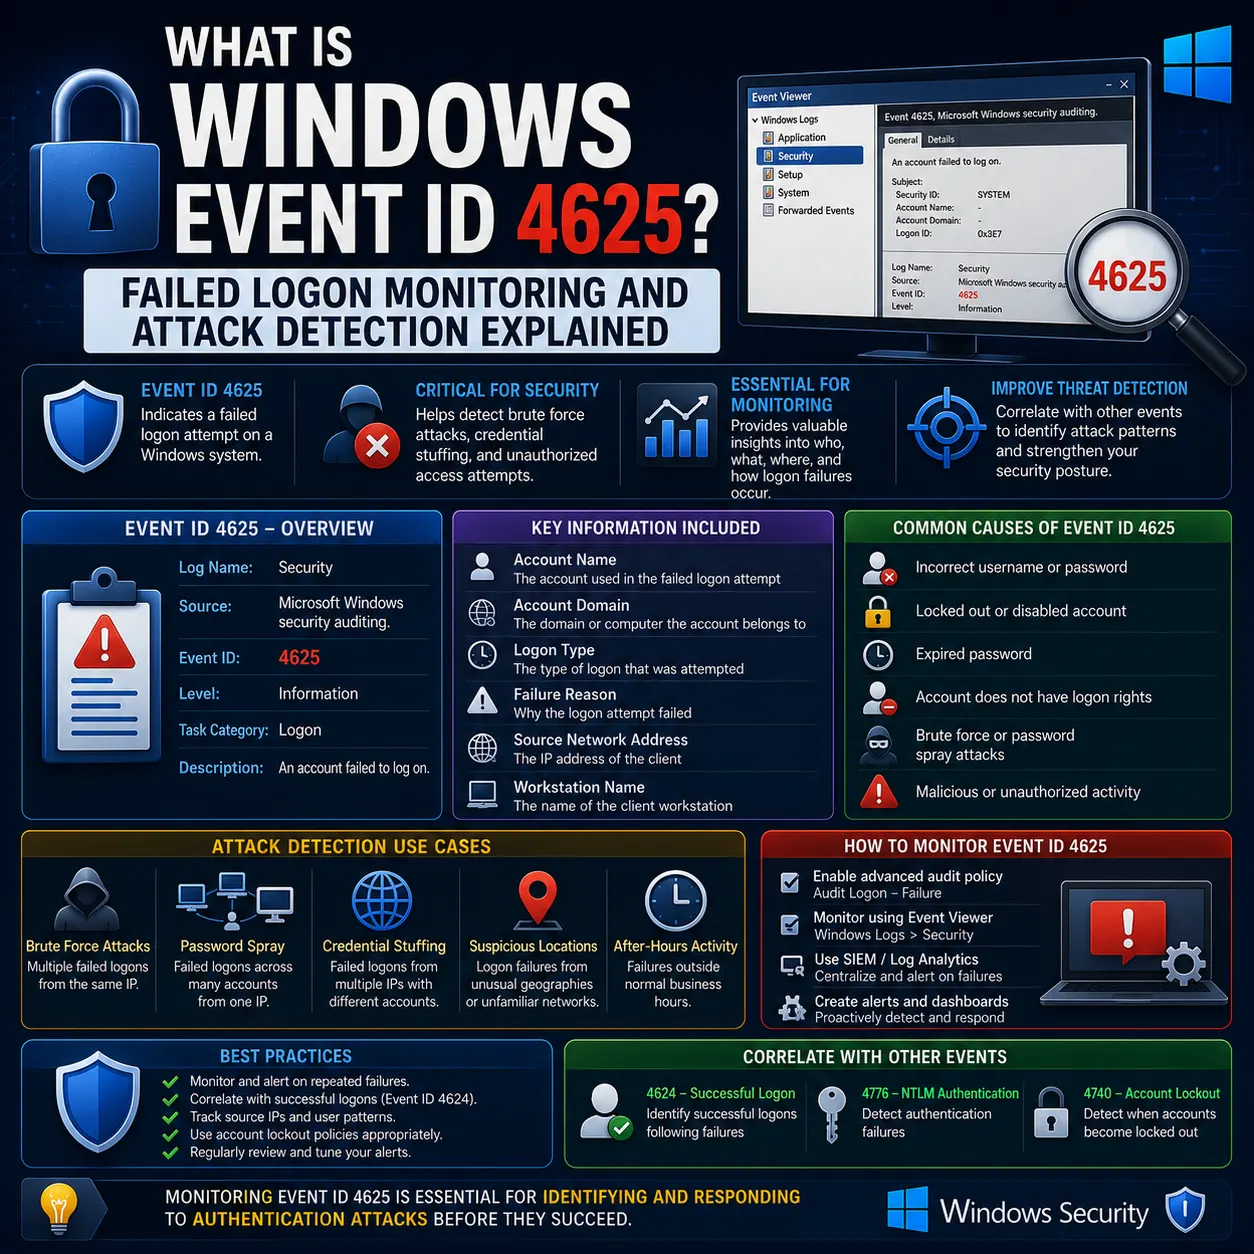
Table of contents
Event ID 4625 fires whenever a logon attempt fails on a Windows system. The event captures over 20 fields of forensic data: the account name, the source IP, the logon type, and a Sub Status code that maps to the exact reason for failure. It's the primary detection signal for brute-force attacks, password spraying, credential stuffing, and account lockout troubleshooting.
Key takeaways
- Event 4625 fires for every failed logon attempt on a Windows system, regardless of logon type.
- The Sub Status code pinpoints the exact failure: 0xC000006A (wrong password), 0xC0000064 (unknown user), 0xC0000234 (locked out).
- Logon Type identifies the method: Type 2 (interactive/console), Type 3 (network/SMB), Type 10 (RDP).
- The Source Network Address field reveals where the attempt came from, critical for brute-force detection.
- Requires the Audit Logon policy to be enabled for failure events.
Quick explanation
In simple terms
Event ID 4625 is the Windows Security log entry generated when someone fails to log in. It records the account name, where the attempt came from, what type of login was tried, and exactly why it failed.
Technical definition
Event 4625 is a failure audit event from the Microsoft-Windows-Security-Auditing provider. It's generated by the Local Security Authority (LSA) on the target machine for failed interactive, network, batch, service, and remote interactive logons. Key fields: TargetUserName, TargetDomainName, LogonType (2/3/4/5/10), Status/SubStatus (NTSTATUS codes), IpAddress, IpPort, LogonProcessName, AuthenticationPackageName.
Analogy
Think of Event 4625 like a security camera at a locked door. Every time someone tries to enter and fails, the camera records who they claimed to be, where they came from, and why the door wouldn't open (wrong key, expired badge, revoked access). A few failed entries per day is normal. Dozens from the same person or location in minutes is a break-in attempt.
Definition
Event ID 4625 is the Windows Security log entry generated when a logon attempt fails. It records the target account, source IP, logon type, and a Sub Status code identifying the exact failure reason.
Event ID 4625 is generated by the Microsoft-Windows-Security-Auditing provider on any Windows system (workstations, member servers, domain controllers) when a logon attempt fails. The Local Security Authority (LSA) evaluates the credentials and logs the failure with detailed forensic data.
The event includes Subject information (the process that initiated the logon), Logon Information (Logon Type: 2=Interactive, 3=Network, 4=Batch, 5=Service, 7=Unlock, 8=NetworkCleartext, 9=NewCredentials, 10=RemoteInteractive, 11=CachedInteractive), Account For Which Logon Failed (TargetUserName, TargetDomainName, SID), Failure Information (Status and SubStatus NTSTATUS codes, Failure Reason description), Network Information (source IP, port, Workstation Name), and Authentication Information (Logon Process, Authentication Package, Transited Services, Package Name, Key Length).
The Sub Status code is the most forensically valuable field: 0xC000006A = wrong password, 0xC0000064 = user doesn't exist, 0xC0000072 = account disabled, 0xC0000234 = account locked out, 0xC0000193 = account expired, 0xC000006F = outside allowed logon hours, 0xC0000071 = password expired. Per Microsoft documentation, the event requires the 'Audit Logon' advanced audit policy to be enabled for Failure events.
Why it matters
Core concepts
Sub Status Codes and Failure Reasons
The Sub Status field contains an NTSTATUS code that maps to the exact reason the logon failed.
Key codes for security monitoring: 0xC000006A = wrong password (the brute-force indicator), 0xC0000064 = unknown username (reconnaissance/enumeration indicator), 0xC0000072 = account disabled, 0xC0000234 = account locked out, 0xC0000193 = account expired, 0xC000006F = outside allowed logon hours, 0xC0000071 = password expired. The Sub Status is more specific than the Status field; always check Sub Status first.
Example
Sub Status 0xC000006A means the password was wrong. Sub Status 0xC0000064 means the username doesn't exist in the system or domain. Sub Status 0xC0000234 means the account is locked out.
Why it matters — The Sub Status code drives both troubleshooting (is it an expired password or a locked account?) and security detection (is it brute-force or enumeration?).
Logon Types: Identifying the Attack Vector
The Logon Type field indicates how the logon was attempted, revealing the attack vector or access method.
Common Logon Types in 4625 events: Type 2 (Interactive) = console logon, someone at the keyboard. Type 3 (Network) = SMB, mapped drives, IIS, accessing shared resources. Type 5 (Service) = Windows service failed to start with its credentials. Type 7 (Unlock) = workstation unlock failure. Type 10 (RemoteInteractive) = RDP/Terminal Services. Type 11 (CachedInteractive) = cached credentials used offline. Type 3 and Type 10 from external IPs are the most security-relevant.
Example
Logon Type 3 from an external IP = network-based attack (SMB, mapped drives). Logon Type 10 from an unknown IP = RDP brute-force. Logon Type 2 from the local console = someone physically at the machine.
Why it matters — Logon Type tells you how the attacker tried to get in, which determines the appropriate response (block RDP? restrict SMB? check physical access?).
Attack Pattern Detection: Brute-Force, Spray, and Stuffing
Brute-force, password spraying, and credential stuffing each produce distinct 4625 patterns.
Brute-force: many failures from one source against one account. Build SIEM rules: >10 failures from one IP in 5 minutes. Password spray: one or two failures per account across many accounts, staying below lockout thresholds. Detect by grouping by source IP and counting unique TargetUserName values. Credential stuffing: failures with valid-looking usernames from distributed IPs (often Sub Status 0xC000006A). Detect by correlating across time and looking for known-compromised credential patterns. Enumeration: bursts of Sub Status 0xC0000064 (unknown username), indicating the attacker is testing which accounts exist.
Example
Brute-force: 50x 4625 from one IP against one account in 5 minutes (Sub Status 0xC000006A). Password spray: 1x 4625 per account across 200 accounts from one IP. Credential stuffing: 4625 events with varied usernames and passwords from many IPs.
Why it matters — Each attack type requires a different detection rule. A brute-force threshold alert won't catch a password spray that stays below lockout limits.
Benefits
Primary signal for credential attack detection
4625 fires for every failed logon with source IP, account name, logon type, and exact failure reason. No other event provides this level of detail.
After a breach, investigators filter 4625 events by source IP to build the attacker's timeline: when they started, which accounts they targeted, and when they succeeded (correlate with 4624).
Fast help desk troubleshooting
Sub Status 0xC000006A, 0xC0000072, 0xC0000234, and 0xC0000071 map directly to specific account issues, saving troubleshooting time.
User calls help desk: 'I can't log in.' Admin filters 4625 for the username, sees Sub Status 0xC0000234 = account locked out. Immediate resolution.
Compliance audit trail
SOX, HIPAA, PCI-DSS, and ISO 27001 require logging of failed authentication attempts. 4625 events provide the audit trail.
During a PCI-DSS audit, the assessor asks for evidence of failed logon monitoring. The admin exports 4625 events from the SIEM with alerting rules.
Limitations
Logged on the target machine, not the source
Medium4625 fires on the machine where the logon was attempted. For domain logons, it fires on the DC that processed the request, not the client. For local logons, it fires on the target machine.
Workaround — Collect 4625 events from all DCs and member servers via WEF or SIEM agents. Don't rely on a single machine's logs.
Source IP may be missing for some logon types
MediumNetwork logon failures (Type 3) for NTLM authentication may show '-' or '127.0.0.1' as the source IP instead of the actual client IP.
Workaround — Cross-reference with Event 4776 (NTLM credential validation on DC) which often has better source workstation info. Also check the WorkstationName field.
High noise from legitimate failures
LowLegitimate scenarios like expired passwords, service account credential rotations, and scheduled tasks with stale credentials generate 4625 noise.
Workaround — Baseline normal failure patterns. Exclude known service accounts and expected patterns from alerting. Focus detection on external IPs, off-hours, and unknown accounts.
Myths, corrected
Myth
Event 4625 only fires on domain controllers
Correction
4625 fires on any Windows machine where a logon attempt fails: workstations, member servers, and domain controllers. For interactive logons, it fires on the target machine. For network logons to a DC, it fires on the DC.
Why it happens: Admins look for 4625 only on DCs and miss failed RDP or SMB logons on member servers.
Myth
A single 4625 event means an attack
Correction
Single 4625 events are usually users mistyping passwords or services with stale credentials. Attacks show patterns : clusters of failures from one IP, sequential account targeting, or high-frequency failures in short time windows.
Why it happens: Alert fatigue from threshold rules set too low (e.g. alert on 1 failure).
Myth
Event 4625 shows the password that was used
Correction
Windows never logs the attempted password in 4625 events. The event records only the target account name, source IP, logon type, and failure reason. Passwords are hashed during authentication and never written to the Security log.
Why it happens: Admins expect full forensic detail, but logging passwords would be a security risk itself.
Practical implications
For admins
Enable Audit Logon (Failure) on all systems. Set Security log to 100+ MB. Build PowerShell scripts grouping 4625 by IpAddress and TargetUserName. Correlate with 4624 (success) and 4740 (lockout) for full context.
For MSPs
Include 4625 monitoring in every client's security stack. Build standardized SIEM rules: brute-force threshold (>10 failures/IP/5min), password spray (>5 unique accounts/IP/10min), and enumeration (>5 events with Sub Status 0xC0000064/IP/5min).
For business
4625 monitoring directly supports compliance (SOX, HIPAA, PCI-DSS, ISO 27001). It reduces incident response time by providing immediate forensic data on failed access attempts.
For security
Build layered detection: threshold rules for brute-force (Sub Status 0xC000006A clusters), unique-account-count rules for password spray, 0xC0000064 burst rules for enumeration. Correlate 4625 with 4624 to detect successful compromise after failed attempts. Monitor Logon Type 10 from external IPs for RDP attacks.
Decision guide
Use when
- You need to detect brute-force attacks, password spraying, or credential stuffing.
- Help desk needs to diagnose why a user can't log in.
- Compliance requires logging all failed authentication attempts.
Avoid when
- You only need Kerberos authentication monitoring (use Event 4768/4771 instead).
- You're looking for successful logons (use Event 4624).
Requirements
- Audit Logon policy enabled for Failure events on all target systems.
- Centralized log collection (WEF or SIEM) for complete coverage.
- Sufficient Security log size (100+ MB) to avoid event loss.
Alternatives
- Event 4768/4771 for Kerberos-specific authentication failures on domain controllers.
- Event 4776 for NTLM credential validation failures (often has better source workstation info).
- Event 4740 for account lockout events specifically.
Frequently asked questions
When should I be concerned about 4625 events?
Be concerned when you see 5+ failures from the same source IP in 10 minutes, failures against admin or service accounts, failures from external IPs, or sequential failures across multiple accounts from one source (password spray). Single isolated failures are usually users mistyping passwords.
What do the Sub Status codes mean?
The key codes: 0xC000006A = wrong password, 0xC0000064 = user doesn't exist, 0xC0000072 = account disabled, 0xC0000234 = account locked out, 0xC0000193 = account expired, 0xC000006F = outside allowed hours, 0xC0000071 = password expired. Always check Sub Status, not just Status.
How do I tell apart user errors from attacks?
Legitimate errors: sporadic, internal IPs, Sub Status 0xC000006A, during business hours. Attacks: rapid clusters, external IPs, targeting admin accounts, sequential targeting of multiple accounts, or bursts of 0xC0000064 (username enumeration).
How do I enable 4625 logging?
Enable Audit Logon for Failure events: auditpol /set /subcategory:"Logon" /failure:enable. For domain-wide, use Group Policy: Computer Configuration > Advanced Audit Policy Configuration > Logon/Logoff > Audit Logon = Failure. Also enable Audit Account Lockout.
Does 4625 only fire on domain controllers?
No. 4625 fires on any Windows machine where a logon fails: workstations (interactive, RDP), member servers (SMB, services), and domain controllers (network logons). Collect from all systems for complete visibility.
Does 4625 show the password that was tried?
No. Windows never logs the attempted password. The event records the target account, source IP, logon type, and failure reason. Passwords are hashed during authentication and never written to the Security log.
Conclusion
Event ID 4625 logs every failed logon on Windows with the account name, source IP, Logon Type, and Sub Status code. Sub Status tells you exactly why it failed (wrong password, unknown user, locked out, expired). Logon Type tells you how (console, network, RDP). Detection rules should target clusters by source IP, unique account counts per IP (password spray), and Sub Status 0xC0000064 bursts (enumeration).
Main takeaway
Look into Event 4624 (successful logon, the success counterpart), Event 4740 (account lockout), Event 4768 (Kerberos TGT request), and Event 4776 (NTLM credential validation) to build a complete authentication monitoring strategy.