What Is Windows Event ID 4728? Active Directory Group Membership Auditing Explained

- Level
- Intermediate
- Reading time
- 12 min
- Concept
- Windows Event ID 4728
- Last reviewed
- July 18, 2026
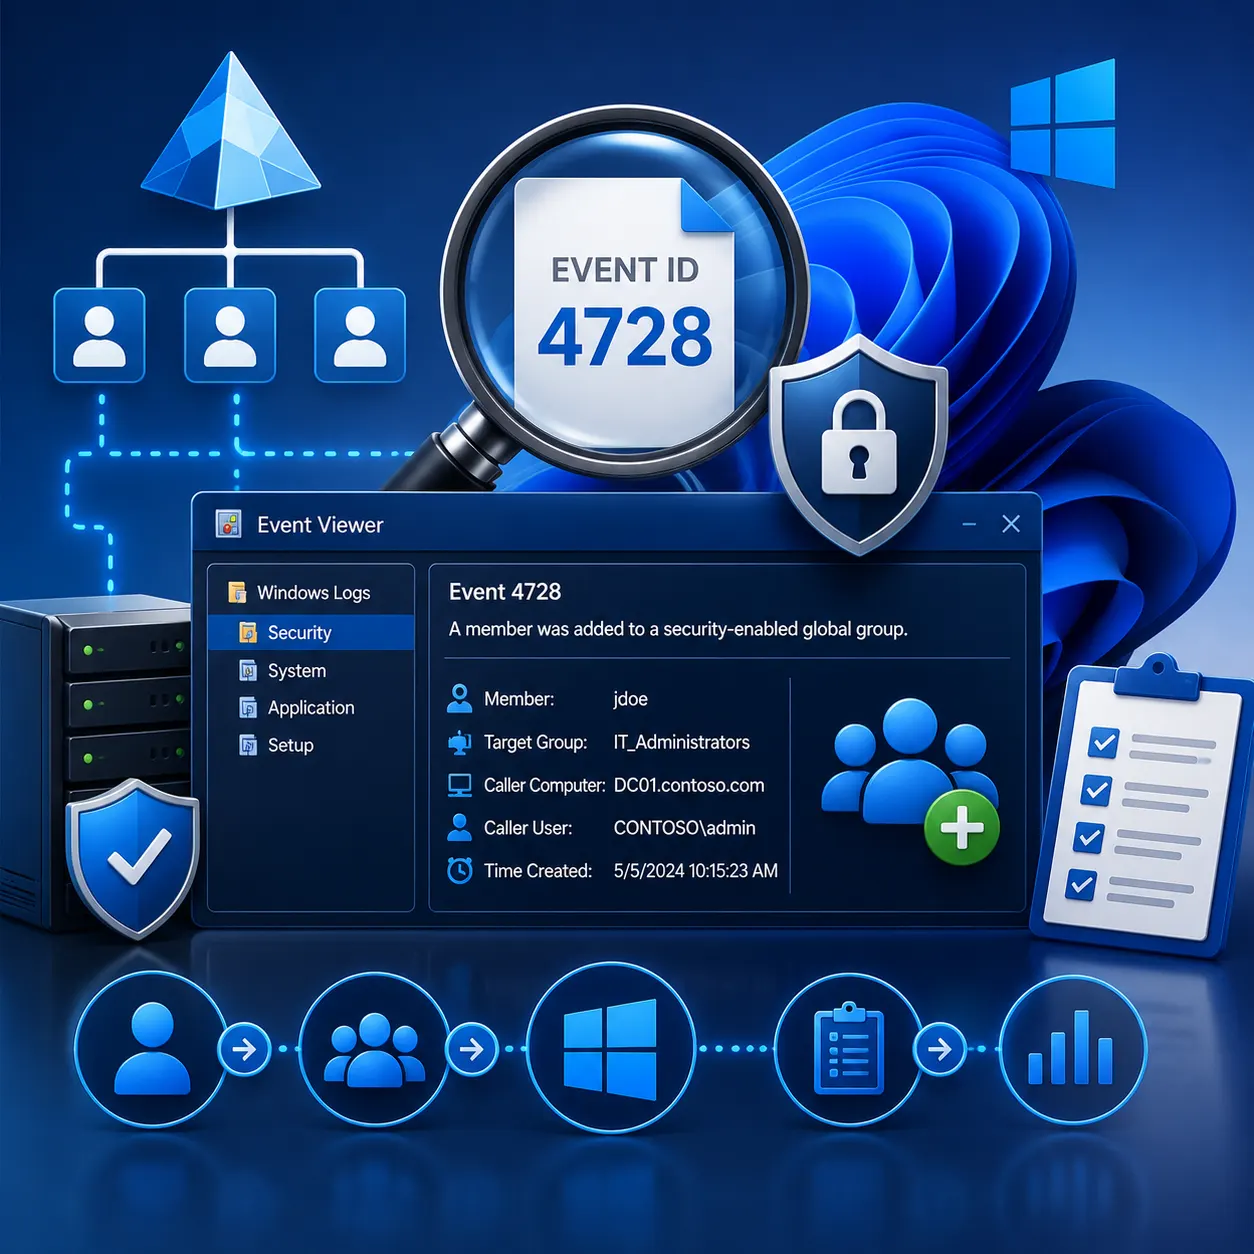
Table of contents
Event ID 4728 fires on Active Directory domain controllers every time a member is added to a security-enabled global group. Per Microsoft's audit policy documentation, this event tracks one of the most security-sensitive operations in AD: changing who has access to domain-wide resources.
Key takeaways
- Event 4728 logs when any account is added to a global security group in AD.
- It only fires on domain controllers, not member servers or workstations.
- The event requires the Audit Security Group Management policy to be enabled.
- It captures who made the change, which account was added, and which group was modified.
- Attackers target this event path for privilege escalation (MITRE T1098).
Quick explanation
In simple terms
Event 4728 is a Windows Security log entry that records when someone adds a user, computer, or group to a global security group in Active Directory.
Technical definition
A success audit event (Event ID 4728) generated by the Microsoft-Windows-Security-Auditing provider on domain controllers. It fires under the Account Management task category, subcategory Security Group Management, when a principal is added to a group with groupType containing SECURITY_ENABLED and GROUP_SCOPE_GLOBAL flags.
Analogy
Think of Event 4728 like a building's access log entry that records each time someone is given a new master key. The log doesn't prevent the key from being given, but it records who authorized it, who received it, and when.
Definition
Event ID 4728 is the Windows Security log entry generated whenever a user, computer, or group account is added to a security-enabled global group in Active Directory. It's logged on domain controllers under the Security Group Management audit category.
Event ID 4728 is a success audit event produced by the Microsoft-Windows-Security-Auditing provider on domain controllers. It fires each time an Active Directory principal (user, computer, or group) is added to a global security group. The event captures four data blocks: Subject (who performed the change), Member (the account added), Group (the target group's name, domain, and SID), and Additional Information (privileges used and logon session ID). Because global security groups can be granted permissions across any trusting domain, monitoring this event is central to detecting privilege escalation, enforcing least-privilege policies, and meeting compliance mandates like SOX, HIPAA, and PCI-DSS.
Why it matters
Core concepts
Security-Enabled Global Groups
A security-enabled global group is an AD group that can be assigned permissions and whose members must belong to the same domain.
Active Directory has two group purposes: security and distribution. Distribution groups are for email lists and can't control access. Security groups can be assigned permissions on resources. The "global" scope means the group can be granted access in any trusting domain but only contains members from its own domain. Event 4728 fires only for this specific combination, not for distribution groups (Event 4753) or local groups (Event 4732).
Example
Domain Admins, DNS Admins, and Group Policy Creator Owners are all security-enabled global groups.
Why it matters — Because global security groups control domain-wide access, any membership change is a potential privilege escalation.
Audit Security Group Management Policy
The Windows advanced audit policy setting that controls whether Event 4728 (and related events) are generated.
Event 4728 only fires when the Audit Security Group Management policy is enabled for Success events. This setting lives under Computer Configuration > Policies > Windows Settings > Security Settings > Advanced Audit Policy Configuration > Account Management. Without it, group changes happen silently. Per Microsoft Learn, this policy covers Events 4727-4737, 4754-4758, and 4764.
Example
Enable via Group Policy: set Audit Security Group Management to Success under Advanced Audit Policy Configuration.
Why it matters — If this policy isn't enabled, administrators have zero visibility into who is modifying security group memberships.
Event Data Structure
Event 4728 contains four data blocks: Subject, Member, Group, and Additional Information.
The Subject block identifies the account that performed the action (Security ID, Account Name, Domain, Logon ID). The Member block shows the account being added (SID and distinguished name). The Group block provides the target group's SID, name, and domain. Additional Information includes the privileges used and logon session. Per Microsoft, Event 4728 uses the same field structure as Event 4732 (local groups), only the group scope differs.
Example
Subject: CORP\AdminUser, Member: CORP\JSmith, Group: CORP\Domain Admins, Privileges: -
Why it matters — Understanding these fields is essential for building SIEM rules and forensic queries.
How it works
Group membership change is initiated
An administrator, script, or automated system issues an LDAP modify operation to add a member to a global security group in Active Directory. This can happen through ADUC, PowerShell's Add-ADGroupMember, or any LDAP-capable application.
Initiate
Example — An IT admin runs Add-ADGroupMember -Identity 'Domain Admins' -Members 'JSmith' in PowerShell.
Domain controller processes the change
The domain controller that receives the request validates permissions, applies the change to the AD database (NTDS.dit), and prepares the security audit event. The change is then replicated to other domain controllers.
Process
Example — The DC verifies the admin has write access to the group object and commits the change.
Event 4728 is written to the Security log
If the Audit Security Group Management policy is enabled for Success events, the DC writes Event ID 4728 to its local Security log. The event captures the Subject, Member, Group, and Additional Information fields.
Log
Example — Event Viewer > Windows Logs > Security shows the 4728 entry with full forensic details.
SIEM and monitoring tools pick up the event
Windows Event Forwarding, SIEM agents, or log collectors ingest the event. Rules and alerts evaluate whether the change matches suspicious patterns, such as additions to Domain Admins outside business hours or by non-admin accounts.
Alert
Example — A Sentinel KQL rule triggers an alert because a user was added to Domain Admins at 3 AM.
Use cases
Privilege escalation detection
SOC analysts, security engineersMonitor for unauthorized additions to high-privilege groups like Domain Admins, Enterprise Admins, or Schema Admins.
A SIEM rule alerts when Event 4728 fires for Domain Admins and the Subject account isn't in the approved admin list.
Benefit — Catches attackers and insiders who try to elevate their own or an accomplice's privileges.
Compliance auditing
IT admins, compliance officersGenerate reports on all security group membership changes for SOX, HIPAA, PCI-DSS, or internal audit requirements.
A scheduled PowerShell report exports all Event 4728 entries from the past quarter for the compliance team.
Benefit — Provides documented evidence that access changes are tracked and reviewed.
Incident forensics
Incident responders, forensic analystsTrace the timeline of account privilege changes during or after a security incident.
After detecting a breach, analysts correlate Event 4728 with logon events (4624) to map the attacker's lateral movement.
Benefit — Reconstructs exactly when and how an attacker gained elevated access.
Benefits
Real-time visibility into privilege changes
Event 4728 fires immediately when a group membership change occurs, giving security teams a near-instant signal.
A SIEM alert triggers within seconds of an unauthorized Domain Admins addition.
Complete forensic trail
Each event records who made the change, which account was added, and which group was modified, with SIDs and timestamps.
Investigators trace a compromised service account's privilege escalation path using 4728 entries.
Compliance evidence
Archived 4728 events satisfy audit requirements for frameworks like SOX, HIPAA, and PCI-DSS.
Quarterly compliance reports pull all 4728 events to show security group changes were monitored.
Limitations
Only fires on domain controllers
MediumEvent 4728 is logged only on the DC that processes the group change.
Workaround — Use Windows Event Forwarding or a SIEM agent on every domain controller.
Requires explicit audit policy
HighWithout Audit Security Group Management enabled, no Event 4728 is generated.
Workaround — Deploy the advanced audit policy via Group Policy to all DCs and verify with auditpol /get.
No context on legitimacy
MediumThe event records the change but doesn't indicate whether it was authorized.
Workaround — Correlate 4728 with change management records and approved admin account lists.
Myths, corrected
Myth
Event 4728 fires on member servers and workstations
Correction
Event 4728 is generated only on domain controllers , per Microsoft's audit documentation. Member servers never produce this event.
Why it happens: Confusion with Event 4732 which fires for local group changes on any machine.
Myth
Event 4728 is enabled by default
Correction
The Audit Security Group Management policy must be explicitly enabled. Default installations don't always log this event.
Why it happens: Admins assume all security events are logged automatically.
Myth
Event 4728 covers distribution groups too
Correction
Event 4728 only fires for security-enabled groups. Distribution group changes generate Event 4753.
Why it happens: Both group types appear in ADUC and the visual distinction isn't always obvious.
Practical implications
For admins
Enable Audit Security Group Management on all DCs via Group Policy. Centralize Security logs using Windows Event Forwarding. Set up baseline reports for normal group change patterns.
For MSPs
Include Event 4728 monitoring in every AD-connected client's security stack. It's a quick win for demonstrating security value and meeting compliance requirements.
For business
Event 4728 monitoring directly supports compliance mandates (SOX, HIPAA, PCI-DSS) that require tracking privileged access changes. It also reduces incident response time by providing immediate alerts.
For security
Build detection rules around high-value groups (Domain Admins, Enterprise Admins, Schema Admins, DNSAdmins). Correlate with logon events (4624) and account creation (4720) for attack chain detection. The pattern 4720+4728 within 60 seconds is a high-confidence backdoor indicator.
For end users
End users don't interact with Event 4728 directly, but they benefit from the security monitoring it enables, which protects against unauthorized access to shared resources.
Operational impact
High-volume AD environments can generate thousands of 4728 events daily from automated provisioning. Tune SIEM rules to focus on sensitive groups and unusual patterns to avoid alert fatigue.
Decision guide
Use when
- You run Active Directory and need to monitor privilege changes.
- Compliance frameworks require tracking security group membership modifications.
- Your security team needs to detect privilege escalation attacks.
Avoid when
- You only need to monitor distribution group changes (use Event 4753 instead).
- You need to track local group changes on member servers (use Event 4732 instead).
Requirements
- Active Directory domain controllers running Windows Server 2008 or later.
- Audit Security Group Management policy enabled for Success events.
- Centralized log collection (WEF or SIEM agent) across all DCs.
Alternatives
- Event 4732 for local security group membership changes.
- Event 4756 for universal security group membership changes.
- Event 4729 for member removal from global security groups.
Frequently asked questions
What does Event ID 4728 mean?
Event ID 4728 means a member (user, computer, or group) was successfully added to a security-enabled global group in Active Directory. It's a success audit event logged on domain controllers under the Security Group Management category.
Where is Event ID 4728 logged?
Event 4728 is logged only on Active Directory domain controllers, in the Windows Security event log. It never appears on member servers or workstations because global security group changes are AD operations processed by DCs.
How do I enable Event ID 4728 logging?
Enable the Audit Security Group Management policy under Computer Configuration > Policies > Windows Settings > Security Settings > Advanced Audit Policy Configuration > Account Management. Set it to audit Success events. Deploy via Group Policy to all domain controllers.
What is the difference between Event 4728 and Event 4732?
Both events log a member being added to a security group. Event 4728 fires for global security groups (domain-wide scope, DC only). Event 4732 fires for local security groups (can fire on any machine where the local group exists). The event data structure is identical, per Microsoft.
How can I detect privilege escalation with Event 4728?
Monitor Event 4728 for additions to high-privilege groups like Domain Admins, Enterprise Admins, and Schema Admins. Alert when the Subject account isn't an approved admin, when changes happen outside business hours, or when Event 4720 (account created) and 4728 fire within seconds of each other.
How long should I retain Event 4728 logs?
Most organizations retain these events for 1-2 years minimum. Regulatory frameworks like SOX, HIPAA, and PCI-DSS may require 7 years. Use centralized log management or SIEM systems with automated archiving to maintain searchability over long retention periods.
Conclusion
Event ID 4728 is the Windows Security audit event that records every addition to a security-enabled global group in Active Directory. It fires only on domain controllers, requires the Audit Security Group Management policy, and captures complete forensic details about who made the change, which account was added, and which group was modified.
Main takeaway
Look into Event 4732 for local group changes, Event 4756 for universal group changes, and Event 4729 for member removals to build a complete group membership monitoring strategy.