

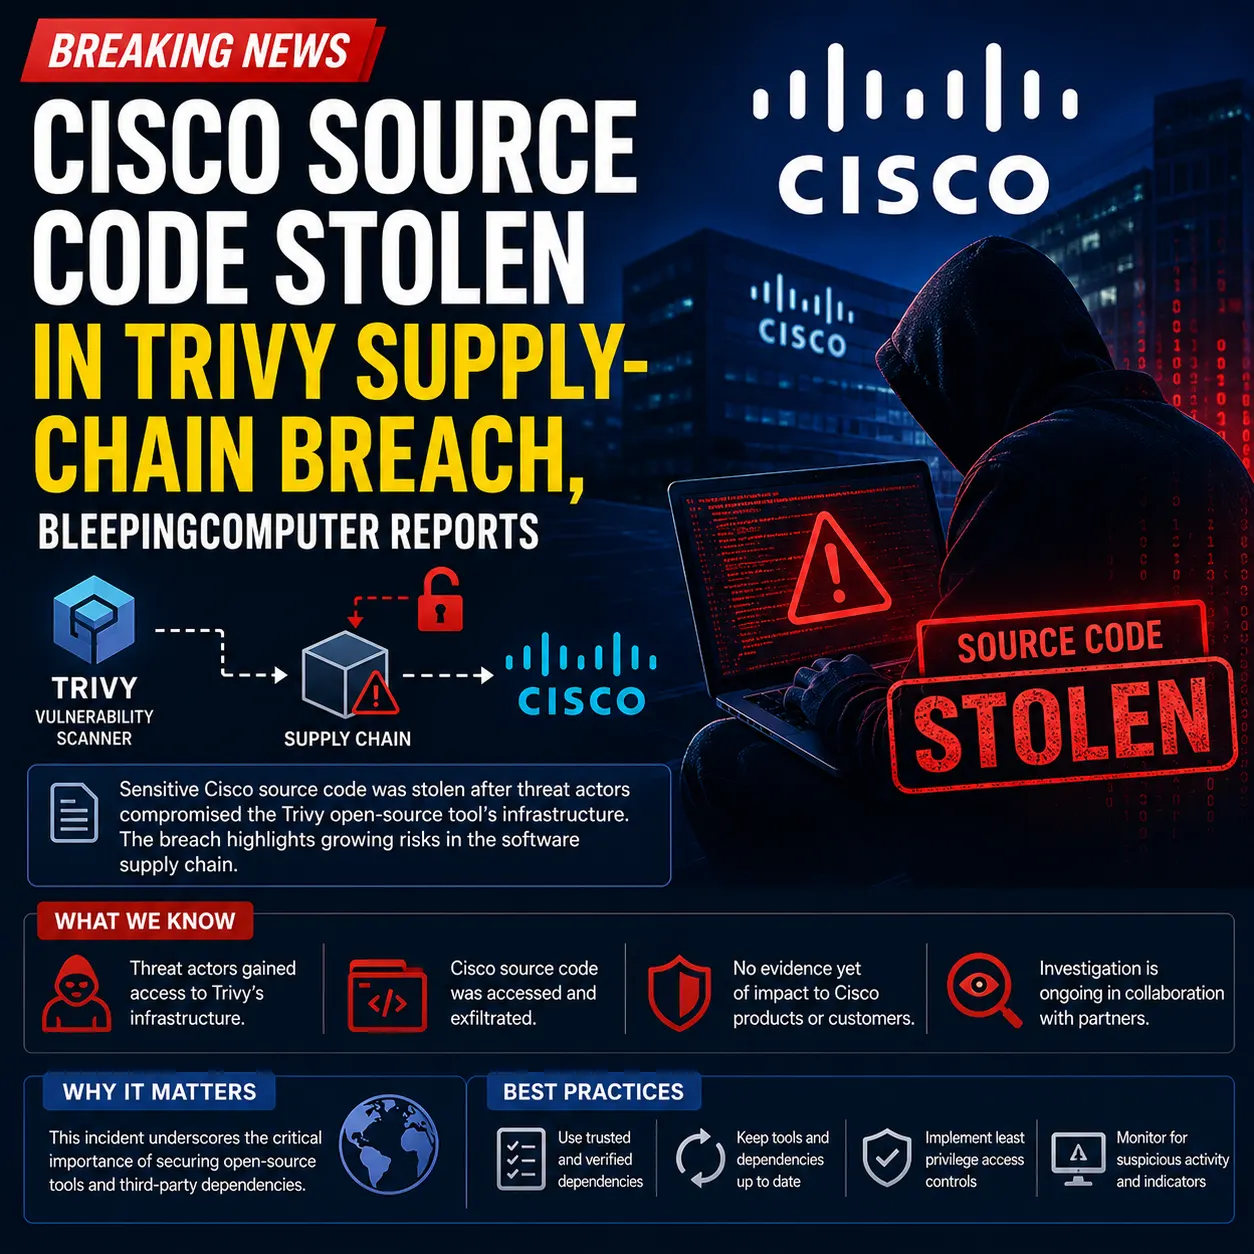
Cisco Source Code Stolen in Trivy Supply-Chain Breach, BleepingComputer Reports
Cisco has not issued a public statement; the breach was reported by BleepingComputer citing a source, and separate ShinyHunters extortion claims remain unverified.

On this page
Key takeaways
- Attackers used credentials stolen via the Trivy compromise (CVE-2026-33634, CVSS 9.4) to reach Cisco's dev environment.
- Reporting says 300+ GitHub repositories were cloned, including AI Assistant and AI Defense source code.
- Stolen AWS keys were used across a small number of Cisco AWS accounts.
- The breach was reported by BleepingComputer citing a source - Cisco has not issued a public statement.
- Separate ShinyHunters extortion claims (3M+ Salesforce records) rest on screenshots and are unverified.
What to do now
High urgency- Update to Trivy v0.69.2+, trivy-action v0.35.0, and setup-trivy v0.2.6.
- Rotate all credentials accessible to CI/CD during the March 19-27, 2026 window (AWS/SSH/GitHub/K8s/API keys).
- Pin GitHub Actions to commit SHAs, adopt OIDC over long-lived cloud keys, and apply least privilege to CI/CD jobs.
- Cisco customers/partners: contact Cisco to determine whether your repositories were affected.
Threat actors used credentials harvested in the TeamPCP Trivy supply-chain compromise to breach Cisco's internal build and development environment, BleepingComputer reported on March 31, 2026, citing a source close to the matter. According to the reporting, attackers cloned more than 300 GitHub repositories - including source code for Cisco's AI Assistant and AI Defense products - and used stolen AWS keys to conduct unauthorized activity across a small number of Cisco AWS accounts. Cisco has not published a public statement, and separate extortion claims by ShinyHunters remain unverified.
The breach is the highest-profile confirmed casualty of a broader campaign (CVE-2026-33634) that poisoned a security scanner trusted inside thousands of CI/CD pipelines - a reminder that the tools guarding the build are themselves high-value targets.
Attackers leveraged the TeamPCP Trivy supply-chain compromise to breach Cisco's development environment and clone 300+ repositories, per BleepingComputer, while broader ShinyHunters extortion claims remain unverified.
TeamPCP poisoned Trivy's GitHub Action (CVE-2026-33634); the harvested credentials let attackers into Cisco's dev environment, cloning 300+ repos (incl. AI Assistant/AI Defense) and touching a few AWS accounts. Reported by BleepingComputer, not officially confirmed by Cisco. ShinyHunters' bigger claims are unverified. Patch Trivy and rotate CI/CD credentials.
Affected & context
According to BleepingComputer, threat actors used credentials harvested in the TeamPCP Trivy supply-chain compromise (CVE-2026-33634) to breach Cisco's internal build and development environment. Reporting indicates attackers cloned more than 300 GitHub repositories - including source code for Cisco's AI Assistant and AI Defense - and used stolen AWS keys to access a small number of Cisco AWS accounts. Cisco has not issued a public statement; separately, ShinyHunters posted extortion claims that remain unverified.
A vulnerability scanner Cisco embedded in its CI/CD pipelines became the entry point to its source code, showing how a single poisoned developer tool can cascade into a major vendor's crown-jewel repositories and cloud accounts.
Cisco (build/dev environment, AWS accounts, source code including some customer repositories for banks, BPOs, and US government agencies), and any organization that ran Trivy's GitHub Actions or the malicious binary in CI/CD during the compromise window.
- Vendors
- CiscoAqua Security (Trivy)
- Products
- Aqua Security Trivy (trivy-action / setup-trivy GitHub Actions, Trivy binary)Cisco internal build/development environment
- Organizations
- Cisco
- Threat actors
- TeamPCP (Google GTIG: UNC6780; aliases DeadCatx3, PCPcat, ShellForce, CipherForce)ShinyHunters (separate, unverified extortion claims)
- Malware
- TeamPCP Cloud Stealer / SANDCLOCK (GTIG naming)
- Geography
- Global
- Industry
- Technology / networkingSoftware development / DevSecOpsCisco customers in finance, BPO, and government
- CVEs
- CVE-2026-33634
What happened
On March 31, 2026, BleepingComputer reported - citing a source close to the matter - that Cisco's internal build and development environment had been breached using credentials stolen in the recent Trivy supply-chain compromise. According to the reporting, a malicious GitHub Action plugin from the Trivy attack harvested credentials and data from Cisco's environment, impacting dozens of devices including some developer and lab workstations. Attackers cloned more than 300 GitHub repositories and used stolen AWS keys to perform unauthorized activity across a small number of Cisco AWS accounts. Importantly, Cisco has not issued a public statement confirming these details; the account rests on BleepingComputer's sourcing, later corroborated by other outlets and consistent with Aqua Security's disclosure of the Trivy compromise.
- Reported by BleepingComputer on March 31, 2026, citing a source - not an official Cisco statement.
- 300+ GitHub repositories cloned; a small number of AWS accounts accessed.
- Cisco's CSIRT/EOC teams reportedly contained the breach.
Cisco has not publicly confirmed the breach. Attribute the specifics to BleepingComputer's reporting, not to a Cisco statement.
How the Trivy compromise worked
Trivy is Aqua Security's widely used open-source vulnerability scanner, embedded in CI/CD pipelines where it runs with access to build secrets. On March 19, 2026, the threat group TeamPCP - tracked by Google's Threat Intelligence Group as UNC6780 - force-pushed malicious code to 76 of 77 version tags in the aquasecurity/trivy-action GitHub Action and all tags in aquasecurity/setup-trivy, and published a malicious Trivy binary (v0.69.4) to official distribution channels. Any pipeline that ran the poisoned action produced normal-looking scan output while the group's infostealer - named SANDCLOCK by GTIG - harvested environment variables, cloud tokens, SSH keys, and AWS credentials in the background. The incident was assigned CVE-2026-33634 with a CVSS of 9.4. When Cisco's pipelines executed the compromised action, the stealer captured the credentials used to reach its internal infrastructure.
- TeamPCP (GTIG: UNC6780) force-pushed to 76/77 trivy-action tags on March 19, 2026.
- A malicious Trivy binary v0.69.4 was published; the SANDCLOCK stealer harvested CI/CD secrets.
- Tracked as CVE-2026-33634, CVSS 9.4.
What was stolen
Per BleepingComputer, the cloned repositories include source code for Cisco's AI Assistant and AI Defense products, along with other repositories - some reportedly belonging to Cisco customers such as banks, business process outsourcing firms, and US government agencies. The theft of AI-product source code is strategically sensitive: access to the logic behind a threat-detection product can help adversaries study how it works and craft evasions. The stolen AWS keys added a cloud dimension, enabling unauthorized activity in a limited set of Cisco accounts before credentials were rotated. Reporting notes multiple threat actors may have been active in the environment with varying degrees of involvement.
- Cloned repos include AI Assistant and AI Defense source code.
- Some customer repositories (banks, BPOs, US government) were reportedly among them.
What organizations should do
Any organization that ran Trivy, trivy-action, or setup-trivy (or the malicious binary) in CI/CD between roughly March 19 and March 27, 2026 should treat all credentials accessible to those pipelines as compromised. Update to fixed versions - Trivy v0.69.2+, trivy-action v0.35.0, setup-trivy v0.2.6 - and rotate AWS keys, SSH keys, GitHub tokens, Kubernetes secrets, and any other pipeline secrets. As durable hardening, pin GitHub Actions to specific commit SHAs rather than movable version tags (the attack abused tag mutability), prefer OIDC over long-lived cloud keys, and apply least privilege to CI/CD jobs. Cisco customers or partners with code or build artifacts in Cisco's infrastructure should contact Cisco to determine whether their repositories were affected.
- Update to Trivy 0.69.2+, trivy-action 0.35.0, setup-trivy 0.2.6.
- Rotate all CI/CD-accessible credentials from the March 19-27 window; pin Actions to commit SHAs.
The ShinyHunters claims and wider campaign
Separately from the substantiated dev-environment breach, the extortion group ShinyHunters published a post on March 31 with an April 3 deadline, alleging theft of 3 million or more Salesforce records, additional GitHub repositories, and AWS S3 data. As of that reporting, the public evidence consisted of screenshots (some showing Cisco AWS resources), and no dataset had been released - so these broader claims are unverified and should be treated as a claim of access rather than confirmed scope. The Cisco breach is one node in a broader TeamPCP/UNC6780 campaign that also hit Checkmarx (KICS/AST Actions), LiteLLM (PyPI), and the Telnyx SDK. Watch for any official Cisco statement, further ShinyHunters disclosures, and downstream exposure for customers whose repositories were among those cloned.
- ShinyHunters' 3M+ Salesforce-records claim is unverified (screenshots only).
- Part of a broader TeamPCP/UNC6780 campaign (Checkmarx, LiteLLM, Telnyx).
Timeline
Initial token theft
An automated bot reportedly exploits a misconfigured GitHub Actions workflow in Aqua Security's Trivy project to steal a privileged token; rotation is incomplete and TeamPCP retains access.
Source: modemguides / security analyses
Confidence: Medium
Trivy GitHub Action poisoned
TeamPCP force-pushes malicious code to 76 of 77 tags in aquasecurity/trivy-action and all tags in setup-trivy, and publishes a malicious Trivy binary (v0.69.4); the stealer harvests CI/CD credentials silently.
Source: SANS ISC / BleepingComputer
Confidence: High
Cisco breach reported
BleepingComputer reports, citing a source, that Cisco's dev environment was breached via the Trivy compromise; 300+ repos cloned and a few AWS accounts accessed. ShinyHunters posts an extortion note with an April 3 deadline.
Source: BleepingComputer / SOCRadar
Confidence: High
Campaign attribution
Google GTIG tracks TeamPCP as UNC6780 and names the stealer SANDCLOCK; the same campaign is linked to Checkmarx, LiteLLM, and Telnyx compromises.
Source: SANS ISC (GTIG)
Confidence: High
Impact
A poisoned Trivy GitHub Action harvested Cisco's CI/CD credentials, leading to the cloning of 300+ repositories (including AI product source code) and access to a small number of AWS accounts. Broader extortion claims are unverified, but the supply-chain exposure extends to any org that ran the compromised Trivy tooling.
Business impact
Loss of strategically sensitive source code (AI Assistant, AI Defense) and potential downstream exposure for customers whose repositories were cloned.
Technical impact
CI/CD credential theft leading to source-code exfiltration and unauthorized AWS account activity.
Security impact
Exposed AI-product source code can aid adversaries in finding weaknesses or building evasions; stolen cloud keys enable lateral movement until rotated.
Privacy impact
Customer and possibly government-agency repositories were reportedly among those cloned, creating secondary exposure obligations.
Affected audience: Cisco and its customers/partners with code in Cisco infrastructure, Any organization using Trivy/trivy-action/setup-trivy in CI/CD, DevSecOps and cloud security teams
Action required.
Technical details
- CVEs
- CVE-2026-33634
- CVSS
- 9.4
- Exploitation
- Exploited in the wild
- Attack vector
- Poisoned Trivy GitHub Action (force-pushed malicious version tags) and a malicious Trivy binary in CI/CD pipelines, harvesting build credentials
- Affected versions
- aquasecurity/trivy-action - compromised version tags (pre-fix), aquasecurity/setup-trivy - compromised tags (pre-fix), Malicious Trivy binary v0.69.4
- Patched versions
- Trivy v0.69.2+, trivy-action v0.35.0, setup-trivy v0.2.6
- CWEs
- CWE-506 (Embedded Malicious Code), CWE-522 (Insufficiently Protected Credentials)
- MITRE ATT&CK
- T1195.001 - Supply Chain Compromise: Software Dependencies and Development Tools, T1552 - Unsecured Credentials, T1078.004 - Valid Accounts: Cloud Accounts
Indicators of compromise
- File
Malicious Trivy binary v0.69.4Trojanized Trivy release published to official channels during the compromise
Source: SANS ISC / security analyses
Confidence: High
- Other
SANDCLOCK / 'TeamPCP Cloud Stealer' infostealerCredential-stealing payload run inside CI/CD pipelines
Source: Google GTIG via SANS ISC
Confidence: High
Detection methods
- Review CI/CD logs for Trivy Action runs during March 19-27, 2026
- Audit AWS CloudTrail for anomalous activity using CI/CD-scoped credentials
Mitigations
- Update Trivy/trivy-action/setup-trivy to fixed versions and rotate exposed credentials
- Pin Actions to commit SHAs; use OIDC; apply least privilege in CI/CD
Technical references
Response
Vendor statement
Cisco has not issued a public statement confirming the breach. Per BleepingComputer's source, Cisco's Unified Intelligence Center, CSIRT, and EOC teams contained the incident, though the company expects continued fallout from the broader supply-chain campaign.
Authorities
Singapore's Cyber Security Agency issued advisories on the TeamPCP campaign (AD-2026-001) and a related npm compromise (AD-2026-002); no Five Eyes joint advisory had been identified as of reporting.
Customer guidance
Aqua Security published fixed Trivy versions; organizations are advised to update and rotate credentials exposed to CI/CD during the compromise window.
Response status: Mitigated
Patch available: Yes
FAQ
Did Cisco officially confirm this breach?
No. The breach was reported by BleepingComputer citing a source close to the matter, and corroborated by other outlets. Cisco has not published a public statement confirming the specifics as of this reporting.
How many repositories were stolen - 300 or 15,000?
BleepingComputer reported more than 300 GitHub repositories were cloned. Figures far higher than that are not supported by the primary reporting; treat any much larger number with caution.
What is CVE-2026-33634?
It's the identifier for the Trivy supply-chain compromise (CVSS 9.4), in which TeamPCP poisoned Trivy's GitHub Actions and a Trivy binary to harvest CI/CD credentials. Fixes: Trivy v0.69.2+, trivy-action v0.35.0, setup-trivy v0.2.6.
Are the ShinyHunters claims (3 million Salesforce records) confirmed?
No. Those extortion claims rest on screenshots and were unverified at the time of reporting. The substantiated part is the Trivy-linked dev-environment breach and repository cloning; the broader ShinyHunters narrative is unsettled.
What should my organization do if we use Trivy?
Update to fixed versions (Trivy 0.69.2+, trivy-action 0.35.0, setup-trivy 0.2.6), and rotate every credential accessible to CI/CD during roughly March 19-27, 2026. Pin Actions to commit SHAs and prefer OIDC over long-lived cloud keys.
The bottom line
According to BleepingComputer, credentials stolen in the TeamPCP Trivy supply-chain compromise (CVE-2026-33634) were used to breach Cisco's development environment, cloning 300+ repositories - including AI Assistant and AI Defense source code - and accessing a small number of AWS accounts. Cisco has not publicly confirmed the incident, and separate ShinyHunters extortion claims remain unverified.
A trusted security scanner became the attack path - update Trivy, rotate CI/CD credentials from the compromise window, and treat pipeline tooling as production-grade attack surface.
What happens next
Watch for any official Cisco statement, further ShinyHunters disclosures after the April 3 deadline, and downstream exposure for customers whose repositories were cloned, amid continued fallout from the wider TeamPCP/UNC6780 campaign.
What to do
Patch Trivy/trivy-action/setup-trivy and rotate all credentials exposed to CI/CD during March 19-27, 2026.
Sources
BleepingComputer · Mar 31, 2026 · Primary source
Claims supported
- Cisco's dev environment was breached via a malicious GitHub Action from the Trivy compromise, per a source.
- 300+ repositories cloned (incl. AI Assistant/AI Defense); AWS keys used across a small number of Cisco accounts.
SC Media · Apr 1, 2026
Claims supported
- Attackers used a malicious GitHub Action from the Trivy hack to compromise Cisco's build/dev environment.
- Cloned repos include Cisco AI Assistant and AI Defense source code.
SANS Internet Storm Center · Apr 8, 2026
Claims supported
- The Trivy compromise is tracked as CVE-2026-33634; GTIG tracks TeamPCP as UNC6780 and names the stealer SANDCLOCK.
- The campaign also affected Checkmarx, LiteLLM, and Telnyx; patched versions were published.
SOCRadar · Apr 1, 2026
Claims supported
- ShinyHunters' extortion claims (3M+ Salesforce records) rest on screenshots and are unverified.
- The Trivy-linked dev-environment breach is the most substantiated part of the story.