

Cruciferra Crypter: How a $450-a-Month Service Hides RATs From EDR
Multiple unrelated criminal clusters rent the same evasion layer, which means one detection gap now serves a dozen malware families at once.

On this page
Key takeaways
- Proofpoint published its Cruciferra analysis on July 20, 2026, based on dozens of observed campaigns.
- The service has been sold on the Exploit forum since autumn 2025 for between 450 and 2,000 US dollars a month, tiered by feature set.
- It drops a vulnerable signed driver to terminate EDR processes, unhooks Windows APIs, and uses indirect system calls.
- More than 90 encryption routines are used across samples, most of them stitched together from parts of established algorithms rather than used whole.
- Payloads observed behind it include Agent Tesla, AsyncRAT, Remcos, XWorm, zgRAT, ValleyRAT, Formbook, XLoader and Snake Keylogger.
What to do now
Medium urgency- Enable Microsoft's vulnerable driver blocklist and equivalent application control policies to block the BYOVD step
- Alert on Run key values of putty and on programmatic disabling of toast notifications and balloon tips
- Block or quarantine disk image attachments and restrict externally sourced shortcut files
- Constrain PowerShell execution and log script block activity
- Hunt for DLL side-loading patterns where a delivered executable and DLL pair run from a user-writable directory
- Treat unexpected EDR agent process termination as a high-severity signal in its own right
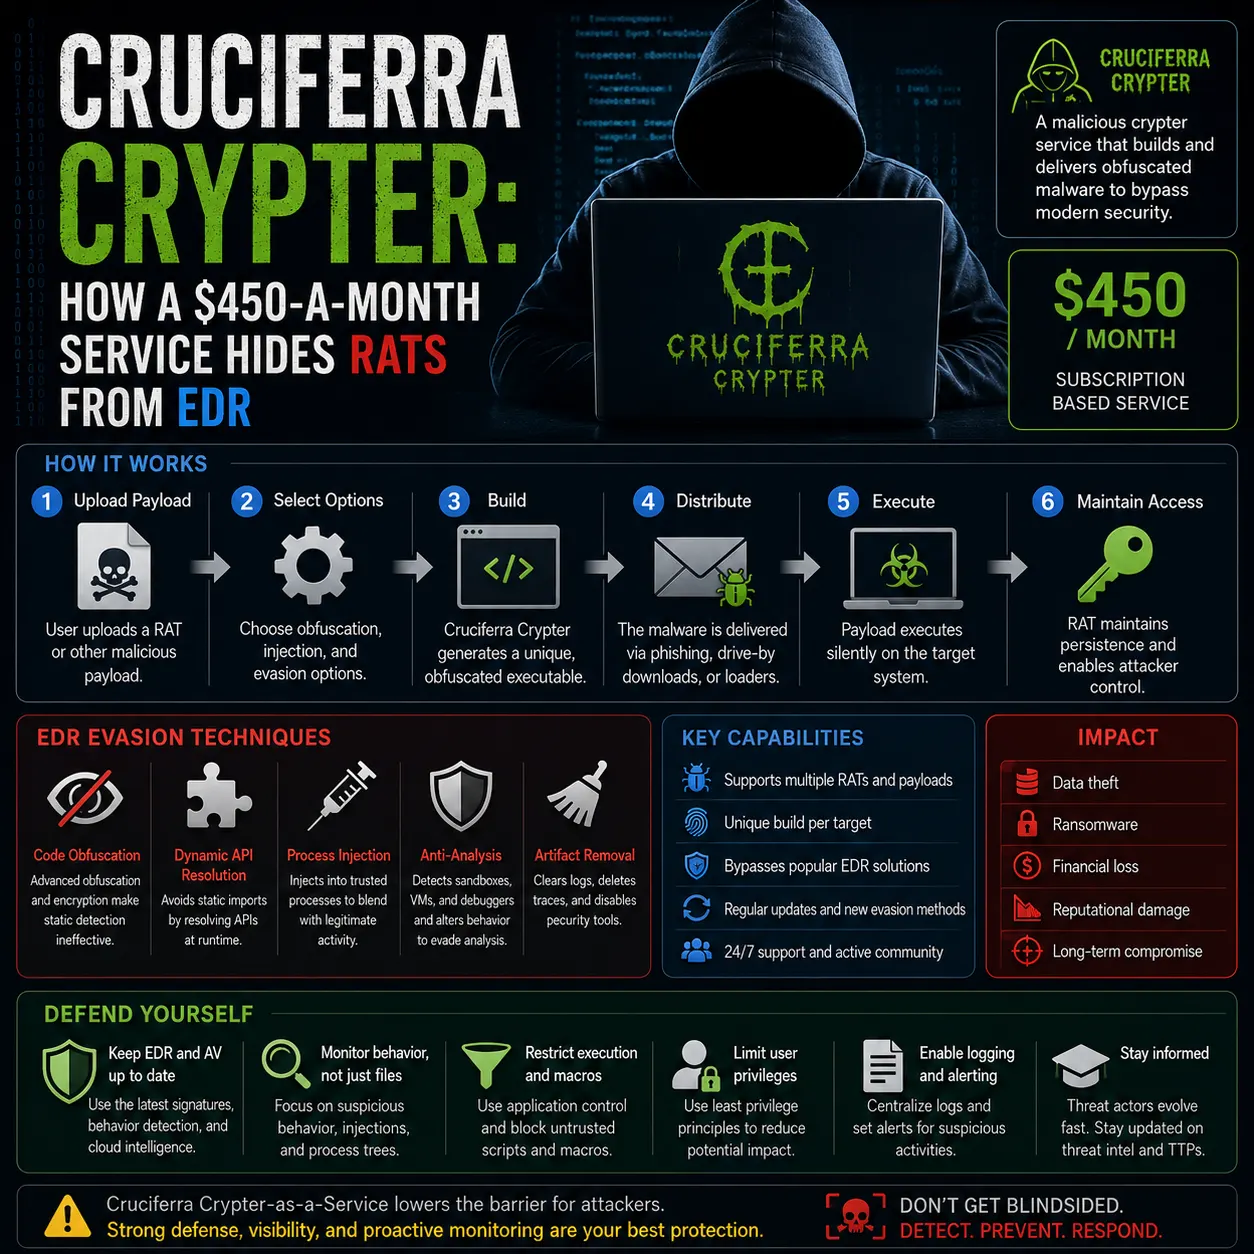
The Cruciferra crypter is a rented evasion layer, and Proofpoint says multiple unrelated criminal groups are now using the same one. In an analysis published on July 20, 2026, the company's threat research team describes a service sold on underground forums since autumn 2025 for 450 to 2,000 US dollars a month, which hides commodity remote access trojans and infostealers behind driver-based EDR tampering, API unhooking and a modified Process Ghosting routine.
For defenders the practical consequence is uncomfortable. Detection built around a specific malware family now sits behind a shared obfuscation layer that changes shape between samples, so the payload you can name is not the thing you have to catch first.
Proofpoint has documented Cruciferra, a crypter service rented by several unrelated criminal clusters that uses BYOVD, unhooking and Process Ghosting to hide commodity RATs and stealers.
Cruciferra is a paid crypter service that wraps commodity malware in a heavy evasion layer: a vulnerable driver to kill EDR processes, API and IAT unhooking, indirect syscalls, UAC bypass, Run key persistence, and a modified Process Ghosting loader. Over 90 varying encryption routines defeat signature matching. It arrives by phishing and always runs through DLL side-loading.
Affected & context
Proofpoint's threat research team published an analysis of Cruciferra on July 20, 2026, describing a crypter service used by multiple unrelated cybercriminal clusters to hide remote access trojans and infostealers. The service has been sold since autumn 2025 for between 450 and 2,000 US dollars a month, and combines bring-your-own-vulnerable-driver EDR tampering, API and IAT unhooking, indirect system calls and a modified Process Ghosting routine.
The evasion layer is now a rented commodity. A single detection gap in Cruciferra benefits every actor renting it, which breaks the usual assumption that a malware family and its delivery tradecraft travel together.
Organisations receiving commodity phishing at volume, with financial services, healthcare and government appearing most often in observed campaigns. Windows endpoints protected by EDR are the specific target of the tampering routines.
- Products
- Microsoft Windows endpointsEDR and antivirus agents
- Threat actors
- TA4922
- Malware
- CruciferraAgent TeslaAsyncRATRemcosXWormzgRATValleyRAT
- Geography
- GlobalIndiaUnited States
- Industry
- Financial servicesHealthcareGovernmentEducationHospitality and travel
What Proofpoint found
Proofpoint's threat research team published an analysis of Cruciferra on July 20, 2026, written by Chris Wakelin, Georgi Mladenov, Kyle Cucci and colleagues. The report covers dozens of campaigns in which the tool was used to hide the real payload.
The headline finding is not the tooling itself but who uses it. Cruciferra is rented by several unrelated criminal clusters, so the same evasion layer sits in front of malware families that otherwise have nothing in common. Proofpoint also notes that Cruciferra appears to be an umbrella name covering several crypters bundled into one service, and that its analysis focuses on the variant it sees most often.
Researchers found both production and apparent test builds, some carrying debugging functionality and experimental features. That points to a service under active development rather than a static tool.
What a crypter is, and why this one stands out
A crypter is a packaging tool that obfuscates a malicious payload so it survives contact with security controls long enough to run. It does not steal anything itself. Its whole job is to get something else past the door.
The category is old and mostly unremarkable. What separates Cruciferra, in Proofpoint's assessment, is the depth of the evasion stack and the variation between builds. It is written in Mono, the cross-platform implementation of the .NET runtime, and it treats endpoint tooling as an obstacle to be actively dismantled rather than simply avoided.
It is also sold openly. The operators advertise it as the underground's most lethal crypter on the Exploit forum, with tiered pricing from 450 to 2,000 US dollars a month depending on the feature set. It first went on sale in autumn 2025.
How the Cruciferra crypter evades detection
Execution always starts the same way. The victim opens an archive containing an executable and a DLL, runs the executable, and the DLL carrying Cruciferra's code is side-loaded. Before anything else happens, the tool checks whether it is running inside a sandbox or an analyst's virtual machine.
From there the evasion stack is unusually broad. Cruciferra drops a legitimate but vulnerable signed driver, most often GoFlyDrv.sys, and uses it to terminate endpoint security processes from kernel level. This is the bring-your-own-vulnerable-driver technique, and Proofpoint lists eight drivers with hashes that have been observed in this role.
Alongside that, it restores Windows API functions and Import Address Table entries that security products had hooked, and calls system functions indirectly to sidestep the hooks that remain. It suppresses Windows toast notifications and balloon tips so the user sees nothing. If it lacks administrator rights it attempts a UAC bypass, then writes a Run key entry with the innocuous value putty for persistence.
The payload itself is loaded through a modified Process Ghosting routine, which runs code from a file already deleted from disk, leaving nothing for a scanner to inspect.
Thousands of decoy exports
The DLLs ship with hundreds or thousands of decoy exported functions pointing at junk code, with only one or a few reaching the real routine. That is an anti-sandbox measure aimed squarely at automated analysis.
More than 90 encryption routines, almost none of them standard
The most distinctive part of the analysis concerns how payloads are protected. Cruciferra draws on more than 90 different encryption routines, and Proofpoint's point is that they are almost never complete algorithms.
Instead each routine is assembled from parts of others. A key schedule borrowed from one algorithm might be bolted onto a cipher core taken from another. The researchers assess that these combinations are probably generated polymorphically from elements of well-known hashing, pseudorandom number generation and cipher algorithms, given how much they vary between sample sets.
The consequence for defenders is direct. Static analysis and signature-based detection both assume something stable to match against, and this design removes it deliberately. Proofpoint's tracking has instead leaned on YARA rules combined with a quirk in the file metadata: Cruciferra-packed binaries carry randomly generated copyright, product and description fields following a recognisable pattern, such as a year followed by two to four invented words.
The campaigns delivering it
Delivery is by email in every case Proofpoint observed, and targeting is opportunistic rather than selective. Message volumes run from several hundred to several thousand per campaign.
Between late April and early June 2026, four campaigns were attributed to the Chinese-speaking cybercrime actor TA4922, using tax-themed lures impersonating the Indian Income Tax Department and the Government of India. Victims were driven to convincing replica tax portals hosting archives, and the chain ended in AsyncRAT. These campaigns were smaller, at up to 250 messages each. The Hacker News notes that TA4922 shows some overlap with the group tracked as Silver Fox, and that the same tax-lure activity was documented separately by Seqrite Labs under the name Operation DragonReturn.
Two other campaigns show the range. In May, emails impersonating the US Social Security Administration led to a disk image file that ultimately delivered XWorm and AdaptixC2. At the end of June, a lure built around bed bug complaints targeted hospitality and travel firms and delivered zgRAT.
Who is in the line of fire
Proofpoint's breakdown of observed campaign targeting puts financial services well ahead at 34 percent, followed by healthcare at 25 percent and government at 10 percent. Education accounts for 7 percent, with several other sectors at roughly 4 percent each.
Those proportions describe where the mail landed, not where compromise succeeded, and the targeting is explicitly opportunistic. A sector concentration in this data says more about who receives high volumes of unsolicited financial and administrative correspondence than about deliberate selection.
The payload list matters more than the sector list for risk assessment. These families have all been seen behind it:
- Remote access trojans: AsyncRAT, Remcos, XWorm, zgRAT, ValleyRAT (also known as Winos4.0)
- Infostealers and keyloggers: Agent Tesla, DarkCloud Stealer, Phantom Stealer, Snake Keylogger
- Form grabbers: Formbook and XLoader
Those are credential theft and remote access tools, which means the realistic outcome is stolen accounts and a foothold sold onward.
What defenders can act on
Driver blocklisting is the highest-value control here. The BYOVD step is what neutralises endpoint tooling, and it depends on loading a known vulnerable signed driver. Microsoft's vulnerable driver blocklist and equivalent application control policies remove that step, and Proofpoint published hashes for the eight drivers it observed.
The persistence and stealth artifacts are cheap to alert on because they are specific.
Persistence
  Software\Microsoft\Windows\CurrentVersion\Run          value: putty

Notification suppression
  Software\Microsoft\Windows\CurrentVersion\PushNotifications   ToastEnabled
  Software\Microsoft\Windows\CurrentVersion\Explorer\Advanced   Balloon
  Software\Microsoft\Windows\CurrentVersion\Explorer\Advanced   ShowInfoTip

Most frequently abused driver
  GoFlyDrv.sys   2fdfdd13a0c548bb68c9d5aa8599a9265d4659da3e237fe7a42ac6ac06b9a06a
A Run key value of putty is not something a legitimate estate produces at scale, and neither is the programmatic disabling of toast notifications and balloon tips.
On the delivery side, the chain depends on the user opening an archive or disk image and running the executable inside it. Blocking or quarantining disk image attachments, restricting shortcut files arriving from outside, and constraining PowerShell all break the chain earlier than any endpoint control. Detection engineering should also expect the payload to be unnameable at the point of entry, since the crypter is the constant and the malware behind it is not.
Timeline
Cruciferra goes on sale
The service is first made available for purchase, advertised on the Exploit forum. Proofpoint dates this to autumn 2025 without a precise day.
Source: Proofpoint
Confidence: Medium
First TA4922 campaign observed
The Chinese-speaking cybercrime actor TA4922 begins a series of tax-themed campaigns using Cruciferra to deliver AsyncRAT.
Source: Proofpoint
Confidence: High
Social Security Administration lure
Emails impersonating the US Social Security Administration lead to a disk image download that runs Cruciferra, delivering XWorm and AdaptixC2.
Source: Proofpoint
Confidence: High
Hospitality sector campaign
A guest complaint lure targeting hospitality and travel firms delivers zgRAT through a shortcut file and a PowerShell chain.
Source: Proofpoint
Confidence: High
Build cadence measured
Proofpoint observes new Cruciferra-packed samples appearing in VirusTotal every few minutes across a single morning.
Source: Proofpoint
Confidence: High
Analysis published
Proofpoint publishes its Cruciferra report with indicators, driver hashes and campaign detail.
Source: Proofpoint
Confidence: High
Impact
Cruciferra lowers the skill required to defeat endpoint tooling. Any actor able to pay a monthly fee gets kernel-level EDR tampering, unhooking and a fileless loader, which shifts the detection burden from the payload to the delivery chain.
Business impact
The realistic outcome of a successful infection is credential theft and persistent remote access, which typically leads on to fraud, data theft or resale of the access.
Technical impact
Termination of endpoint security processes through an abused signed driver, removal of API and IAT hooks, suppression of Windows notifications, UAC bypass, registry persistence and in-memory execution of a payload with no scannable file on disk.
Security impact
Endpoint detection can be blinded before the payload runs, so telemetry from the affected host may be incomplete or absent during the infection window.
Privacy impact
The payload families observed behind Cruciferra are predominantly infostealers and remote access trojans, so credential and personal data exposure is the expected consequence of a successful infection.
Affected audience: Security operations and detection engineering teams, Windows endpoint administrators, MSPs managing mixed client estates, Email security administrators
Action required.
Technical details
- Attack vector
- Email phishing leading to an archive or disk image containing an executable and DLL pair, executed through DLL side-loading on Windows.
- MITRE ATT&CK
- T1566 Phishing, T1574.001 Hijack Execution Flow: DLL Side-Loading, T1562.001 Impair Defenses: Disable or Modify Tools, T1068 Exploitation for Privilege Escalation, T1548.002 Abuse Elevation Control Mechanism: Bypass User Account Control, T1547.001 Registry Run Keys, T1027 Obfuscated Files or Information, T1574.001 DLL Side-Loading, T1548.002 Bypass User Account Control
Indicators of compromise
- File
GoFlyDrv.sysMost frequently abused vulnerable driver used to terminate endpoint security processes
Source: Proofpoint, July 20, 2026
Confidence: High
- Hash
2fdfdd13a0c548bb68c9d5aa8599a9265d4659da3e237fe7a42ac6ac06b9a06aSHA256 of GoFlyDrv.sys as observed by Proofpoint
Source: Proofpoint, July 20, 2026
Confidence: High
- Hash
17aae57cf6255c7eb169bf62ea67376d9708976eb7831f8cdd0ea38bdcb37dc4SHA256 of Core64.sys, an alternative BYOVD helper driver
Source: Proofpoint, July 20, 2026
Confidence: High
- Registry
Software\Microsoft\Windows\CurrentVersion\Run value puttyPersistence artifact written by Cruciferra
Source: Proofpoint, July 20, 2026
Confidence: High
- Registry
Software\Microsoft\Windows\CurrentVersion\PushNotifications ToastEnabledModified to suppress Windows notification pop-ups including Defender and SmartScreen alerts
Source: Proofpoint, July 20, 2026
Confidence: High
- Domain
gatuso[.]duckdns[.]orgXWorm command and control observed in the Social Security Administration campaign
Source: Proofpoint, July 20, 2026
Confidence: High
- Ip
89[.]34[.]90[.]99:56001zgRAT command and control observed in the hospitality campaign
Source: Proofpoint, July 20, 2026
Confidence: High
Detection methods
- Vulnerable driver load events matching the published hash set
- Unexpected termination of EDR or antivirus agent processes
- Run key value of putty
- Registry writes disabling toast notifications, balloon tips and infotips
- Executable and DLL pair delivered together in an archive and run from a user-writable path
- PE file version metadata containing random invented words in copyright, product and description fields
Mitigations
- Microsoft vulnerable driver blocklist and application control policies
- Attachment policy blocking disk images and externally sourced shortcut files
- PowerShell constrained language mode and script block logging
- Tamper protection on endpoint agents, with alerting on agent stop events
Technical references
Response
Customer guidance
Proofpoint says it will continue to monitor the development and adoption of Cruciferra and publish updates as new capabilities and campaigns are identified. It has released example indicators, driver hashes and campaign artifacts in the report.
Response status: Acknowledged
Patch available: No
Workaround available: No
Updates
Initial draft
Built from the Proofpoint Threat Research analysis of July 20, 2026, with The Hacker News coverage of July 27 used for attribution context only.
FAQ
What is a crypter, and what does Cruciferra actually do?
A crypter obfuscates a malicious payload so it survives contact with security controls long enough to run. It does not steal data itself. Cruciferra wraps commodity remote access trojans and infostealers, checks for sandboxes, disables endpoint tooling, then loads the real payload into memory.
What is BYOVD and why does it matter here?
Bring-your-own-vulnerable-driver means dropping a legitimate signed driver that contains a known flaw, then abusing it to run privileged operations. Cruciferra uses it to terminate endpoint security processes from kernel level. Because the driver is properly signed, code signing checks do not stop it. Blocklisting known vulnerable drivers does.
Which malware families have been seen behind Cruciferra?
Proofpoint lists Agent Tesla, AsyncRAT, DarkCloud Stealer, Formbook, Phantom Stealer, Remcos, Snake Keylogger, ValleyRAT, XLoader, XWorm and zgRAT. All are commodity credential theft or remote access tools, which means account compromise and persistent access are the expected outcomes.
Why do signature-based detections struggle with it?
Cruciferra draws on more than 90 encryption routines, and most are stitched together from fragments of established algorithms rather than used whole. Proofpoint assesses that these are probably generated polymorphically, so the encrypted payload looks different between sample sets and there is little stable content to match against.
What is the single most effective control against this chain?
Blocking vulnerable driver loads. The BYOVD step is what disables endpoint tooling, and it depends on loading a known vulnerable signed driver. Microsoft's vulnerable driver blocklist and application control policies remove that capability. Blocking disk image and shortcut attachments breaks the chain even earlier.
The bottom line
Proofpoint documented Cruciferra on July 20, 2026: a crypter service sold since autumn 2025 that uses vulnerable driver abuse, unhooking and a modified Process Ghosting loader to hide commodity RATs and stealers delivered by phishing.
The stealth layer is now rented separately from the malware, so detection anchored to a named family arrives too late in the chain to help.
What happens next
Proofpoint says it will publish updates as new capabilities appear. Given the build cadence observed in July, the evasion set should be expected to shift rather than hold still.
What to do
Confirm vulnerable driver blocklisting is enforced across the estate, and add the published persistence and notification-suppression artifacts to your detection rules.
Sources
Proofpoint Threat Research · Jul 20, 2026 · Primary source
The Hacker News · Jul 27, 2026
MITRE · Primary source
Elastic · Primary source