

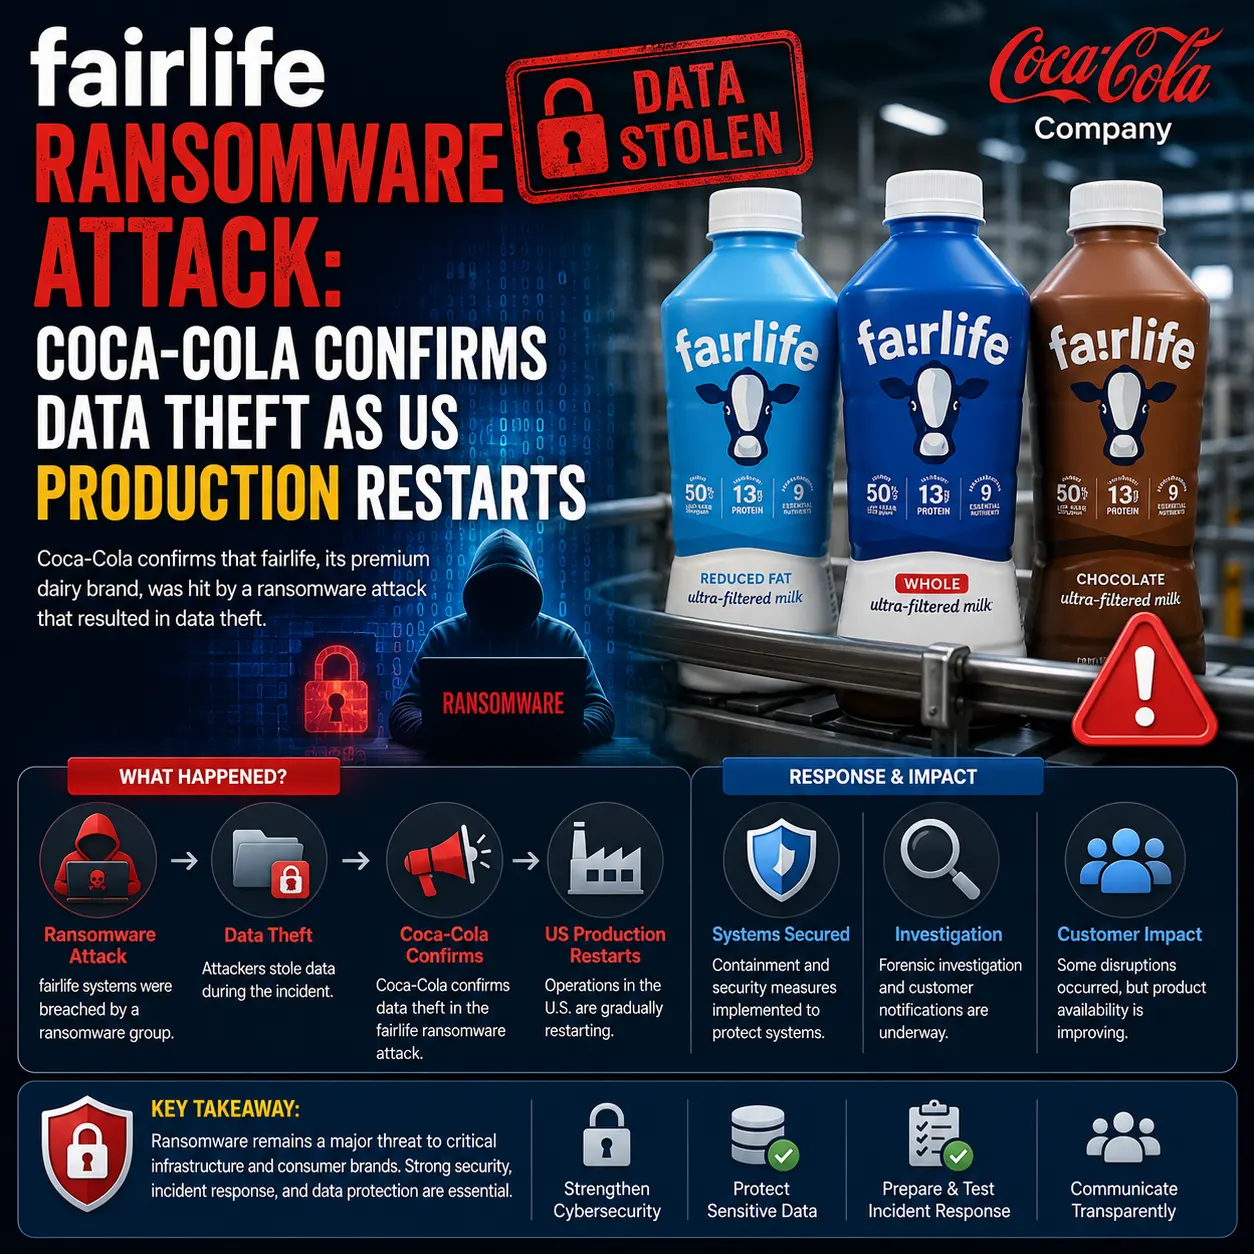
fairlife Ransomware Attack: Coca-Cola Confirms Data Theft as US Production Restarts
The company refused to negotiate, restored most production in eleven days, and let the Anubis gang publish what it stole.

On this page
Key takeaways
- Coca-Cola has confirmed data was taken, going beyond the July 16 SEC filing which only described unauthorised access to systems.
- The majority of production has resumed across fairlife's four US facilities. Canadian operations were never affected.
- The Anubis ransomware group claimed the attack and said it would leak one terabyte of files. That leak went live on July 27.
- Coca-Cola reported the intrusion to law enforcement and did not follow the attacker's instructions to negotiate.
- Retail availability held up because existing inventory covered the gap, and product quality and safety were not affected.
The fairlife ransomware attack has cost Coca-Cola eleven days of US dairy production and a data leak it chose not to pay to stop. The company said on July 27, 2026 that its wholly owned subsidiary has resumed the majority of production at its four American plants, and confirmed for the first time that an unauthorised third party took certain data. Coca-Cola first disclosed the incident in a Form 8-K filed with the US Securities and Exchange Commission on July 16.
Most ransomware coverage stops at the disclosure. This one has run long enough to show the outcome of a decision that boards rarely get to see tested in public: refuse to negotiate, rebuild, and accept the leak.
Coca-Cola has confirmed that data was stolen during the ransomware attack on fairlife and says most US production has now been restored, while the Anubis gang has published its leak.
A ransomware attack disclosed on July 16, 2026 stopped all fairlife production in the United States. Eleven days later Coca-Cola says most of it is back and admits data was taken. It never negotiated with Anubis, which has now published what it claims is a terabyte of stolen files.
Affected & context
The Coca-Cola Company disclosed a ransomware incident at its wholly owned dairy subsidiary fairlife, LLC in a Form 8-K filed with the US Securities and Exchange Commission on July 16, 2026, which suspended all US production. On July 27, 2026 the company said the majority of production had resumed at fairlife's four US facilities and confirmed that an unauthorised third party had taken certain data. The Anubis ransomware group claimed the attack in the intervening days and has since published its leak.
This is one of the clearest public examples of a large manufacturer refusing to negotiate, absorbing a full production stoppage, and getting most operations back within days while accepting that stolen data would be published.
fairlife US production operations and, through the data theft, anyone whose information sat in the affected systems. Coca-Cola has not said what the stolen data contains. Canadian production was not impacted.
- Products
- fairlife ultra-filtered milkfairlife protein shakes and nutrition drinks
- Organizations
- fairlife, LLCThe Coca-Cola Company
- Threat actors
- Anubis ransomware group
- Malware
- Anubis
- Geography
- United StatesNorth America
- Industry
- Food and beverage manufacturingDairyConsumer goods
What Coca-Cola has confirmed
Coca-Cola confirmed on July 27, 2026 that data was taken from fairlife during the ransomware attack, and that the majority of production has resumed at the subsidiary's four US facilities. The company describes the incident as involving access by an unauthorised third party to a portion of its systems and the taking of certain data.
That wording matters. The Form 8-K filed on July 16 described unauthorised access to systems, including production-related systems, but stopped short of confirming exfiltration. Eleven days later the company has closed that gap.
What Coca-Cola still has not said is what the data contains. There is no indication yet of whether it covers employee records, customer information, supplier contracts or purely internal operational material. The company also continues to state that product quality and safety were never affected, and that retail availability held up because existing inventory absorbed the production gap.
How the fairlife ransomware attack unfolded
fairlife, LLC is a wholly owned Coca-Cola dairy subsidiary that makes ultra-filtered milk, protein shakes and nutrition drinks. It runs four production facilities in the United States and reports more than 1 billion dollars in annual retail sales.
Coca-Cola detected the intrusion and filed its Form 8-K with the SEC on July 16, 2026. The filing said the company had activated its incident response and business continuity protocols, engaged outside advisors and cybersecurity experts, notified law enforcement, and could not yet determine whether the incident was reasonably likely to have a material effect.
When SecurityWeek covered the disclosure on July 17, no known ransomware group had claimed responsibility. That changed within days. Anubis listed fairlife on its extortion site and set a countdown, and Coca-Cola declined to comment on the group's specific allegations when asked.
What Anubis says it did
Anubis is a ransomware-as-a-service operation running a double extortion model, encrypting systems and threatening to publish stolen files. Everything in this section comes from the group's own claims and should be read that way.
The group told BleepingComputer it had encrypted fairlife's Nutanix infrastructure and that recovery without its key was impossible. It also said it had been inside the network about a week before the disclosure, and that Coca-Cola reported the incident rather than following the instructions left on the network. On its leak site the group claimed one terabyte of stolen files and set a deadline for negotiations.
Claimed by Anubis      Confirmed by Coca-Cola
---------------------  ----------------------
1 TB of files stolen   data taken, volume not stated
Nutanix fully encrypted  no comment
no recovery possible   majority of production resumed
ransom demand issued   no comment
That deadline passed on July 27 and the data was made available for download. Coca-Cola has not confirmed the volume, the nature of the encrypted systems, or the existence of a ransom demand.
Read leak site posts as marketing
Extortion groups routinely inflate volumes and overstate the damage they caused, because the claim itself is what creates the pressure.
Where the claims meet the company's timeline
One tension is worth naming. Anubis said recovery without its decryption key was impossible. Coca-Cola restored the majority of production across four plants within eleven days of disclosure.
Both statements can be true at once. Restoring production does not require decrypting the encrypted estate if usable backups exist, if the affected systems can be rebuilt, or if the plants can run on a reduced set of systems while recovery continues. Coca-Cola has been careful to say the majority of production, not all of it, and that work on impacted systems and operations continues.
What the sequence does show is which half of the extortion worked. The encryption did not force a payment. The threat to publish could not be answered at all: the company got its factories back on its own schedule, but it could not stop the files going out. That asymmetry is exactly why double extortion exists.
What the production halt actually cost
The operational impact was total on the US side and zero on the Canadian side. Every US facility stopped. Coca-Cola said in the 8-K that fairlife's Canada production operations were not impacted, and it has repeated that position since.
Consumers largely did not notice. Coca-Cola says retail availability was mostly unaffected because existing inventory covered the interruption, which is a function of shelf stock and distribution lead times rather than of how quickly the systems came back.
The financial picture is still open. The July 16 filing said the company had not determined whether the incident was reasonably likely to have a material effect, and that assessment has not been publicly updated. Coca-Cola is due to report second quarter results on July 28, 2026, which is the next obvious moment for any figure to surface.
Coca-Cola did not negotiate
The response pattern is textbook, and unusually well documented for a company of this size. Coca-Cola activated incident response and business continuity protocols on detection, brought in outside advisors and cybersecurity experts, and notified law enforcement. It disclosed to the SEC within the reporting window and issued a public update once restoration was substantially under way.
It also declined to engage with the attackers. According to BleepingComputer, the company reported the intrusion to authorities and did not follow the instructions the group left on its network. Anubis complained about precisely that in its own post, which is an unintentional confirmation that the refusal was real.
Coca-Cola has consistently declined to comment on the attacker's specific allegations, including when asked directly about the terabyte figure and the encryption claims.
What to watch next
Three questions stay open as the story moves out of the acute phase.
- Whether the intrusion reached plant floor systems, or whether production stopped as a precaution when business systems were isolated. Coca-Cola's phrase, production-related systems, does not settle it, and the answer changes how the recovery timeline should be read.
- What the leaked data contains. Now that the files are public, the contents will be characterised by researchers and journalists rather than by the company, and any notification obligations follow from that.
- Whether a material impact figure appears. The second quarter results on July 28 are the next scheduled opportunity, though a company is not obliged to quantify an incident whose assessment is still ongoing.
Timeline
Coca-Cola files the 8-K
The company discloses that an unauthorised third party accessed a portion of fairlife's systems, including production-related systems, and that US production is temporarily suspended.
Source: SEC Form 8-K
Confidence: High
No claim of responsibility yet
SecurityWeek reports the disclosure and notes that no known ransomware group had claimed the attack at that point.
Source: SecurityWeek
Confidence: High
Anubis claims the attack
The Anubis ransomware group adds fairlife to its extortion site and threatens to leak one terabyte of files. The exact date of the listing is approximate.
Source: BleepingComputer
Confidence: Medium
Coca-Cola confirms data theft and restart
A company statement says the majority of production has resumed at the four US plants and acknowledges the taking of certain data.
Source: The Coca-Cola Company
Confidence: High
Anubis publishes the leak
The countdown the group had set expires and the files are made available for download, according to BleepingComputer.
Source: BleepingComputer
Confidence: High
Impact
All fairlife production in the United States stopped for roughly eleven days across four facilities, data was taken and has now been published, and Canadian operations continued throughout. Retail supply held up on existing inventory.
Business impact
A complete US production stoppage at a subsidiary reporting more than 1 billion dollars in annual retail sales, absorbed at retail level by existing inventory. No material impact figure has been published.
Technical impact
Unauthorised access to a portion of fairlife's systems including production-related systems, with restoration work still ongoing at the time of the July 27 statement.
Security impact
Confirmed exfiltration of data by an unauthorised third party, now publicly leaked by the Anubis group.
Privacy impact
Unknown. Coca-Cola has not described the contents of the stolen data, so any notification obligations cannot be assessed from the public record.
Affected audience: fairlife US production sites, Undisclosed data subjects whose information was taken, Coca-Cola shareholders awaiting a materiality assessment, Food and beverage manufacturers watching the response playbook
Urgency: Low
Technical details
- Attack vector
- Not disclosed. Coca-Cola has not said how the intrusion occurred, and no initial access vector has been established publicly.
- MITRE ATT&CK
- T1486 Data Encrypted for Impact, T1657 Financial Theft
Technical references
Response
Vendor statement
Coca-Cola says the event involved access by an unauthorised third party to a portion of its systems and the taking of certain data, along with a temporary suspension of production operations. It states that product quality and safety were not impacted and that it continues to restore affected systems.
Customer guidance
Coca-Cola says retail availability of fairlife products was largely unaffected because of existing inventory, and that product already in distribution was not impacted. It has issued no guidance to individuals about the stolen data, having not described its contents.
Response status: Mitigated
Patch available: No
Workaround available: No
Updates
Initial draft
Written against the state of the story on July 27, 2026, after Coca-Cola confirmed data theft and the resumption of most US production. The originally supplied SecurityWeek article of July 17 predates both developments.
FAQ
Is fairlife milk safe to drink after the ransomware attack?
Coca-Cola has stated consistently, in both the July 16 SEC filing and the July 27 update, that product quality and safety were not impacted. The attack affected information systems rather than the physical product, and anything already in distribution was produced before the incident.
What data was stolen from fairlife?
Coca-Cola has confirmed that an unauthorised third party took certain data but has not described what it contains. The Anubis ransomware group claims one terabyte of files and has published its leak, so the contents are likely to be characterised publicly by researchers rather than by the company.
Did Coca-Cola pay the ransom?
There is no indication that it did. According to BleepingComputer, the company reported the intrusion to law enforcement and did not follow the instructions the attackers left on its network. Anubis went on to publish the stolen data after its deadline expired, which is consistent with a refusal to negotiate.
Has fairlife production returned to normal?
Not entirely. Coca-Cola said on July 27, 2026 that the majority of production had resumed at fairlife's four US facilities, and that it continues to work on restoring some impacted systems and operations. Canadian production was never suspended.
How much did the attack cost Coca-Cola?
No figure has been published. The July 16 Form 8-K said the company had not determined whether the incident was reasonably likely to have a material effect, and that assessment has not been publicly updated. Second quarter results are scheduled for July 28, 2026.
The bottom line
Coca-Cola disclosed a ransomware attack at fairlife on July 16, 2026 that stopped all US production. On July 27 it confirmed data was taken and said most production had resumed, while the Anubis group published its leak.
The encryption did not force a payment, but the threat to publish could not be countered. A company that refuses to pay can get its factories back, and still cannot get its files back.
What happens next
Watch for clarity on whether plant floor systems were reached, for analysis of the leaked files now that they are public, and for any materiality figure at or after the July 28 results.
Sources
US Securities and Exchange Commission via StockTitan · Jul 16, 2026 · Primary source
The Coca-Cola Company · Jul 27, 2026 · Primary source
BleepingComputer · Jul 27, 2026
SecurityWeek · Jul 17, 2026
Just Drinks via Yahoo Finance · Jul 27, 2026
Help Net Security · Jul 17, 2026