

IronWorm Infects 36 npm Packages with Rust Infostealer and eBPF Rootkit
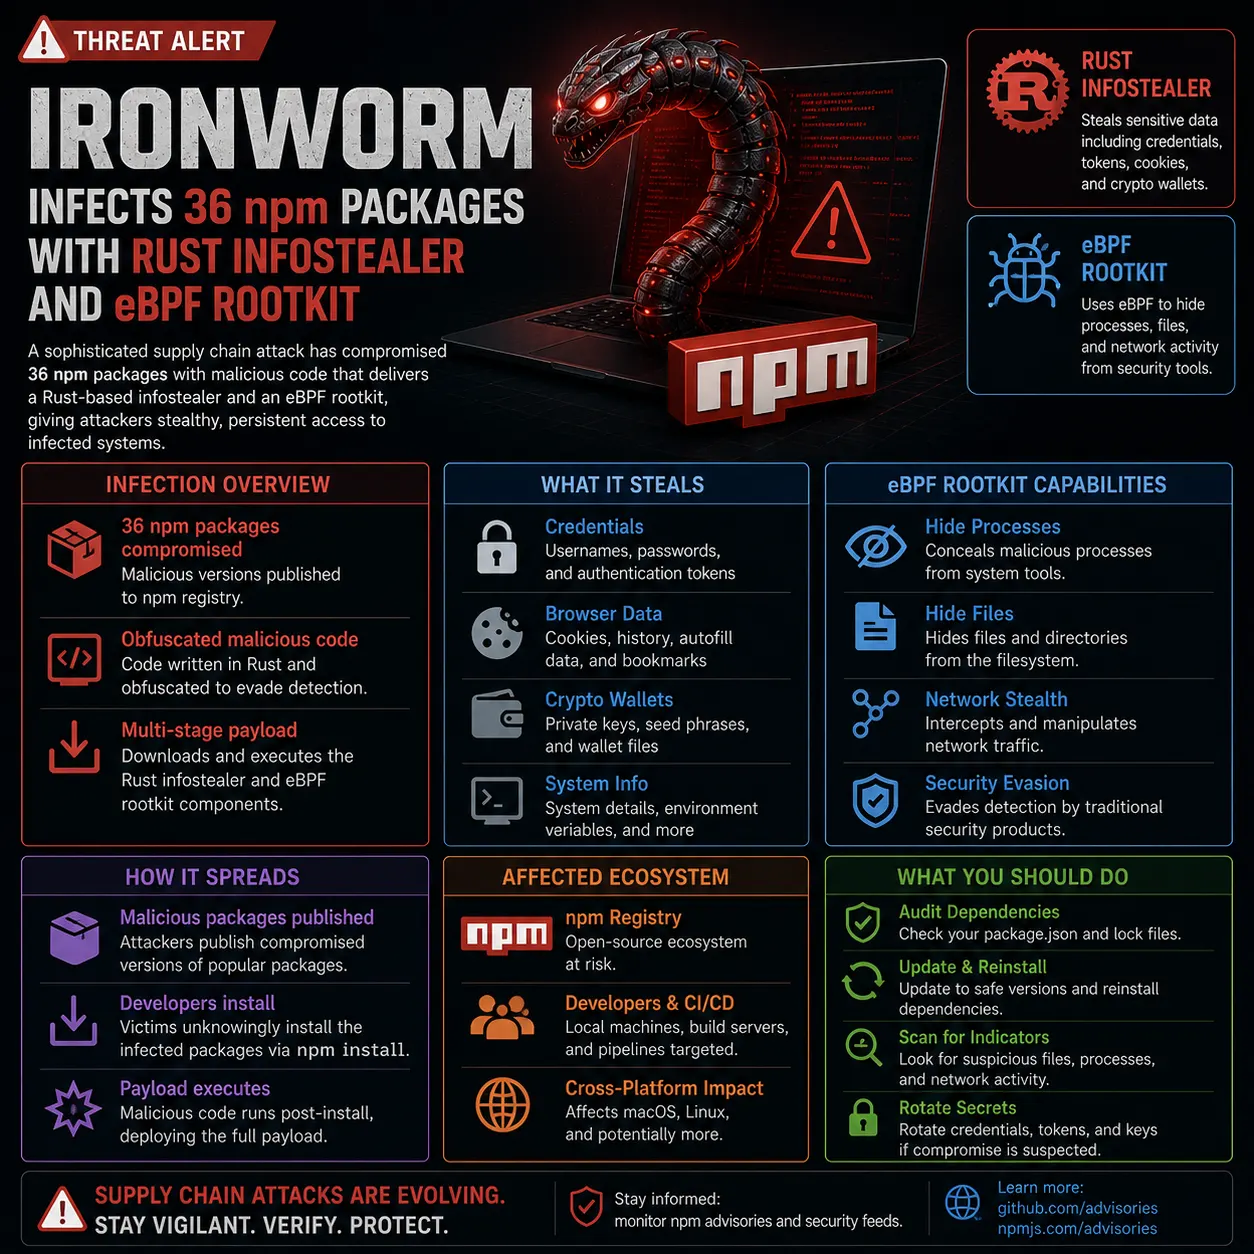
JFrog discovered IronWorm, a Rust-based self-propagating infostealer that infected 36 npm packages via the compromised asteroiddao account. eBPF rootkit, Tor C2, stolen npm Trusted Publishing tokens for self-propagation.

On this page
Key takeaways
- 36 npm packages from asteroiddao infected with Rust-based IronWorm infostealer.
- Steals 86 env vars and 20 credential files: AWS, OpenAI, Anthropic, npm, SSH, crypto wallets.
- Self-propagates by publishing trojanized packages using stolen npm Trusted Publishing tokens.
- Hides behind eBPF kernel rootkit and communicates over Tor.
- 32,177 combined monthly downloads. Mitigated before reaching popular packages.
What to do now
High urgency- Audit for asteroiddao packages in dependencies.
- Rotate all credentials if any affected package was installed.
- Enable 2FA on npm and GitHub.
- Disable install scripts and pin packages with integrity hashes.
JFrog Security Research discovered IronWorm in early June 2026, a Rust-based self-propagating infostealer that infected 36 npm packages from the compromised asteroiddao account. Per BleepingComputer, the malware harvests credentials from 86 environment variables and 20 files, then uses stolen npm Trusted Publishing tokens to publish trojanized packages automatically, creating a self-replicating supply chain attack.
IronWorm's self-propagation mechanism is the key escalation: one compromised developer triggers an automated chain where stolen npm credentials publish malicious package versions, infecting the next developer who runs npm install. Per DarkReading, the eBPF rootkit uses unique encryption keys throughout its codebase, making analysis significantly harder.
IronWorm infected 36 npm packages with a Rust infostealer that self-propagates by publishing trojanized packages using stolen npm tokens.
36 npm packages from asteroiddao. Rust infostealer: 86 env vars, 20 credential files. Self-propagates via stolen npm tokens. eBPF rootkit + Tor C2. Rotate credentials if affected.
Affected & context
JFrog discovered IronWorm, a Rust-based worm that infected 36 npm packages from the asteroiddao account and self-propagates via stolen npm tokens. 32,177 combined monthly downloads. Mitigated.
Self-propagation via stolen npm tokens means one compromised developer infects dozens of downstream packages without additional attacker action.
JavaScript developers who installed any asteroiddao npm packages.
- Vendors
- npm (GitHub/Microsoft)
- Products
- npm (Node Package Manager)
IronWorm Infects 36 npm Packages via Compromised Account
JFrog Security Research discovered IronWorm in early June 2026, a Rust-based infostealer worm that infected 36 npm packages from the compromised asteroiddao account. Per BleepingComputer, the malware targets 86 environment variables and 20 credential files containing OpenAI, AWS, Anthropic, npm credentials, SSH keys, and Exodus wallet files.
Per JFrog and The Hacker News, IronWorm executes via a preinstall hook during npm install. It hides behind an eBPF kernel rootkit and communicates over Tor. It self-propagates by publishing trojanized packages using stolen npm Trusted Publishing tokens. Commit timestamps were backdated up to 13 years.
Self-Propagation Compounds Attack Scope
Per OX Security, the 36 packages had 32,177 combined monthly downloads. A single compromised CI pipeline becomes a vector into dozens of dependent projects. Per DevOps.com, JFrog noted IronWorm still appears to be a work in progress with debug metadata and a hardcoded wallet recovery phrase. The threat was mitigated before reaching popular packages.
Affected Developers and Remediation
JavaScript developers who installed any asteroiddao package. Rotate all credentials (AWS, GCP, npm, SSH, API keys). Enable 2FA. Pin packages with integrity hashes. Disable install scripts in .npmrc.
Timeline
IronWorm discovered and reported
JFrog publishes research on IronWorm campaign infecting 36 npm packages.
Source: JFrog / BleepingComputer
Confidence: High
Malicious packages removed
Attacker deprecates malicious packages and removes them from GitHub.
Source: BleepingComputer
Confidence: High
Miasma variant reported
Related Miasma worm variant reported targeting AI IDE configurations.
Source: The Hacker News
Confidence: High
Impact
36 npm packages infected with self-propagating Rust infostealer targeting developer credentials and CI/CD pipelines. 32,177 combined monthly downloads.
Business impact
Stolen npm tokens enable cascading supply chain compromise. Stolen cloud credentials expose infrastructure.
Security impact
Credential theft enables lateral movement into cloud infrastructure and further supply chain poisoning.
Affected audience: JavaScript/Node.js developers using npm, CI/CD pipelines installing npm packages, Organizations in the Arweave/WeaveDB ecosystem
Action required.
Technical details
- Exploitation
- Exploited in the wild
- Attack vector
- Supply chain (npm preinstall hook executes Rust ELF binary)
Mitigations
- Audit and remove asteroiddao packages.
- Rotate all credentials.
- Enable 2FA on npm and GitHub.
- Disable install scripts: ignore-scripts=true in .npmrc
Response
Response status: Resolved
Patch available: No
Workaround available: Yes
FAQ
What is IronWorm?
A Rust-based self-propagating infostealer that infects npm packages. Per JFrog, it steals credentials, hides behind an eBPF rootkit, communicates over Tor, and publishes trojanized packages using stolen npm tokens.
How many packages were affected?
36 packages from the asteroiddao scope with 32,177 combined monthly downloads, per OX Security. Mitigated before reaching more popular packages.
What credentials does IronWorm steal?
Per BleepingComputer, it targets 86 environment variables and 20 credential files: AWS, OpenAI, Anthropic, npm tokens, SSH keys, Vault configs, and Exodus crypto wallets.
What should I do if affected?
Rotate all credentials. Enable 2FA on npm and GitHub. Pin packages with integrity hashes. Disable install scripts in .npmrc (ignore-scripts=true).
The bottom line
IronWorm infected 36 npm packages with a Rust infostealer that harvests credentials and self-propagates by publishing trojanized packages using stolen npm tokens. eBPF rootkit and Tor C2 add stealth.
IronWorm shows supply chain attacks evolving: self-propagation via stolen tokens means one compromised developer infects dozens of packages automatically. Disable install scripts, pin hashes, enable 2FA.
What happens next
JFrog and npm continue monitoring for IronWorm variants. A related Miasma worm variant was discovered targeting AI IDE configurations.
What to do
Audit for asteroiddao packages. Rotate credentials. Enable 2FA. Disable install scripts in .npmrc.
Sources
BleepingComputer · Jun 4, 2026
Claims supported
- 36 packages, 86 env vars, 20 credential files
- Rust, eBPF rootkit, Tor C2
- Self-propagation via npm tokens
- Backdated commits up to 13 years
OX Security · Jun 7, 2026
Claims supported
- 32,177 monthly downloads
- Mitigated before popular packages
The Hacker News · Jun 6, 2026
Claims supported
- Preinstall hook execution
- Miasma worm variant
DarkReading · Jun 4, 2026
Claims supported
- Unique encryption keys throughout codebase
- eBPF rootkit conceals processes