

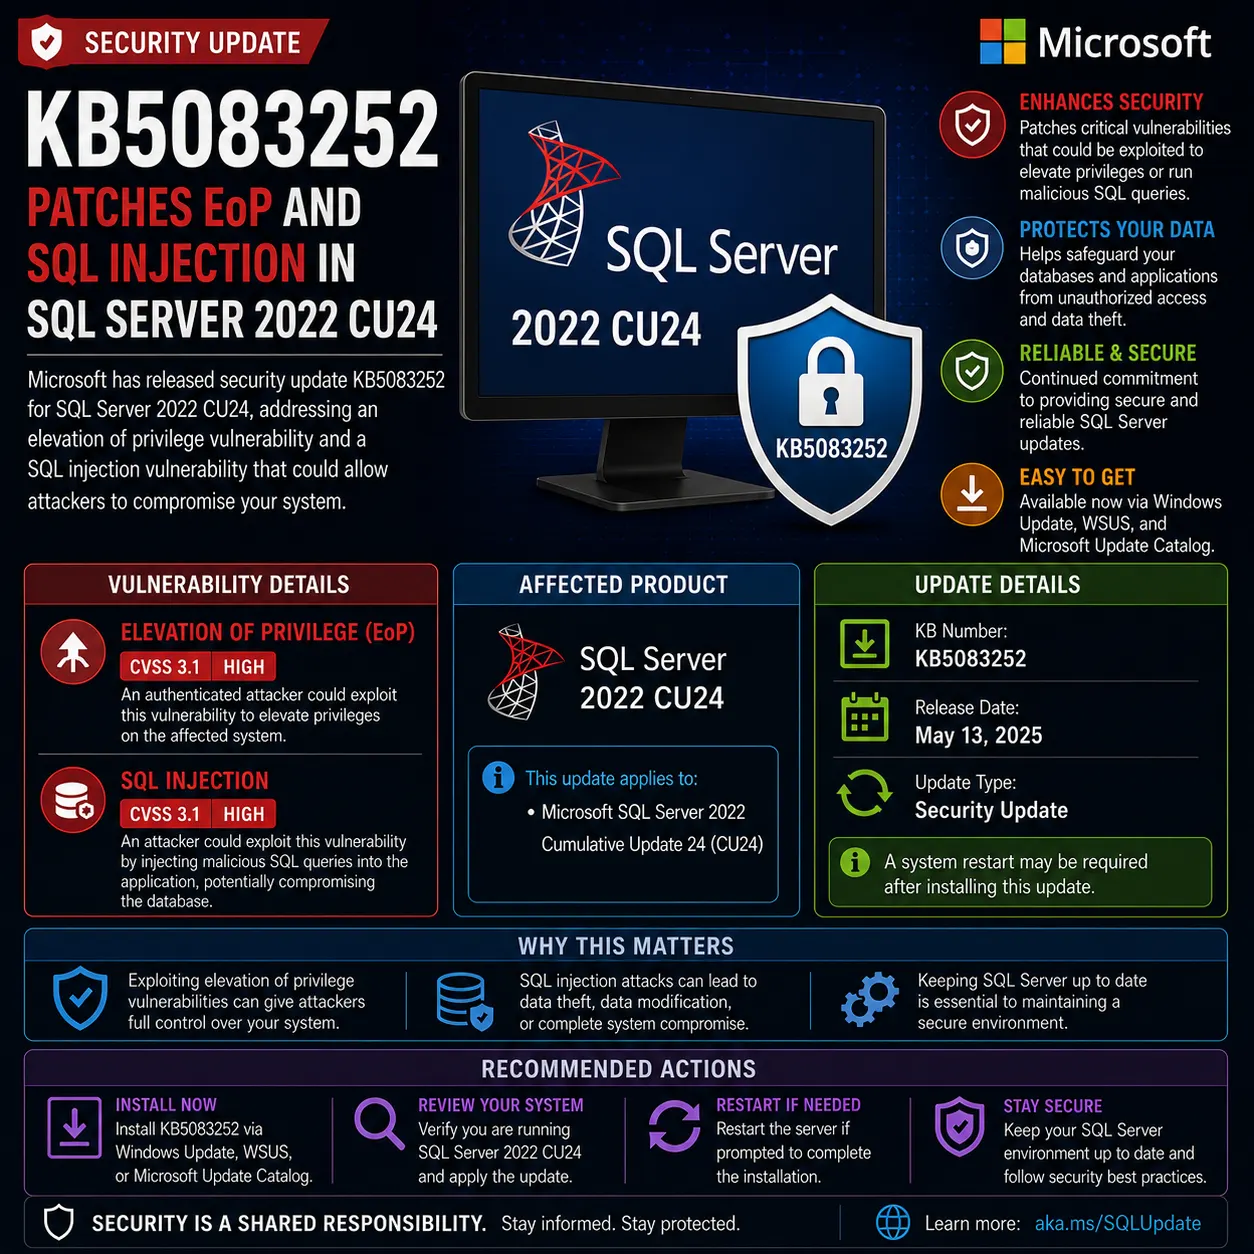
KB5083252 Patches EoP and SQL Injection in SQL Server 2022 CU24
April 2026 security update for SQL Server 2022 CU24 patches CVE-2026-32167 (internal SQL injection EoP), CVE-2026-32176 (PolyBase EoP), and a separate SQL injection in system stored procedures. Build 16.0.4250.1.

On this page
Key takeaways
- CVE-2026-32167: CVSS 6.7, SQL injection in internal procedures (CWE-89).
- CVE-2026-32176: PolyBase linked server EoP.
- Separate SQL injection fix in system stored procedures.
- Build 16.0.4250.1. MSDASQL breaking change (Msg 7416).
What to do now
High urgency- Install latest SQL Server 2022 CU.
- Test MSDASQL linked servers.
Microsoft released KB5083252 on April 14, 2026, a security update for SQL Server 2022 CU24 patching CVE-2026-32167 (SQL injection EoP, CVSS 6.7), CVE-2026-32176 (PolyBase EoP), and a SQL injection in system stored procedures. Per sqlfingers.com, these are the same vulnerabilities patched in parallel for SQL Server 2019 (KB5084816).
SQL Server 2022 is the current production version. The PolyBase linked server escalation and internal SQL injection affect both 2019 and 2022, requiring patches on both.
KB5083252 patches SQL injection EoP, PolyBase EoP, and stored procedure injection in SQL Server 2022 CU24.
SQL Server 2022 CU24: CVE-2026-32167 SQLi EoP + CVE-2026-32176 PolyBase EoP + stored proc injection. Build 16.0.4250.1. MSDASQL breaking change.
Affected & context
April 2026 security update for SQL Server 2022 CU24 patching CVE-2026-32167 (SQL injection EoP), CVE-2026-32176 (PolyBase EoP), and SQL injection in stored procedures.
Same EoP vectors as SQL Server 2019. Sysadmin escalation via PolyBase and internal SQL injection.
SQL Server 2022 RTM with any CU, all editions.
- Vendors
- Microsoft
- Products
- SQL Server 2022 (Windows)SQL Server 2022 (Linux)
- CVEs
- CVE-2026-32167CVE-2026-32176
KB5083252 Patches EoP and SQL Injection in SQL Server 2022 CU24
Microsoft released KB5083252 on April 14, 2026, a security update for SQL Server 2022 CU24. Per Microsoft's KB article, it patches CVE-2026-32167 and CVE-2026-32176 (both elevation of privilege) plus a SQL injection flaw in system stored procedures. Build updates to 16.0.4250.1.
Per sqlfingers.com analysis, CVE-2026-32167 (CVSS 6.7, CWE-89) is SQL injection in the engine's own internal routines. CVE-2026-32176 affects the PolyBase linked server component. The same vulnerabilities are patched in parallel for SQL Server 2019 (KB5084816). The MSDASQL linked server breaking change (Msg 7416) also applies.
Same EoP Vectors as SQL Server 2019, Plus SQL Injection
SQL Server 2022 is the current production version. The SQL injection in system stored procedures is a separate fix from the CVE-2026-32167 internal SQL injection. Per sqlfingers.com, the PolyBase linked server bug allows a low-privileged user to gain sysadmin. Organizations running either SQL Server 2019 or 2022 need to patch both versions.
All SQL Server 2022 Editions
SQL Server 2022 RTM with any CU applied, Windows and Linux, all editions. Build 16.0.4250.1. File size 464.4 MB (x64). MSDASQL linked server breaking change. Check for newer SQL Server 2022 CU releases that supersede this update.
Timeline
KB5083252 released
Microsoft releases KB5083252 for SQL Server 2022 CU24.
Source: Microsoft Support
Confidence: High
Impact
Three vulnerability fixes plus MSDASQL breaking change in SQL Server 2022 CU24.
Business impact
EoP enables sysadmin escalation. SQL injection in stored procedures enables code execution. MSDASQL failures break integrations.
Security impact
CVE-2026-32167 allows sysadmin escalation via SQL injection. CVE-2026-32176 enables PolyBase linked server escalation.
Affected audience: SQL Server 2022 DBAs, Environments with PolyBase and MSDASQL linked servers
Action required.
Technical details
- CVEs
- CVE-2026-32167, CVE-2026-32176
- CVSS
- 6.7
- Affected versions
- SQL Server 2022 (before 16.0.4250.1)
- Patched versions
- SQL Server 2022 Build 16.0.4250.1
- CWEs
- CWE-89
Mitigations
- Install latest SQL Server 2022 CU.
- Restrict PolyBase and linked server permissions.
Technical references
Response
Response status: Patched
Patch available: Yes
Workaround available: No
FAQ
What does KB5083252 fix?
CVE-2026-32167 (SQL injection EoP, CVSS 6.7), CVE-2026-32176 (PolyBase EoP), and a separate SQL injection in system stored procedures. Build 16.0.4250.1.
Which systems are affected?
SQL Server 2022 RTM with any CU, Windows and Linux, all editions.
Is there a known breaking change?
Yes. MSDASQL linked server queries with @provstr fail with Msg 7416.
The bottom line
KB5083252 patches CVE-2026-32167 (SQL injection EoP), CVE-2026-32176 (PolyBase EoP), and SQL injection in system stored procedures for SQL Server 2022 CU24.
Same EoP vectors as SQL Server 2019. Patch both versions. Test MSDASQL linked servers before production deployment.
What happens next
Check for newer SQL Server 2022 CU releases.
What to do
Install latest SQL Server 2022 CU. Test MSDASQL linked servers.
Sources
Microsoft · Apr 14, 2026 · Primary source
Claims supported
- CVE-2026-32167 and CVE-2026-32176
- SQL injection fix
- Build 16.0.4250.1
- MSDASQL breaking change
sqlfingers.com · Apr 14, 2026
Claims supported
- CVE-2026-32167 is SQL injection in internal procedures
- CVE-2026-32176 PolyBase linked server component