Microsoft released KB5094128 on June 9, 2026, a critical security update for Windows Server 2022 that patches multiple high-severity vulnerabilities, including an unauthenticated remote code execution flaw in the Windows Network File System (NFS) service. The update raises the operating system build number to 20348.5256 and requires a system restart to complete installation.
The most severe flaw, CVE-2026-26001, carries a CVSS score of 9.8 and can be exploited by unauthenticated attackers over the network against systems running NFS, while a separate AD CS authentication bypass could enable domain-wide compromise.
Key takeaways
- KB5094128 is a critical update for Windows Server 2022 released June 9, 2026, raising the build to 20348.5256.
- CVE-2026-26001 is an unauthenticated NFS remote code execution flaw rated CVSS 9.8.
- Other fixes include Task Scheduler privilege escalation (CVE-2026-26002), an AD CS authentication bypass (CVE-2026-26003), and a kernel memory corruption bug (CVE-2026-26004).
- The update applies to Standard, Datacenter, and Azure Edition on both full and Server Core installations, and requires a restart.
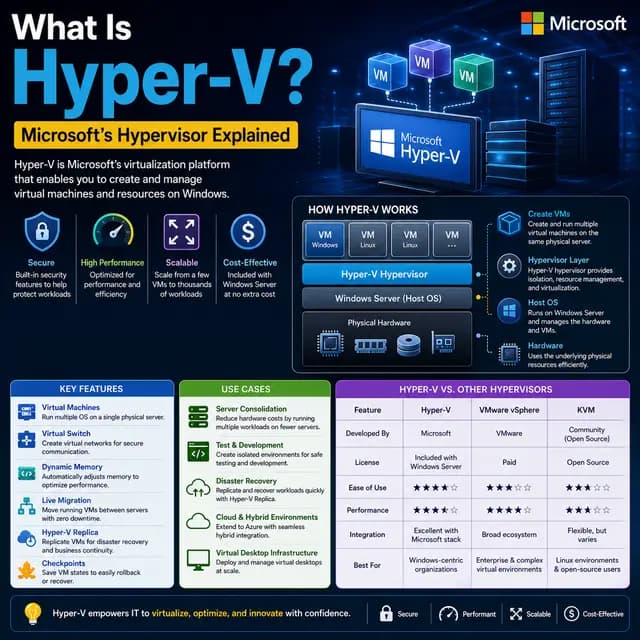
- Known issues include Hyper-V VM startup delays and a possible manual NFS service restart after installation.
Affected
What KB5094128 fixes
KB5094128 is a critical cumulative security update for Windows Server 2022, released on June 9, 2026. It addresses several high-severity vulnerabilities across core server components and raises the operating system build number to 20348.5256.
According to the update documentation, the vulnerabilities stem from insufficient input validation in networking components, improper memory handling in system services, and authentication bypass flaws in Windows Server authentication mechanisms. The issues affect both full installation and Server Core deployment modes.
- Update raises build number to 20348.5256
- Released June 9, 2026
- Restart required to complete installation
Key vulnerabilities addressed
CVE-2026-26001 — NFS Remote Code Execution (CVSS 9.8)
A critical flaw in the Windows NFS service lets unauthenticated remote attackers execute arbitrary code by sending malformed network packets. It affects systems with NFS enabled and requires network access to the NFS service port (typically 2049). The fix adds proper input validation and bounds checking in NFS packet processing.
CVE-2026-26002 — Task Scheduler Privilege Escalation
Local attackers able to create scheduled tasks could exploit insufficient validation of task definition files to escalate to SYSTEM. The update enforces stricter validation of task configurations.
CVE-2026-26003 — AD CS Authentication Bypass
A flaw in Active Directory Certificate Services certificate template validation could allow attackers to obtain unauthorized certificates, potentially leading to domain compromise by impersonating any user or computer. The update strengthens certificate template validation.
CVE-2026-26004 — Windows Kernel Memory Corruption
Improper handling of memory allocation in kernel-mode drivers could lead to system crashes or arbitrary code execution in kernel mode. The fix adds enhanced memory management and validation checks.
The update also improves Windows Defender Application Control (WDAC) bypass prevention and strengthens Hyper-V security isolation between guests and the host.
- CVE-2026-26001 carries a CVSS score of 9.8
- NFS RCE is exploitable by unauthenticated attackers
Affected systems
KB5094128 applies to the following Windows Server 2022 configurations, all of which advance to build 20348.5256:
- Windows Server 2022 Standard — Full Installation
- Windows Server 2022 Datacenter — Full Installation
- Windows Server 2022 Standard — Server Core
- Windows Server 2022 Datacenter — Server Core
- Windows Server 2022 Azure Edition — Server Core
Deployment and verification
The update is delivered through Windows Update and is also available via the Microsoft Update Catalog, WSUS (Security Updates classification), and SCCM software update management. The full installation package is approximately 485 MB, and the Server Core package is about 312 MB. A restart is required.
Restart required
Plan installation during a maintenance window. The update requires at least 1 GB of free system-drive space, administrative privileges, and no pending restarts from prior updates.
After installation, verify the update from PowerShell:
Get-HotFix -Id KB5094128
(Get-ItemProperty "HKLM:SOFTWARE\Microsoft\Windows NT\CurrentVersion").BuildLabEx
Confirm the OS build shows 20348.5256 (for example via msinfo32) and that KB5094128 appears in the installed updates list.
Known issues
- Hyper-V VMs may see 10-30 second longer startup times due to enhanced hypervisor security checks; this is expected behavior.
- Systems running NFS may require a manual restart of the NFS service after installing the update.
- AD CS environments may need to clear the certificate template cache (restart the AD CS service or refresh templates).
- Systems using WDAC policies may require a policy refresh after the update.
Timeline
Impact & actions
Windows Server 2022 systems that do not apply KB5094128 remain exposed to remote code execution, privilege escalation, and authentication bypass attacks.
Security: Addresses a critical unauthenticated NFS RCE (CVSS 9.8), Task Scheduler EoP, AD CS authentication bypass, and kernel memory corruption.
Recommended actions · High urgency
- 1Install KB5094128 on all Windows Server 2022 systems and restart
- 2Prioritize systems exposed to the network with NFS enabled
- 3Pilot test before broad rollout and maintain a rollback plan
- 4Restart NFS/AD CS services and refresh WDAC policies where applicable after install
Technical details
- CVEs
- CVE-2026-26001, CVE-2026-26002, CVE-2026-26003, CVE-2026-26004
- CVSS
- 9.8
- Attack vector
- Network (NFS service, typically port 2049) for CVE-2026-26001; local access required for CVE-2026-26002.
- Affected versions
- Windows Server 2022 (build prior to 20348.5256)
- Patched versions
- 20348.5256
Mitigations
- Install KB5094128 and restart
- Limit network exposure of the NFS service where patching is delayed
Response
Customer guidance
Microsoft distributes KB5094128 through Windows Update, the Microsoft Update Catalog, WSUS, and SCCM; administrators should approve and deploy it as a critical security update and restart affected systems.
FAQ
What does KB5094128 resolve?
It resolves multiple critical Windows Server 2022 vulnerabilities, including NFS remote code execution (CVE-2026-26001), Task Scheduler privilege escalation (CVE-2026-26002), AD CS authentication bypass (CVE-2026-26003), and kernel memory corruption (CVE-2026-26004).
Which systems require KB5094128?
All Windows Server 2022 systems, including Standard and Datacenter in both full installation and Server Core, plus Azure Edition Server Core.
What build number does KB5094128 install?
The update raises the OS build number to 20348.5256. You can verify with Get-HotFix -Id KB5094128 or by checking the OS build in msinfo32.
Is a restart required?
Yes. KB5094128 requires a system restart to complete installation, so plan deployment during a maintenance window.
The bottom line
KB5094128 is a critical June 2026 security update for Windows Server 2022 that patches four high-severity vulnerabilities and raises the build to 20348.5256.
What happens next
What to do