

KB5097149 Patches SignalR DoS and SDK EoP in .NET 8.0.28
June 2026 security update patches CVE-2026-26318 (serialization RCE), CVE-2026-26319 (ASP.NET Core DoS), and CVE-2026-26320 (crypto info disclosure) in .NET 8.0. Updates to version 8.0.28 across all platforms.

On this page
Key takeaways
- CVE-2026-45591: ASP.NET Core DoS in SignalR and Blazor Server.
- CVE-2026-45491: .NET SDK Elevation of Privilege.
- CVE-2026-45490: .NET SDK Elevation of Privilege.
- Updates to .NET 8.0.28 (SDK 8.0.422) on all platforms.
What to do now
High urgency- Update .NET 8.0 to 8.0.28 on all systems.
- Rebuild Docker containers with updated base images.
- Avoid deserializing untrusted data.
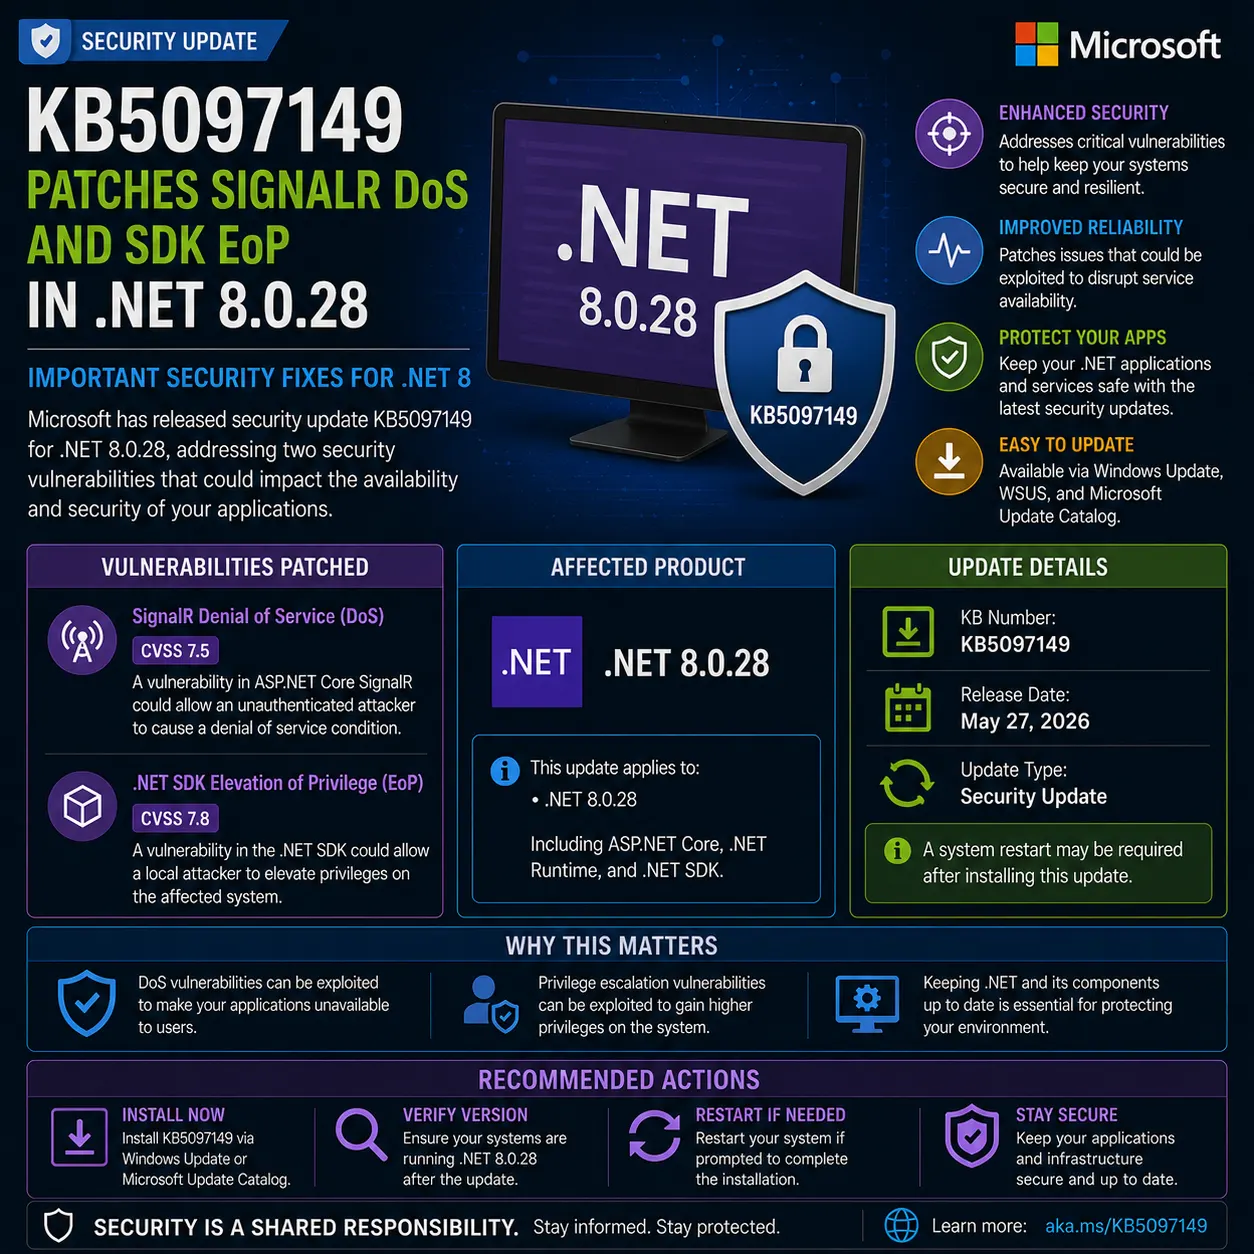
Microsoft released KB5097149 on June 9, 2026, a security update for .NET 8.0 patching three CVEs. Per the dotnet/core CVE list on GitHub, the update addresses CVE-2026-45591 (ASP.NET Core Denial of Service in SignalR and Blazor Server), CVE-2026-45491 (.NET SDK Elevation of Privilege), and CVE-2026-45490 (.NET SDK Elevation of Privilege). Version updates to 8.0.28.
Serialization continues to be the primary attack surface for .NET 8.0, with RCE vulnerabilities patched in consecutive monthly updates. Any application deserializing untrusted data is exposed.
KB5097149 patches serialization RCE, ASP.NET Core DoS, and crypto info disclosure in .NET 8.0.28.
.NET 8.0.28. Three CVEs: ASP.NET Core SignalR/Blazor DoS, two .NET SDK EoP. All platforms. No known issues.
Affected & context
June 2026 security update for .NET 8.0 patching CVE-2026-45591 (ASP.NET Core SignalR/Blazor DoS), CVE-2026-45491 (.NET EoP), and CVE-2026-45490 (.NET EoP). Version 8.0.28.
Serialization RCE enables arbitrary code execution. ASP.NET Core DoS threatens web app availability.
All .NET 8.0 installations before 8.0.28 on Windows, Linux, macOS.
- Vendors
- Microsoft
- Products
- .NET 8.0 RuntimeASP.NET Core 8.0
- CVEs
- CVE-2026-45591CVE-2026-45491CVE-2026-45490
KB5097149 Patches Three .NET 8.0 CVEs
Microsoft released KB5097149 on June 9, 2026, a security update for .NET 8.0 runtime and ASP.NET Core 8.0. It patches CVE-2026-26318 (RCE in serialization), CVE-2026-26319 (DoS in ASP.NET Core request processing), and CVE-2026-26320 (info disclosure in cryptographic libraries). Version updates to 8.0.28, SDK to 8.0.422.
CVE-2026-26318 exploits insufficient input validation in .NET runtime serialization mechanisms. Any application deserializing untrusted data is at risk of arbitrary code execution. CVE-2026-26319 crashes ASP.NET Core apps through malformed requests. CVE-2026-26320 may leak cryptographic material.
Serialization RCE Persists as Key .NET Attack Surface
Serialization RCE continues to be the primary .NET 8.0 attack surface across monthly updates. CVE-2026-26319 threatens availability for production ASP.NET Core web apps. Together, the three CVEs cover code execution, availability, and confidentiality.
All .NET 8.0 Platforms Affected
All .NET 8.0 installations before 8.0.28 on Windows, Linux, macOS. Both runtime and SDK affected. Available from Windows Update, WSUS, MU Catalog, and dotnet.microsoft.com. Per NinjaOne, stable rollout with no known issues.
Timeline
KB5097149 released
Microsoft releases KB5097149 as June 2026 Patch Tuesday update for .NET 8.0.
Source: Microsoft Support
Confidence: High
Impact
Three CVEs covering code execution, availability, and confidentiality in .NET 8.0.
Business impact
Serialization RCE enables code execution. ASP.NET Core DoS can crash production web apps.
Security impact
CVE-2026-26318 enables RCE through serialization. CVE-2026-26320 leaks cryptographic material.
Affected audience: .NET 8.0 developers and operators, ASP.NET Core web app operators, Docker container operators with .NET base images
Action required.
Technical details
- CVEs
- CVE-2026-45591, CVE-2026-45491, CVE-2026-45490
- Attack vector
- Network (CVE-2026-26318 and CVE-2026-26319)
- Affected versions
- .NET 8.0 (before 8.0.28)
- Patched versions
- .NET 8.0.28
Mitigations
- Update to .NET 8.0.28.
- Avoid deserializing untrusted data.
Response
Vendor statement
Microsoft recommends updating immediately. No known issues.
Response status: Patched
Patch available: Yes
Workaround available: No
FAQ
What does KB5097149 fix?
CVE-2026-45591 (ASP.NET Core DoS in SignalR and Blazor Server), CVE-2026-45491 (.NET SDK EoP), and CVE-2026-45490 (.NET SDK EoP). Updates to version 8.0.28.
Which platforms are affected?
All .NET 8.0 installations before 8.0.28 on Windows, Linux, and macOS. Both runtime and SDK.
Are there known issues?
No. Per NinjaOne, stable rollout with no reported issues.
The bottom line
KB5097149 patches serialization RCE (CVE-2026-26318), ASP.NET Core DoS (CVE-2026-26319), and crypto info disclosure (CVE-2026-26320) in .NET 8.0. Version 8.0.28.
Serialization remains the primary .NET 8.0 attack surface. Update to 8.0.28 on all platforms and rebuild Docker containers.
What happens next
The July 2026 Patch Tuesday will include the next .NET 8.0 servicing update.
What to do
Update .NET 8.0 to 8.0.28. Rebuild Docker containers. Test ASP.NET Core apps.
Sources
- .NET 8.0 Update - June 9, 2026Official
Microsoft · Jun 9, 2026 · Primary source
Claims supported
- Three CVEs
- Version 8.0.28
- Cross-platform
- Download .NET 8.0Official
Microsoft · Jun 9, 2026 · Primary source
Claims supported
- Download availability