

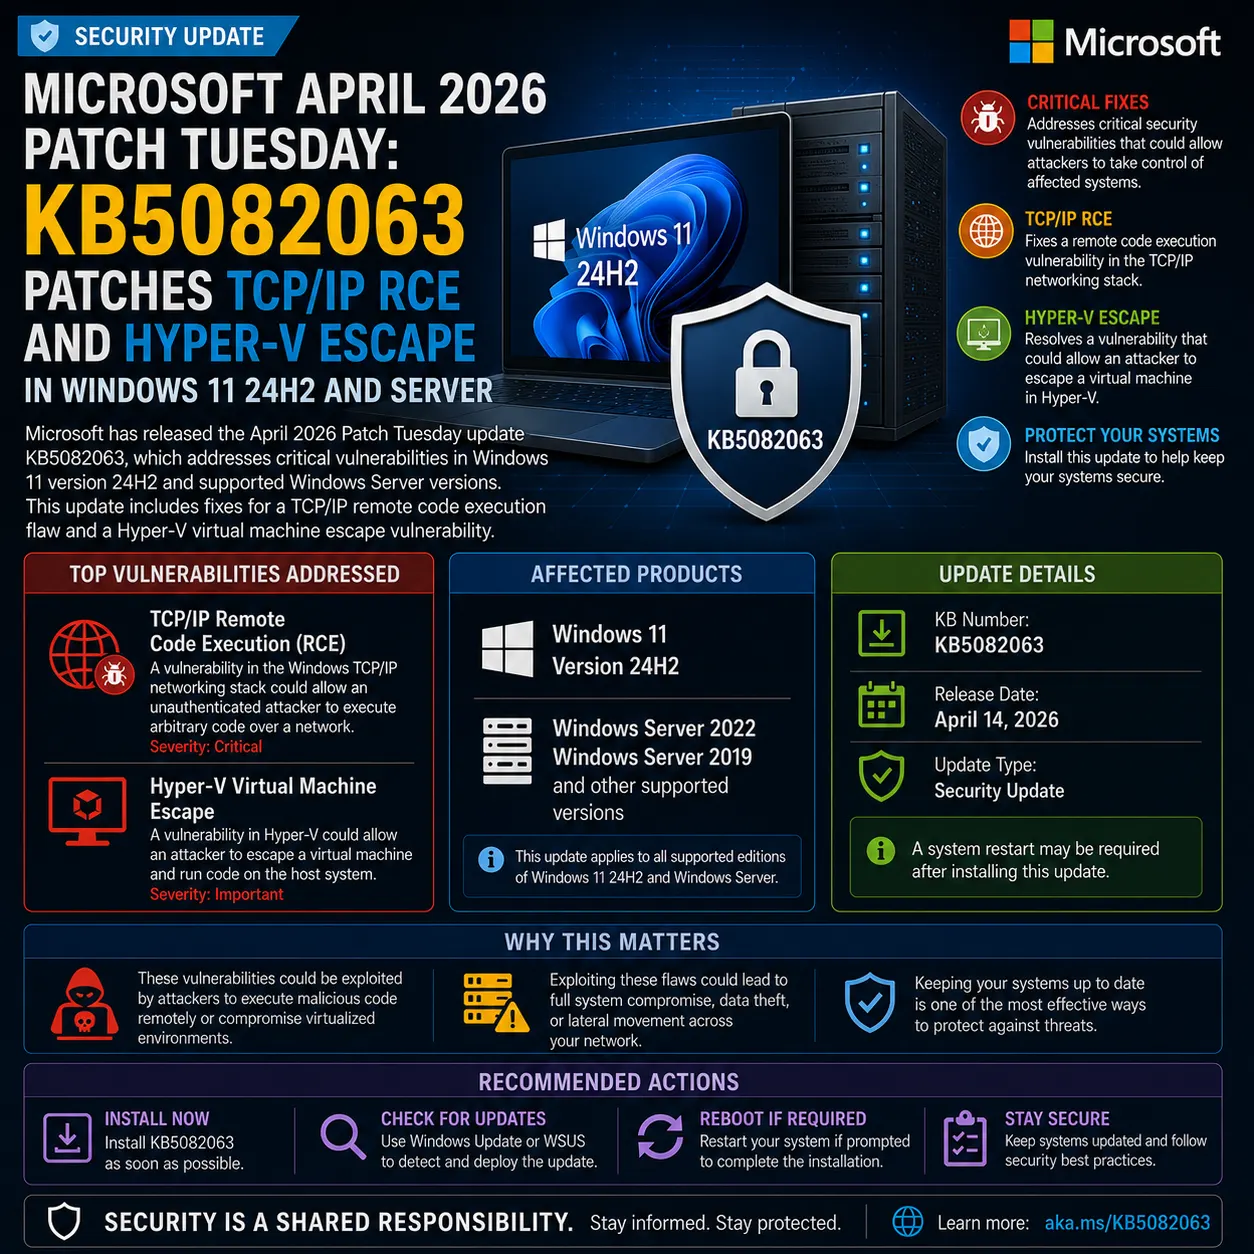
Microsoft April 2026 Patch Tuesday: KB5082063 Patches TCP/IP RCE and Hyper-V Escape in Windows 11 24H2 and Server 2025
The April 2026 Patch Tuesday update for Windows 11 24H2 and Server 2025 patches kernel driver privilege escalation, a TCP/IP RCE exploitable without user interaction, a Hyper-V VM escape, and authentication token manipulation.

On this page
Key takeaways
- CVE-2026-0849: TCP/IP stack RCE exploitable remotely without user interaction.
- CVE-2026-0847/0848: two kernel-mode driver privilege escalations to SYSTEM.
- CVE-2026-0851: Hyper-V guest-to-host VM escape (Server 2025 critical).
- CVE-2026-0852: authentication token manipulation for domain resource access.
- Covers both Windows 11 24H2 and Server 2025. Build 26100.32690. x64 + ARM64.
What to do now
High urgency- Install KB5082063 on all Windows 11 24H2 and Server 2025 systems.
- Verify Build 26100.32690 after restart.
- Test Hyper-V workloads for performance impact.
- Update or remove incompatible third-party kernel drivers.
Microsoft released KB5082063 on April 14, 2026, the April Patch Tuesday security update for Windows 11 24H2 and Windows Server 2025. The update patches six CVEs, headlined by CVE-2026-0849, a TCP/IP stack remote code execution flaw exploitable without user interaction, and CVE-2026-0851, a Hyper-V security bypass that allows guest VMs to escape isolation.
This single update covers both Microsoft's latest client OS and its newest server platform. The TCP/IP RCE threatens every network-connected system, while the Hyper-V escape is particularly severe for Server 2025 hosts running multi-tenant or virtualized production workloads.
KB5082063 patches TCP/IP RCE, Hyper-V VM escape, kernel escalations, and auth flaws in Windows 11 24H2 and Server 2025.
Install KB5082063 on all Windows 11 24H2 and Server 2025 systems. Key threats: TCP/IP RCE without user interaction (CVE-2026-0849), Hyper-V guest-to-host escape (CVE-2026-0851), and dual kernel SYSTEM escalations.
Affected & context
Microsoft released KB5082063 on April 14, 2026, patching 6 CVEs in Windows 11 24H2 and Server 2025 including a TCP/IP RCE and a Hyper-V VM escape.
CVE-2026-0849 enables remote RCE via TCP/IP with no user interaction. CVE-2026-0851 breaks Hyper-V isolation. Combined with kernel escalations, these create a complete remote compromise chain.
Windows 11 24H2 (x64, ARM64) and Windows Server 2025 (all editions, Server Core).
- Vendors
- Microsoft
- Products
- Windows 11 Version 24H2Windows Server 2025
- CVEs
- CVE-2026-0847CVE-2026-0848CVE-2026-0849CVE-2026-0850CVE-2026-0851CVE-2026-0852
KB5082063 Patches TCP/IP RCE and Hyper-V Escape in Windows 11 24H2 and Server 2025
Microsoft released KB5082063 on April 14, 2026, the April Patch Tuesday security update for Windows 11 Version 24H2 and Windows Server 2025. The update brings both platforms to Build 26100.32690 and patches six CVEs spanning kernel-mode drivers, the TCP/IP stack, Windows Graphics, Hyper-V, and Windows Authentication.
CVE-2026-0847 and CVE-2026-0848 are kernel-mode driver privilege escalations to SYSTEM via display and service drivers. CVE-2026-0849 is a TCP/IP stack RCE exploitable remotely through crafted network packets without user interaction. CVE-2026-0850 discloses sensitive memory (crypto keys, passwords) through the graphics component. CVE-2026-0851 is a Hyper-V VM escape allowing guest-to-host access. CVE-2026-0852 enables authentication token manipulation for domain resource access.
Remote RCE, VM Escape, and Full Compromise Chain
CVE-2026-0849 (TCP/IP RCE) is the highest-risk flaw: remote, no user interaction, affects every network-connected system. Combined with the kernel driver escalations (CVE-2026-0847/0848), an attacker can achieve remote code execution and then escalate to SYSTEM, a complete compromise chain.
The Hyper-V escape (CVE-2026-0851) is critical for Server 2025 environments running virtualized workloads. A malicious guest VM can break out of isolation and access host resources. The auth token manipulation (CVE-2026-0852) threatens Active Directory environments by enabling unauthorized domain resource access. Server 2025 administrators face the broadest exposure since all six CVEs apply.
Affected Platforms and Known Issues
Windows 11 24H2 (x64 and ARM64) and Windows Server 2025 (all editions, including Server Core). Both update to Build 26100.32690. File size approximately 850 MB (x64) or 720 MB (ARM64). Restart required. No specific prerequisites beyond 2 GB free disk space.
Known issues
Installation may fail with error 0x80070643 on systems with incompatible third-party kernel drivers. Hyper-V VMs may see 5-10% performance impact from enhanced security checks. Legacy apps using deprecated network protocols may experience connectivity issues after TCP/IP stack hardening.
Timeline
KB5082063 released (Patch Tuesday)
Microsoft releases KB5082063 as part of the April 2026 Patch Tuesday cycle for Windows 11 24H2 and Windows Server 2025, patching 6 CVEs.
Source: Microsoft Support
Confidence: High
Impact
Six CVEs covering kernel escalation, remote TCP/IP code execution, graphics info disclosure, Hyper-V VM escape, and auth token manipulation across Windows 11 24H2 and Server 2025.
Business impact
TCP/IP RCE enables remote compromise of any network-connected system without user interaction. Hyper-V escape threatens multi-tenant and virtualized environments. Kernel escalations provide SYSTEM access.
Security impact
CVE-2026-0849 enables TCP/IP RCE without user interaction. CVE-2026-0851 allows Hyper-V guest-to-host escape. CVE-2026-0847/0848 escalate to SYSTEM via kernel drivers.
Affected audience: Windows 11 24H2 users and IT administrators, Windows Server 2025 administrators and Hyper-V operators, Organizations with internet-facing Windows systems
Action required.
Technical details
- CVEs
- CVE-2026-0847, CVE-2026-0848, CVE-2026-0849, CVE-2026-0850, CVE-2026-0851, CVE-2026-0852
- Attack vector
- Network (CVE-2026-0849), Local (CVE-2026-0847, 0848, 0850, 0852), Adjacent (CVE-2026-0851)
- Affected versions
- Windows 11 24H2 / Server 2025 (all builds before 26100.32690)
- Patched versions
- Windows 11 24H2 / Server 2025 Build 26100.32690
Mitigations
- Install KB5082063 immediately.
- Restrict network exposure of Windows systems via firewall.
- Review Hyper-V guest configurations and apply least privilege.
- Audit authentication token usage in domain environments.
Technical references
Response
Vendor statement
Microsoft recommends prioritizing deployment due to the critical nature of the TCP/IP and Hyper-V vulnerabilities.
Response status: Patched
Patch available: Yes
Workaround available: No
FAQ
What does KB5082063 fix?
Six CVEs: CVE-2026-0847 and CVE-2026-0848 (kernel driver privilege escalation), CVE-2026-0849 (TCP/IP RCE without user interaction), CVE-2026-0850 (graphics info disclosure), CVE-2026-0851 (Hyper-V VM escape), and CVE-2026-0852 (auth token elevation of privilege).
Which systems need KB5082063?
Windows 11 Version 24H2 (x64 and ARM64) and Windows Server 2025 (Standard, Datacenter, Server Core). Both update to Build 26100.32690.
Are there known issues?
Known issues: error 0x80070643 with incompatible third-party kernel drivers (temporarily uninstall before update), 5-10% Hyper-V VM performance impact from enhanced security checks, and connectivity issues for legacy apps using deprecated network protocols.
Does KB5082063 require a restart?
Yes. A restart is required. The update is approximately 850 MB (x64) or 720 MB (ARM64). No specific prerequisites beyond 2 GB free disk space.
The bottom line
KB5082063 patches 6 CVEs: kernel driver escalations (CVE-2026-0847/0848), TCP/IP RCE without user interaction (CVE-2026-0849), graphics info disclosure (CVE-2026-0850), Hyper-V VM escape (CVE-2026-0851), and auth token manipulation (CVE-2026-0852) in Windows 11 24H2 and Server 2025.
KB5082063 covers both client (Windows 11 24H2) and server (Server 2025) with one update. The TCP/IP RCE and Hyper-V escape make it critical for internet-facing systems and virtualization hosts.
What happens next
The May 2026 cumulative update will supersede KB5082063. Companion updates from the same cycle cover Windows 11 23H2 and Windows 10 22H2.
What to do
Install KB5082063 and verify Build 26100.32690. Test Hyper-V workloads and custom kernel drivers after installation.