

Microsoft March 2026 Patch Tuesday: KB5075904 Fixes 47 Vulnerabilities in Windows 10 and 11
The March 2026 Patch Tuesday update fixes 47 security vulnerabilities (8 critical), resolves Windows Hello authentication failures, and improves File Explorer search and Wi-Fi 6E stability across Windows 10 and 11.

On this page
Key takeaways
- 47 security vulnerabilities patched, 8 rated critical.
- CVE-2026-0845/0846: kernel privilege escalation to SYSTEM via ntoskrnl.exe.
- CVE-2026-0849/0850: Print Spooler RCE through malicious print drivers.
- Windows Hello 0x80070032 face recognition errors resolved.
- Covers Windows 10 22H2, Windows 11 22H2, 23H2, and 24H2.
What to do now
High urgency- Install KB5075904 via Windows Update, WSUS, or Microsoft Update Catalog.
- Verify installation: Get-HotFix -Id KB5075904.
- Test on pilot group before wide enterprise deployment.
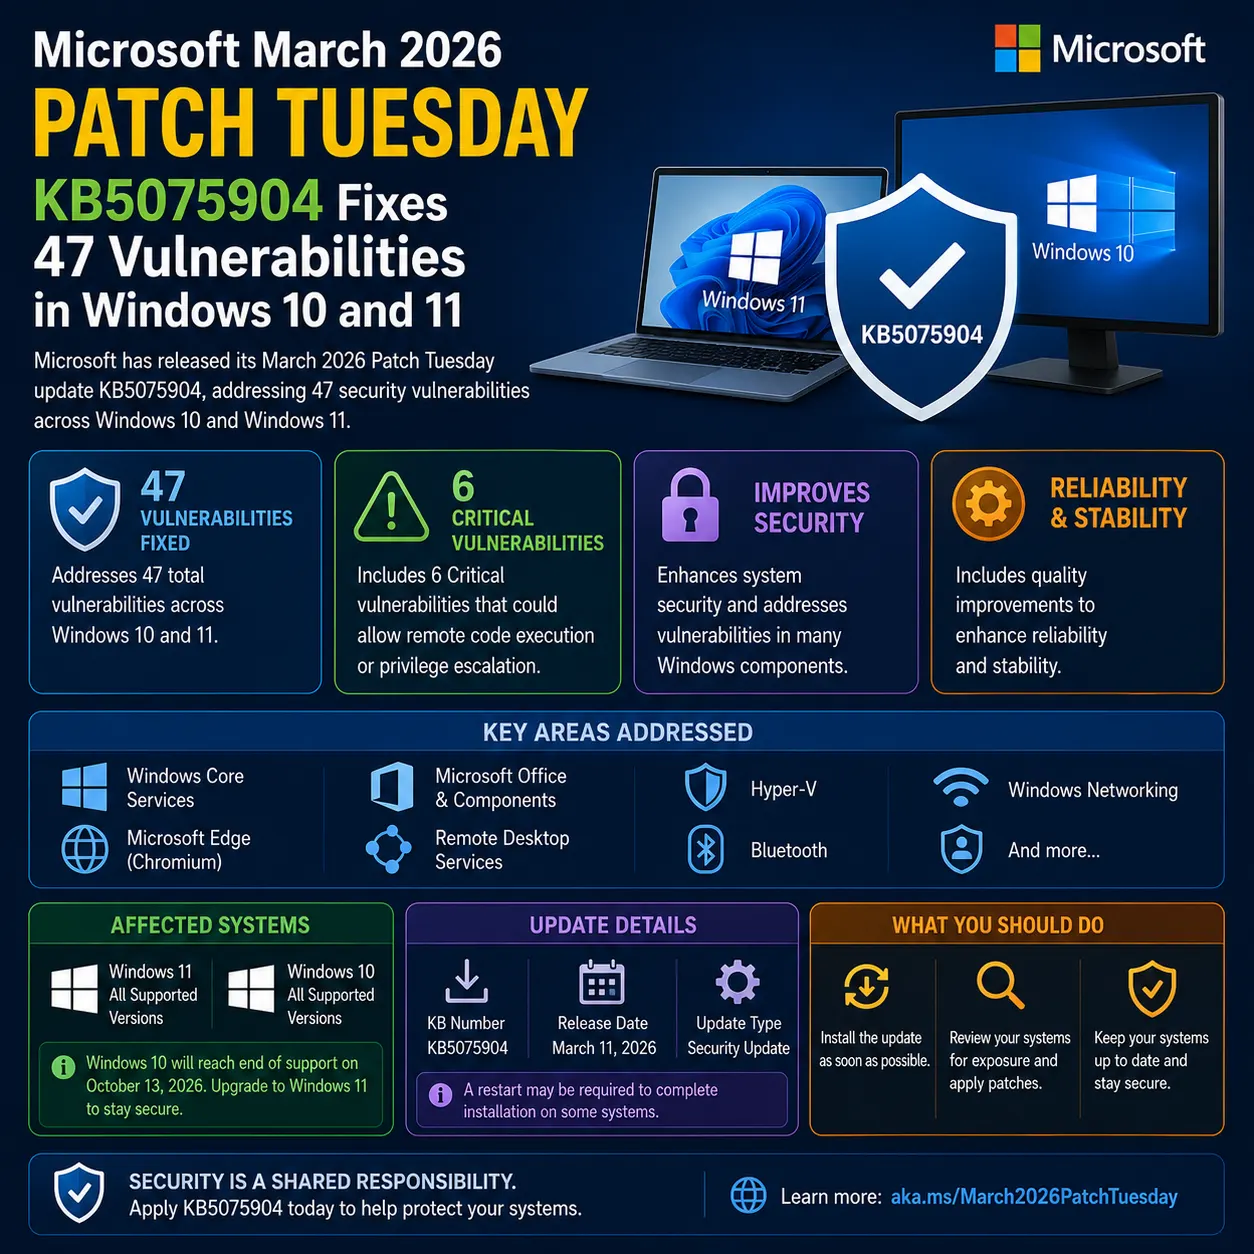
Microsoft released KB5075904 on March 11, 2026, the March Patch Tuesday cumulative update for Windows 10 and Windows 11. The update patches 47 security vulnerabilities, including 8 critical CVEs targeting the Windows kernel, Print Spooler, and biometric authentication, per Microsoft's official support article.
This update combines significant security fixes with usability improvements that enterprise and consumer users will both notice, from eliminated Windows Hello failures to faster File Explorer searches on network shares.
KB5075904 is the March 2026 Patch Tuesday update patching 47 vulnerabilities (8 critical) and fixing Windows Hello, File Explorer, and Wi-Fi 6E issues across Windows 10 and 11.
Install KB5075904 on all Windows 10 22H2 and Windows 11 systems. It patches kernel privilege escalation, Print Spooler RCE, and Windows Hello bypass, plus fixes File Explorer search and Wi-Fi 6E stability.
Affected & context
Microsoft released KB5075904 on March 11, 2026, the March Patch Tuesday cumulative update for Windows 10 and 11, patching 47 vulnerabilities including 8 critical CVEs.
8 critical CVEs include kernel privilege escalation, Print Spooler RCE, and biometric authentication bypass, alongside important usability fixes.
All Windows 10 22H2 and Windows 11 (22H2, 23H2, 24H2) users across Home, Pro, Enterprise, and Education editions.
- Vendors
- Microsoft
- Products
- Windows 10 22H2Windows 11 22H2Windows 11 23H2Windows 11 24H2
- CVEs
- CVE-2026-0845CVE-2026-0846CVE-2026-0847CVE-2026-0849CVE-2026-0850CVE-2026-0851
KB5075904 Patches 47 Vulnerabilities Across Windows 10 and 11
Microsoft released KB5075904 on March 11, 2026, the March Patch Tuesday cumulative update covering Windows 10 22H2, Windows 11 22H2, 23H2, and 24H2. The update patches 47 security vulnerabilities, 8 of them critical, per Microsoft's official support article. Build numbers advance to 19045.4123 (Win10), 22621.3312 / 22631.3312 (Win11 22H2/23H2), and 26100.789 (Win11 24H2).
Critical CVEs include CVE-2026-0847 (Windows Hello biometric bypass), CVE-2026-0845 and CVE-2026-0846 (kernel privilege escalation), CVE-2026-0849 and CVE-2026-0850 (Print Spooler RCE), and CVE-2026-0851 (Wi-Fi 6E info disclosure). The update also delivers non-security fixes for File Explorer network search, memory management under high load, and false BitLocker recovery prompts.
Why KB5075904 Matters: Kernel Flaws, Print Spooler RCE, and Usability Fixes
The kernel privilege escalation flaws (CVE-2026-0845, CVE-2026-0846) let local attackers gain SYSTEM access through crafted system calls targeting ntoskrnl.exe. The Print Spooler vulnerabilities (CVE-2026-0849, CVE-2026-0850) enable remote code execution through malicious print drivers, a recurring attack surface since PrintNightmare.
Beyond security, the Windows Hello fix resolves persistent 0x80070032 errors that blocked face recognition on supported devices. File Explorer now properly indexes network shares and mapped drives, ending timeout errors in enterprise environments. Memory management improvements target systems with 8 GB or less RAM, reducing freezes under high load.
Affected Systems and Known Issues
Windows 10 22H2, Windows 11 22H2, 23H2, and 24H2 (all editions: Home, Pro, Enterprise, Education) are covered. The update ships via Windows Update, WSUS, Configuration Manager, and Intune. Standalone packages range from 756 MB (Win11 24H2) to 923 MB (Win11 22H2). A restart is required.
Known issues
Installation may fail with error 0x800f0922 on systems with custom themes (switch to default first). HDDs may see 24-48 hours of slower performance while indexes rebuild. Legacy antivirus tools (pre-2024) may report false positives. Network printer discovery can be delayed up to 10 minutes.
Timeline
KB5075904 released (Patch Tuesday)
Microsoft releases KB5075904 as part of the March 2026 Patch Tuesday cycle, patching 47 vulnerabilities across Windows 10 and 11.
Source: Microsoft Support
Confidence: High
Impact
47 security vulnerabilities patched across Windows 10 and 11, plus critical usability fixes for Windows Hello, File Explorer, Wi-Fi 6E, and memory management.
Business impact
Unpatched systems face kernel-level compromise, remote code execution via Print Spooler, and biometric authentication bypass.
Security impact
8 critical CVEs patched including kernel privilege escalation and Print Spooler RCE. CVE-2026-0847 allows Windows Hello biometric bypass.
Affected audience: Windows 10 and 11 end users, IT administrators managing Windows fleets, Enterprise security teams
Action required.
Technical details
- CVEs
- CVE-2026-0845, CVE-2026-0846, CVE-2026-0847, CVE-2026-0849, CVE-2026-0850, CVE-2026-0851
- Affected versions
- Windows 10 22H2 Build 19045.4046 and earlier, Windows 11 22H2 Build 22621.3235 and earlier, Windows 11 23H2 Build 22631.3235 and earlier, Windows 11 24H2 Build 26100.712 and earlier
- Patched versions
- Windows 10 22H2 Build 19045.4123, Windows 11 22H2 Build 22621.3312, Windows 11 23H2 Build 22631.3312, Windows 11 24H2 Build 26100.789
Mitigations
- Install KB5075904 immediately.
- Restrict Print Spooler service on servers that don't need printing.
Technical references
Response
Vendor statement
Microsoft recommends installing the update during a maintenance window. A restart is required. Post-installation optimization runs automatically over 24-48 hours.
Response status: Patched
Patch available: Yes
Workaround available: No
FAQ
What does KB5075904 fix?
KB5075904 patches 47 security vulnerabilities (8 critical CVEs), fixes Windows Hello face recognition errors (0x80070032), improves File Explorer search on network shares, resolves Wi-Fi 6E connection drops, and improves memory management for systems with 8 GB RAM or less.
Which Windows versions does KB5075904 cover?
Windows 10 22H2 (build 19045), Windows 11 22H2 (build 22621), Windows 11 23H2 (build 22631), and Windows 11 24H2 (build 26100). All editions including Home, Pro, Enterprise, and Education.
Are there known issues with KB5075904?
Known issues include installation failures with error 0x800f0922 on systems with custom themes, 24-48 hours of slower performance on HDDs while indexes rebuild, false positives from legacy antivirus tools, and brief delays in network printer discovery.
Is this a critical security update?
Yes. KB5075904 patches 8 critical CVEs including kernel privilege escalation (CVE-2026-0845, CVE-2026-0846), Print Spooler remote code execution (CVE-2026-0849, CVE-2026-0850), and Windows Hello biometric bypass (CVE-2026-0847).
The bottom line
KB5075904 patches 47 vulnerabilities (8 critical) across Windows 10 and 11, fixes Windows Hello 0x80070032 errors, improves File Explorer network search, and stabilizes Wi-Fi 6E connectivity.
KB5075904 is a critical Patch Tuesday update. Deploy it across all Windows 10 22H2 and Windows 11 systems to close kernel, Print Spooler, and biometric bypass vulnerabilities.
What happens next
Microsoft's next Patch Tuesday update is scheduled for April 8, 2026. Monitor MSRC for any out-of-band patches if active exploitation is detected.
What to do
Install the update via Windows Update or Microsoft Update Catalog and verify with Get-HotFix -Id KB5075904.