

Microsoft May 2026 Patch Tuesday: KB5087537 Fixes RDP RCE and Kernel Flaws in Windows 10 1607 and Server 2016
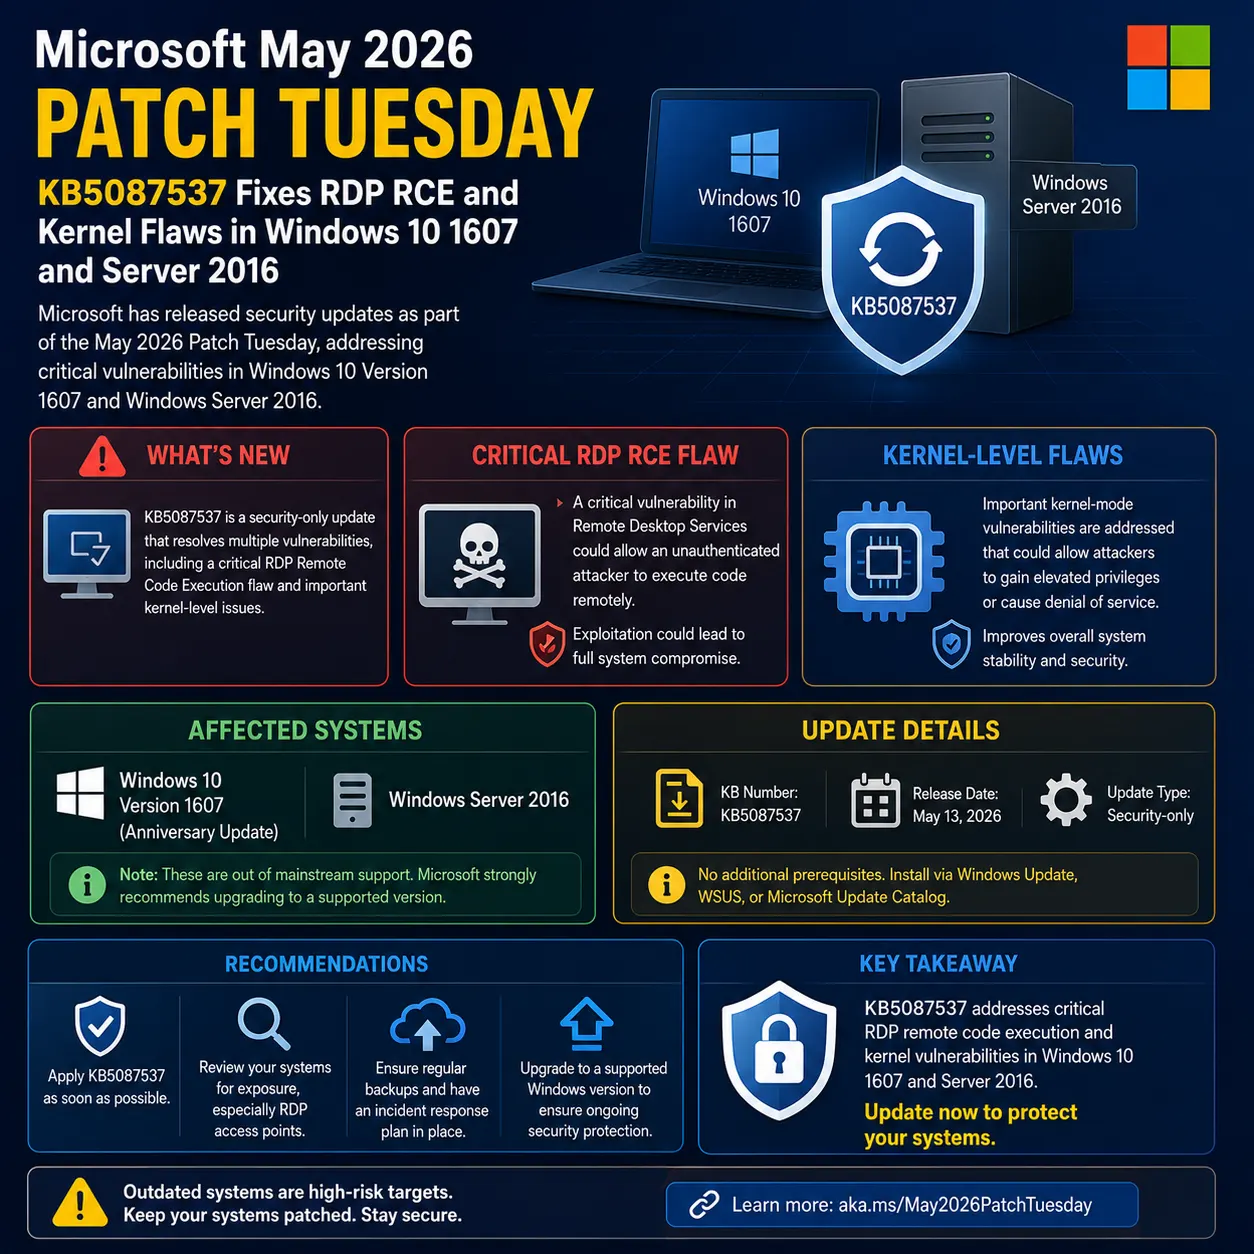
The May 2026 Patch Tuesday update for Windows 10 1607 and Server 2016 patches kernel privilege escalation, RDP remote code execution, graphics component flaws, MSMQ RCE, and Print Spooler vulnerabilities.

On this page
Key takeaways
- Kernel privilege escalation fixes close multiple paths from standard user to SYSTEM.
- RDP RCE allows remote code execution via crafted requests without user interaction.
- MSMQ RCE enables code execution through malicious queue messages.
- GDI memory corruption exploitable via malformed graphics files.
- Covers Windows 10 1607 (32-bit/x64) and Server 2016 (all editions). Build 14393.9140.
What to do now
High urgency- Install KB5087537 on all Windows 10 1607 and Server 2016 systems.
- Verify Build 14393.9140 after restart.
- Restrict RDP access to trusted networks or VPN only.
- Disable MSMQ and Print Spooler on servers where not needed.
Microsoft released KB5087537 on May 12, 2026, the May Patch Tuesday security update for Windows 10 Version 1607 and Windows Server 2016. The update patches vulnerabilities across five Windows components: the kernel, Remote Desktop Services, Windows Graphics (GDI), Microsoft Message Queuing, and the Print Spooler.
Windows 10 1607 and Server 2016 are legacy platforms past mainstream support but still widely deployed. The RDP RCE combined with kernel escalation provides a full remote compromise chain, making this update critical for any organization that hasn't yet migrated.
KB5087537 patches kernel EoP, RDP RCE, GDI, MSMQ, and Print Spooler flaws in Windows 10 1607 and Server 2016.
Install KB5087537 on all Windows 10 1607 and Server 2016 systems. Patches RDP RCE, kernel escalation, MSMQ RCE, GDI corruption, and Print Spooler flaws. Build 14393.9140.
Affected & context
Microsoft released KB5087537 on May 12, 2026, patching kernel, RDP, GDI, MSMQ, and Print Spooler vulnerabilities in Windows 10 1607 and Server 2016.
RDP RCE enables remote compromise. Kernel EoP provides SYSTEM access. MSMQ RCE threatens messaging infrastructure. All on a widely deployed legacy platform.
Windows 10 1607 (32-bit/x64) and Windows Server 2016 (Standard, Datacenter, Server Core).
- Vendors
- Microsoft
- Products
- Windows 10 Version 1607Windows Server 2016
KB5087537 Patches Kernel, RDP, MSMQ, and Print Spooler Flaws in Windows 10 1607 and Server 2016
Microsoft released KB5087537 on May 12, 2026, the May Patch Tuesday security update for Windows 10 Version 1607 and Windows Server 2016. The update brings both platforms to Build 14393.9140 and patches vulnerabilities across five core Windows components: kernel, Remote Desktop Services, graphics (GDI), Microsoft Message Queuing (MSMQ), and the Print Spooler.
The kernel fixes address multiple privilege escalation paths from standard user to SYSTEM through memory management flaws. The RDP vulnerabilities enable remote code execution via crafted RDP requests without user interaction. The MSMQ flaws allow RCE through malicious queue messages. The GDI issues can be exploited via malformed graphics files. The Print Spooler patches close both escalation and RCE vectors through driver validation weaknesses.
RDP RCE and Kernel Escalation on Legacy Platforms
Windows 10 1607 and Server 2016 are legacy platforms still widely deployed in enterprises. The RDP RCE is the highest-risk flaw: remote, no user interaction required, and RDP is commonly exposed. Combined with kernel escalation, an attacker can achieve full remote compromise.
The MSMQ RCE affects organizations using message queuing for application integration, a pattern common in financial services and manufacturing. The Print Spooler continues to be a persistent attack surface, with new escalation and RCE vectors in every patch cycle. Server 2016 domain controllers and file servers are the most critical targets.
Affected Systems and Known Issues
Windows 10 Version 1607 (32-bit and x64) and Windows Server 2016 (including Server Core). Build updates to 14393.9140. File size approximately 1.2 GB (x64) or 950 MB (x86). Restart required. Available via Windows Update, WSUS, SCCM, and Microsoft Update Catalog.
Known issues
Installation may fail with less than 2 GB free disk space. Temporary performance impact on first boot after installation. Some third-party drivers may need updates for compatibility with the security enhancements.
Timeline
KB5087537 released (Patch Tuesday)
Microsoft releases KB5087537 as part of the May 2026 Patch Tuesday cycle for Windows 10 1607 and Windows Server 2016.
Source: Microsoft Support
Confidence: High
Impact
Five vulnerability categories across kernel, RDP, graphics, MSMQ, and Print Spooler in Windows 10 1607 and Server 2016.
Business impact
RDP RCE enables remote compromise without user interaction. Kernel escalation provides SYSTEM access. MSMQ RCE threatens message queuing infrastructure. Print Spooler remains a persistent attack vector.
Security impact
RDP RCE enables remote code execution via crafted RDP requests. Kernel escalation grants SYSTEM from standard user. MSMQ RCE allows code execution through malicious queue messages.
Affected audience: Windows 10 1607 and Server 2016 administrators, Organizations with RDP-exposed legacy servers, Environments using MSMQ for application integration
Action required.
Technical details
- Attack vector
- Network (RDP, MSMQ), Local (Kernel, Print Spooler, GDI)
- Affected versions
- Windows 10 1607 / Server 2016 (all builds before 14393.9140)
- Patched versions
- Windows 10 1607 / Server 2016 Build 14393.9140
Mitigations
- Install KB5087537 immediately.
- Restrict RDP exposure via firewall or VPN.
- Disable MSMQ on servers that don't use message queuing.
- Disable Print Spooler on servers that don't need printing.
Technical references
Response
Vendor statement
Microsoft recommends installing this update during planned maintenance windows. A system restart is required.
Response status: Patched
Patch available: Yes
Workaround available: No
FAQ
What does KB5087537 fix?
Kernel privilege escalation, RDP remote code execution, Windows Graphics (GDI) memory corruption, MSMQ remote code execution, and Print Spooler privilege escalation and RCE vulnerabilities. Updates Build to 14393.9140.
Which systems need KB5087537?
Windows 10 Version 1607 (32-bit and x64) and Windows Server 2016 (Standard, Datacenter, Server Core). All editions on both platforms.
Are there known issues?
Known issues: installation failure with less than 2 GB free disk space, temporary performance impact on first boot, and possible third-party driver compatibility issues.
Does KB5087537 require a restart?
Yes. File size is approximately 1.2 GB (x64) or 950 MB (x86). A restart is required. Plan installation during a maintenance window.
The bottom line
KB5087537 patches kernel privilege escalation, RDP remote code execution, GDI memory corruption, MSMQ RCE, and Print Spooler vulnerabilities in Windows 10 1607 and Server 2016, updating to Build 14393.9140.
KB5087537 covers five attack surfaces on a legacy platform still widely deployed. The RDP RCE and kernel escalation combination is the most urgent. Plan migration to a supported version while keeping current with patches.
What happens next
The June 2026 update KB5094122 supersedes KB5087537 for Windows 10 1607 and Server 2016. Plan migration to Server 2022 or 2025.
What to do
Install KB5087537 and verify Build 14393.9140. Restrict RDP exposure. Disable MSMQ and Print Spooler where not needed.