

Microsoft Patches Critical .NET 8.0 JSON Deserialization RCE in KB5086096
The April 2026 .NET 8.0 security update patches a CVSS 9.8 RCE in System.Text.Json, an SDK privilege escalation via NuGet, and an ASP.NET Core info disclosure flaw across all platforms.

On this page
Key takeaways
- CVE-2026-0145 is a CVSS 9.8 RCE in System.Text.Json polymorphic type handling.
- CVE-2026-0146 allows SDK privilege escalation during NuGet package restoration.
- CVE-2026-0147 leaks sensitive config data through ASP.NET Core error messages.
- All .NET 8.0 versions 8.0.0-8.0.4 are affected on Windows, Linux, and macOS.
- Update brings .NET 8.0 to version 8.0.5.26084. No restart needed for runtime-only installs.
What to do now
High urgency- Update .NET 8.0 to version 8.0.5 on all systems.
- Rebuild Docker containers with updated .NET 8.0 base images.
- Review custom JsonConverter implementations for compatibility.
- Verify ASP.NET Core production apps don't expose detailed error messages.
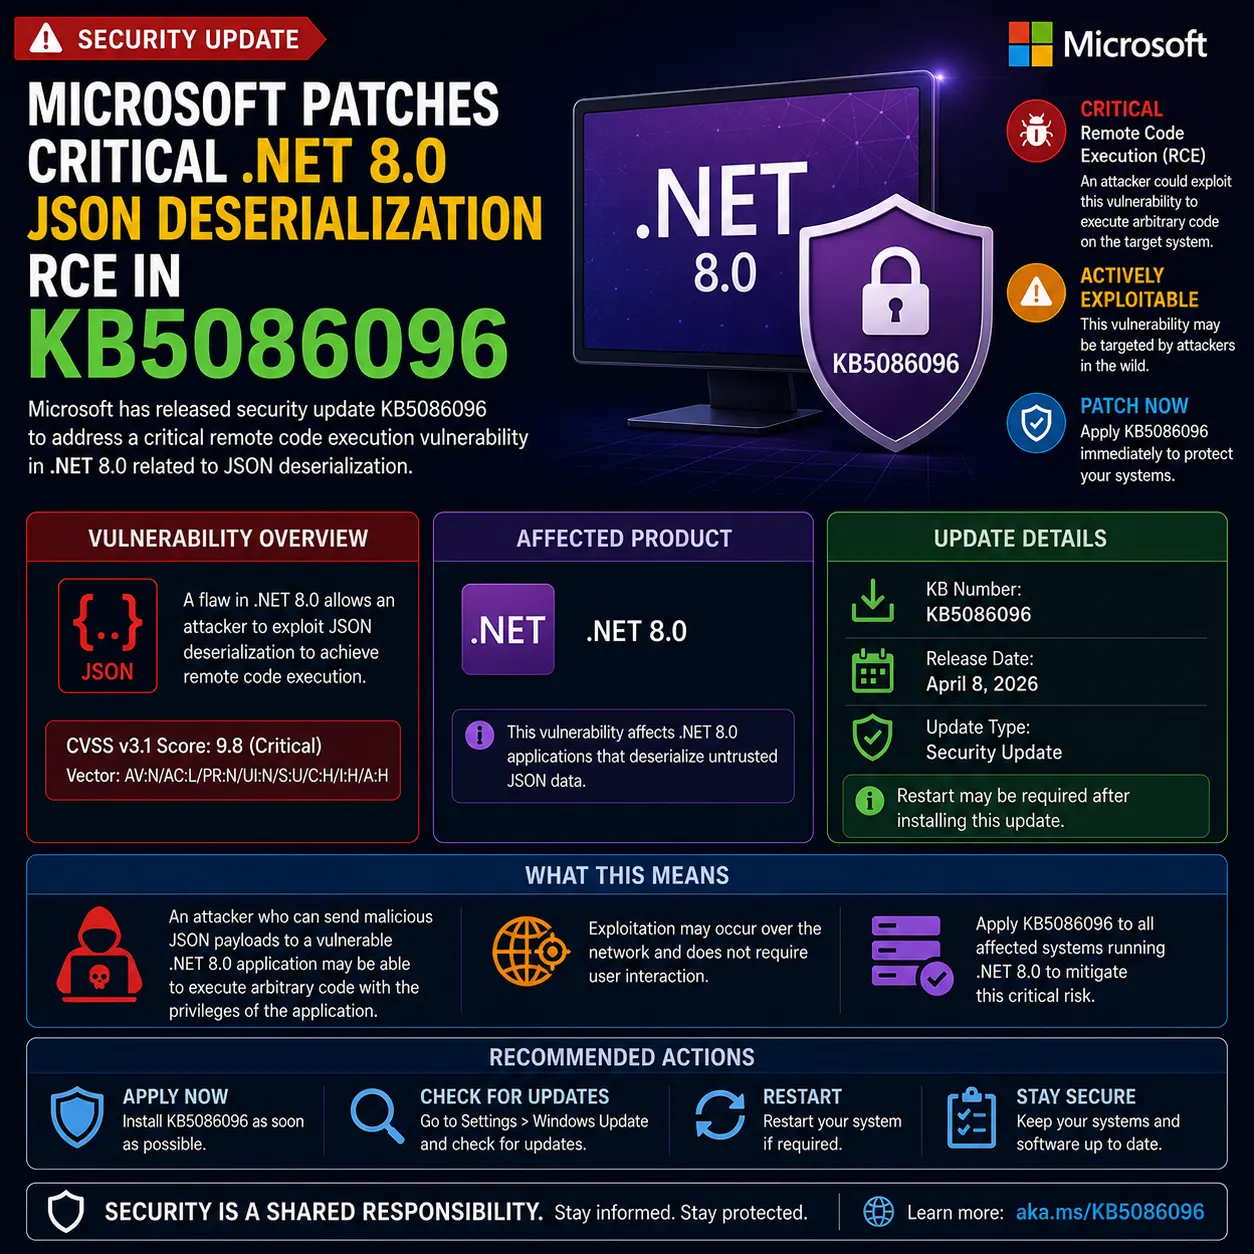
Microsoft released KB5086096 on April 16, 2026, a critical security update for .NET 8.0 that patches three vulnerabilities in the runtime, SDK, and ASP.NET Core. The most severe, CVE-2026-0145, carries a CVSS 9.8 score and allows remote code execution through crafted JSON data sent to applications using System.Text.Json deserialization.
The update affects the most widely used JSON library in the .NET ecosystem. Any .NET 8.0 application that processes untrusted JSON input is a potential target, making this update urgent for both development environments and production deployments.
KB5086096 patches a CVSS 9.8 RCE in .NET 8.0's System.Text.Json, plus SDK privilege escalation and ASP.NET Core info disclosure flaws.
Update .NET 8.0 to version 8.0.5 now. CVE-2026-0145 enables RCE through JSON deserialization. Also fixes NuGet-based SDK escalation and ASP.NET Core config leaks.
Affected & context
Microsoft released KB5086096 on April 16, 2026, patching three security vulnerabilities in .NET 8.0 runtime and SDK, including a CVSS 9.8 RCE in System.Text.Json.
CVE-2026-0145 targets System.Text.Json, the default JSON library in .NET 8.0. Any application deserializing untrusted JSON is at risk of remote code execution.
Developers and operators running .NET 8.0 runtime or SDK versions 8.0.0-8.0.4 on Windows, Linux, or macOS.
- Vendors
- Microsoft
- Products
- .NET 8.0 Runtime.NET 8.0 SDKASP.NET Core 8.0
- CVEs
- CVE-2026-0145CVE-2026-0146CVE-2026-0147
KB5086096 Patches CVSS 9.8 RCE and Two More .NET 8.0 Flaws
Microsoft released KB5086096 on April 16, 2026, a security update for .NET 8.0 runtime and SDK that patches three CVEs and addresses garbage collector memory corruption and NuGet package validation weaknesses. The update brings .NET 8.0 to version 8.0.5.26084 across Windows, Linux, and macOS.
CVE-2026-0145 is the most critical flaw (CVSS 9.8): a remote code execution vulnerability in System.Text.Json's polymorphic type handling. Attackers can execute arbitrary code by sending crafted JSON to applications that deserialize untrusted input. CVE-2026-0146 is an SDK privilege escalation exploitable during NuGet package restoration. CVE-2026-0147 leaks sensitive config data (connection strings, API keys) through ASP.NET Core error messages.
Why KB5086096 Matters: JSON RCE, Build Pipeline Risk, and Config Leaks
The System.Text.Json RCE (CVE-2026-0145) targets the most widely used JSON library in the .NET ecosystem. Any .NET 8.0 application processing untrusted JSON input is at risk, from web APIs to microservices. The vulnerability exploits insufficient validation in polymorphic type handling during deserialization.
The SDK privilege escalation (CVE-2026-0146) affects build pipelines and dev environments. Attackers can place malicious NuGet packages in local sources to gain elevated access during dotnet restore operations. The ASP.NET Core info disclosure (CVE-2026-0147) is lower severity but can expose database credentials and API keys through detailed error messages, especially in misconfigured production deployments.
Affected Versions and Deployment Details
All .NET 8.0 installations from version 8.0.0 through 8.0.4 are affected across Windows (x64, x86, ARM64), Linux (x64, ARM64), and macOS (x64, ARM64). The update ships via Windows Update, Microsoft Update Catalog, Visual Studio Installer, dotnet.microsoft.com, and platform package managers. No restart is required for runtime-only installations.
Known issues
Build times may increase 5-10 seconds due to enhanced NuGet validation. Custom JsonConverter implementations relying on undocumented behavior may break. Docker containers must be rebuilt with updated base images.
Timeline
KB5086096 released
Microsoft releases KB5086096, updating .NET 8.0 to version 8.0.5 with fixes for CVE-2026-0145, CVE-2026-0146, and CVE-2026-0147.
Source: .NET Release Notes
Confidence: High
Impact
Three security vulnerabilities in .NET 8.0 allow remote code execution, privilege escalation, and information disclosure across all supported platforms.
Business impact
Unpatched applications face remote code execution through JSON input, build pipeline compromise via NuGet, and config data leaks through error messages.
Security impact
CVE-2026-0145 (CVSS 9.8) allows RCE through crafted JSON data sent to any .NET 8.0 app deserializing untrusted input.
Affected audience: .NET 8.0 application developers, DevOps teams running .NET 8.0 in production, Organizations with .NET 8.0 containerized workloads
Action required.
Technical details
- CVEs
- CVE-2026-0145, CVE-2026-0146, CVE-2026-0147
- CVSS
- 9.8
- Attack vector
- Network (CVE-2026-0145), Local (CVE-2026-0146)
- Affected versions
- .NET 8.0.0-8.0.4 Runtime, .NET 8.0 SDK (all 8.0.x versions before 8.0.5)
- Patched versions
- .NET 8.0.5.26084
Mitigations
- Update to .NET 8.0.5 immediately.
- Review and restrict NuGet package sources in build pipelines.
- Ensure ASP.NET Core production apps disable detailed error pages.
Technical references
Response
Vendor statement
Microsoft recommends immediate deployment to all .NET 8.0 installations. Applications using affected components should be restarted after applying the update.
Response status: Patched
Patch available: Yes
Workaround available: No
FAQ
What does KB5086096 fix?
KB5086096 patches CVE-2026-0145 (System.Text.Json RCE, CVSS 9.8), CVE-2026-0146 (SDK privilege escalation via NuGet), CVE-2026-0147 (ASP.NET Core info disclosure), plus GC memory corruption fixes and NuGet validation improvements.
Which platforms are affected?
All .NET 8.0 runtime and SDK installations from version 8.0.0 through 8.0.4 on Windows (x64/x86/ARM64), Linux (x64/ARM64), and macOS (x64/ARM64). Both development and production environments.
Are there known issues?
Known issues: 5-10 second build time increase from NuGet validation, custom JsonConverter compatibility (workaround: set DOTNET_SYSTEM_TEXT_JSON_STRICT_VALIDATION=false temporarily), and Docker images needing rebuild.
Does KB5086096 require a restart?
No restart for runtime-only installations. Visual Studio restart required if SDK components are updated while the IDE is running. Applications using affected components should be restarted.
The bottom line
KB5086096 patches a CVSS 9.8 RCE in System.Text.Json, an SDK privilege escalation via NuGet, and an ASP.NET Core info disclosure flaw across Windows, Linux, and macOS.
Update all .NET 8.0 installations to version 8.0.5 immediately. The System.Text.Json RCE (CVSS 9.8) affects any application processing untrusted JSON input.
What happens next
Microsoft releases monthly .NET security updates. The companion update KB5086097 covers the same cycle for .NET 9.0.
What to do
Update .NET 8.0 runtime and SDK. Rebuild Docker containers. Review custom JsonConverter implementations for compatibility.