Microsoft released KB5078766 on March 10, 2026, a security update for Windows Server 2022 that patches four critical vulnerabilities. The most severe, CVE-2026-0847, allows unauthenticated remote code execution through the Windows RPC runtime with SYSTEM privileges, requiring no user interaction.
The combination of an unauthenticated RPC RCE and a Kerberos authentication bypass makes this update particularly urgent for domain controllers and any internet-facing Server 2022 infrastructure.
Key takeaways
- CVE-2026-0847: unauthenticated RPC RCE with SYSTEM privileges, no user interaction needed.
- CVE-2026-0851: Print Spooler privilege escalation from authenticated user to SYSTEM.
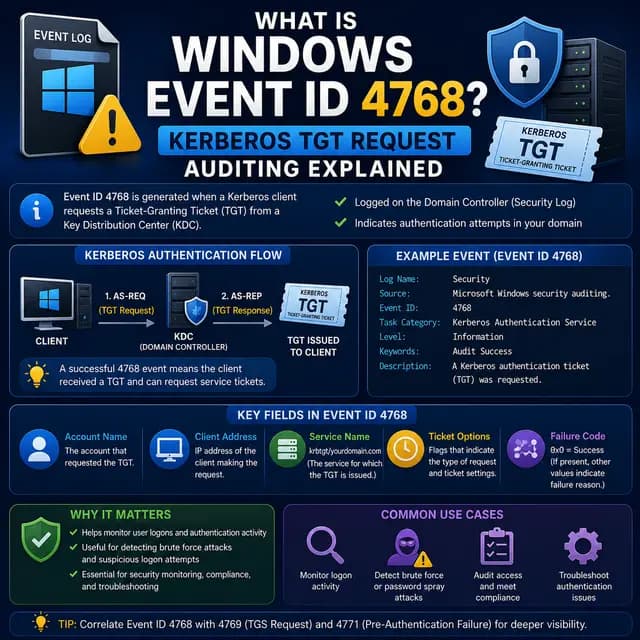
- CVE-2026-0863: Kerberos ticket validation bypass enabling domain user impersonation.
- CVE-2026-0871: kernel memory corruption leading to crashes or code execution.
- Updates Server 2022 to Build 20348.4893. Affects Standard, Datacenter, and Server Core.
Affected
KB5078766 Patches RPC RCE and Three More Server 2022 Flaws
Microsoft released KB5078766 on March 10, 2026, as part of the March Patch Tuesday cycle. The update targets Windows Server 2022 (Standard, Datacenter, and Server Core) and brings the OS build to 20348.4893. It patches four named CVEs across the RPC runtime, Print Spooler, Kerberos authentication, and the Windows kernel, per the official Microsoft support article.
CVE-2026-0847 is the most critical: an unauthenticated RCE in the Windows RPC runtime that lets attackers execute code with SYSTEM privileges by sending crafted RPC requests. CVE-2026-0851 is a Print Spooler privilege escalation exploitable by authenticated users. CVE-2026-0863 is a Kerberos ticket validation bypass that enables domain user impersonation. CVE-2026-0871 covers multiple kernel memory corruption flaws that can crash systems or enable code execution.
Why KB5078766 Matters: RPC, Kerberos, and Kernel Risks
The RPC RCE (CVE-2026-0847) is particularly dangerous for server infrastructure because RPC is fundamental to Windows networking. Unauthenticated exploitation with SYSTEM privileges means any reachable Server 2022 instance is a potential target. Domain controllers, file servers, and application servers are all exposed.
The Kerberos bypass (CVE-2026-0863) directly threatens Active Directory environments by allowing attackers to forge ticket validation and impersonate domain users. Combined with the kernel memory corruption flaws, these vulnerabilities give attackers multiple paths from initial access to full domain compromise.
Affected Systems and Known Issues
All Windows Server 2022 installations (Standard, Datacenter, Server Core) on x64 architecture are affected. The update ships via Windows Update, WSUS, SCCM, Intune, and Microsoft Update Catalog. File size is approximately 1.2 GB. A restart is required. Installation takes 15-30 minutes.
Known issues
Installation may fail with error 0x80070643 (disk space) or 0x800f0922 (corrupted update components). Print Spooler may need a manual restart after installation. Domain controllers may need a Group Policy refresh for Kerberos fixes to take effect.
Timeline
Impact & actions
Four critical vulnerabilities in Server 2022 allow unauthenticated RCE, privilege escalation, Kerberos bypass, and kernel-level compromise.
Security: CVE-2026-0847 allows unauthenticated SYSTEM-level RCE via crafted RPC requests. CVE-2026-0863 enables domain user impersonation through Kerberos ticket forgery.
Recommended actions · High urgency
- 1Install KB5078766 on all Server 2022 systems.
- 2Verify Build 20348.4893 with Get-ComputerInfo.
- 3Run gpupdate /force on domain controllers after installation.
- 4Restart Print Spooler service if printing issues occur.
Technical details
- CVEs
- CVE-2026-0847, CVE-2026-0851, CVE-2026-0863, CVE-2026-0871
- Attack vector
- Network (CVE-2026-0847, CVE-2026-0863), Local (CVE-2026-0851, CVE-2026-0871)
- Affected versions
- Windows Server 2022 Build 20348.x (all builds before 20348.4893)
- Patched versions
- Windows Server 2022 Build 20348.4893
Mitigations
- Install KB5078766 immediately.
- Restrict RPC exposure via firewall rules on internet-facing servers.
- Disable Print Spooler on servers that don't need printing.
Response
Vendor
FAQ
What does KB5078766 fix?
KB5078766 patches CVE-2026-0847 (unauthenticated RPC remote code execution), CVE-2026-0851 (Print Spooler privilege escalation), CVE-2026-0863 (Kerberos authentication bypass enabling domain user impersonation), and CVE-2026-0871 (kernel memory corruption). It updates the OS build to 20348.4893.
Which systems need KB5078766?
All Windows Server 2022 installations: Standard, Datacenter, and Server Core editions on x64 architecture. Both full and Core installations are affected.
Are there known issues?
Known issues: error 0x80070643 (insufficient disk space), error 0x800f0922 (corrupted update components, fix with sfc /scannow and DISM). Print Spooler may need a manual restart. Domain controllers may need gpupdate /force for Kerberos fixes.
Does KB5078766 require a restart?
Yes. The update is approximately 1.2 GB and requires a restart. Installation takes 15-30 minutes. Schedule during a maintenance window to minimize service impact.
The bottom line
KB5078766 patches CVE-2026-0847 (RPC RCE), CVE-2026-0851 (Print Spooler EoP), CVE-2026-0863 (Kerberos bypass), and CVE-2026-0871 (kernel corruption) in Windows Server 2022, updating to Build 20348.4893.
What happens next
What to do