

Microsoft Patches SQL Server 2022 CU24 PolyBase EoP and SQL Injection with KB5083252
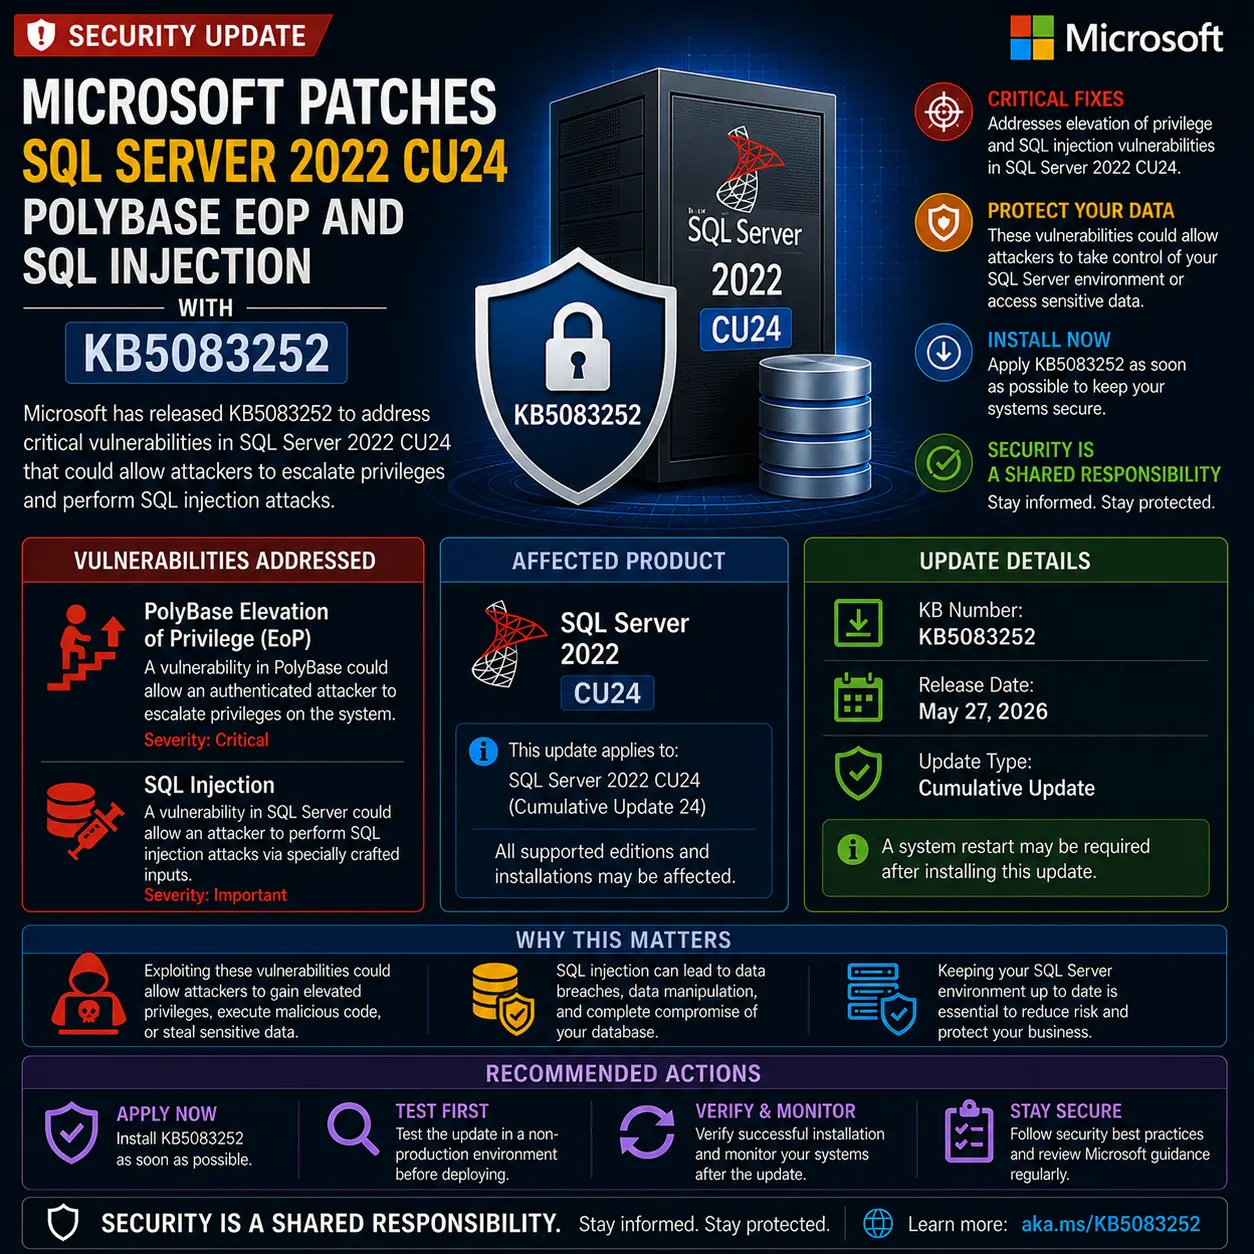
The April 2026 security update for SQL Server 2022 CU24 patches CVE-2026-32167 (PolyBase EoP to sysadmin) and CVE-2026-32176 (EoP/DoS), plus a SQL injection fix in system stored procedures. Build 16.0.4250.1.

On this page
Key takeaways
- CVE-2026-32167: low-priv to sysadmin via PolyBase linked servers (same as SQL 2019).
- SQL injection fix in system stored procedures.
- Build 16.0.4250.1. File size: 464.4 MB (x64).
- MSDASQL linked server breaking change (Msg 7416).
What to do now
High urgency- Install KB5083252 or latest SQL Server 2022 CU.
- Test MSDASQL linked servers before production deployment.
Microsoft released KB5083252 on April 14, 2026, a security update for SQL Server 2022 CU24 patching CVE-2026-32167 (PolyBase privilege escalation to sysadmin), CVE-2026-32176, and a SQL injection flaw in system stored procedures.
The PolyBase sysadmin escalation affects both SQL Server 2019 and 2022. Organizations running either version should patch promptly.
KB5083252 patches PolyBase EoP, SQL injection, and CVE-2026-32176 in SQL Server 2022 CU24.
SQL Server 2022 CU24: PolyBase sysadmin escalation + SQL injection fix. Build 16.0.4250.1. MSDASQL breaking change.
Affected & context
April 2026 security update for SQL Server 2022 CU24 patching PolyBase EoP and SQL injection.
PolyBase sysadmin escalation and SQL injection in stored procedures.
SQL Server 2022 RTM with any CU applied, all editions.
- Vendors
- Microsoft
- Products
- SQL Server 2022 (Windows)SQL Server 2022 (Linux)
- CVEs
- CVE-2026-32167CVE-2026-32176
KB5083252 Patches PolyBase EoP and SQL Injection in SQL Server 2022 CU24
Microsoft released KB5083252 on April 14, 2026, a security update for SQL Server 2022 Cumulative Update 24. The update patches CVE-2026-32167, which allows a low-privileged SQL Server user to gain sysadmin permissions through PolyBase linked servers, and CVE-2026-32176, an additional elevation of privilege vulnerability. It also fixes a SQL injection flaw in system stored procedures caused by improper neutralization of special elements. Build updates to 16.0.4250.1.
Like the parallel SQL Server 2019 update (KB5084816), this introduces the MSDASQL linked server breaking change: queries using the OLE DB Provider for ODBC Drivers with @provstr fail with Msg 7416 due to stricter connection validation.
Same PolyBase Sysadmin Escalation as SQL Server 2019
CVE-2026-32167 is the same PolyBase linked server escalation vector patched in SQL Server 2019 (KB5084816). A low-privileged database user can escalate to sysadmin, making it critical for any multi-user SQL Server environment. The SQL injection fix in system stored procedures closes an additional code execution path.
SQL Server 2022 is the current production version. Organizations running CU24 or earlier should patch immediately. File size: 464.4 MB (x64), significantly smaller than the SQL Server 2019 update.
Affected Systems and Known Issues
SQL Server 2022 RTM instances with any CU applied, on Windows and Linux. All editions (Express, Developer, Standard, Enterprise). Build 16.0.4250.1. File size: 464.4 MB.
Known issue: MSDASQL linked server
Linked server queries using MSDASQL with @provstr fail with Msg 7416 due to stricter validation. Same breaking change as SQL Server 2019 updates.
Timeline
KB5083252 released
Microsoft releases KB5083252 as April Patch Tuesday security update for SQL Server 2022 CU24.
Source: Microsoft Support
Confidence: High
Impact
PolyBase EoP, SQL injection, and MSDASQL breaking change in SQL Server 2022 CU24.
Business impact
PolyBase EoP enables sysadmin escalation. SQL injection in stored procedures enables code execution.
Security impact
CVE-2026-32167 allows low-privileged users to gain sysadmin via PolyBase linked servers.
Affected audience: SQL Server 2022 DBAs, Environments with PolyBase linked servers and non-admin users
Action required.
Technical details
- CVEs
- CVE-2026-32167, CVE-2026-32176
- Attack vector
- Network (authenticated)
- Affected versions
- SQL Server 2022 (all builds before 16.0.4250.1)
- Patched versions
- SQL Server 2022 Build 16.0.4250.1
Mitigations
- Install KB5083252.
- Restrict PolyBase and linked server permissions.
Technical references
Response
Response status: Patched
Patch available: Yes
Workaround available: No
FAQ
What does KB5083252 fix?
CVE-2026-32167 (PolyBase linked server EoP to sysadmin), CVE-2026-32176 (EoP), SQL injection in system stored procedures, and the MSDASQL linked server validation tightening. Build 16.0.4250.1.
Which systems need this update?
SQL Server 2022 RTM instances with any CU applied, all editions, on Windows and Linux.
Are there known issues?
Yes. MSDASQL linked server queries with @provstr fail with Msg 7416. Same issue as the SQL Server 2019 updates.
The bottom line
KB5083252 patches CVE-2026-32167 (PolyBase EoP to sysadmin), CVE-2026-32176, and SQL injection in system stored procedures for SQL Server 2022 CU24. Build 16.0.4250.1.
Same PolyBase sysadmin escalation as SQL Server 2019. Patch SQL Server 2022 to Build 16.0.4250.1 or install the latest available CU.
What happens next
Check for newer SQL Server 2022 CU releases that supersede this update.
What to do
Install KB5083252 or the latest SQL Server 2022 CU. Test MSDASQL linked servers before production.
Sources
Microsoft · Apr 14, 2026 · Primary source
Claims supported
- CVE-2026-32167 PolyBase EoP
- SQL injection fix
- Build 16.0.4250.1
- MSDASQL breaking change
Microsoft · Apr 14, 2026 · Primary source
Claims supported
- 464.4 MB file size
Microsoft · Apr 14, 2026 · Primary source
Claims supported
- Update availability