

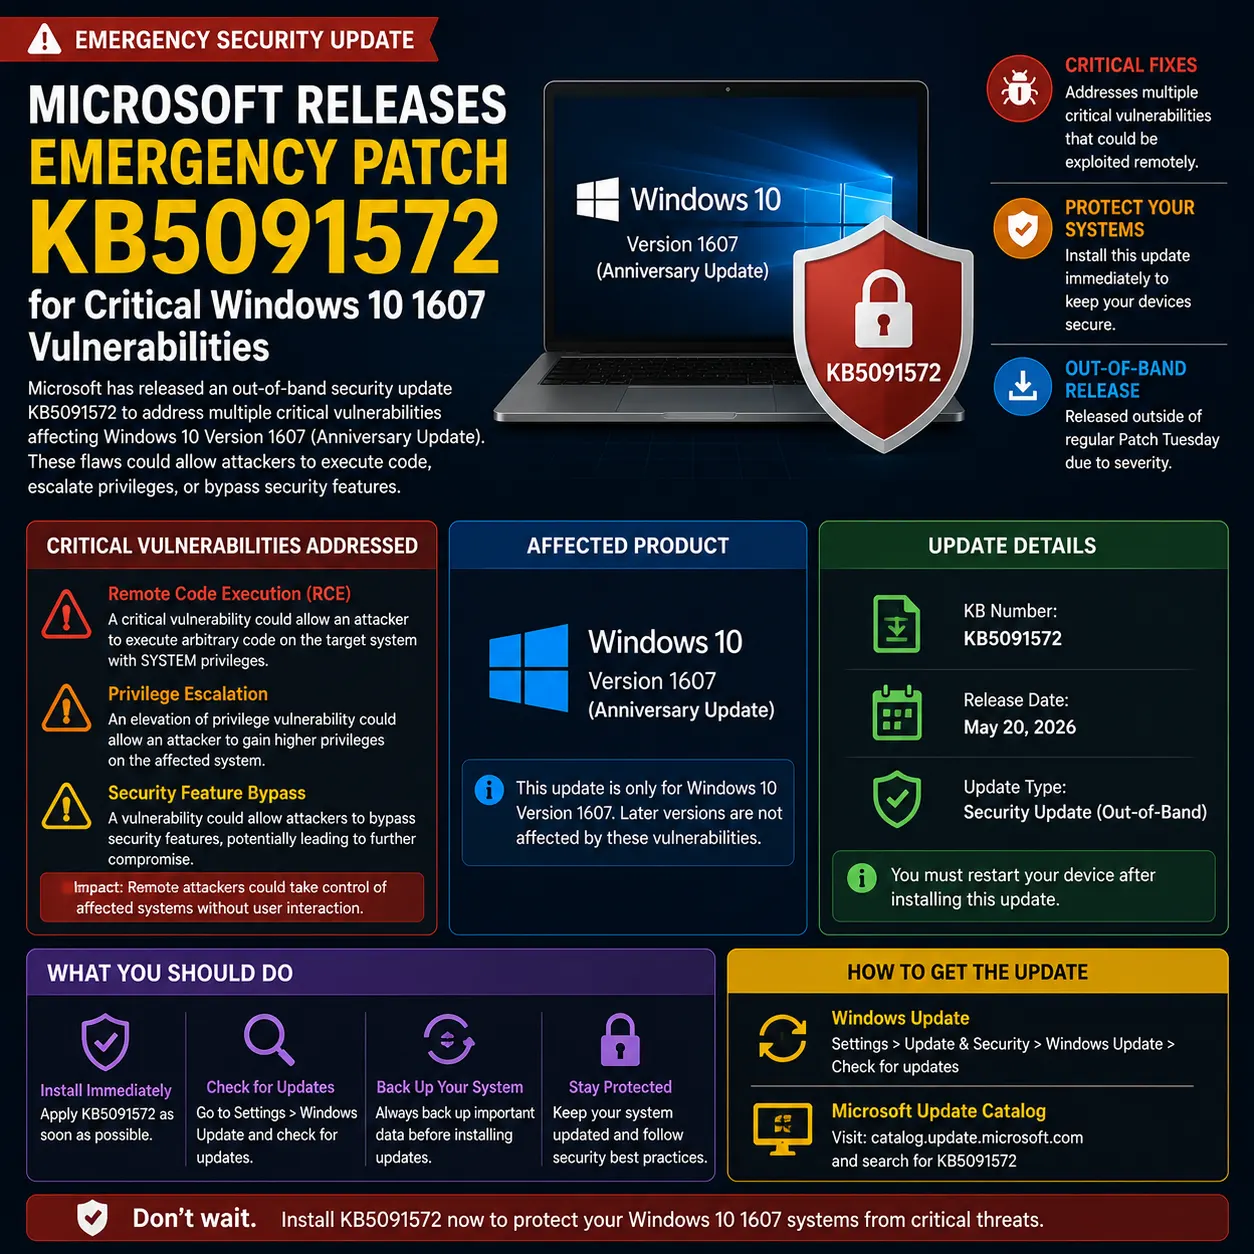
Microsoft Releases Emergency Patch KB5091572 for Critical Windows 10 1607 Vulnerabilities
The April 19, 2026 out-of-band update patches four critical vulnerabilities in Windows 10 1607 and Server 2016, including a network-based RCE and a kernel privilege escalation flaw.

On this page
Key takeaways
- KB5091572 is an out-of-band emergency patch, released outside the normal Patch Tuesday cycle.
- CVE-2026-0847 enables remote code execution via crafted network packets with no user interaction.
- CVE-2026-0848 allows local privilege escalation to SYSTEM through kernel-mode driver flaws.
- The update applies to Windows 10 1607 and Windows Server 2016, updating to Build 14393.9062.
- A restart is required. File size is approximately 847 MB (x64) or 623 MB (x86).
What to do now
Immediate urgency- Install KB5091572 via Windows Update, WSUS, or Microsoft Update Catalog.
- Verify installation by checking for Build 14393.9062.
- Plan migration off Windows 10 1607 to a supported version.
Microsoft released KB5091572 on April 19, 2026, an out-of-band security update for Windows 10 Version 1607 and Windows Server 2016. The emergency patch addresses four critical vulnerabilities, including CVE-2026-0847, a remote code execution flaw in the Windows TCP/IP stack that can be exploited without user interaction.
Out-of-band releases are rare and signal that Microsoft considers the vulnerabilities too severe to wait for the next Patch Tuesday. Organizations running Windows 10 1607 or Server 2016 should deploy this update immediately.
KB5091572 is an emergency out-of-band patch for four critical Windows 10 1607 and Server 2016 vulnerabilities, including a network-based RCE flaw.
Install KB5091572 now if you run Windows 10 1607 or Server 2016. It patches CVE-2026-0847 (RCE in TCP/IP), CVE-2026-0848 (kernel privilege escalation), CVE-2026-0849 (CryptoAPI info disclosure), and CVE-2026-0850 (auth DoS).
Affected & context
Microsoft released KB5091572 on April 19, 2026, an out-of-band emergency security update for Windows 10 1607 and Server 2016 patching four critical vulnerabilities including a network-based RCE in the TCP/IP stack.
The out-of-band release signals critical severity. CVE-2026-0847 allows remote code execution without user interaction via crafted network packets.
Organizations running Windows 10 Version 1607 or Windows Server 2016 on Build 14393.9061 or earlier.
- Vendors
- Microsoft
- Products
- Windows 10 Version 1607Windows Server 2016
- CVEs
- CVE-2026-0847CVE-2026-0848CVE-2026-0849CVE-2026-0850
Microsoft Ships Emergency Patch KB5091572 for Windows 10 1607
Microsoft released KB5091572 on April 19, 2026, an out-of-band cumulative update for Windows 10 Version 1607 (Anniversary Update) and Windows Server 2016. The emergency patch addresses four critical vulnerabilities and updates affected systems to Build 14393.9062, per Microsoft's official support article.
The update targets CVE-2026-0847 (remote code execution in the TCP/IP stack), CVE-2026-0848 (kernel privilege escalation), CVE-2026-0849 (info disclosure in CryptoAPI), and CVE-2026-0850 (denial of service in NTLM/Kerberos authentication). Out-of-band releases signal severity: Microsoft deemed these flaws too critical to wait for the next Patch Tuesday.
Why KB5091572 Matters: Four Critical Flaws Fixed
CVE-2026-0847 is the most severe flaw: a buffer overflow in Windows TCP/IP that lets remote attackers execute code by sending crafted network packets, with no user interaction required. CVE-2026-0848 allows local attackers to escalate to SYSTEM privileges through improper object reference handling in kernel-mode drivers.
CVE-2026-0849 could expose encryption keys through a memory management flaw in Windows CryptoAPI. CVE-2026-0850 targets legacy NTLM and Kerberos authentication with resource exhaustion attacks that can crash domain services. Organizations still running 1607 or Server 2016 should treat this update as immediate priority.
Affected Systems and Deployment Details
Windows 10 Version 1607 (x86 and x64) and Windows Server 2016 (Standard and Datacenter) running Build 14393.9061 or earlier are vulnerable. The update is available through Windows Update, WSUS, Configuration Manager, Intune, and the Microsoft Update Catalog. File size is approximately 847 MB for x64 and 623 MB for x86 systems. A restart is required.
Known issues
Installation may fail with error 0x80070070 if less than 2 GB of free space is available. Some third-party antivirus tools may flag system files during the update process. Brief network connectivity interruptions may occur during installation.
Timeline
KB5091572 released out-of-band
Microsoft releases KB5091572 as an out-of-band emergency patch for Windows 10 1607 and Server 2016.
Source: Microsoft Support
Confidence: High
Impact
Four critical vulnerabilities in Windows 10 1607 and Server 2016 allow remote code execution, privilege escalation, info disclosure, and denial of service.
Business impact
Unpatched systems face remote code execution without user interaction, kernel-level compromise, and authentication service disruption.
Security impact
CVE-2026-0847 allows remote code execution via crafted TCP/IP packets with no user interaction. CVE-2026-0848 enables SYSTEM-level privilege escalation.
Affected audience: IT administrators managing Windows 10 1607 environments, Organizations running Windows Server 2016
Action required.
Technical details
- CVEs
- CVE-2026-0847, CVE-2026-0848, CVE-2026-0849, CVE-2026-0850
- Attack vector
- Network
- Affected versions
- Windows 10 1607 Build 14393.0-14393.9061, Windows Server 2016 Build 14393.0-14393.9061
- Patched versions
- Windows 10 1607 Build 14393.9062, Windows Server 2016 Build 14393.9062
Mitigations
- Install KB5091572 immediately.
- Network segmentation to limit exposure of unpatched systems.
Workarounds
- Restrict network exposure of vulnerable systems via firewall rules until the patch is applied.
Technical references
Response
Vendor statement
Microsoft released KB5091572 as an out-of-band critical security update. Systems receive it automatically via Windows Update within 24-48 hours.
Response status: Patched
Patch available: Yes
Workaround available: No
FAQ
What does KB5091572 fix?
KB5091572 patches four critical vulnerabilities: CVE-2026-0847 (remote code execution in TCP/IP), CVE-2026-0848 (kernel privilege escalation), CVE-2026-0849 (CryptoAPI info disclosure), and CVE-2026-0850 (authentication denial of service). It updates systems to Build 14393.9062.
Why is this an out-of-band update?
An out-of-band update is released outside the normal monthly Patch Tuesday cycle. Microsoft uses this for vulnerabilities too critical to wait. It signals that the flaws pose immediate risk.
Which systems need KB5091572?
Windows 10 Version 1607 (Anniversary Update) and Windows Server 2016 running Build 14393.9061 or earlier. Both x86 and x64 architectures are affected.
Are there prerequisites for installation?
No specific prerequisites. The update installs on any Windows 10 1607 system regardless of previous update state. Ensure at least 2 GB free disk space (x64) or 1.5 GB (x86). A restart is required.
Are there known issues with KB5091572?
Known issues include installation failures with error 0x80070070 if disk space is insufficient, brief network connectivity interruptions during installation, and possible false positives from third-party antivirus tools.
The bottom line
KB5091572 patches four critical vulnerabilities in Windows 10 1607 and Server 2016, headlined by a network-based RCE flaw that requires no user interaction.
Deploy KB5091572 immediately on all Windows 10 1607 and Server 2016 systems. Out-of-band releases are rare and indicate critical, actively relevant threats.
What happens next
Microsoft will include these fixes in the next cumulative Patch Tuesday update. Organizations should also plan migration off Windows 10 1607, which is nearing extended support end.
What to do
Install the update via Windows Update, WSUS, or the Microsoft Update Catalog. Verify installation by checking for Build 14393.9062.