

Fake IT Support Calls on Microsoft Teams Push EtherRAT Malware
Unit 42 details a social-engineering campaign that pairs "Employee Survey" phishing with external Teams calls posing as a System Administrator to deploy the EtherRAT trojan.

On this page
Key takeaways
- Unit 42 reported that attackers pose as a 'System Administrator' over Microsoft Teams voice calls to gain remote access.
- The attack starts with an 'Employee Survey' phishing email carrying a malicious PDF attachment.
- Attackers guide victims to install legitimate tools such as HopToDesk and AnyDesk, then run a malicious MSI (v7.msi) that loads EtherRAT.
- EtherRAT is a cross-platform Node.js trojan that uses Ethereum smart contracts to retrieve its C2 server, complicating takedowns.
- Microsoft has added Teams protections, including external-caller warnings and a policy that sends suspected third-party bots to the meeting lobby.
What to do now
High urgency- Restrict external Teams calls and chats and enforce external-caller warnings.
- Verify any IT support remote-access request through known internal channels.
- Block unsanctioned remote-access tools with application control.
- Monitor for unexpected MSI and Node.js runtime activity on endpoints.
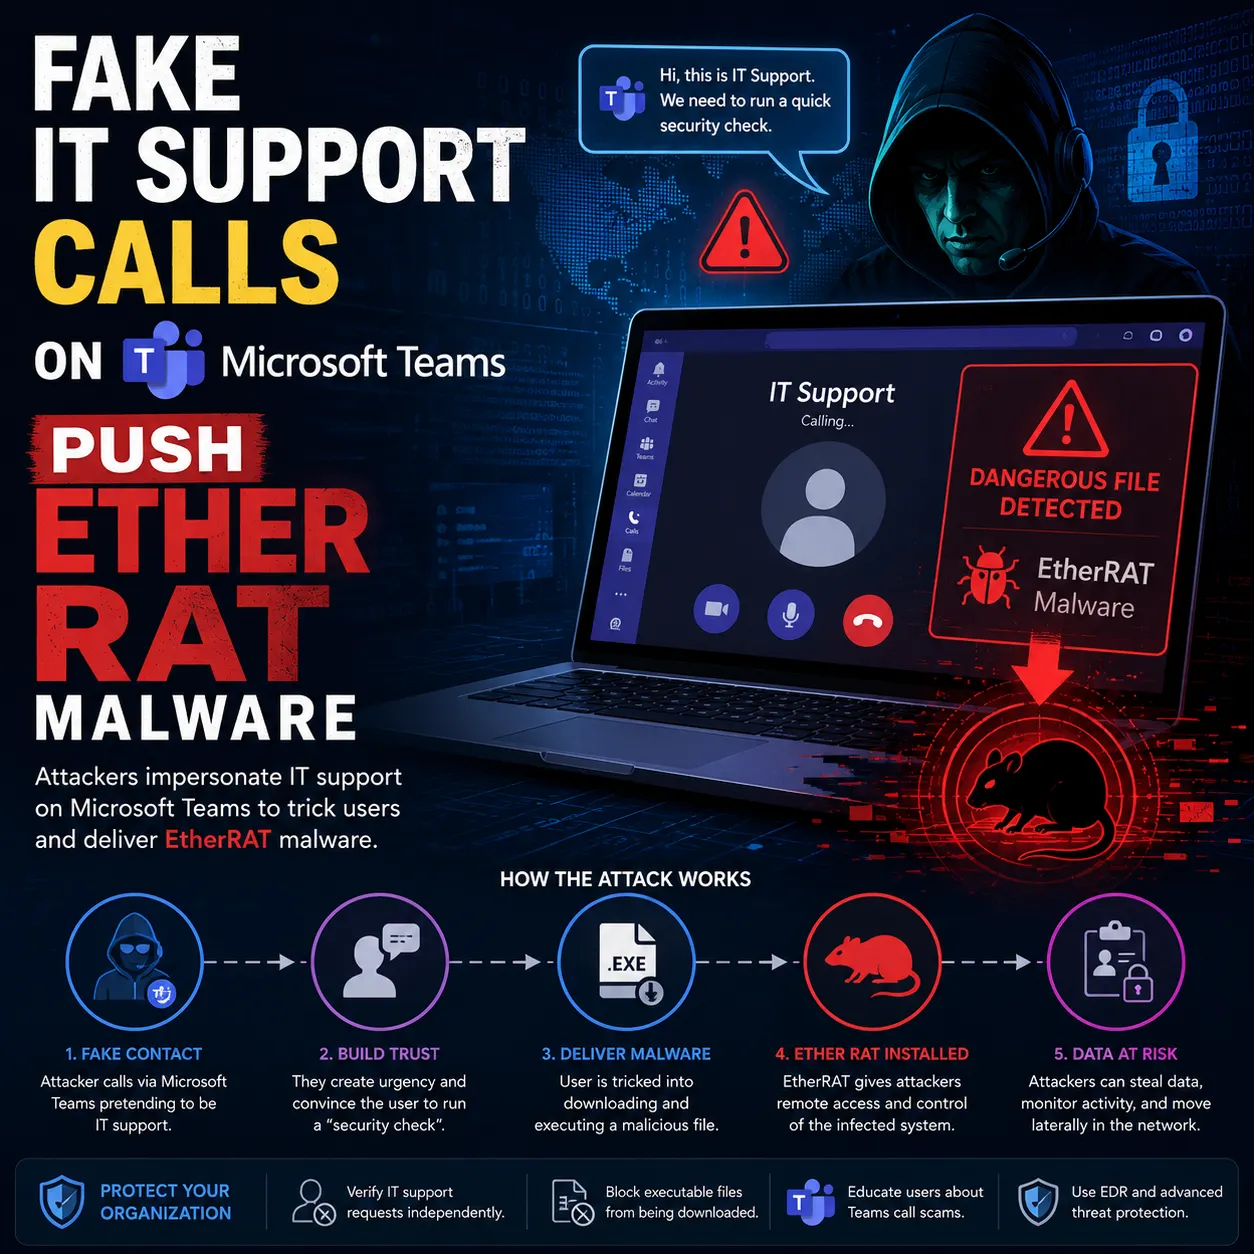
Attackers are abusing Microsoft Teams voice calls to impersonate corporate IT support and trick employees into installing EtherRAT, a Node.js-based remote access trojan, according to a report from Palo Alto Networks' Unit 42. The campaign gives attackers initial access to corporate networks by combining phishing emails, external Teams calls, legitimate remote-management tools, and a malicious MSI loader.
The technique sidesteps traditional email defenses by moving the attack into a trusted collaboration channel and relying on legitimate software, making the intrusion harder to spot and stop.
Unit 42 reports attackers impersonating IT support over Microsoft Teams calls to install the EtherRAT trojan and gain corporate network access.
Fake IT support callers on Microsoft Teams talk employees into granting remote access and running an MSI loader that deploys EtherRAT, a Node.js RAT using Ethereum smart contracts for C2.
Affected & context
Palo Alto Networks' Unit 42 reported a campaign in which attackers impersonate corporate IT support over Microsoft Teams voice calls to trick employees into granting remote access and installing the EtherRAT trojan, granting initial access to corporate networks.
The campaign abuses trusted collaboration tools and legitimate remote-access software, letting attackers bypass many technical controls through social engineering rather than exploiting a software flaw.
Organizations using Microsoft 365 and Microsoft Teams whose employees can receive external calls and chats.
- Vendors
- Microsoft
- Products
- Microsoft TeamsMicrosoft 365
- Malware
- EtherRAT
What happened
Palo Alto Networks' Unit 42 reported a campaign in which threat actors abuse Microsoft Teams voice calls to impersonate corporate IT support staff and trick employees into installing the EtherRAT malware. The goal is initial access to corporate networks.
According to Unit 42's report posted on GitHub, the attack starts with a phishing email using an 'Employee Survey' lure and a malicious PDF attachment. Shortly after the victim opens the document, they receive a Microsoft Teams voice call from an external account impersonating a 'System Administrator.'
Researchers observed the Teams session showing the 'External unfamiliar' label, indicating the caller belonged to a different Microsoft 365 tenant than the recipient. Audit logs showed the attacker initiated the external chat using the account helpdesk@Progressive936.onmicrosoft[.]com while posing as IT support.
- Attack begins with an 'Employee Survey' phishing email and malicious PDF.
- Caller displayed the Teams 'External unfamiliar' label from a different M365 tenant.
How the attack chain works
After convincing the victim to grant remote control through Microsoft Teams' built-in screen-sharing feature, the attacker walks them through installing legitimate remote-access tools, including HopToDesk and AnyDesk.
With remote access established, the attacker downloads and executes a malicious MSI installer (v7.msi) from camorreado[.]click. The MSI acts as a malware loader: it downloads a legitimate Node.js runtime, decrypts embedded payloads, and ultimately launches EtherRAT.
About EtherRAT
EtherRAT is a cross-platform remote access trojan written in Node.js that gives attackers full control over compromised systems. It can execute commands, manipulate files, steal data, and maintain persistence. Notably, it uses Ethereum smart contracts to retrieve its active command-and-control (C2) server, making the infrastructure harder to disrupt.
Unit 42 notes that EtherRAT was previously used in state-sponsored attacks exploiting the React2Shell vulnerability and has since been adopted by numerous other threat actors. Researchers also found an open directory on a distribution server holding multiple installer versions (v1 through v9), indicating the campaign is under active development.
- Malicious loader: v7.msi from camorreado[.]click.
- EtherRAT uses Ethereum smart contracts to locate its C2 server.
- Installer versions v1 through v9 found on a distribution server.
The MSI loader downloads a legitimate Node.js runtime and decrypts embedded payloads before launching EtherRAT, blending malicious activity with trusted software.
Part of a broader Teams abuse trend
The campaign follows a growing number of attacks abusing Microsoft Teams to breach corporate networks.
In March, a campaign targeted financial and healthcare organizations by flooding inboxes with spam, then contacting victims over Microsoft Teams while posing as company IT staff. Victims were tricked into launching Quick Assist sessions that led to deployment of the A0Backdoor malware. A month later, Microsoft warned that attackers were increasingly abusing external Microsoft Teams to impersonate helpdesk personnel, obtain remote access, perform reconnaissance, move laterally, and steal data.
Microsoft's Teams protections
To help defend against these attacks, Microsoft has been adding new protections to Teams.
- Earlier this year, Microsoft added warnings that identify external callers and chats to protect against potential phishing and vishing attacks.
- More recently, Microsoft introduced a Teams administrator policy that automatically places suspected third-party bots into the meeting lobby until an organizer manually approves their admission.
What defenders can do
Because the campaign relies on social engineering and legitimate tools, layered controls and user awareness matter as much as endpoint detection.
- Restrict or disable external Teams calls and chats where they are not business-critical, and enforce external-caller warnings.
- Train staff that IT support will not cold-call over Teams to request remote control; verify requests through known internal channels.
- Apply application control to block unsanctioned remote-access tools such as HopToDesk and AnyDesk.
- Monitor for unexpected MSI executions and Node.js runtime downloads on endpoints.
- Adopt Microsoft's new Teams policy that sends suspected third-party bots to the meeting lobby.
Verify any remote-access request out-of-band: attackers count on employees trusting a Teams call that looks like it comes from IT.
Impact
Successful attacks give threat actors remote control of employee devices and initial access to corporate networks via the EtherRAT trojan.
Business impact
Compromise can lead to lateral movement, data theft, and broader network intrusion following an initial foothold.
Technical impact
An MSI loader installs a legitimate Node.js runtime and decrypts payloads to launch EtherRAT, which executes commands, manipulates files, and maintains persistence.
Security impact
Full remote control of compromised systems with resilient C2 via Ethereum smart contracts, complicating disruption.
Privacy impact
EtherRAT can steal data from compromised systems.
Affected audience: IT and security teams, Help desk / IT support staff, Microsoft 365 / Teams end users
Action required.
Technical details
- Exploitation
- Exploited in the wild
- Attack vector
- Social engineering via Microsoft Teams external voice calls impersonating IT support, followed by remote-access tool abuse and MSI loader execution.
Indicators of compromise
helpdesk@Progressive936.onmicrosoft[.]comAttacker account used to initiate external Teams chat while posing as IT support.
Source: Unit 42
Confidence: High
- Domain
camorreado[.]clickHost serving the malicious MSI loader (v7.msi).
Source: Unit 42
Confidence: High
- File
v7.msiMalicious MSI installer acting as the EtherRAT loader.
Source: Unit 42
Confidence: High
Detection methods
- Review Teams audit logs for external chats/calls from unfamiliar tenants.
- Alert on unexpected MSI execution and Node.js runtime downloads on endpoints.
Mitigations
- Restrict external Teams calls and chats.
- Enforce external-caller warnings in Teams.
- Block unsanctioned remote-access tools (e.g., HopToDesk, AnyDesk) via application control.
Technical references
Response
Customer guidance
Microsoft has added Teams protections including external-caller/chat warnings and an administrator policy that places suspected third-party bots into the meeting lobby until manually approved.
Response status: Acknowledged
Patch available: No
Workaround available: Yes
FAQ
What is EtherRAT?
EtherRAT is a cross-platform remote access trojan written in Node.js that gives attackers full control over compromised systems, including command execution, file manipulation, data theft, and persistence. It uses Ethereum smart contracts to retrieve its command-and-control server, making it harder to disrupt.
How does the Microsoft Teams attack start?
According to Unit 42, it begins with an 'Employee Survey' phishing email carrying a malicious PDF. Soon after the victim opens it, they get a Microsoft Teams voice call from an external account impersonating a 'System Administrator.'
How can organizations defend against this campaign?
Restrict external Teams calls and chats, enforce external-caller warnings, block unsanctioned remote-access tools, verify IT support requests through internal channels, and monitor endpoints for unexpected MSI and Node.js runtime activity.
The bottom line
Unit 42 documented a campaign that abuses Microsoft Teams voice calls to impersonate IT support, obtain remote access, and deploy the EtherRAT Node.js trojan for initial network access.
Treat unsolicited IT support contact over Teams as suspicious and verify through internal channels before granting remote access.
What happens next
With installer versions v1–v9 observed, the campaign is actively evolving; expect continued Teams abuse and further Microsoft Teams protections.
What to do
Restrict external Teams communications, enforce caller warnings, and brief staff on IT-support impersonation.
Sources
Palo Alto Networks Unit 42 · Primary source
Claims supported
- Attackers impersonate IT support over Teams to install EtherRAT.
- Attack chain uses phishing PDF, external Teams call, HopToDesk/AnyDesk, and v7.msi from camorreado[.]click.
- EtherRAT uses Ethereum smart contracts to retrieve its C2 server.