

News
Microsoft to Retire OWA Light Client in Exchange Server
Microsoft will remove OWA Light from Exchange Server in an August 2026 update, directing users to modern Outlook on the web.
Latest updates on cloud, security, Microsoft and the tools that keep your infrastructure running.
Stay informed with the latest IT news, security updates and product changes.
Microsoft will remove OWA Light from Exchange Server in an August 2026 update, directing users to modern Outlook on the web.
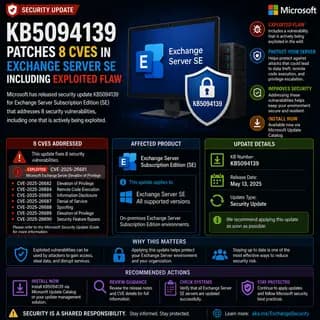
KB5094139 patches 8 CVEs in Exchange Server SE including RCE, spoofing, info disclosure, and EoP. At least one actively exploited. Max CVSS 8.8. Also available for Exchange 2019 and 2016 via ESU.
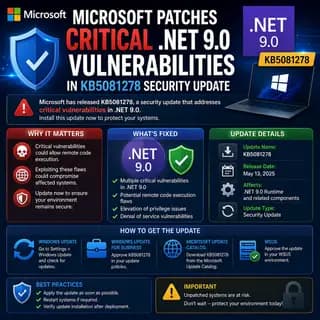
Microsoft released KB5081278 on March 10, 2026, a critical security update for .NET 9.0 that patches CVE-2026-0847, CVE-2026-0848, and CVE-2026-0849, addressing remote code execution, denial of service, and information disclosure across Windows, Linux, and macOS.
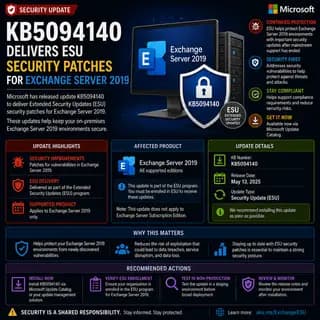
KB5094140 is the June 2026 ESU security update for Exchange 2019 CU14/CU15 patching 8 CVEs including actively exploited OWA spoofing. Same CVEs as Exchange SE SU7 (KB5094139). Requires ESU Period 2 eligibility.
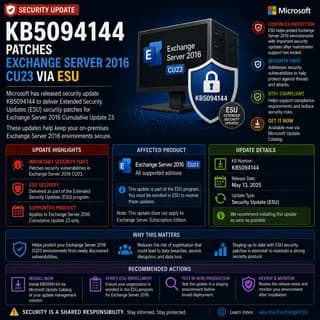
KB5094144 is the June 2026 ESU update for Exchange 2016 CU23 patching 8 CVEs including actively exploited OWA spoofing. Exchange 2016 is deep in extended support. Requires ESU Period 2.
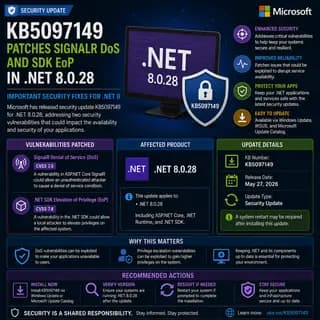
KB5097149 patches three CVEs in .NET 8.0: serialization RCE, ASP.NET Core DoS, and cryptographic info disclosure. Updates to version 8.0.28 on Windows, Linux, and macOS. No known issues.
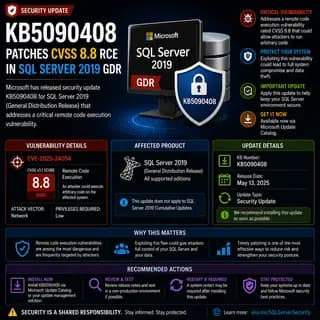
KB5090408 patches CVE-2026-40370 (CVSS 8.8 RCE via path manipulation) in SQL Server 2019 GDR. Build 15.0.2170.1. For instances on the GDR servicing branch (no CUs). MSDASQL Msg 7416 breaking change. Superseded by KB5102336.
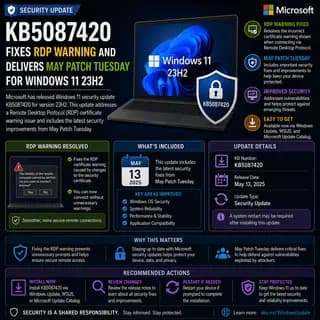
KB5087420 is the May 2026 Patch Tuesday update for Windows 11 23H2 (Build 22631.7079). Fixes the RDP multi-monitor warning issue from KB5082052, includes Secure Boot cert targeting improvements, and addresses BitLocker recovery behavior.
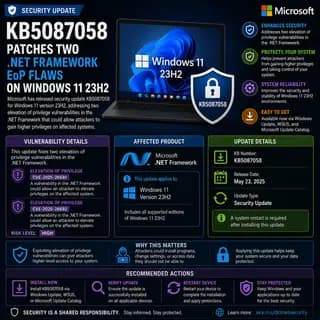
KB5087058 patches CVE-2026-32177 and CVE-2026-35433 (both .NET Framework EoP) on Windows 11 23H2. May 2026 Patch Tuesday security update for .NET Framework 3.5 and 4.8.1. No known issues.
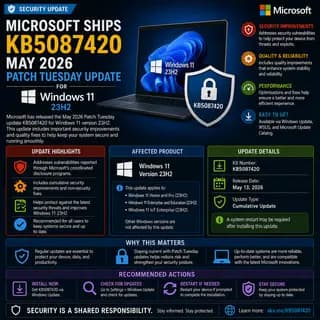
Microsoft released KB5087420 on May 12, 2026, the May Patch Tuesday cumulative security update for Windows 11 23H2. Patches kernel vulnerabilities and includes the March/April preview fixes. Build 22631.7100.
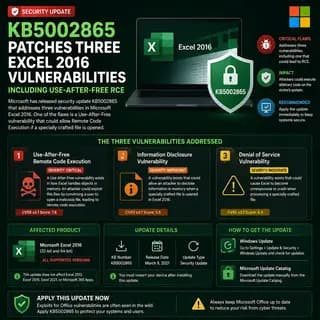
Microsoft released KB5002865 on May 12, 2026, patching three security vulnerabilities in Excel 2016: two remote code execution flaws (CVE-2026-40362, CVE-2026-40359) and an out-of-bounds read (CVE-2026-40360), all with CVSS 7.8.
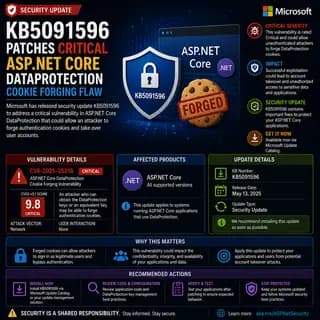
KB5091596 is a .NET 10.0.7 out-of-band security update patching CVE-2026-40372, a critical ASP.NET Core DataProtection HMAC bypass allowing authentication cookie forging and privilege escalation. Update immediately.
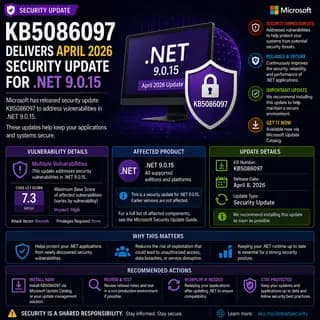
KB5086097 is the April 2026 security update for .NET 9.0, updating to version 9.0.15. Includes security fixes for runtime and ASP.NET Core on Windows, Linux, and macOS. Part of the April Patch Tuesday cycle.
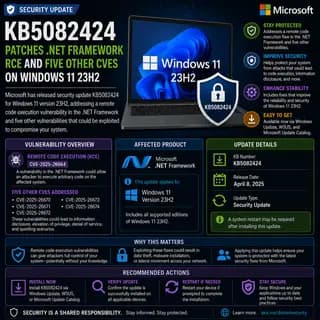
KB5082424 patches six CVEs in .NET Framework 3.5 and 4.8.1 for Windows 11 23H2: CVE-2026-32178 (RCE), CVE-2026-32203/32226/23666 (DoS), CVE-2026-26171 (bypass), CVE-2026-33116 (info disclosure).
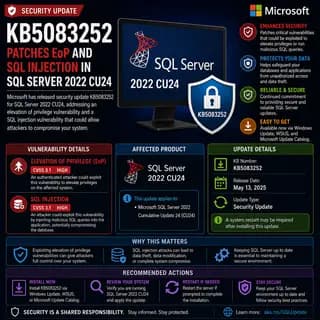
KB5083252 patches CVE-2026-32167 (SQL injection EoP), CVE-2026-32176 (PolyBase EoP), and a SQL injection in system stored procedures in SQL Server 2022 CU24. Build 16.0.4250.1. MSDASQL breaking change.
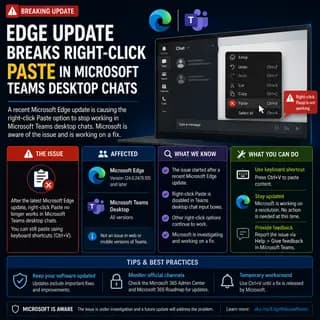
An Edge update broke right-click paste in Teams desktop chats starting April 14, 2026. The paste option appears greyed out for URLs, text, and images. Ctrl+V still works. Root cause: Edge WebView2 runtime regression. Fix rolling out in stages.
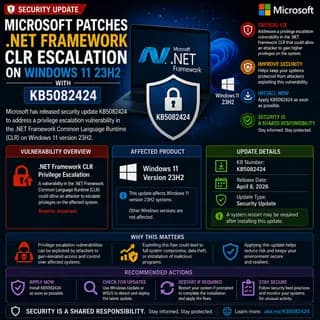
Microsoft released KB5082424 on April 14, 2026, a cumulative update for .NET Framework 3.5 and 4.8.1 on Windows 11 23H2 patching CLR privilege escalation. Superseded by KB5087058.
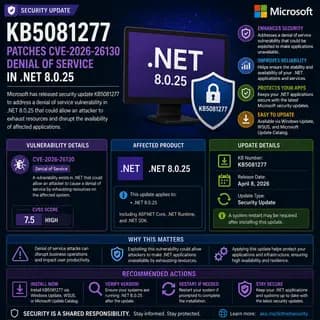
KB5081277 patches CVE-2026-26130 (.NET Denial of Service) in .NET 8.0, updating to version 8.0.25. Available on Windows, Linux, and macOS. Superseded by .NET 8.0.28 (July 2026).