

11 articles · Curated and written by practitioners
More 32
Enable DNS-over-HTTPS (DoH) on Windows Server 2025 DNS Server
Learn how to enable DNS-over-HTTPS (DoH) on the Windows Server 2025 DNS Server role, covering certificates, netsh binding, the Set-DnsServerEncryptionProtocol cmdlet, and client testing.

Certighost CVE-2026-54121: Public Exploit Turns a Domain User Into a Domain Controller
Researchers H0j3n and Aniq Fakhrul have released a working exploit for Certighost, an Active Directory Certificate Services flaw patched in July 2026 that let any low-privileged domain user impersonate a domain controller and reach full domain compromise.
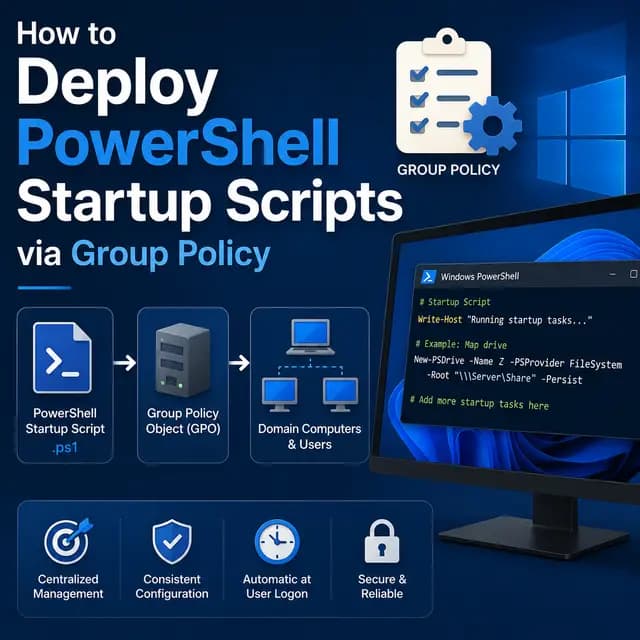
How to Deploy PowerShell Startup Scripts via Group Policy
Learn how to deploy PowerShell startup scripts to domain computers using Group Policy. Covers the Scripts (Startup/Shutdown) extension, the PowerShell Scripts tab, execution policy, Netlogon storage, and verifying execution with Event ID 5018.
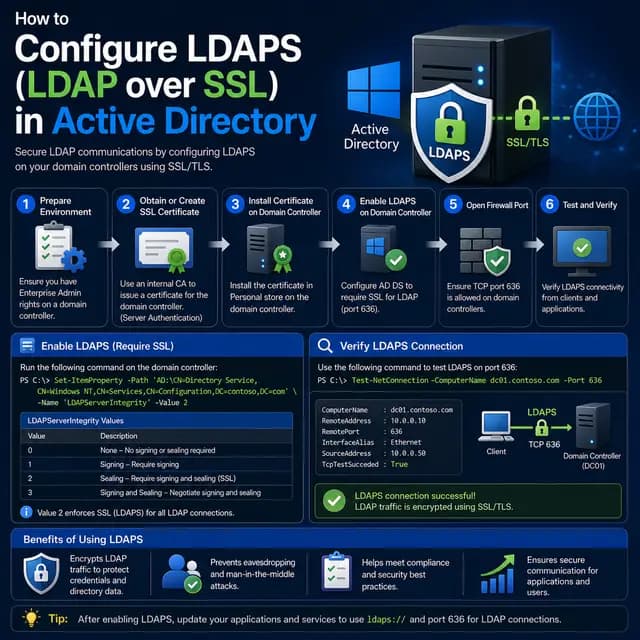
How to Configure LDAPS (LDAP over SSL) in Active Directory
Learn how to configure LDAPS (LDAP over SSL) in Active Directory Domain Services. Covers certificate requirements, the NTDS Personal store, firewall rules for port 636, and verifying the connection with ldp.exe.

Event ID 5719: Why Netlogon Can't Reach a Domain Controller
Event ID 5719 is a Netlogon warning logged when a domain-joined Windows computer fails to establish a secure session with a domain controller. Common causes include network timing at boot, DNS misconfiguration, and broken secure channel trust.

What Is LDAP? Lightweight Directory Access Protocol Explained
LDAP is the standard protocol for querying and modifying directory services like Active Directory. It runs on port 389 (plaintext) or 636 (TLS). This explainer covers LDAP operations, Active Directory integration, LDAPS, and security best practices.
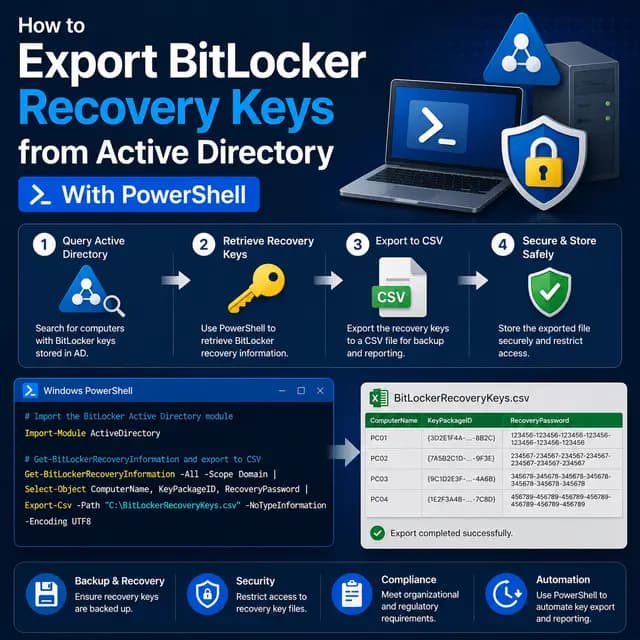
How to Export BitLocker Recovery Keys from Active Directory With PowerShell
Use the ActiveDirectory PowerShell module to export BitLocker recovery keys from Active Directory into a CSV, then validate the 48-digit passwords and keep the file secure.
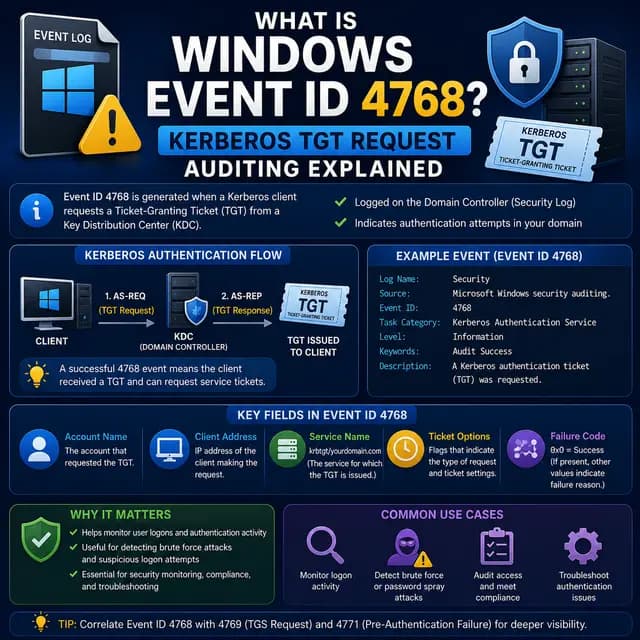
What Is Windows Event ID 4768? Kerberos TGT Request Auditing Explained
Windows Event ID 4768 logs every Kerberos TGT request on domain controllers. This explainer covers what it means, how the Kerberos AS-REQ flow works, key result codes, and how to use 4768 for security monitoring.
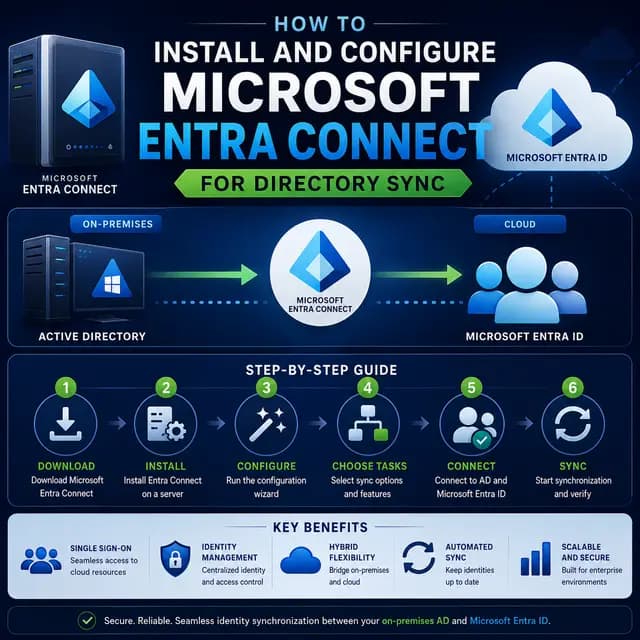
How to Install and Configure Microsoft Entra Connect for Directory Sync
Install and configure Microsoft Entra Connect to synchronize your on-premises Active Directory with Microsoft Entra ID, enabling hybrid identity with password hash sync, OU filtering, and SSO.
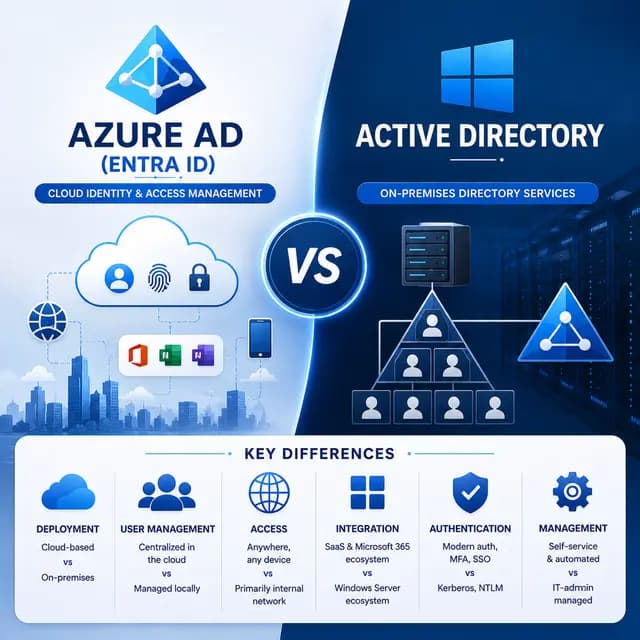
Azure AD vs Active Directory (Entra ID): Key Differences Explained
Active Directory and Microsoft Entra ID (formerly Azure AD) both handle identity, but they were built for different eras. This explainer breaks down their trust models, authentication protocols, and when to use each.
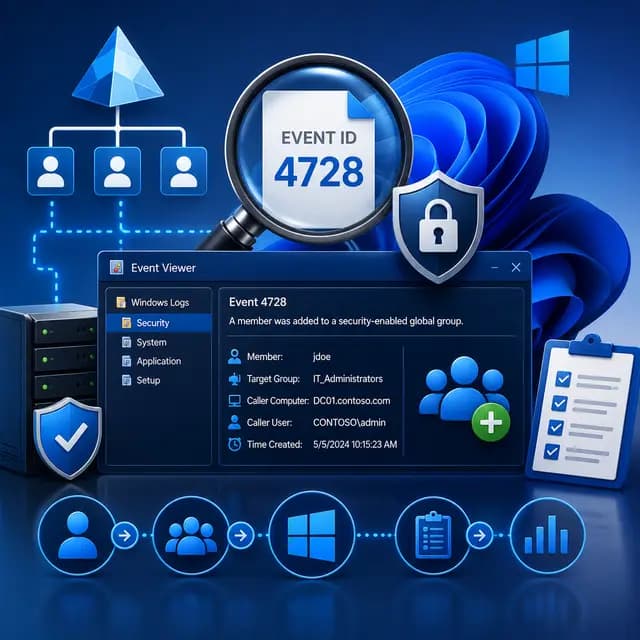
What Is Windows Event ID 4728? Active Directory Group Membership Auditing Explained
Windows Event ID 4728 logs every time a member is added to a security-enabled global group in Active Directory. This explainer covers what the event means, how it works, why it matters for security teams, and how to monitor it effectively.