

4 articles · Curated and written by practitioners
Google patches CVE-2026-85046, the sixth exploited Chrome zero-day of 2026
Google shipped Chrome 152.0.7977.82/.83 on 3 September 2026 with 12 security fixes, including CVE-2026-85046, a type confusion bug in V8 that attackers are already exploiting. CISA added it to the KEV catalog a day later.
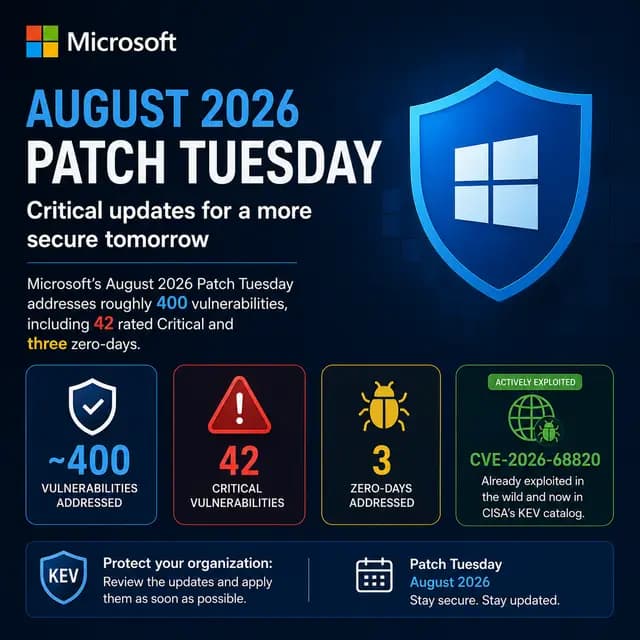
Microsoft's August 2026 Patch Tuesday Fixes About 400 Flaws and 3 Zero-Days
Microsoft's August 2026 Patch Tuesday addresses roughly 400 vulnerabilities, including 42 rated Critical and three zero-days. One, CVE-2026-68820, is already exploited in the wild and now sits in CISA's KEV catalog.
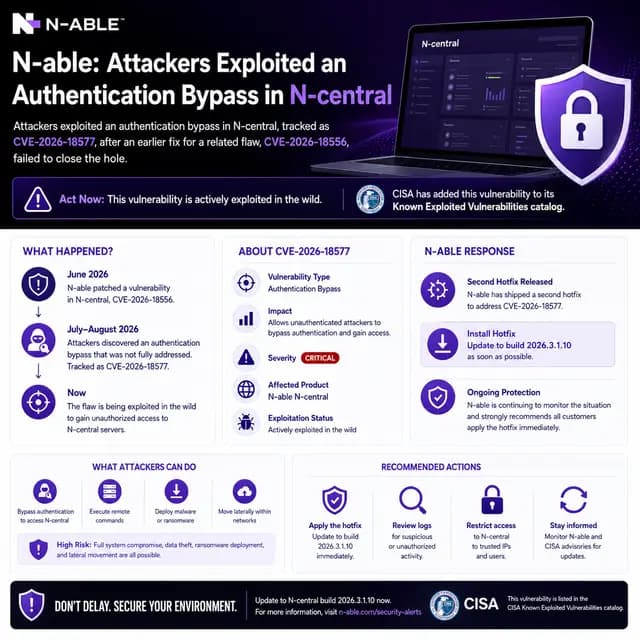
N-able Patches N-central Auth Bypass Again After CVE-2026-18577 Exploited
N-able says attackers exploited an authentication bypass in N-central, tracked as CVE-2026-18577, after an earlier fix for a related flaw, CVE-2026-18556, failed to close the hole. The company has shipped a second hotfix, build 2026.3.1.10, and CISA has added the bug to its Known Exploited Vulnerabilities catalog.
CISA Adds Actively Exploited SharePoint RCE CVE-2026-45659 to KEV Catalog
CISA added Microsoft SharePoint Server flaw CVE-2026-45659 (CVSS 8.8) to its Known Exploited Vulnerabilities catalog, citing active exploitation and setting a July 4, 2026 remediation deadline for U.S. federal agencies.