

3 articles · Curated and written by practitioners
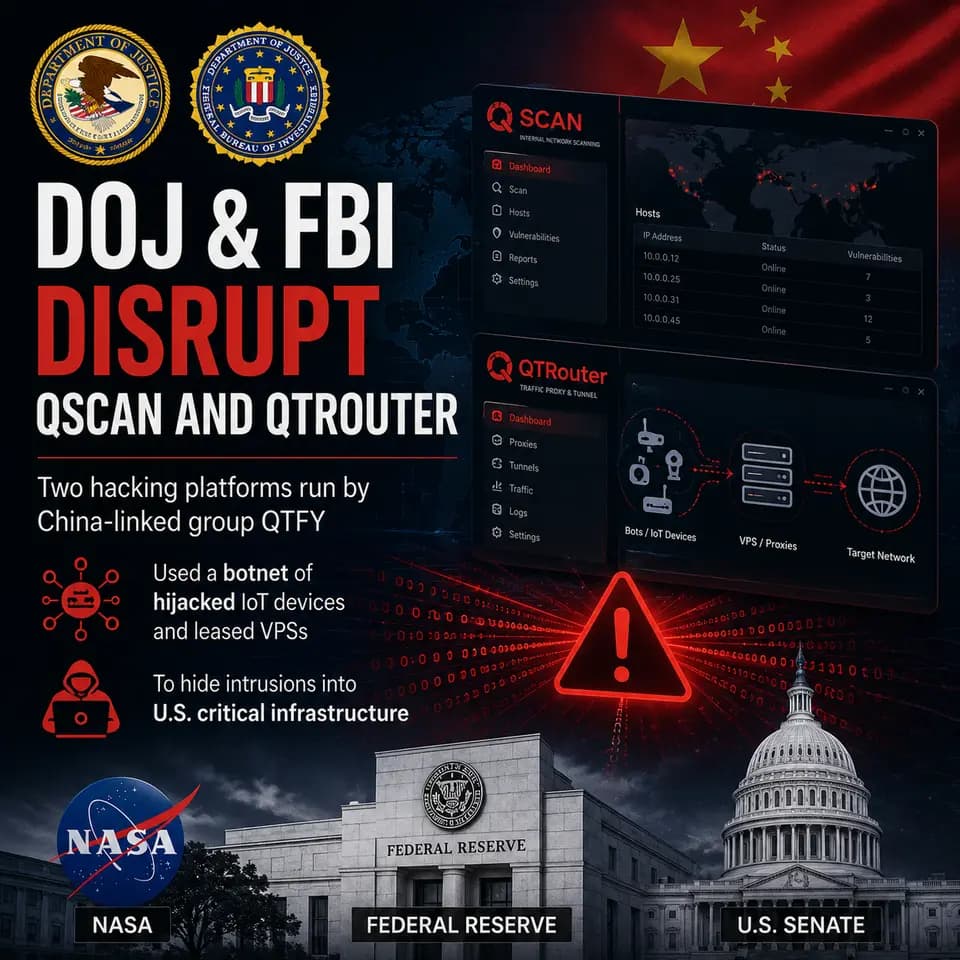
FBI Disrupts China-Linked QTFY Botnet Infrastructure Targeting US Networks
The DoJ and FBI announced the disruption of QScan and QTRouter, two hacking platforms run by China-linked group QTFY, which used a botnet of hijacked IoT devices and leased VPSs to hide intrusions into U.S. critical infrastructure, including NASA, the Federal Reserve, and the Senate.
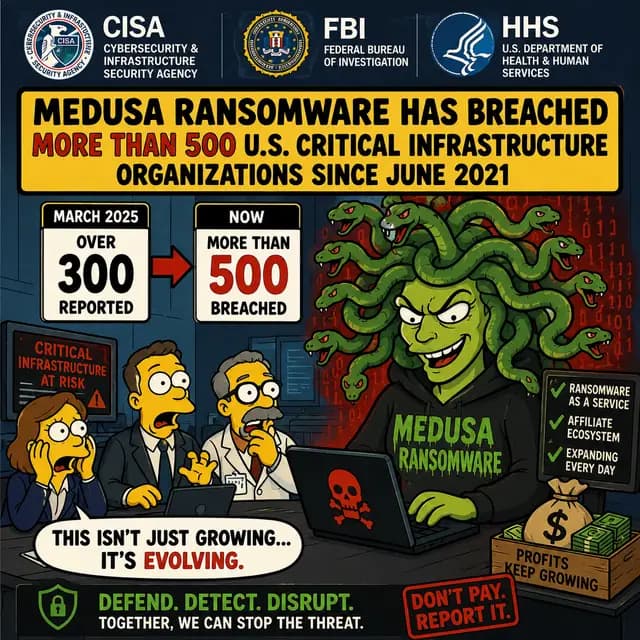
CISA: Medusa Ransomware Has Hit Over 500 Critical Infrastructure Orgs
CISA, the FBI and HHS say Medusa ransomware has breached more than 500 U.S. critical infrastructure organizations since June 2021, up from over 300 reported in March 2025, as the group's ransomware-as-a-service model keeps expanding.
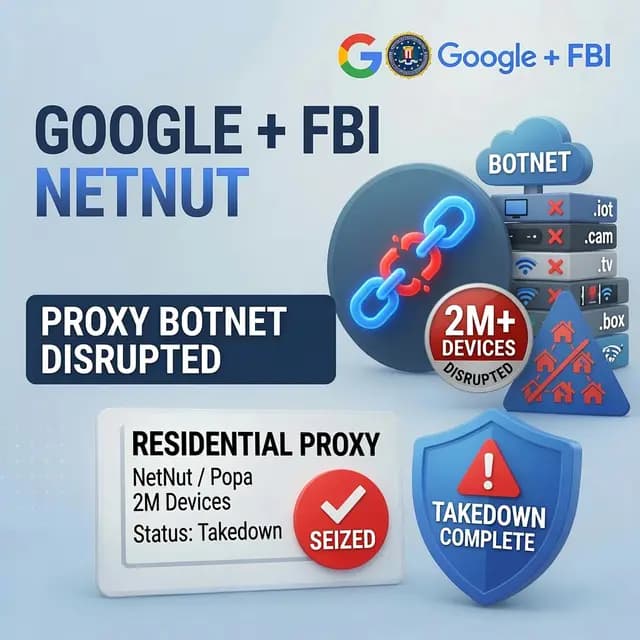
Google, FBI Disrupt NetNut Residential Proxy Botnet
Google, the FBI and Lumen coordinated to disrupt NetNut, a residential proxy network built on at least 2 million hijacked consumer devices and rented to cybercriminal and espionage groups. Its parent firm rejects the characterization.