

4 articles · Curated and written by practitioners
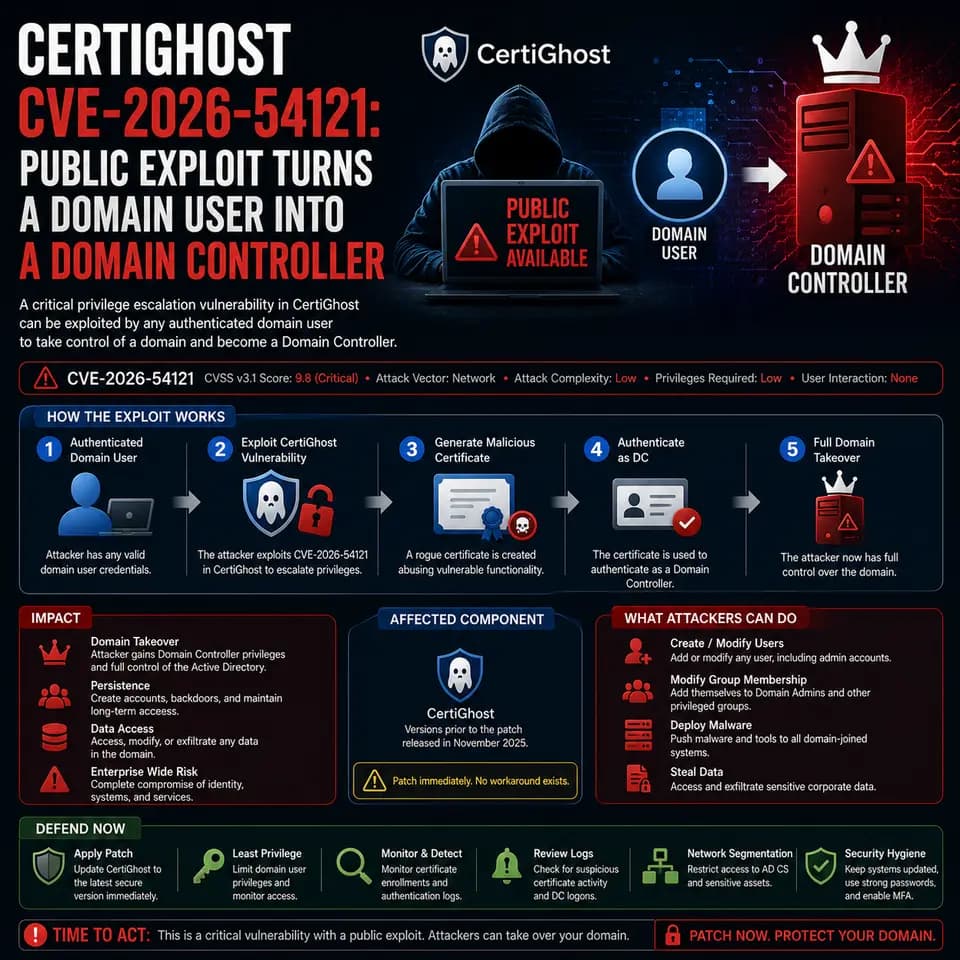
Certighost CVE-2026-54121: Public Exploit Turns a Domain User Into a Domain Controller
Researchers H0j3n and Aniq Fakhrul have released a working exploit for Certighost, an Active Directory Certificate Services flaw patched in July 2026 that let any low-privileged domain user impersonate a domain controller and reach full domain compromise.
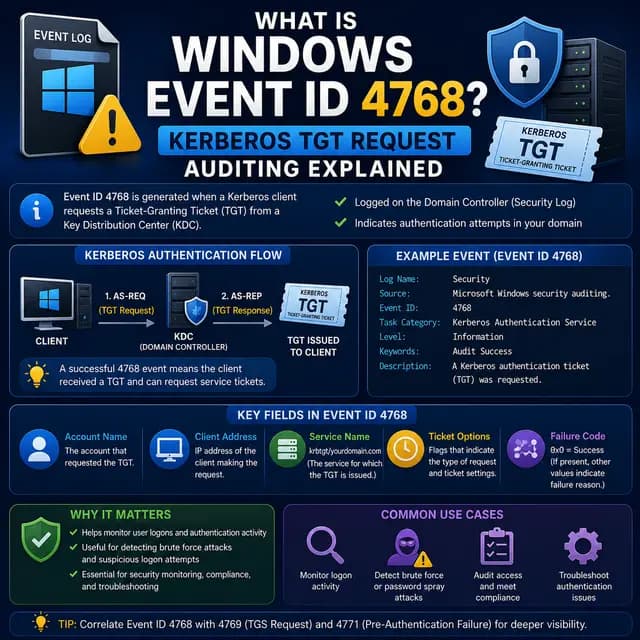
What Is Windows Event ID 4768? Kerberos TGT Request Auditing Explained
Windows Event ID 4768 logs every Kerberos TGT request on domain controllers. This explainer covers what it means, how the Kerberos AS-REQ flow works, key result codes, and how to use 4768 for security monitoring.
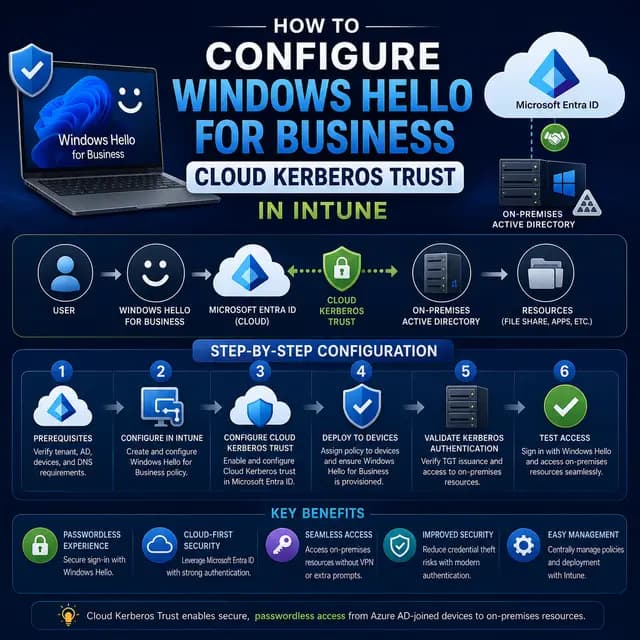
How to Configure Windows Hello for Business Cloud Kerberos Trust in Intune
Configure Windows Hello for Business with cloud Kerberos trust in Microsoft Intune. Covers Entra Kerberos server setup, Intune policy creation via Account Protection and Settings Catalog, and verification.
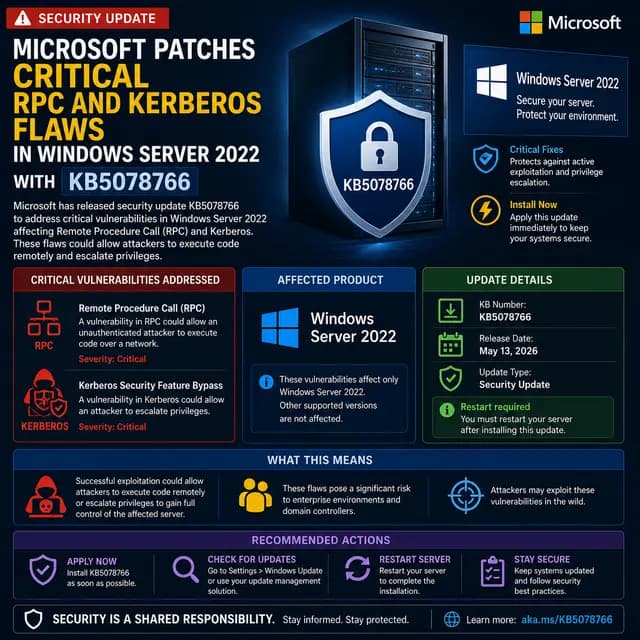
Microsoft Patches Critical RPC and Kerberos Flaws in Windows Server 2022 with KB5078766
Microsoft released KB5078766 on March 10, 2026, a security update for Windows Server 2022 patching CVE-2026-0847 (RPC RCE), CVE-2026-0851 (Print Spooler EoP), CVE-2026-0863 (Kerberos bypass), and CVE-2026-0871 (kernel corruption).