

12 articles · Curated and written by practitioners
More 38
Microsoft Tells Users to Ignore False 'Antivirus Is Turned Off' Alerts
Microsoft has confirmed a known issue in which recent Microsoft Defender Antivirus updates trigger false "Microsoft Defender Antivirus is turned off" alerts in the Windows Security app, even though the antivirus is running normally. The bug affects all supported Windows client and server versions, including Windows 11 26H1 and Windows Server 2025, and a fix is still pending.
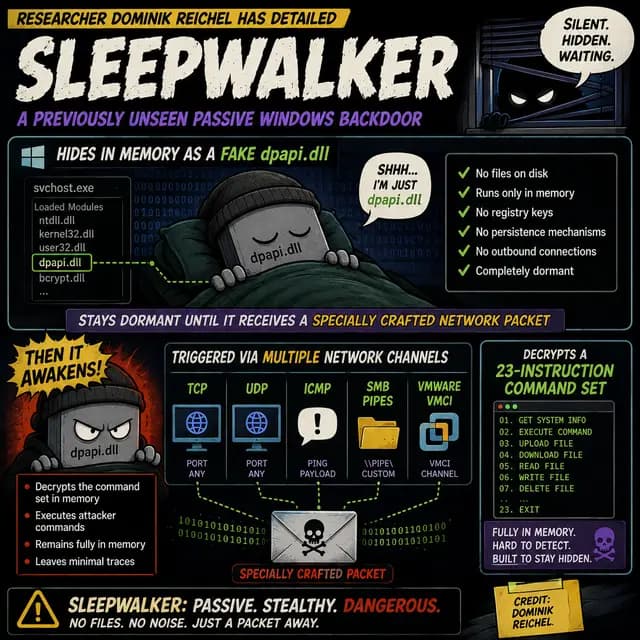
Sleepwalker: New Windows Backdoor Hides in Memory Until a 'Magic Packet' Wakes It
Researcher Dominik Reichel has detailed Sleepwalker, a previously unseen passive Windows backdoor that hides in memory as a fake dpapi.dll and stays dormant until it receives a specially crafted network packet, then decrypts a 23-instruction command set over TCP, UDP, ICMP, SMB pipes or VMware VMCI.

Cruciferra Crypter: How a $450-a-Month Service Hides RATs From EDR
Proofpoint has published an analysis of Cruciferra, a crypter service sold since autumn 2025 that combines BYOVD driver abuse, API unhooking and a modified Process Ghosting routine to deliver commodity RATs and infostealers through phishing.
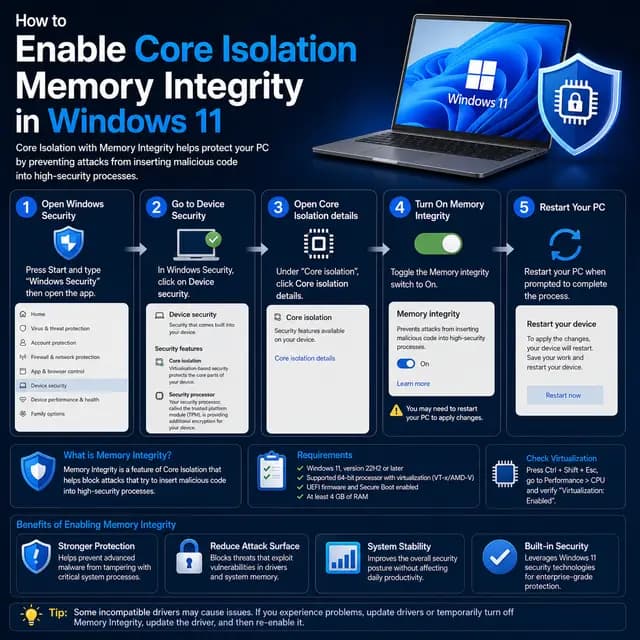
How to Enable Core Isolation Memory Integrity in Windows 11
Learn how to enable Memory Integrity (HVCI) in Windows 11 via Windows Security, Group Policy, Registry, or Intune. Includes troubleshooting for incompatible drivers and BIOS virtualization requirements.
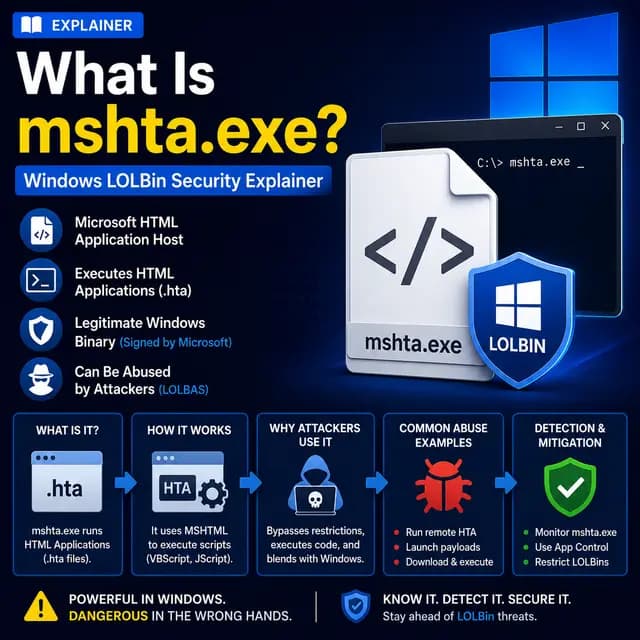
What Is mshta.exe? Windows LOLBin Security Explainer
mshta.exe is a Windows binary for running HTA files. Per MITRE ATT&CK T1218.005, attackers abuse it as a LOLBin to execute malicious VBScript/JScript, bypass AppLocker, and proxy payload execution. Covers detection, blocking, and defense strategies.
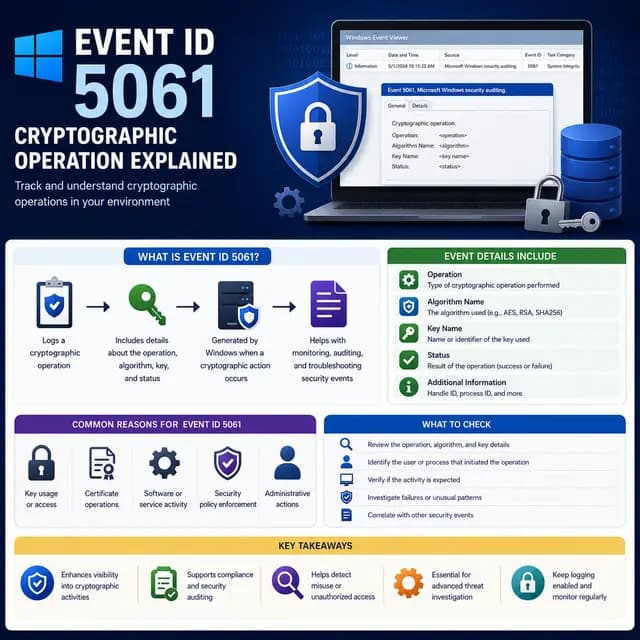
Event ID 5061: Cryptographic Operation Explained
Event ID 5061 is a Windows security audit event that logs cryptographic operations performed through a Key Storage Provider. This explainer covers what triggers it, how to read its fields, the common 0x80090016 failure, and when it signals a real security concern.
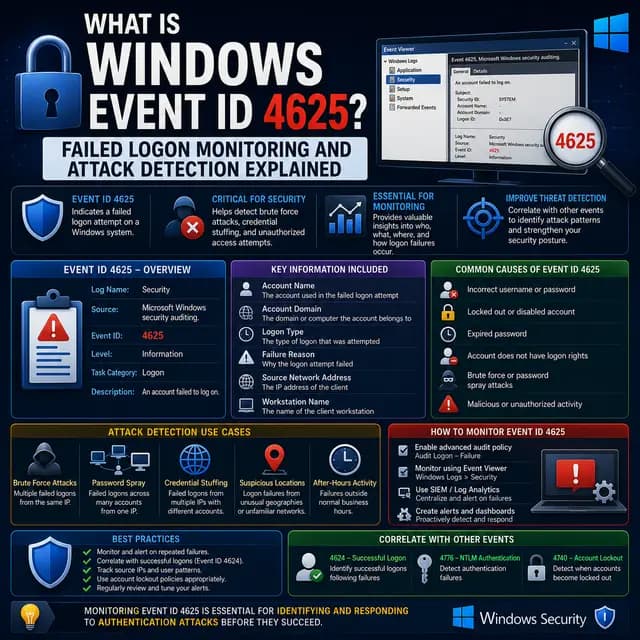
What Is Windows Event ID 4625? Failed Logon Monitoring and Attack Detection Explained
Windows Event ID 4625 logs every failed logon attempt. This explainer covers Sub Status codes, Logon Types, brute-force detection patterns, audit policy setup, and PowerShell analysis techniques.
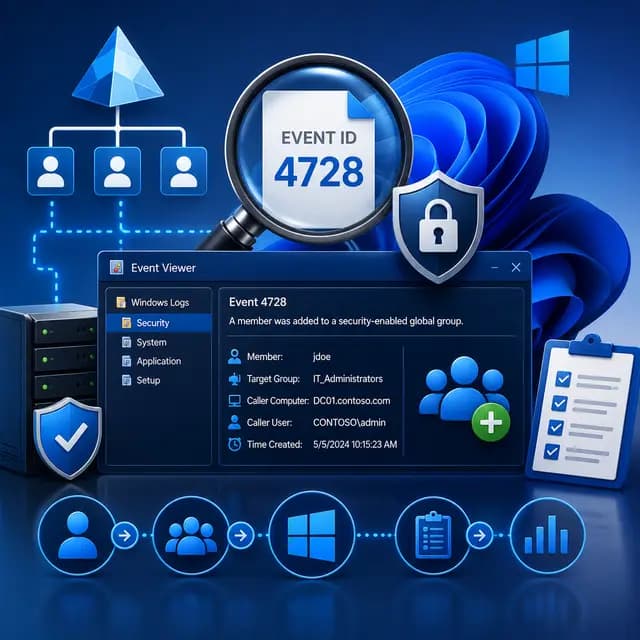
What Is Windows Event ID 4728? Active Directory Group Membership Auditing Explained
Windows Event ID 4728 logs every time a member is added to a security-enabled global group in Active Directory. This explainer covers what the event means, how it works, why it matters for security teams, and how to monitor it effectively.
Microsoft Patches "RoguePlanet" Defender Zero-Day (CVE-2026-50656) via Engine Update
Microsoft has released Malware Protection Engine 1.1.26060.3008 to fix "RoguePlanet" (CVE-2026-50656), a Microsoft Defender race-condition zero-day that a researcher using the "Nightmare Eclipse" handle said could grant SYSTEM privileges on fully patched Windows 10 and 11 devices.
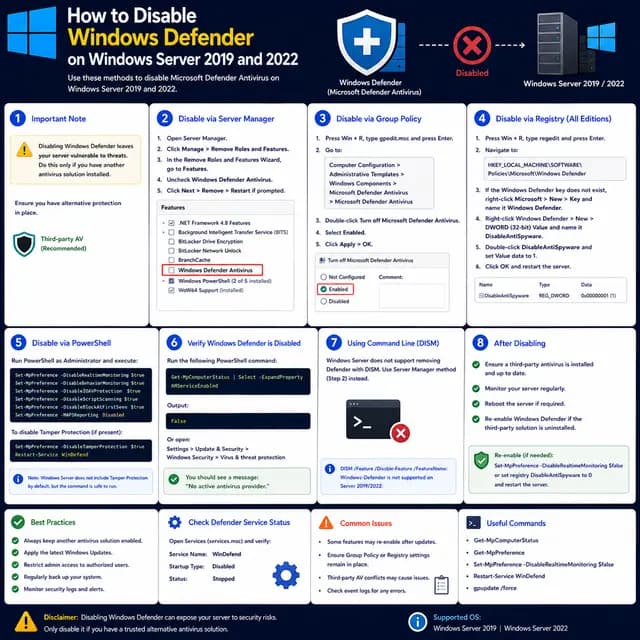
How to Disable Windows Defender on Windows Server 2019 and 2022
Step-by-step guide to disabling or uninstalling Microsoft Defender Antivirus on Windows Server 2019 and 2022 using PowerShell, Group Policy, the registry, or Server Manager - safely and with a replacement AV.
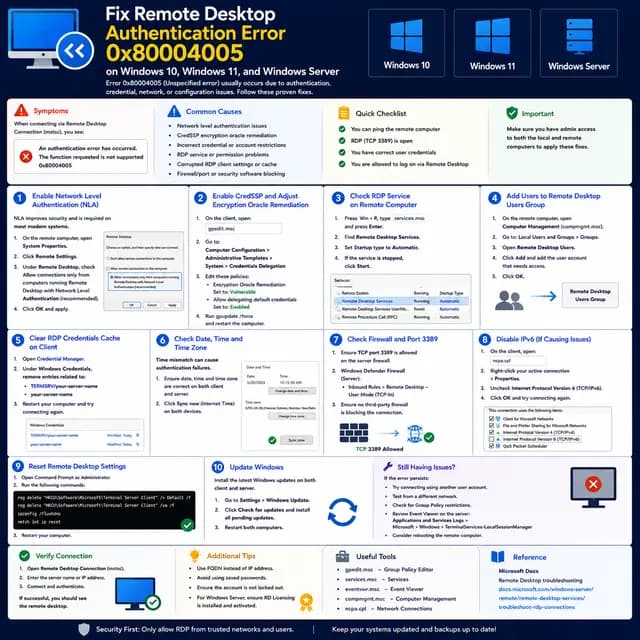
Fix Remote Desktop Authentication Error 0x80004005 on Windows 10, 11, and Windows Server
Getting "An authentication error has occurred (Code: 0x80004005)" when connecting with Remote Desktop? Fix the NLA and CredSSP causes with the right credentials, updates, and .rdp settings.
How to Activate Windows 10 ESU (Extended Security Updates): Complete Enrollment Guide
Windows 10 hit end of support on October 14, 2025. This guide walks through every ESU activation path: consumer enrollment, commercial MAK activation with slmgr, and Intune deployment, so your devices keep getting security updates.