How to Check Microsoft Defender Antivirus Signature Versions Using 5 Methods
Learn five proven methods to verify Microsoft Defender antivirus signature versions on Windows, including PowerShell, Windows Security app, Command Prompt, Registry, and Intune.

- Difficulty
- Beginner
- Time required
- 5 minutes
- Steps
- 5
- Platform
- Microsoft Defender Antivirus
- Last tested
- July 13, 2026
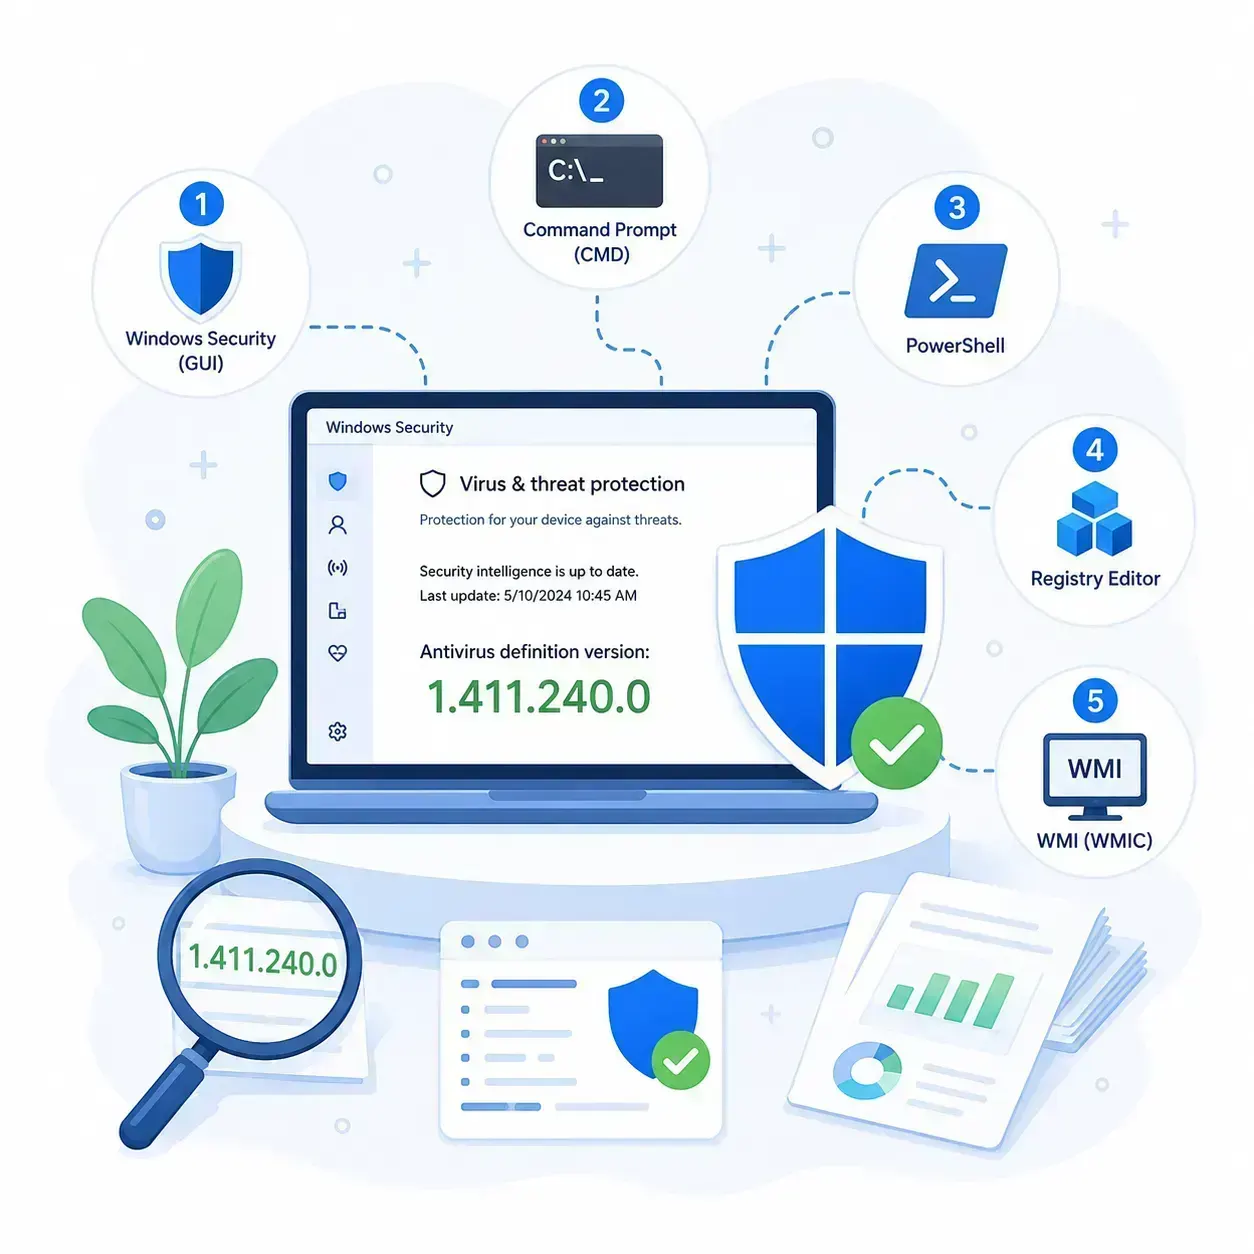
Table of contents
Quick Answer
Go to the stepsOpen the Windows Security app, go to Virus & threat protection, then click Protection updates. The Security Intelligence version number shown is your current Defender antivirus signature version. Alternatively, run Get-MpComputerStatus in PowerShell to see AntivirusSignatureVersion, AntispywareSignatureVersion, and last-update timestamps in one output.
- Open Windows Security from the Start menu.
- Click Virus & threat protection.
- Click Protection updates to view the Security Intelligence version.
- Or run Get-MpComputerStatus in an elevated PowerShell for detailed output.
Windows Security > Virus & threat protection > Protection updatesGet-MpComputerStatus | Select-Object AntivirusSignatureVersion, AntispywareSignatureVersion, AntivirusSignatureLastUpdatedExpected result: A signature version number in the format 1.xxx.xxxx.0 and a recent last-updated timestamp.
Key takeaways
- You'll learn five different methods to check the current Microsoft Defender antivirus signature version on Windows systems, from the GUI-based Windows Security app to PowerShell, Command Prompt, Registry, and centralized Intune monitoring.
- Outdated antivirus signatures leave your systems exposed to the latest malware threats. Microsoft releases security intelligence updates multiple times daily, and confirming your devices run current definitions is a basic security hygiene check.
- Use Get-MpComputerStatus in PowerShell for the most detailed signature version information, or the Windows Security app for a quick visual check.
Introduction
Microsoft Defender Antivirus protects Windows devices using regularly updated signature files, also called security intelligence updates. Microsoft releases these definitions multiple times per day to cover newly discovered viruses, ransomware, spyware, and other threats. Keeping signatures current is one of the simplest, most effective things you can do for endpoint security.
This tutorial walks through five distinct ways to check your Defender signature version. The Windows Security app gives you a quick GUI check, PowerShell returns detailed version data you can script against, and the MpCmdRun command-line tool offers direct access to Defender's core functions. You can also query the Windows Registry for programmatic monitoring, or use the Intune admin center to audit signature compliance across an entire fleet of managed devices.
Who this is for: Windows users, IT administrators, and MSPs who need to verify that Microsoft Defender signature definitions are current on local or managed devices.
Before you start
- Access
- Access to a Windows 10 or Windows 11 device with Microsoft Defender Antivirus enabled. The Intune method requires access to the Microsoft Intune admin center with enrolled devices.
- Environment
- Windows 10 or Windows 11 with Microsoft Defender Antivirus as the active antivirus solution. PowerShell and Command Prompt methods require an elevated (Administrator) session.
- Vendor
- Microsoft
- Tested environment
- Tested on Windows 11 24H2 with Microsoft Defender platform 4.18.x, July 2026.
- Last tested
- Read-only procedure
All methods tested on Windows 11 24H2 with Microsoft Defender platform version 4.18.x in July 2026.
Each individual method takes under two minutes. The full tutorial covers all five.
This procedure is read-only and does not modify your system or antivirus configuration.
1Check signature versions in Windows Security app
View the current security intelligence version through the built-in Windows Security GUI.
Start menu > Windows Security > Virus & threat protection > Protection updatesOpen the Windows Security app by typing "Windows Security" in the Start menu search bar and clicking the result.
From the main dashboard, click Virus & threat protection.
Under the Virus & threat protection updates section, click Protection updates.
The page displays your current Security Intelligence version (for example, 1.443.xxx.0), the creation date of the definitions, and the timestamp of the last successful update.
Expected result: The Protection updates page displays your current Security Intelligence version, the creation date, and the last update timestamp.
Note
No administrator privileges are required for this method. The Windows Security app refreshes this data automatically every few hours.
2Use PowerShell Get-MpComputerStatus for detailed signature data
Retrieve comprehensive signature version details using PowerShell, suitable for scripting and automation.
Open PowerShell as Administrator by right-clicking the Start button and selecting Windows PowerShell (Admin) or Terminal (Admin).
Run the following command to display antivirus and antispyware signature versions along with their last-updated timestamps:
Get-MpComputerStatus | Select-Object AntivirusSignatureVersion, AntispywareSignatureVersion, AMProductVersion, AntivirusSignatureLastUpdated, AntispywareSignatureLastUpdated
The output shows each signature type's version number and the corresponding last-update time. AMProductVersion is the antimalware engine version.
Get-MpComputerStatus | Select-Object AntivirusSignatureVersion, AntispywareSignatureVersion, AMProductVersion, AntivirusSignatureLastUpdated, AntispywareSignatureLastUpdatedExpected result: PowerShell returns the AntivirusSignatureVersion, AntispywareSignatureVersion, engine version (AMProductVersion), and last-updated timestamps for each signature type.
Note
For a broader view that includes NIS (Network Inspection System) signature data, run: Get-MpComputerStatus | Format-List Signature, Version, Updated. If the Defender module is not available, confirm the Windows Defender service is running with Get-Service WinDefend.
3Verify signatures using MpCmdRun in Command Prompt
Use the MpCmdRun.exe command-line tool to check and optionally update Defender signatures.
Open Command Prompt as Administrator by right-clicking the Start button and selecting Terminal (Admin), then switching to Command Prompt.
Run the following command to navigate to the Defender directory and trigger a signature status check:
cd "%ProgramFiles%\Windows Defender" && MpCmdRun.exe -SignatureUpdate
The tool checks for newer signatures and displays the current antivirus and antispyware signature versions in its output. If your signatures are already current, you'll see a message confirming no updates are available.
cd "%ProgramFiles%\Windows Defender" && MpCmdRun.exe -SignatureUpdateExpected result: The command outputs the current signature update status, including antivirus and antispyware signature versions. If signatures are already current, you'll see a message indicating no updates are available.
Note
MpCmdRun.exe lives in C:\Program Files\Windows Defender on most systems. On some configurations, the active platform binary is under %ProgramData%\Microsoft\Windows Defender\Platform\<version> instead. The -SignatureUpdate flag also triggers a download if newer signatures exist.
4Query signature versions from Windows Registry
Read Defender signature version data directly from the Windows Registry for custom monitoring or scripting.
HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows Defender\Signature UpdatesOpen Registry Editor as Administrator by typing "regedit" in the Start menu, right-clicking the result, and selecting Run as administrator.
Navigate to: HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows Defender\Signature Updates
Look for the AVSignatureVersion value in the right pane. This shows your current antivirus signature version.
For a scriptable approach, run this PowerShell command instead: Get-ItemProperty -Path "HKLM:\SOFTWARE\Microsoft\Windows Defender\Signature Updates" | Select-Object AVSignatureVersion, ASSignatureVersion
Get-ItemProperty -Path "HKLM:\SOFTWARE\Microsoft\Windows Defender\Signature Updates" | Select-Object AVSignatureVersion, ASSignatureVersionExpected result: The registry key displays values for AVSignatureVersion and ASSignatureVersion matching the signature versions shown by other methods.
Note
You can also browse to this key manually in regedit. The registry approach is useful for building custom monitoring scripts or integrating with third-party RMM tools.
5Monitor signature versions across devices in Intune admin center
Audit Defender signature compliance across your managed device fleet using the Intune admin center.
Intune admin center > Reports > Endpoint security > Microsoft Defender AntivirusSign in to the Microsoft Intune admin center at intune.microsoft.com with your organizational credentials.
Navigate to Reports > Endpoint security > Microsoft Defender Antivirus.
Switch to the Reports tab and click Antivirus agent status to generate a report.
Once the report loads, locate the Signature Version column to view the Defender antivirus signature version for each enrolled device. You can filter and export this data for compliance auditing.
Expected result: The report displays each enrolled device with its current Defender signature version, last sync time, and compliance state. You can filter for devices with outdated signatures.
Note
Intune reporting data syncs every 6 to 24 hours, so results may lag behind the real-time state. For an immediate check on a specific device, use one of the local methods above. This method requires Microsoft Intune licensing and enrolled Windows devices.
How to Interpret Defender Signature Version Numbers
Interpret result
Microsoft Defender signature versions follow a format like 1.443.xxx.0. The first number is always 1 for security intelligence. The second group increments with each major release cycle. The third group identifies the specific update within that cycle, and the final digit is typically 0.
A recent signature version and a last-updated timestamp within the past 24 hours indicate healthy protection. If your signatures are more than 7 days old, Microsoft considers them out of date, per its own update management documentation on Microsoft Learn. Outdated signatures don't necessarily mean you're unprotected, because Defender also uses cloud-delivered protection, behavioral monitoring, and machine learning. But current signatures remain a critical layer of defense.
When comparing versions across methods, all five should return the same signature version number. If they don't match, the device may have a stale cache or a pending update that hasn't applied yet.
Normal result: Signature version is recent (within the last 24 hours), and AntivirusSignatureAge returns 0 or 1 in PowerShell. All methods show the same version number.
Abnormal result: Signature version is older than 7 days, AntivirusSignatureAge returns a high number, or different methods show mismatched versions. This suggests update failures, network issues, or a corrupted signature cache.
Current signature
1.443.xxx.0
A recent version with a last-updated timestamp within 24 hours indicates healthy, current protection.
Outdated signature (7+ days)
AntivirusSignatureAge: 8
A signature age of 7 or more days is considered out of date by Microsoft. Force an update with Update-MpSignature.
Engine version
AMProductVersion: 4.18.xxxxx.x
The antimalware engine version. This updates less frequently than signatures and is delivered through platform updates.
Troubleshooting
PowerShell returns an error about the Defender module not being found
Warning
Cause: The Windows Defender service may be stopped or disabled, or a third-party antivirus is active and Defender is in passive mode.
Check the service status with Get-Service WinDefend. If it's stopped, start it with Start-Service WinDefend. If a third-party AV is installed, Defender may run in passive mode and the cmdlet should still work, but real-time protection will be off.
MpCmdRun.exe is not recognized as a command
Warning
Cause: The command prompt is not running from the correct directory, or the Defender platform folder path has changed after a recent platform update.
Navigate to C:\Program Files\Windows Defender first, or use the full path: "%ProgramFiles%\Windows Defender\MpCmdRun.exe" -SignatureUpdate. On some systems the active binary is under %ProgramData%\Microsoft\Windows Defender\Platform\<version>.
Signature version appears outdated despite running an update
Warning
Cause: Network connectivity issues, WSUS configuration blocking direct Microsoft Update access, or a corrupted local signature cache.
Clear the signature cache by running MpCmdRun.exe -RemoveDefinitions -DynamicSignatures from an elevated Command Prompt, then run Update-MpSignature -UpdateSource MicrosoftUpdateServer in PowerShell. If your organization uses WSUS, check that Defender definitions are approved and synced.
Intune reports show Unknown status for enrolled devices
Note
Cause: The device has not synced with Intune recently, or the device enrollment is incomplete.
On the affected device, open the Company Portal app and trigger a manual sync. In the Intune admin center, verify the device appears under Devices > All devices and that its last check-in time is recent. Allow up to 24 hours for the report to refresh.
Frequently asked questions
How often does Microsoft update Defender antivirus signatures?
Microsoft releases Defender security intelligence updates multiple times per day, typically every 1 to 3 hours when new threats are identified. The system checks for updates hourly via Windows Update by default. Enterprise environments may have different schedules based on WSUS, Configuration Manager, or Intune policies.
What is the difference between antivirus and antispyware signature versions?
Antivirus signatures detect traditional malware like viruses, trojans, and worms. Antispyware signatures target potentially unwanted programs (PUPs), adware, and spyware. Both update independently and may show different version numbers. The Security Intelligence version in Windows Security encompasses both types.
Can I check Defender signature versions remotely across multiple computers?
Yes. PowerShell remoting with Invoke-Command and Get-MpComputerStatus lets you query multiple machines. The Intune admin center provides centralized reporting for enrolled devices. Configuration Manager (SCCM) and third-party RMM tools also support fleet-wide Defender signature monitoring.
What should I do if my Defender signatures are more than 7 days old?
Force an immediate update by running Update-MpSignature in an elevated PowerShell session. If that fails, download the latest definitions manually from the Microsoft Security Intelligence updates page (mpam-feX64.exe for 64-bit). Clear any corrupted cache with MpCmdRun.exe -RemoveDefinitions -DynamicSignatures first.
Does checking the signature version require administrator privileges?
The Windows Security app method does not require admin privileges. PowerShell's Get-MpComputerStatus and the MpCmdRun.exe command-line tool require an elevated (Administrator) session. Registry browsing works without admin rights, but writing or scripting against it may need elevation.
Conclusion
Checking your Microsoft Defender antivirus signature version is a quick, read-only operation you can perform through the Windows Security app GUI, PowerShell's Get-MpComputerStatus cmdlet, the MpCmdRun command-line tool, the Windows Registry, or the Intune admin center for fleet-wide visibility. Pick whichever method fits your workflow: the Windows Security app for a fast visual check, PowerShell for scripting, or Intune for centralized enterprise monitoring.
If you find outdated signatures, force an update with Update-MpSignature or download the latest definitions from Microsoft's Security Intelligence updates page. Keeping signatures current is one of the simplest ways to maintain strong endpoint protection.
Use Get-MpComputerStatus in PowerShell for the most detailed signature version information, or the Windows Security app for a quick visual check.
Windows Security > Virus & threat protection > Protection updates, or PowerShell: Get-MpComputerStatus | Select-Object AntivirusSignatureVersion, AntivirusSignatureLastUpdatedSources4