Microsoft's Secure Boot certificate authorities issued in 2011 begin expiring in June 2026, and Microsoft is rolling out replacement 2023 certificates - chiefly Windows UEFI CA 2023 (which signs the Windows boot manager) and Microsoft Corporation KEK 2K CA 2023. The key thing to understand before checking: Secure Boot certificates do not live in the Windows certificate store. They live in UEFI firmware variables - the signature database (db) and the Key Exchange Key (kek). So the reliable way to check is to read those variables with Get-SecureBootUEFI and look for the 2023 certificate names, exactly as Microsoft documents. This is a read-only audit: it only reads firmware variables and registry status, and changes nothing. It also does not force the update - installing the certificates is a separate, deliberate action covered at the end.
Before you start
What you will learn
- You will confirm Secure Boot is enabled, then read the UEFI signature database (db) and Key Exchange Key (KEK) to check whether the Windows UEFI CA 2023 and Microsoft Corporation KEK 2K CA 2023 certificates are present, and cross-check the result in the registry and Windows Security.
- Microsoft's original 2011 Secure Boot certificates start expiring in June 2026. Devices without the 2023 certificates keep booting but stop receiving Secure Boot and Boot Manager security updates, leaving them exposed to bootkits like BlackLotus (CVE-2023-24932).
Requirements
- Local administrator rights on the device (Get-SecureBootUEFI requires an elevated session), and a UEFI-based system with Secure Boot support.
- UEFI firmware with Secure Boot (not legacy BIOS/CSM). Windows 11 (23H2/24H2/25H2) or Windows 10 22H2; Windows Server 2022+ also supported. The Get-SecureBootUEFI cmdlet must be available (it is not on legacy-BIOS systems).
- Local administrator
Good to know
- About 5 minutes per device.
- Commands verified against Microsoft and vendor documentation, July 2026.
- This procedure only reads Secure Boot UEFI variables and registry status - it does not modify your firmware or install any certificate.
Quick answer
Open PowerShell as administrator and run the db check below. If it returns True, your active Secure Boot database already contains the Windows UEFI CA 2023 certificate and your device is transitioned. False means the 2023 certificate isn't in the active db yet. Confirm Secure Boot is on first with Confirm-SecureBootUEFI, and cross-check the registry value UEFICA2023Status (which should read 'Updated').
[System.Text.Encoding]::ASCII.GetString((Get-SecureBootUEFI db).bytes) -match 'Windows UEFI CA 2023'Step-by-step tutorial
7 stepsOpen PowerShell as administrator
Get an elevated session, which is required to read Secure Boot UEFI variables.
Right-click the Start menu (or press Win + X) and choose Terminal (Admin) or Windows PowerShell (Admin). Accept the UAC prompt. Get-SecureBootUEFI returns access-denied errors in a non-elevated session.
If your device uses legacy BIOS/CSM instead of UEFI, the Secure Boot cmdlets won't work - Secure Boot requires UEFI.
Confirm Secure Boot is enabled
Make sure Secure Boot is actually on, so the db/KEK checks are meaningful.
Run Confirm-SecureBootUEFI. It returns True if Secure Boot is enabled and False if it is disabled. An error such as 'Cmdlet not supported on this platform' means the device is booting in legacy BIOS mode rather than UEFI.
Confirm-SecureBootUEFI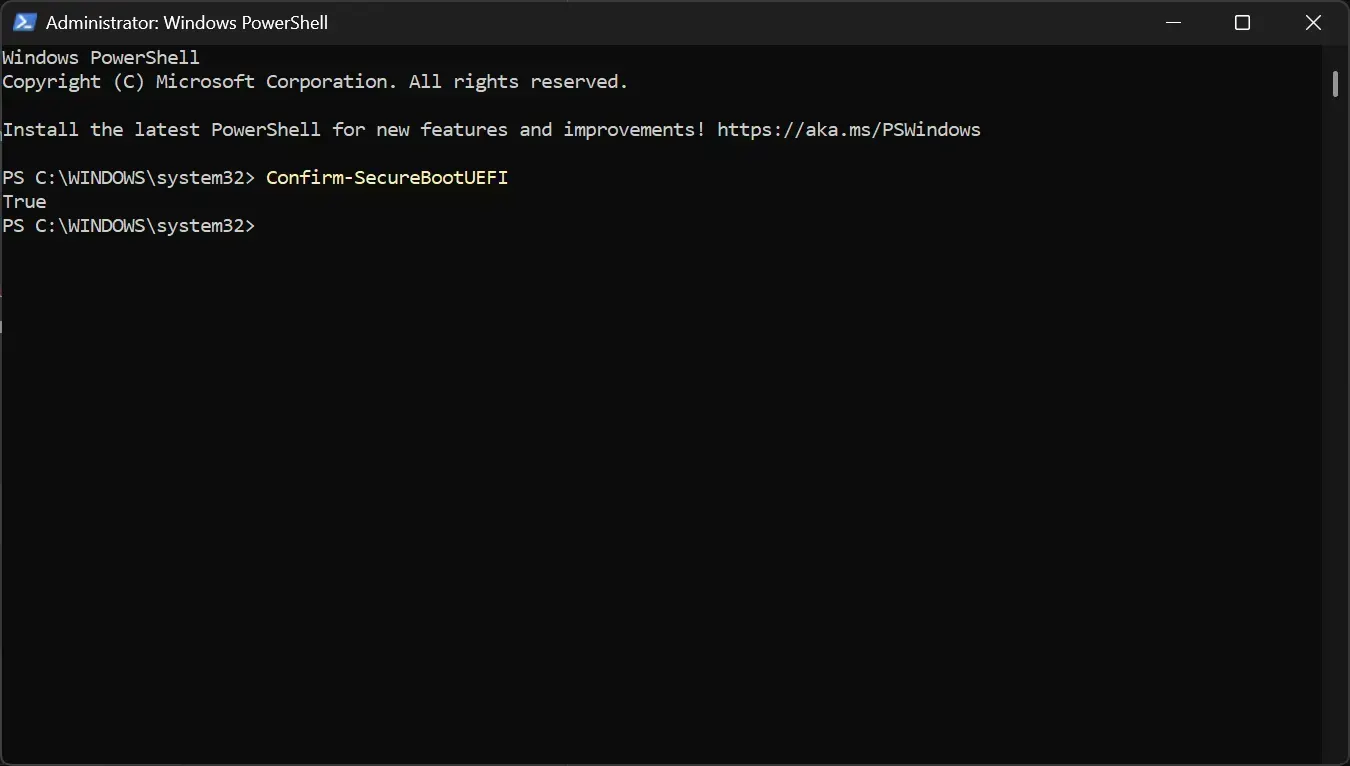
If this returns False, enable Secure Boot in firmware before relying on certificate checks - while disabled, the certificates aren't used for boot validation.
Check the active db for Windows UEFI CA 2023
Determine whether the 2023 boot-manager signing certificate is in the active signature database.
Run the command below. It reads the active Secure Boot db variable, converts it to text, and searches for the certificate name. This is Microsoft's documented check.
[System.Text.Encoding]::ASCII.GetString((Get-SecureBootUEFI db).bytes) -match 'Windows UEFI CA 2023'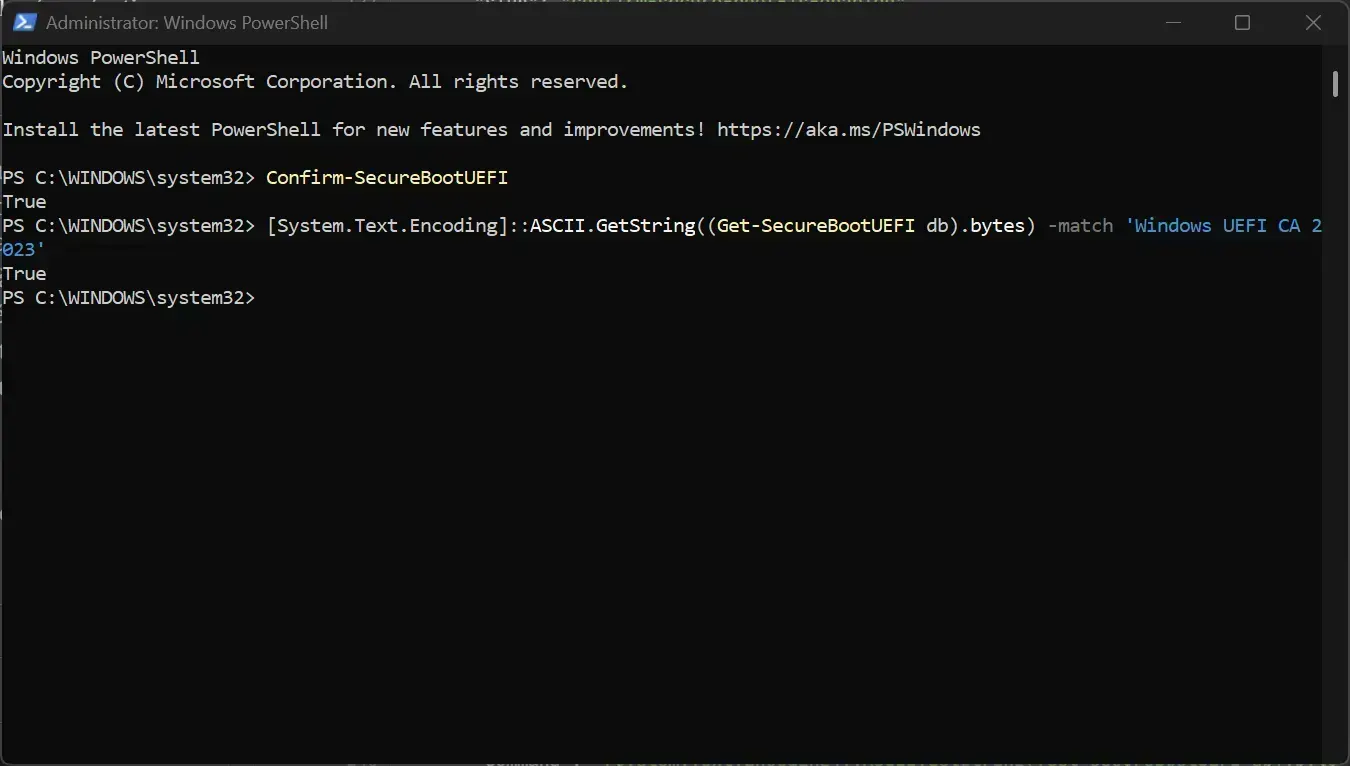
The active db is what the firmware currently uses to validate boot components, so this is the check that matters most.
Check the KEK for the 2023 Key Exchange Key
Confirm the 2023 KEK is present, which is what allows future db updates to be signed.
Run the command below to search the kek variable for the 2023 KEK certificate.
[System.Text.Encoding]::ASCII.GetString((Get-SecureBootUEFI kek).bytes) -match 'Microsoft Corporation KEK 2K CA 2023'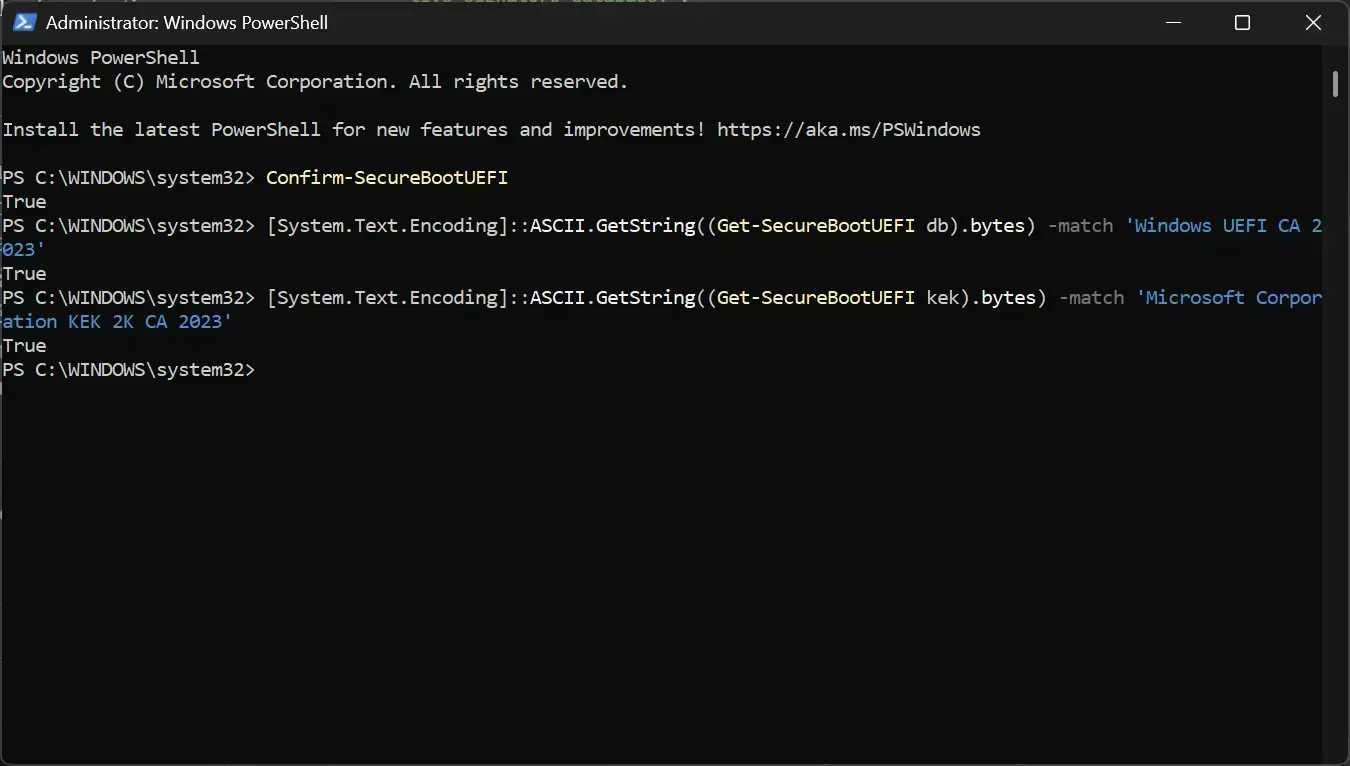
The KEK 2023 usually arrives first (via a Secure Boot KEK update); the db certificate follows. A True KEK with a False db means the transition is in progress.
Optionally check the firmware default db
See whether the OEM baked the 2023 certificate into firmware (informational only).
Run the command below against dbdefault, the firmware's built-in database. A False here is not a problem on its own - it only means the certificate isn't natively embedded by the OEM. What matters for protection is the active db result from step 3.
[System.Text.Encoding]::ASCII.GetString((Get-SecureBootUEFI dbdefault).bytes) -match 'Windows UEFI CA 2023'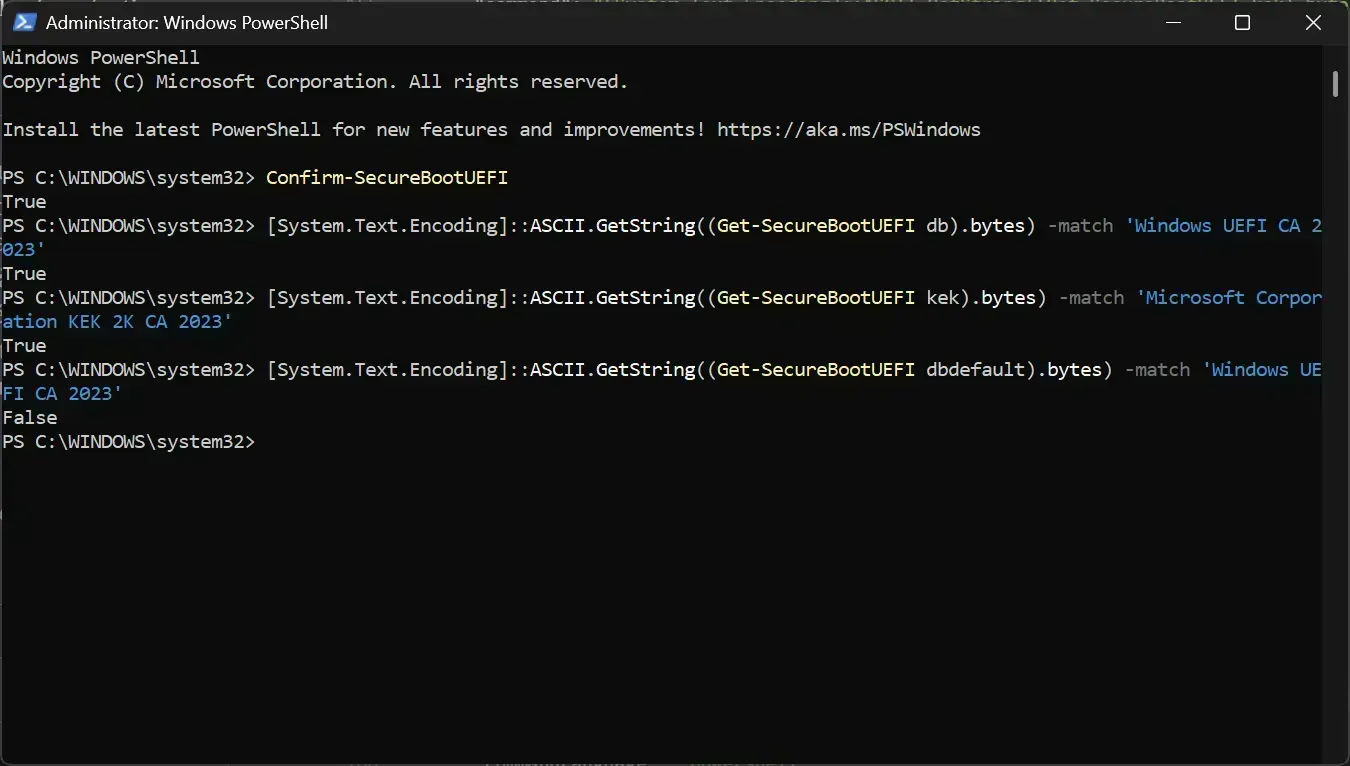
Many PCs made since 2024 ship with the 2023 certificates in firmware; older ones receive them into the active db via Windows Update.
Cross-check the registry servicing status
Read Microsoft's servicing status value, which reflects the OS-side update state.
HKEY_LOCAL_MACHINE\SYSTEM\CurrentControlSet\Control\SecureBoot\ServicingQuery the Secure Boot servicing key. The value UEFICA2023Status should ultimately read Updated. A value of UEFICA2023Error present under this path indicates a failed deployment. Run:
Get-ItemProperty 'HKLM:\SYSTEM\CurrentControlSet\Control\SecureBoot\Servicing' | Format-List UEFICA2023*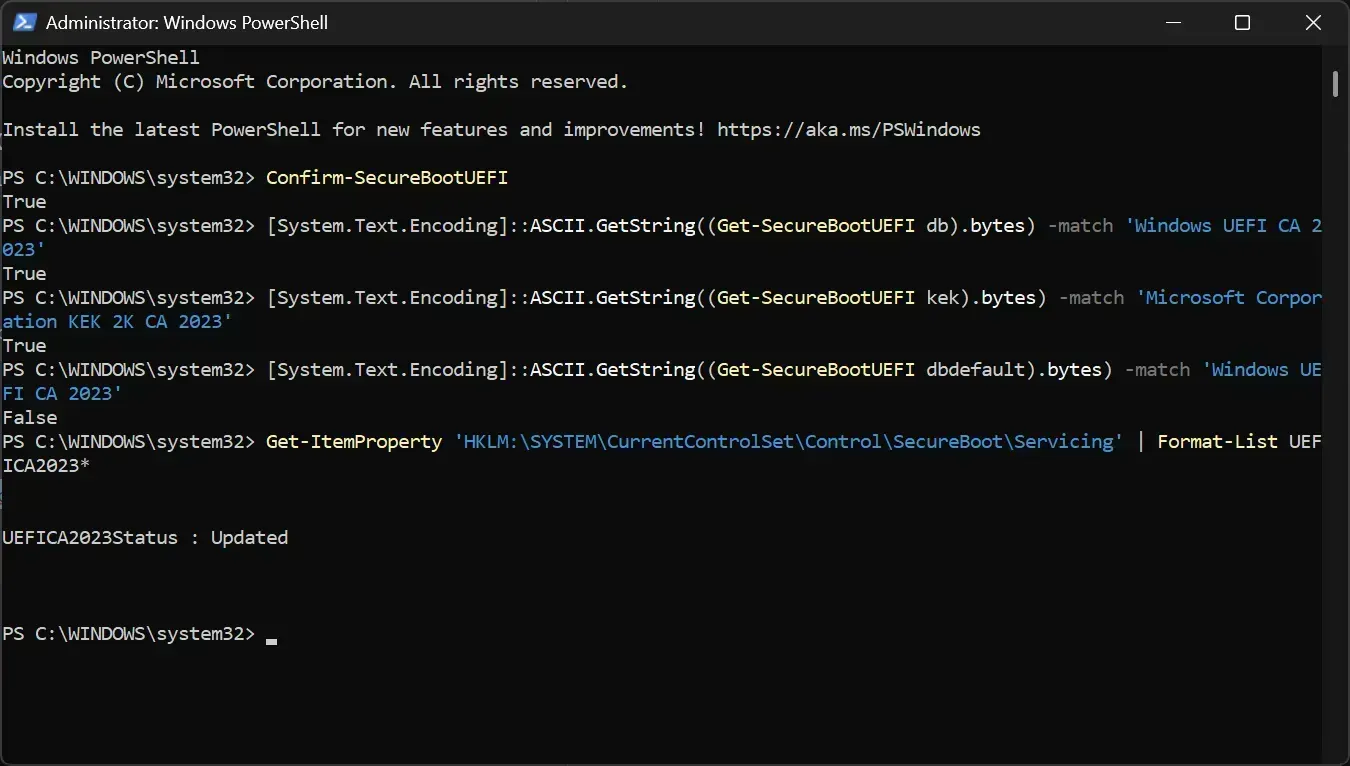
On some newer PCs that shipped with the 2023 certificates, this status can stay 'NotStarted' even though the db check is True - in that case trust the db result from step 3.
Confirm visually in Windows Security or Update history
Get a non-PowerShell confirmation for less technical verification.
Windows Security > Device security > Secure BootOpen Windows Security > Device security > Secure Boot and check the status badge (green means no recommended action). Alternatively, open Settings > Windows Update > Update history > Other updates and look for a Secure Boot Allowed Key (KEK) Update entry, which indicates the certificate update was delivered.
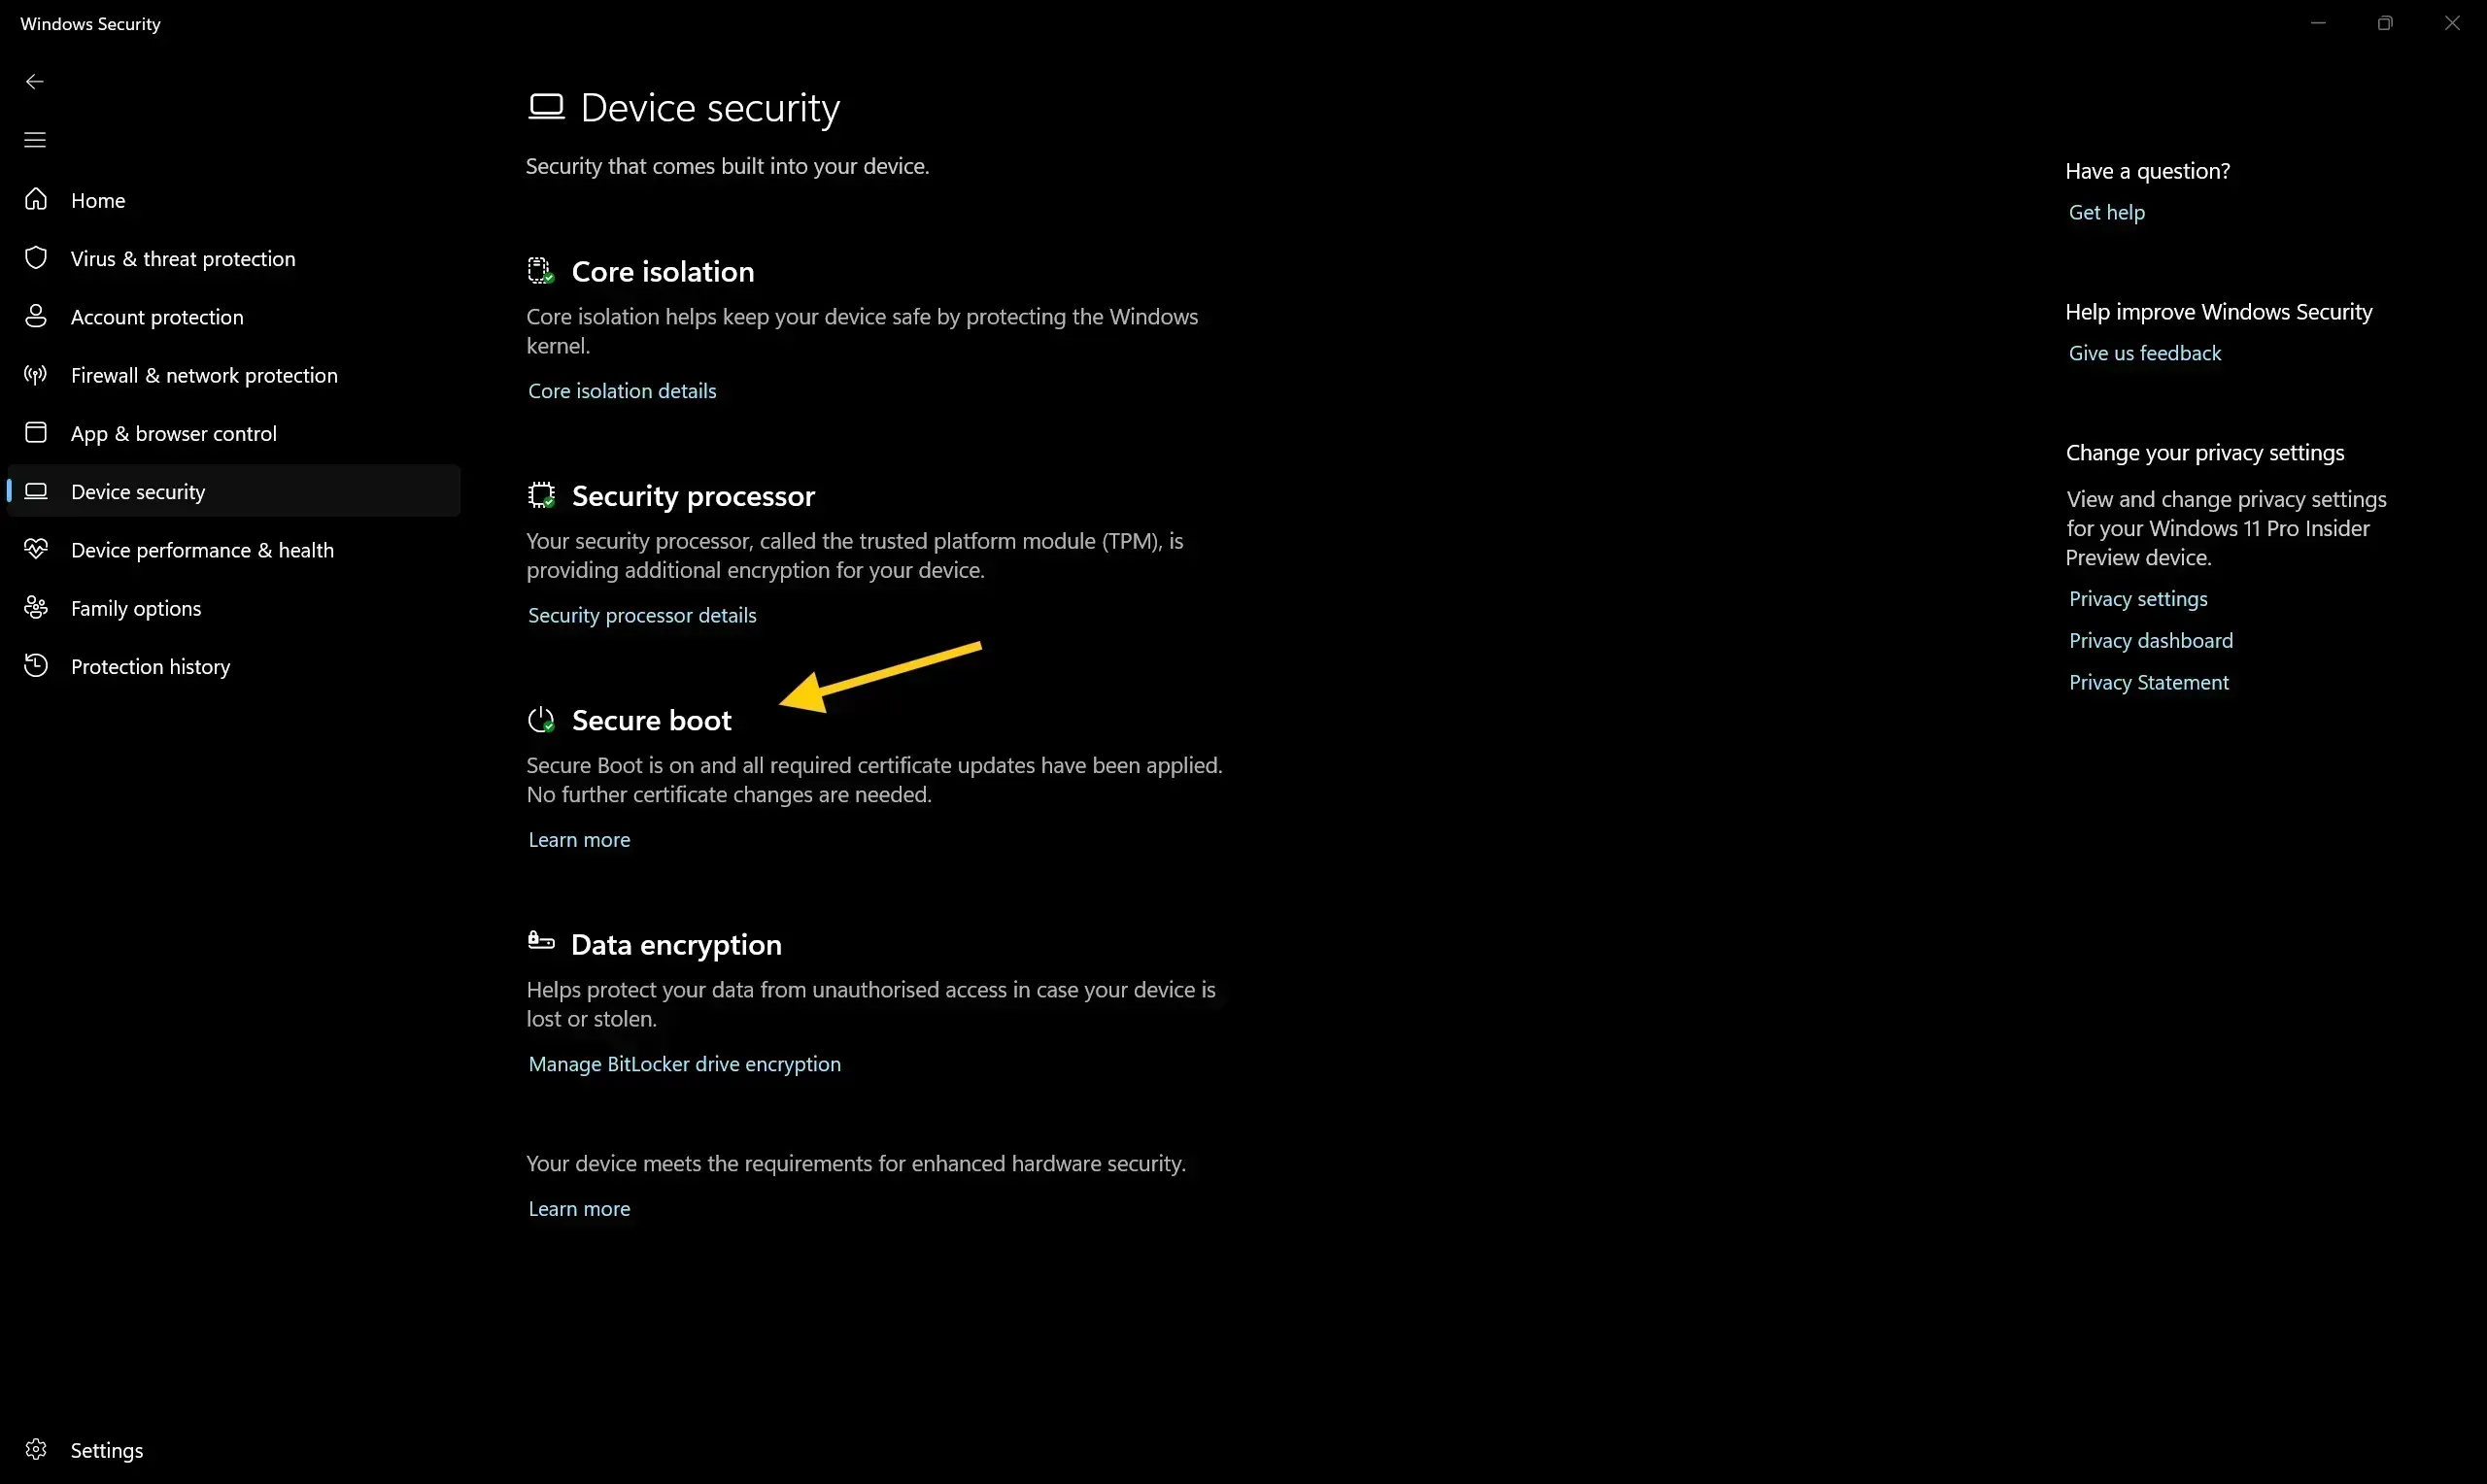
This is a convenience check; the authoritative confirmation is the active-db PowerShell result.
How to Interpret the Results
The single most important result is step 3: if the active db check returns True for Windows UEFI CA 2023, your device has transitioned and will keep receiving Secure Boot and Boot Manager updates past June 2026. If it returns False, the 2023 certificate isn't in the active db yet - but do not panic: an unmodified device with the old 2011 certificates still boots normally after June 2026. What it loses is the ability to receive future Secure Boot / Boot Manager security fixes, which is what leaves it exposed to bootkits over time. A True kek with a False db means the transition has started but isn't complete. A False dbdefault is irrelevant on its own. And a registry status of NotStarted on a machine whose db check is True simply reflects a device that shipped with the certificates rather than receiving them through servicing - trust the db result in that case.
- Confirm-SecureBootUEFI = True; db check = True; kek check = True; UEFICA2023Status = Updated (or NotStarted on a device that shipped with the certs).
- db check = False (2023 cert not in active db yet), or a UEFICA2023Error value present in the registry (a failed deployment needing attention).
- Windows UEFI CA 2023 is in the active database; device keeps getting Secure Boot updates.
- Still on 2011 certs; boots fine, but won't receive future Secure Boot fixes until updated.
- Investigate firmware/KEK before retrying the certificate deployment.
Troubleshooting
The db check returns False
Cause: The 2023 certificate hasn't been applied to the active database yet - the device may be missing recent cumulative updates or the deployment hasn't been triggered.
Install all pending Windows updates, then trigger deployment via the AvailableUpdates value (0x5944) or the Secure Boot certificate deployment Group Policy. Suspend BitLocker first, and re-run the db check after a reboot.
Get-SecureBootUEFI errors or 'not supported on this platform'
Cause: The device is booting in legacy BIOS/CSM mode, or the OS/PowerShell build doesn't expose the cmdlet.
Confirm the system boots in UEFI mode with Secure Boot capability. On unsupported or legacy systems, use the firmware/BIOS Secure Boot screens or an OEM tool instead.
UEFICA2023Status stays 'NotStarted' on a new PC
Cause: The device shipped with the 2023 certificates already in firmware, so the OS servicing flow never ran.
This is expected. Rely on the active-db PowerShell check (step 3); if it returns True, the device is protected regardless of the registry status.
A UEFICA2023Error value appears in the registry
Cause: The certificate deployment failed - often due to firmware limitations or a missing PK-signed KEK.
Apply the latest OEM firmware update, confirm the 2023 KEK is present, then retry deployment. Consult the OEM's Secure Boot advisory for the specific model.
The db check is False even though the OEM says firmware includes the cert
Cause: There is a difference between the firmware default db and the active db; vendor implementations vary.
Check dbdefault as well (step 5). If the certificate is only in dbdefault, apply the OS-side update or an OEM tool to populate the active db.
Frequently asked questions
Will my PC stop booting after June 2026 if it doesn't have the 2023 certificates?
No. Microsoft and OEMs confirm devices continue to boot normally with the expired 2011 certificates. What they lose is the ability to receive future Secure Boot and Boot Manager security updates, which leaves them exposed to boot-level malware over time.
Where are Secure Boot certificates actually stored?
In UEFI firmware variables - the signature database (db) and Key Exchange Key (kek) - not in the Windows certificate store. That's why the check reads them with Get-SecureBootUEFI rather than browsing Cert: paths.
What does a True result from the db check mean?
It means the Windows UEFI CA 2023 certificate is present in your active Secure Boot database, so your device has transitioned and will keep receiving Secure Boot updates past the 2011 expiry.
How do I install the 2023 certificates if they're missing?
Keep Windows fully updated, then trigger deployment with the AvailableUpdates registry value (0x5944) or the 'Enable Secure Boot certificate deployment' Group Policy. Suspend BitLocker first, as the firmware change can prompt BitLocker recovery.
Does this affect Linux, ESXi, or other non-Windows boot loaders?
Yes. Third-party boot loaders are signed under the Microsoft UEFI CA, so systems relying on them also need the corresponding 2023 CA to keep validating after the 2011 certificates expire.
Can I check this on Windows 10?
Yes, on Windows 10 22H2 (with Extended Security Updates where applicable). The PowerShell db/kek checks work the same; certificate delivery depends on the device still receiving the relevant updates.