How to Configure Copilot in Microsoft Edge Using Intune
Create an Intune settings catalog policy to control Microsoft 365 Copilot features in Microsoft Edge — toolbar icon, page context access, and browsing history sharing — then deploy and monitor it.

- Difficulty
- Intermediate
- Time required
- 30 minutes
- Steps
- 8
- Platform
- Microsoft Intune
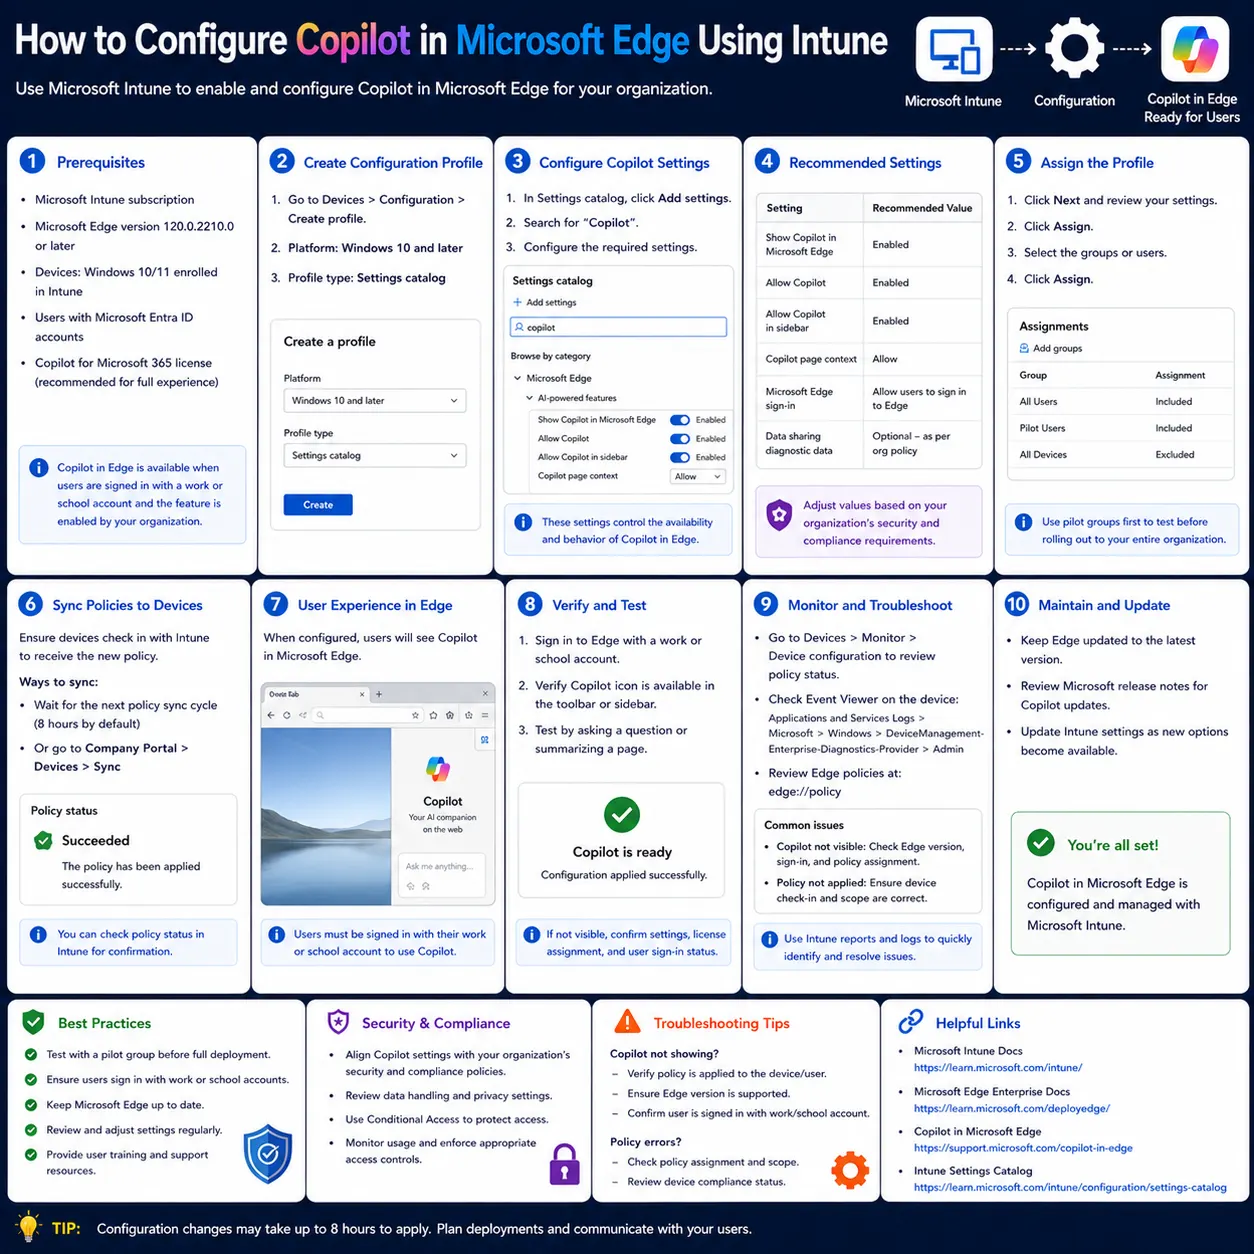
Table of contents
Quick Answer
Go to the stepsCreate a Settings Catalog configuration profile in the Intune admin center under Devices > Windows > Configuration, search the Settings Picker for "Copilot" and add the Microsoft Edge Copilot policies you want to manage, toggle each setting, then assign the profile to an Entra security group. Sync the policy and confirm the settings are managed on a targeted device.
- In the Intune admin center, go to Devices > Windows > Configuration and create a new policy with the Windows 10 and later platform and Settings Catalog profile type.
- In the Settings Picker, search for "Copilot", choose the Microsoft Edge category, and add the Copilot policy settings you want to control.
- Toggle each selected setting on, optionally add scope tags, then assign the profile to a pilot Entra security group.
- Review and click Create, then trigger an Intune sync so devices check in rather than waiting up to 90 minutes.
- Check the profile's overview page for check-in status, and verify the settings show as greyed out with a suitcase icon in Edge on a targeted device.
Devices > Windows > ConfigurationExpected result: A new Windows configuration profile appears in the Intune admin center, and on targeted devices the selected Copilot settings in Edge (Settings > Appearance > Copilot and Sidebar) are greyed out with a suitcase icon indicating organizational management.
Key takeaways
- You will learn how to build, deploy, and monitor a Microsoft Intune settings catalog policy that controls Microsoft 365 Copilot features in Microsoft Edge for your managed users. This includes selecting the right Copilot policies, assigning them to an Entra security group, and confirming they apply on targeted devices.
- Copilot introduces AI features that touch page content and browsing history, so organizations need to enable, restrict, or block these capabilities to meet compliance requirements. Centralizing this control through Intune ensures consistent, enforceable settings across every managed device rather than relying on individual users.
- Intune's settings catalog lets you centrally enable, restrict, or configure Microsoft 365 Copilot features in Microsoft Edge for Entra ID users on managed devices.
Introduction
Microsoft Intune exposes a set of settings catalog policies that let you manage how Microsoft 365 Copilot behaves inside Microsoft Edge. With these policies you can decide whether the Copilot Chat icon appears in the Edge for Business toolbar, whether Copilot in the sidepane can read page content for Entra ID profiles, and whether tenant-approved browsing history is shared with Microsoft 365 Copilot Search.
These controls apply only to users signed in to Edge with an Entra ID account — they do not affect personal Microsoft account profiles. Most Copilot features also require an eligible Microsoft 365 Copilot license, and Edge version 145 or later is recommended so the latest settings apply cleanly.
The workflow follows a familiar Intune pattern: create a Windows 10 and later configuration profile using the Settings Catalog profile type, search for and add the individual Copilot policies, toggle each one, assign the profile to an Entra security group, then sync and monitor the rollout. You start with a pilot group and expand once testing succeeds, and you confirm success by checking that the settings appear greyed out with a suitcase icon in Edge on a targeted device.
Who this is for: This guide is for sysadmins, MSPs, and IT pros who manage Windows devices and Microsoft Edge through Intune. It assumes familiarity with the Intune admin center and Entra ID security groups.
Before you start
- Access
- You need administrative access to the Microsoft Intune admin center with permission to create and assign Windows configuration profiles. You also need access to the Microsoft 365 admin center to confirm the target Entra security group and Microsoft 365 Copilot license assignments.
- Required roles
- Intune Administrator (or a role with permission to manage device configuration profiles)
- Intune Administrator
- Required licenses
- Valid Microsoft Intune license assigned to the managed Windows devices
- Eligible Microsoft 365 Copilot license for target users (required for Copilot features and some policies such as sharing browsing history with Copilot Search)
- Microsoft Intune
- Microsoft 365 Copilot
- Vendor
- Microsoft
- Tested environment
- Microsoft Intune admin center with Windows 11 and Microsoft Edge 145
- Administrator permissions required
Note: Policies only apply to Entra ID sign-ins
Edge Copilot settings deployed through Intune apply exclusively to users signed in to Microsoft Edge with an Entra ID account. They do not apply to users signed in with personal Microsoft accounts, so verify the target profile type before assuming coverage.
Note: Pilot before broad rollout
Assign the profile to a small pilot group of users or devices first and confirm the expected behavior before rolling it out to a larger population. This limits impact if a setting is misconfigured.
1Confirm prerequisites and licensing
Ensure the environment meets all requirements before building the Copilot policy.
Before creating any policy, verify each of the following:
- Intune enrollment: Target Windows devices are managed via Intune and have a valid Intune license assigned.
- Edge version: Devices are running Microsoft Edge version 145 or later (recommended) so the latest Copilot policy settings apply reliably.
- Sign-in method: Users sign in to Microsoft Edge with an Entra ID account. These policies do not apply to profiles signed in with personal Microsoft accounts.
- Copilot licensing: Target users have an eligible Microsoft 365 Copilot license for the license-dependent settings (such as browsing history sharing) to take effect.
- Target group: A Microsoft Entra security group containing the target users or devices already exists.
Expected result: You have a confirmed list of Intune-enrolled devices on Edge 145+, Entra ID sign-in in use, Copilot licenses assigned to target users, and an existing Entra security group ready for assignment.
Note
Most Edge Copilot settings require users to be signed in to Edge with an Entra ID account, and several features also require an eligible Microsoft 365 Copilot license. Verify both before assuming a policy failure is technical.
2Understand the available Edge Copilot policies
Choose which Copilot settings to manage based on your organization's business needs.
Intune exposes four Edge Copilot policies in the settings catalog. Review each and decide which to configure — you do not need to set all of them:
- Microsoft 365 Copilot Chat toolbar icon (
Microsoft365CopilotChatIconEnabled): Controls whether the Microsoft 365 Copilot Chat icon appears in the Microsoft Edge for Business toolbar, for both licensed and unlicensed users. Enabled shows the icon; disabled hides it. - Entra sidepane page content access (
EdgeEntraCopilotPageContext): Controls whether Copilot in the Edge sidepane can access page content (page summarization and contextual queries) for users signed in with an Entra account. Enabled allows access; disabled blocks it. - Page context for Microsoft Entra ID profiles (
CopilotPageContext): Controls page content access for Copilot in the Edge sidebar for Entra ID Edge profiles (not MSA profiles). Enabled allows access; disabled blocks it. This policy does not control Copilot with enterprise data protection (EDP). - Share tenant-approved browsing history with Copilot Search (
ShareBrowsingHistoryWithCopilotSearchAllowed): Controls whether Edge browsing history is shared with Microsoft 365 Copilot Search for more relevant results. Enabled or not configured shares history by default (users can toggle it off in Edge settings); disabled prevents sharing.
Expected result: You have a shortlist of the specific Edge Copilot policies you intend to configure and know the enabled/disabled behavior for each.
Note
The browsing history sharing feature is available only to users signed in with an Entra ID account who also hold an eligible Microsoft 365 Copilot license.
3Create a new settings catalog configuration profile
Start a Windows configuration profile using the settings catalog.
Intune admin center > Devices > Windows > Configuration > Create > New PolicySign in to the Microsoft Intune admin center and go to Devices > Windows > Configuration, then create a new policy.
- Select Windows 10 and later as the Platform.
- Select Settings catalog as the Profile type, then click Next.
- On the Basics tab, enter a descriptive profile Name (for example,
Configure Copilot Settings for Edge) and an optional Description. - Click Next to continue.
Expected result: A new settings catalog profile is started for Windows 10 and later, named and ready to add settings.
4Add the Copilot Edge settings in the Settings Picker
Select the specific Edge Copilot policies you want to configure.
Intune admin center > Devices > Windows > Configuration > (profile) > Configuration settings > Add settingsOn the Configuration settings tab, click Add settings to open the Settings picker.
1. In the search box, type Copilot. 2. From the results, select the Microsoft Edge category — this lists the Copilot policy settings available exclusively for the Edge browser. 3. Select the individual Edge Copilot settings you decided to manage, for example: - EdgeEntraCopilotPageContext - CopilotPageContext - Microsoft365CopilotChatIconEnabled - ShareBrowsingHistoryWithCopilotSearchAllowed 4. Close the Settings picker when you have added your chosen settings.
Expected result: The selected Edge Copilot settings appear in the Configuration settings list, ready to be toggled.
Note
Only add the settings that align with your business needs — you do not have to configure all four.
6Assign the policy and create it
Target the policy at an Entra security group and finalize it.
Intune admin center > Devices > Windows > Configuration > (profile) > Assignments > Review + createOn the Assignments tab, under Included groups, select the Entra security group(s) that should receive the policy.
- Start by assigning the profile to a small pilot group of users or devices. Once testing confirms the settings apply correctly, gradually roll it out to a broader audience.
Click Next, then on the Review + create tab, carefully review all configured settings and click Create.
Expected result: The new profile appears in the list of Windows configuration profiles in the Intune admin center and is assigned to the selected group(s).
Note
Testing on a pilot group first reduces the risk of unexpected Copilot behavior changes across the full user base.
7Sync Intune and monitor policy assignments
Speed up delivery and confirm successful deployment.
Intune admin center > Devices > Windows > Configuration > Configure Copilot Settings for Edge > OverviewBy default, policy updates can take up to 90 minutes to reach targeted devices. To speed this up, trigger an Intune policy sync so devices immediately check in and retrieve the latest policies (for example, from the Company Portal, the device settings sync option, or the Intune admin center device action).
To monitor deployment:
- Go to Devices > Windows > Configuration and select the Configure Copilot Settings for Edge profile.
- On the profile's Overview page, review the device and user check-in status.
- Click View report to see the specific device or user names for which deployment succeeded or failed.
Expected result: The profile overview shows successful device and user check-in counts, and the report lists which devices or users received the policy.
Note
If you see assignment failures, review the Intune Management Extension (IME) logs on the affected device to determine the cause before retrying.
8Verify the end-user experience in Edge
Confirm the managed settings are applied on target devices.
Edge > Settings > Appearance > Copilot and Sidebar > App specific settings > CopilotOn a Windows 11 device that is targeted by the policy, launch Microsoft Edge while signed in with the Entra ID account, then:
1. Go to Settings > Appearance > Copilot and Sidebar. 2. Under App specific settings, select Copilot. 3. Confirm that the relevant settings are greyed out (cannot be changed by the user), such as: - Show Copilot button on the toolbar - Allow Copilot to use browser content - Allow Copilot to transcribe your video
A suitcase icon next to each setting indicates it is now managed by your organization through the Intune policy.
Expected result: The targeted Copilot settings in Edge appear greyed out with a suitcase icon, confirming the Intune policy is enforced and users cannot override it.
Note
If the settings are still editable, confirm the device has checked in, the user is signed in with an Entra ID account, and Edge is on version 145 or later.
Confirming the Copilot Edge Policy Is Applied
Confirm configuration
After the configuration profile is created, assigned, and synced, you confirm success in two places: the Intune admin center and the end-user device. In Intune, the policy's overview page reports device and user check-in status, and the View report button lists the specific devices or users where deployment succeeded or failed. On a targeted Windows 11 device, open Edge and navigate to Settings > Appearance > Copilot and Sidebar > App specific settings > Copilot. The settings you configured should be greyed out and show a suitcase icon, indicating they are now managed by your organization rather than by the user. Remember that policy delivery can take up to 90 minutes unless you trigger a manual Intune sync.
Normal result: The Intune policy overview shows the targeted devices and users with a Succeeded check-in status. On a target Windows 11 device, the configured Copilot settings under Settings > Appearance > Copilot and Sidebar > App specific settings > Copilot are greyed out and display a suitcase icon, meaning the user can no longer change them.
Abnormal result: The overview page reports a Failed or Error status for one or more devices, or the Copilot settings remain editable (no suitcase icon) on the target device. Confirm the device is enrolled and assigned to the group, the user is signed in to Edge with an Entra ID account, Edge is on a supported version, and allow time for a sync — then review the Intune IME logs to identify the exact cause of failure.
Managed toolbar icon setting
Show Copilot button on the toolbar — greyed out with suitcase icon
Corresponds to the Microsoft365CopilotChatIconEnabled policy; the user cannot change it because the organization manages it.
Managed page content setting
Allow Copilot to use browser content — greyed out with suitcase icon
Reflects the Entra page content / page context policies being enforced through Intune.
Intune check-in status
Succeeded — 12 devices, 12 users
Shown on the profile's overview page; use View report to see the individual device and user names.
Policy propagation delay
Up to 90 minutes before delivery
Trigger a manual Intune policy sync to force devices to check in immediately instead of waiting.
Troubleshooting
Copilot settings deployed via Intune do not apply to some users
Warning
Cause: Those users are signed in to Microsoft Edge with a personal Microsoft account (MSA) instead of an Entra ID account. Edge Copilot policies deployed through Intune apply exclusively to Entra ID Edge profiles.
Confirm the affected users are signed in to Microsoft Edge with their Entra ID work account, not a personal Microsoft account. Have them switch to their organizational profile in Edge, then re-check the setting under Settings > Appearance > Copilot and Sidebar > App specific settings > Copilot.
Policy takes a long time to reach targeted devices
Note
Cause: Intune configuration profile updates can take up to 90 minutes to download to targeted devices during a normal check-in cycle.
Trigger a manual Intune policy sync to force targeted devices to immediately check in and retrieve the latest policies, rather than waiting for the standard check-in interval. You can initiate the sync from the device, Company Portal, the Intune admin center, or PowerShell.
Policy assignment shows as failed in the overview report
Warning
Cause: The device did not receive or could not apply the profile — often due to enrollment issues, targeting the wrong group, or a policy-processing error on the client.
Open the profile's overview page and use the view report button to identify the specific devices or users that failed, then review the Intune Management Extension (IME) logs on the affected device to determine the exact cause and remediate it.
Copilot features work as expected but the intended toggles are still editable by users
Note
Cause: The relevant Copilot policy setting was not added in the Settings Picker or was not enabled with the toggle before the profile was created.
Edit the configuration profile and confirm the target settings (for example Microsoft365CopilotChatIconEnabled or ShareBrowsingHistoryWithCopilotSearchAllowed) are added under the Microsoft Edge category and toggled on. Save, then re-sync the device and verify the greyed-out setting and suitcase icon in Edge.
Expected Copilot policies do not appear in the Settings Picker
Note
Cause: An older version of Microsoft Edge on the device may not support the latest Copilot policy settings.
Ensure managed devices are running Microsoft Edge version 145 or later, which supports the current Copilot policies, and search for the term "Copilot" under the Microsoft Edge category in the Settings Picker to locate the individual settings.
Frequently asked questions
Do Edge Copilot Intune policies apply to users signed in with personal Microsoft accounts?
No. Copilot settings deployed through Intune apply exclusively to users signed in to Microsoft Edge with an Entra ID account. They do not apply to users signed in with personal Microsoft accounts (MSA).
Do users need a Microsoft 365 Copilot license for these Edge policies to work?
Most of the Edge Copilot settings you manage via Intune require users to be signed in with an Entra ID account and to have an eligible Microsoft 365 Copilot license. For example, sharing tenant-approved browsing history with Microsoft 365 Copilot Search is available only to Entra ID users with an eligible Copilot license.
How long does it take for the Copilot Edge policy to apply to devices?
Updates may take up to 90 minutes to download to devices targeted by the configuration profile. You can speed this up by manually triggering an Intune policy sync, which forces devices to immediately check in and retrieve the latest policies.
Which Copilot settings can I control in Microsoft Edge through Intune?
Intune exposes four Edge Copilot policies: showing the Microsoft 365 Copilot Chat icon in the Edge for Business toolbar, Copilot access to page content in the sidepane for Entra profiles, Copilot access to page context for Entra ID profiles, and sharing tenant-approved browsing history with Microsoft 365 Copilot Search.
Why are the Copilot settings greyed out in Microsoft Edge?
The settings are greyed out because they are managed by your organization through an Intune policy. A suitcase icon appears next to each managed setting, indicating users cannot change it manually.
What Edge version is recommended for configuring Copilot settings via Intune?
Microsoft Edge version 145 or later is recommended, because most of the latest and updated Copilot features can be applied without issues on that version or newer.
Conclusion
You created an Intune settings catalog configuration profile, added the individual Microsoft Edge Copilot policies you wanted to control, enabled them with the toggle switches, assigned the profile to an Entra security group, and monitored the deployment. You then verified on a targeted Windows 11 device that the managed Copilot settings appear greyed out with a suitcase icon in Edge.
Intune's settings catalog lets you centrally enable, restrict, or configure Microsoft 365 Copilot features in Microsoft Edge for Entra ID users on managed devices.
Devices > Windows > Configuration