How to Delete Windows Autopilot Devices from Intune, Entra ID, and M365
Learn the correct deletion sequence to fully remove stale Windows Autopilot devices from Intune, Entra ID, and Microsoft 365 - including hybrid-joined devices, orphaned records, and BitLocker key cleanup.

- Difficulty
- Intermediate
- Time required
- 30-45 minutes
- Steps
- 7
- Platform
- Microsoft Intune
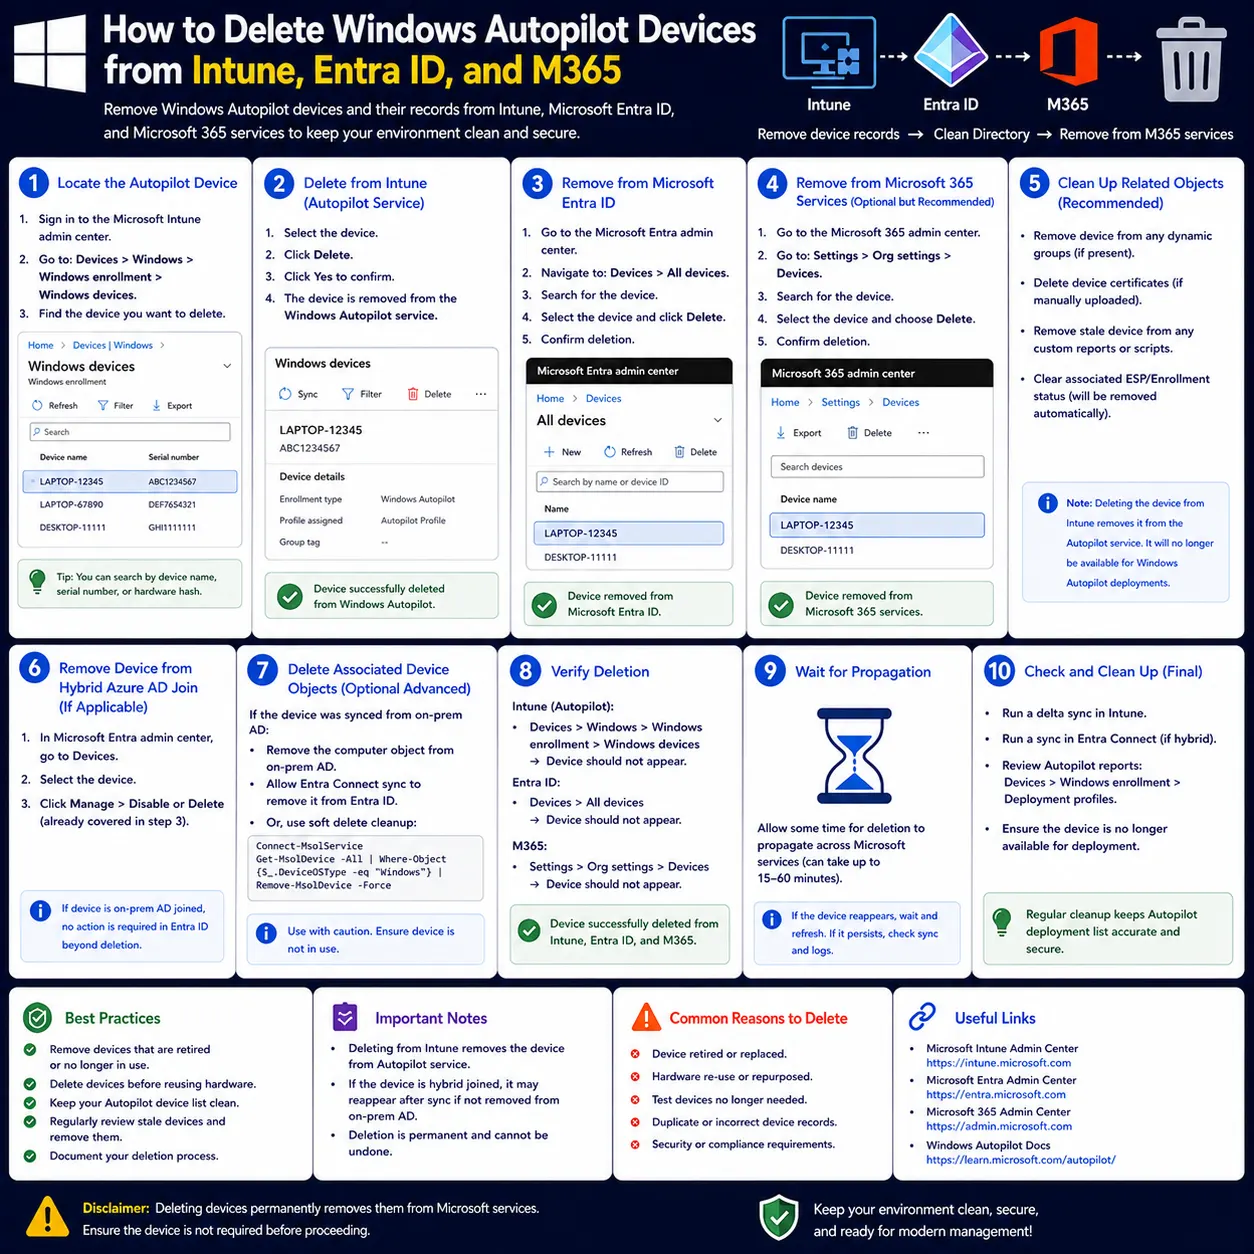
Table of contents
Quick Answer
Go to the stepsDelete the device from Intune Autopilot first, then from Intune managed devices, then from Entra ID - in that order, because the Autopilot registration blocks the Entra ID deletion. For hybrid Azure AD joined devices, also delete the computer object from on-premises Active Directory and force an Azure AD Connect delta sync so it does not reappear. Back up BitLocker recovery keys before you start.
- Back up the device's BitLocker recovery keys from Entra ID before deleting anything.
- In the Intune admin center, go to Devices → Enroll devices → Windows Autopilot devices, find the device, and Delete it.
- In Devices → All devices, select the device and Delete to retire and unenroll it (use Wipe if you will reprovision the same hardware).
- In the Entra admin center under Devices → All devices, Delete the device object; if Delete is greyed out, the Autopilot record still exists.
- For hybrid-joined devices, delete the computer object in on-premises AD and run Start-ADSyncSyncCycle -PolicyType Delta.
Microsoft Intune admin center → Devices → Enroll devices → Windows Autopilot devicesExpected result: The device no longer appears in Windows Autopilot devices, Intune All devices, or Entra ID All devices, and does not reappear after the next Azure AD Connect sync - freeing it for future enrollment with the same hardware.
Key takeaways
- You will learn how to completely remove a stale or decommissioned Windows Autopilot device from Microsoft Intune, Entra ID, and the associated on-premises Active Directory in the correct sequence. You will also learn how to back up BitLocker recovery keys first, clean up orphaned backend records with Graph Explorer, and bulk-delete devices with PowerShell.
- Device identities persist across Intune Autopilot, Intune managed devices, and Entra ID, and an out-of-order deletion leaves orphaned records that consume licensing, retain access, and block re-enrollment of reused hardware. Following the correct sequence ensures the device is fully removed and does not reappear.
- Always delete the Autopilot registration before the Entra ID object, because the Autopilot record blocks Entra ID deletion until it is removed.
Introduction
A single Windows device usually exists in three places at once: as an Autopilot device identity for zero-touch provisioning, as a managed device in Intune for policy enforcement, and as a device object in Entra ID (formerly Azure AD) for authentication and access. Deleting it cleanly means removing it from all three in the right order, because the Autopilot registration blocks deletion from Entra ID - try to delete the Entra object first and the Delete button is greyed out.
The correct sequence is Autopilot first, then Intune managed devices, then Entra ID. Hybrid Azure AD joined devices add a further complication: they sync from on-premises Active Directory, so unless you also delete the computer object on-prem and run an Azure AD Connect delta sync, the device simply reappears in Entra ID at the next sync cycle.
Because these deletions cannot be undone and may orphan BitLocker recovery keys stored in Entra ID, this guide starts with a backup step before any removal. It then covers per-device cleanup, orphaned-record removal via Graph Explorer, and a tested PowerShell approach for bulk deletions.
Who this is for: Sysadmins, MSP technicians, and IT pros who manage Windows device lifecycles in Microsoft Intune and Entra ID, including hybrid Azure AD joined environments.
Before you start
- Access
- You need administrative access to the Microsoft Intune admin center (https://endpoint.microsoft.com) and the Microsoft Entra admin center (https://entra.microsoft.com), plus permission to consent to Microsoft Graph scopes for the PowerShell and Graph Explorer steps. Hybrid-joined device cleanup additionally requires access to an on-premises domain controller and the Azure AD Connect sync server.
- Required roles
- Intune Administrator
- Cloud Device Administrator
- Global Administrator (for consenting to Graph scopes such as Device.ReadWrite.All and BitLockerKey.Read.All)
- On-premises Active Directory account with rights to delete computer objects (hybrid-joined devices only)
- Required licenses
- Microsoft Intune
- Microsoft Entra ID P1
- Vendor
- Microsoft
- Tested environment
- Microsoft Intune admin center, Microsoft Entra admin center, Microsoft Graph PowerShell SDK
- Administrator permissions required
- Backup required
Paths and cmdlets reference the Microsoft Intune admin center, the Microsoft Entra admin center, Microsoft Graph Explorer, and the Microsoft Graph PowerShell SDK modules.
Roughly 15-30 minutes per device; hybrid sync can add up to a full Azure AD Connect delta cycle (typically ~30 minutes) before the device disappears.
Critical: Back up BitLocker recovery keys before deleting anything
Deleting a device from Entra ID also removes the BitLocker recovery keys stored against that device object. Before you delete, export the recovery keys for each affected device (Entra device details or Get-MgInformationProtectionBitlockerRecoveryKey). If the disk is still encrypted and you lose the key, the data becomes unrecoverable.
Critical: Deletions cannot be undone
Removing a device from Autopilot, Intune, and Entra ID is permanent. Only delete devices that are genuinely decommissioned or replaced. If you intend to reuse the same hardware, use Wipe (Remove company data, do not keep enrollment state) instead of Delete so the Autopilot registration is preserved.
Warning: Test bulk PowerShell scripts on a small subset first
The bulk deletion loop removes devices across all three platforms with no confirmation prompts. Run it against two or three known-stale devices before processing a full device list, and confirm you have exported BitLocker keys and noted policy assignments for every device in scope.
Warning: Follow the deletion sequence
Delete the Autopilot registration first. An active Autopilot registration blocks the Entra ID device deletion (the Delete button will be greyed out), so removing devices out of order leaves orphaned records behind.
1Back up BitLocker keys and record dependencies
Preserve recovery data and note assignments before any deletion is performed.
Microsoft Entra admin center → Devices → All devices → [device] → BitLocker keysDeletions across Intune, Entra ID, and on-premises AD are effectively irreversible, and removing a device object can orphan its escrowed BitLocker recovery keys. Capture everything you might need before you delete anything.
- In the Microsoft Entra admin center (
https://entra.microsoft.com), go to Devices → All devices and open the device. - Review the device blade for the escrowed BitLocker keys and copy the recovery key values to your secured key vault or password manager.
- Note the device's Join type (Azure AD joined vs. Hybrid Azure AD joined) - you will need this in a later step.
- In the Intune admin center, check Devices → All devices → [device] → Device compliance and Device configuration to record any device-specific compliance or configuration assignments that should be cleaned up afterward.
Optionally, export BitLocker keys programmatically with the Graph PowerShell SDK (see the command block).
Connect-MgGraph -Scopes "BitLockerKey.Read.All", "Device.Read.All"
$device = Get-MgDevice -Filter "displayName eq 'DEVICE_NAME'"
$bitlockerKeys = Get-MgInformationProtectionBitlockerRecoveryKey -Filter "deviceId eq '$($device.DeviceId)'"
foreach ($key in $bitlockerKeys) {
    $keyDetails = Get-MgInformationProtectionBitlockerRecoveryKey -BitlockerRecoveryKeyId $key.Id
    Write-Host "Device: $($device.DisplayName)"
    Write-Host "Key ID: $($key.Id)"
    Write-Host "Recovery Key: $($keyDetails.Key)"
    Write-Host "Created: $($key.CreatedDateTime)"
    Write-Host "---"
}
Expected result: You have a saved copy of the device's BitLocker recovery key(s) and a written list of any device-specific compliance and configuration assignments.
Note
Replace DEVICE_NAME with the device's display name. Reading BitLocker keys requires the BitLockerKey.Read.All scope and an appropriately privileged admin role; the key value is only returned when you retrieve the individual key by ID, not in the list query. Treat exported recovery keys as sensitive secrets.
2Delete the device from the Intune Autopilot registry
Remove the Autopilot registration first so it no longer blocks the Entra ID deletion.
Microsoft Intune admin center → Devices → Enroll devices → Windows Autopilot devicesThe Autopilot registration must be removed before the Entra ID device object, because an active Autopilot record blocks (greys out) the Entra ID delete action.
- Sign in to the Microsoft Intune admin center at
https://intune.microsoft.com. - Go to Devices → Enroll devices → Windows Autopilot devices.
- Use the search bar to locate the device by serial number; you can also filter by device name if you know it.
- Select the device, click Delete, and confirm the prompt.
Warning: Deleting an Autopilot device removes its zero-touch provisioning capability. Only delete devices that are genuinely being decommissioned or replaced.
Connect-MgGraph -Scopes "DeviceManagementServiceConfig.ReadWrite.All"
Get-MgDeviceManagementWindowsAutopilotDeviceIdentity | Where-Object {$_.SerialNumber -eq "YOUR_SERIAL_NUMBER"}
Expected result: After a few minutes, searching the Windows Autopilot devices list for the serial number returns no matching device.
Note
Replace YOUR_SERIAL_NUMBER with the device's real serial number. Deletion can take several minutes to propagate - re-run the search to confirm rather than assuming it is instant. The PowerShell command shown here only finds the record; use Remove-MgDeviceManagementWindowsAutopilotDeviceIdentity (see the orphaned-records step) to delete it via script.
3Remove the device from Intune managed devices
Retire and unenroll the device so it leaves Intune management and the Company Portal.
Microsoft Intune admin center → Devices → All devices → [device] → DeleteNext, remove the device from Intune's managed device inventory if it still appears there.
- In the Intune admin center, go to Devices → All devices.
- Search for the device by name, user, or device ID.
- Select the device and click Delete. This issues a retire command, removes the device from the Company Portal, unenrolls it from Intune management, and removes company data according to your policies.
If you intend to reprovision the same hardware, do not use Delete here. Instead choose Wipe, then select Remove company data and Do not keep enrollment state to reset the device to OOBE while preserving the Autopilot registration - but note that path conflicts with the Autopilot deletion in the previous step, so decide up front whether the device is being decommissioned or reprovisioned.
Connect-MgGraph -Scopes "DeviceManagementManagedDevices.ReadWrite.All"
$devices = Get-MgDeviceManagementManagedDevice | Where-Object {$_.DeviceName -like "*PATTERN*"}
foreach ($device in $devices) {
    Remove-MgDeviceManagementManagedDevice -ManagedDeviceId $device.Id
    Write-Host "Deleted device: $($device.DeviceName)"
}
Expected result: The device disappears from the All devices list within roughly 5-10 minutes; before it clears it may briefly show a Pending retirement status.
Note
Replace *PATTERN* with a specific name filter and validate the matched set before deleting - a loose pattern can match far more devices than intended. Retirement is asynchronous, so allow time for the status to clear rather than deleting again.
4Delete the device from Microsoft Entra ID
Remove the device identity from Entra ID and revoke its access to organizational resources.
Microsoft Entra admin center → Devices → All devices → [device] → DeleteWith the Autopilot registration gone, you can now remove the Entra ID device object.
- Open the Microsoft Entra admin center at
https://entra.microsoft.com. - Go to Devices → All devices and search for the device by name, device ID, or another attribute.
- (Optional) Select the device and click Disable first to immediately block access while retaining the record - useful if you want to confirm nothing breaks before permanent removal.
- Click Delete and confirm.
If Delete is greyed out, the device still has an active Autopilot registration or is being synced from on-premises AD - return to the Autopilot step (or handle the hybrid case in the next step).
Connect-MgGraph -Scopes "Device.ReadWrite.All"
# Find device by display name
$device = Get-MgDevice -Filter "displayName eq 'DEVICE_NAME'"
# Or find by device ID
# $device = Get-MgDevice -Filter "deviceId eq 'DEVICE_ID'"
Remove-MgDevice -DeviceId $device.Id
Write-Host "Deleted device: $($device.DisplayName) from Entra ID"
Expected result: The device no longer appears in Entra ID; re-running Get-MgDevice -Filter "displayName eq 'DEVICE_NAME'" returns no results.
Note
Replace DEVICE_NAME (or DEVICE_ID) with the actual value. A greyed-out Delete almost always means the Autopilot record still exists or the object is AD-synced - deleting the Entra object alone will not stick for hybrid-joined devices.
5Handle hybrid-joined devices in on-premises AD
Prevent the device from reappearing in Entra ID after an Azure AD Connect sync.
On-premises: Active Directory Users and Computers → Computers (or device OU) → [computer] → DeleteHybrid Azure AD joined devices originate from on-premises Active Directory. If you only delete the Entra ID object, Azure AD Connect will re-synchronize the device and it will reappear. You must delete it at the source.
- Confirm the device shows Hybrid Azure AD joined in its Entra ID device details (recorded in step 1).
- On a domain controller, open Active Directory Users and Computers and navigate to the Computers container or the OU holding the device.
- Right-click the computer object and select Delete.
- Force an Azure AD Connect delta sync from the sync server, or wait for the next scheduled cycle (typically ~30 minutes).
# On a domain controller / with RSAT installed
Import-Module ActiveDirectory
$computer = Get-ADComputer -Filter "Name -eq 'DEVICE_NAME'"
Remove-ADComputer -Identity $computer.DistinguishedName -Confirm:$false
Write-Host "Deleted $($computer.Name) from on-premises AD"

# On the Azure AD Connect sync server, force a delta sync
Start-ADSyncSyncCycle -PolicyType Delta
Expected result: After the next Azure AD Connect sync completes, the device stays absent from Entra ID and does not re-appear in All devices.
Note
Replace DEVICE_NAME with the computer object name. Start-ADSyncSyncCycle runs on the server hosting Azure AD Connect, not a domain controller. You can confirm the sync in the Entra admin center under the Azure AD Connect / Connect Health area. Skip this step entirely for pure Azure AD joined devices - they have no on-premises object.
6Clean up orphaned Autopilot records with Graph Explorer
Remove backend Autopilot identities that persist but do not appear in the Intune console.
Graph Explorer (developer.microsoft.com/graph/graph-explorer) → signed in as adminOccasionally an Autopilot identity remains in the backend even though it no longer shows in Windows Autopilot devices. Use Graph Explorer or Graph PowerShell to find and remove it.
1. Open Graph Explorer at https://developer.microsoft.com/graph/graph-explorer and sign in with an admin account. 2. Get the device's Azure AD device ID: GET https://graph.microsoft.com/v1.0/devices?$filter=displayName eq 'DEVICE_NAME' 3. Copy the deviceId, then look up the matching Autopilot record: GET https://graph.microsoft.com/v1.0/deviceManagement/windowsAutopilotDeviceIdentities?$filter=azureActiveDirectoryDeviceId eq 'DEVICE_ID' 4. If a record is returned, note its id and serialNumber, then delete it: DELETE https://graph.microsoft.com/v1.0/deviceManagement/windowsAutopilotDeviceIdentities/AUTOPILOT_ID
The PowerShell equivalent is shown in the command block.
# Find Autopilot device by Azure AD device ID
$autopilotDevice = Get-MgDeviceManagementWindowsAutopilotDeviceIdentity -Filter "azureActiveDirectoryDeviceId eq 'DEVICE_ID'"
# Delete the Autopilot record
Remove-MgDeviceManagementWindowsAutopilotDeviceIdentity -WindowsAutopilotDeviceIdentityId $autopilotDevice.Id
Expected result: Re-running the windowsAutopilotDeviceIdentities filter query returns an empty result set, confirming the orphaned record is gone.
Note
Replace DEVICE_NAME, DEVICE_ID, and AUTOPILOT_ID with real values. Graph Explorer will prompt you to consent to the DeviceManagementServiceConfig.ReadWrite.All permission the first time you run a write/delete. A successful DELETE returns HTTP 204 No Content.
7Bulk delete multiple devices with PowerShell
Automate removal across Autopilot, Intune, and Entra ID for many stale devices at once.
For large cleanups, script the deletions across all three platforms.
1. Install the required Graph modules (once): - Install-Module Microsoft.Graph.Authentication -Scope CurrentUser - Install-Module Microsoft.Graph.DeviceManagement -Scope CurrentUser - Install-Module Microsoft.Graph.Identity.DirectoryManagement -Scope CurrentUser 2. Create devices.txt with one device name per line and save it (e.g. C:\temp\devices.txt). 3. Run the loop in the command block. It deletes each device from Autopilot, then Intune, then Entra ID, with a short delay for rate limiting.
Warning: Test on a small subset first. Bulk deletions cannot be undone, and you may permanently lose BitLocker recovery keys and device configuration - make sure step 1 (backup) is done for every device in the list.
Connect-MgGraph -Scopes "DeviceManagementManagedDevices.ReadWrite.All", "DeviceManagementServiceConfig.ReadWrite.All", "Device.ReadWrite.All"
$deviceNames = Get-Content "C:\temp\devices.txt"
foreach ($deviceName in $deviceNames) {
    Write-Host "Processing device: $deviceName" -ForegroundColor Yellow
    # 1) Autopilot
    $autopilotDevice = Get-MgDeviceManagementWindowsAutopilotDeviceIdentity | Where-Object {$_.DisplayName -eq $deviceName}
    if ($autopilotDevice) {
        Remove-MgDeviceManagementWindowsAutopilotDeviceIdentity -WindowsAutopilotDeviceIdentityId $autopilotDevice.Id
        Write-Host "  Deleted from Autopilot" -ForegroundColor Green
    }
    # 2) Intune managed devices
    $intuneDevice = Get-MgDeviceManagementManagedDevice | Where-Object {$_.DeviceName -eq $deviceName}
    if ($intuneDevice) {
        Remove-MgDeviceManagementManagedDevice -ManagedDeviceId $intuneDevice.Id
        Write-Host "  Deleted from Intune" -ForegroundColor Green
    }
    # 3) Entra ID
    $entraDevice = Get-MgDevice -Filter "displayName eq '$deviceName'"
    if ($entraDevice) {
        Remove-MgDevice -DeviceId $entraDevice.Id
        Write-Host "  Deleted from Entra ID" -ForegroundColor Green
    }
    Start-Sleep -Seconds 2
}
Expected result: The console logs Deleted from Autopilot/Intune/Entra ID per device, and spot-checking a few devices confirms they are gone from all three platforms.
Note
Ordering matters: Autopilot is deleted before Entra ID so the Entra deletion is not blocked. This script does not delete on-premises AD objects, so hybrid-joined devices in the list still require the AD step to avoid re-sync. To confirm afterward, run: Get-MgDeviceManagementWindowsAutopilotDeviceIdentity | Where-Object {$_.DisplayName -in $deviceNames} - it should return nothing.
Confirm the device is fully removed from all three platforms
Verify fix
A successful cleanup means the device no longer exists as an Autopilot identity, an Intune managed device, or an Entra ID device object - and, for hybrid-joined devices, does not reappear after the next Azure AD Connect sync. Because these platforms are interconnected, verifying only one of them is not enough: a device can vanish from the Intune console while an orphaned Autopilot record still lingers in the backend, or reappear in Entra ID after an AD Connect delta sync.
Check each platform independently after the deletions propagate. Propagation is not instant - allow roughly 5-10 minutes for Intune and Entra ID, and up to a full Azure AD Connect sync cycle (typically ~30 minutes, or immediately after Start-ADSyncSyncCycle -PolicyType Delta) for hybrid devices. Search by serial number, device name, and Azure AD device ID, and confirm each search returns no result. Re-running the Graph query for orphaned Autopilot identities is the most reliable final check, since it surfaces records that the Intune UI does not display.
If a device still appears somewhere, work backwards through the sequence: an Entra Delete that is greyed out or a device that keeps returning almost always points to a surviving Autopilot registration or an undeleted on-premises AD computer object.
Normal result: The device is absent from the Windows Autopilot devices list, from Intune All devices, and from Entra ID All devices. A Graph query for the Autopilot identity by azureActiveDirectoryDeviceId returns an empty result set, and for hybrid devices the object does not reappear after a completed delta sync. BitLocker recovery keys were exported before deletion.
Abnormal result: The device still appears in one or more platforms, the Entra ID Delete option is greyed out (indicating a surviving Autopilot registration), or a hybrid-joined device reappears in Entra ID after the AD Connect sync (indicating the on-premises computer object was not deleted). An orphaned Autopilot record may still return from the Graph query even when the Intune console shows nothing.
Autopilot record removed (Graph)
GET .../deviceManagement/windowsAutopilotDeviceIdentities?$filter=azureActiveDirectoryDeviceId eq '<DEVICE_ID>' → { "value": [] }
An empty value array confirms no backend Autopilot identity remains for that device ID.
Entra ID device removed (PowerShell)
Get-MgDevice -Filter "displayName eq 'FINANCE-LT-042'" → (no objects returned)
No returned object means the Entra ID device identity and its associated access were deleted.
Hybrid device did not re-sync
After Start-ADSyncSyncCycle -PolicyType Delta completes, FINANCE-LT-042 does not reappear in Entra ID All devices
Confirms the on-premises AD computer object was deleted so Azure AD Connect no longer recreates the record.
BitLocker key exported before deletion
Recovery Key: 123456-234567-345678-456789-567890-678901-789012-890123 (saved to secure store)
Evidence that recovery data was preserved before the Entra ID device object - and its keys - were removed.
Troubleshooting
The Delete option is greyed out for a device in Entra ID
Warning
Cause: The device still has an active Windows Autopilot registration, which blocks deletion of the corresponding Entra ID device object.
Return to the Intune admin center and delete the device from Devices → Enroll devices → Windows Autopilot devices first. Allow a few minutes for the deletion to propagate, then retry the Delete action in the Entra admin center. If the record still appears blocked, use Graph Explorer to check for an orphaned Autopilot identity by azureActiveDirectoryDeviceId and delete it there.
A hybrid Azure AD joined device keeps reappearing in Entra ID after deletion
Critical
Cause: The device is still synchronized from on-premises Active Directory, so Azure AD Connect re-creates the Entra ID object on the next sync cycle.
Delete the computer object from on-premises Active Directory (via Active Directory Users and Computers or Remove-ADComputer), then force a sync from the Azure AD Connect server with Start-ADSyncSyncCycle -PolicyType Delta. Verify the device does not return in Entra ID after the sync completes.
An Autopilot device does not appear in the Intune console but still blocks re-enrollment
Warning
Cause: The Autopilot identity persists as an orphaned backend record that is not surfaced in the Windows Autopilot devices list.
Open Graph Explorer, query deviceManagement/windowsAutopilotDeviceIdentities?$filter=azureActiveDirectoryDeviceId eq 'DEVICE_ID' to locate the record, then issue a DELETE against windowsAutopilotDeviceIdentities/{id}. Re-run the query to confirm it returns an empty result set.
BitLocker recovery keys are lost after deleting a device
Critical
Cause: BitLocker recovery keys stored against the Entra ID device object are removed when the device identity is deleted, and deletions cannot be undone.
Before deleting anything, export the recovery keys with Get-MgInformationProtectionBitlockerRecoveryKey (requires the BitLockerKey.Read.All scope) or record them from the device details in Entra ID. Store the exported keys in a secure location such as a password vault.
Bulk PowerShell deletion removes more devices than intended
Critical
Cause: Broad name matching or an unfiltered device list caused the script loop to delete devices that were not meant to be removed, and bulk deletions cannot be easily reversed.
Test the script on a small subset of devices first and use exact-match filters rather than wildcards. Confirm the contents of devices.txt before running, and keep the Start-Sleep rate limiting in place to avoid throttling and mis-processing.
Frequently asked questions
Why is the Delete option greyed out for my device in Entra ID?
The device most likely still has an active Windows Autopilot registration, which blocks deletion of its Entra ID object. Delete the device from the Windows Autopilot devices list in Intune first, wait for the change to propagate, then retry the deletion in the Entra admin center.
In what order should I delete a device from Autopilot, Intune, and Entra ID?
Delete from the Intune Autopilot registry first, then remove it from Intune managed devices, and finally delete it from Entra ID. This sequence matters because the Autopilot registration blocks the Entra ID deletion until it is removed.
Why does my hybrid Azure AD joined device keep reappearing after deletion?
Hybrid Azure AD joined devices sync from on-premises Active Directory, so Azure AD Connect re-creates the Entra ID object unless the source is removed. Delete the computer object from on-premises AD and force a delta sync with Start-ADSyncSyncCycle -PolicyType Delta to stop it reappearing.
Should I use Wipe or Delete if I want to reprovision the same hardware?
Use Wipe instead of Delete when you plan to reprovision the same device. In Intune, select Wipe, check Remove company data and Do not keep enrollment state to reset to OOBE while preserving the Autopilot registration.
How do I find and remove orphaned Autopilot records that don't show in Intune?
Use Graph Explorer or Graph PowerShell to query windowsAutopilotDeviceIdentities filtered by azureActiveDirectoryDeviceId, then DELETE the record by its id. This removes backend Autopilot identities that persist even though they no longer appear in the Intune console.
Will deleting a device also remove its BitLocker recovery keys?
Yes, BitLocker recovery keys are stored against the Entra ID device object and are removed when you delete the device identity. Export the keys with Get-MgInformationProtectionBitlockerRecoveryKey or record them from the device details before deleting anything, since the action cannot be undone.
Conclusion
Removing a stale Windows device cleanly means deleting it from every Microsoft platform in the correct order: back up BitLocker keys first, delete the Autopilot registration, retire it from Intune managed devices, then delete the Entra ID identity. Hybrid-joined devices also require deleting the on-premises Active Directory object and forcing an Azure AD Connect sync, while orphaned backend records can be cleared through Graph Explorer. Following this sequence prevents devices from reappearing or blocking future enrollments.
Always delete the Autopilot registration before the Entra ID object, because the Autopilot record blocks Entra ID deletion until it is removed.
Microsoft Intune admin center → Devices → Enroll devices → Windows Autopilot devices