How to Deploy FortiClient VPN with Configuration Using Microsoft Intune
Deploy and pre-configure FortiClient VPN to Windows devices with Microsoft Intune using MSI extraction, a Line-of-Business app, and a PowerShell registry script - no Fortinet EMS Premium required.

- Difficulty
- Advanced
- Time required
- 60-90 minutes
- Steps
- 6
- Platform
- Microsoft Intune
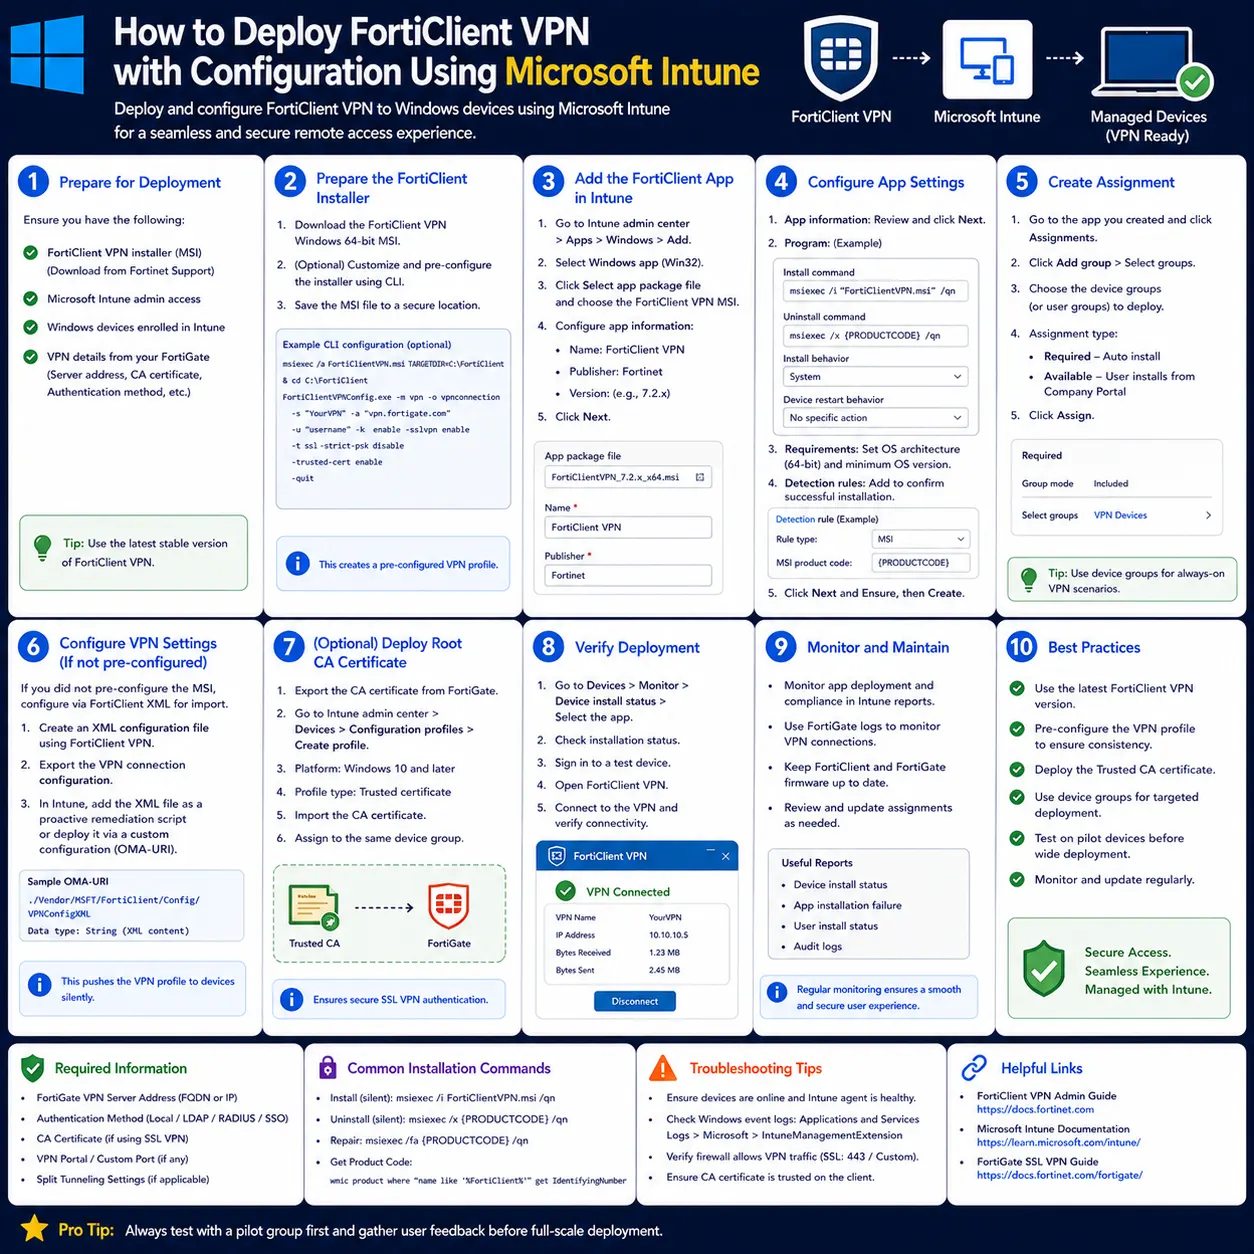
Table of contents
Quick Answer
Go to the stepsExtract the FortiClient VPN MSI from the online installer's cache, upload it to Intune as a Windows Line-of-Business app, then push a PowerShell script (run in system context) that writes the VPN tunnel settings to HKLM\SOFTWARE\Fortinet\FortiClient\Sslvpn\Tunnels. Sequence the app before the script and monitor status in Intune. No Fortinet EMS Premium is required.
- Run the FortiClient VPN online installer to the welcome screen and copy the cached MSI from C:\ProgramData\Applications\Cache\ to a safe folder.
- In Intune, add a Windows Line-of-business app, upload the MSI, set /quiet /norestart and System install behavior, and assign to a pilot group.
- On a test device, configure the VPN manually and export HKLM\SOFTWARE\Fortinet\FortiClient\Sslvpn\Tunnels to document the settings.
- Create Configure-FortiVPN.ps1 to write the tunnel registry values, then deploy it as an Intune platform script in system context and 64-bit host.
- Set app dependencies or a retry loop so the script runs after install, then monitor app and script status in Intune for Success.
Apps > All apps > Add > Line-of-business appExpected result: Target Windows devices install FortiClient VPN, the pre-configured VPN connection appears in the client, and Intune reports both the app and configuration script as Success.
Key takeaways
- You will learn how to extract the FortiClient VPN MSI from Fortinet's online installer, package it as a Line-of-Business app in Microsoft Intune, and use a PowerShell registry script to pre-configure the VPN tunnel automatically. You will also learn how to sequence the app and script so configuration runs only after installation completes.
- This approach delivers centralized, hands-off VPN deployment to hundreds or thousands of Windows devices without Fortinet EMS Premium licensing. It keeps VPN settings consistent across your fleet while reducing manual configuration and support overhead.
- You can deploy and pre-configure FortiClient VPN at scale through Intune by combining a Line-of-business MSI app with a system-context PowerShell registry script.
Introduction
Fortinet does not publish a direct MSI download for FortiClient VPN, and FortiClient settings cannot be delivered through Intune's native VPN profiles. That combination forces a two-part method: package the client as a Line-of-Business (LOB) app and apply the connection settings separately through a PowerShell script that writes to the registry. In this tutorial you extract the MSI from the FortiClient VPN online installer's cache at C:\ProgramData\Applications\Cache\, upload it as a Windows LOB app in the Intune admin center, and assign it to a pilot device group first. You then capture the tunnel registry structure under HKLM\SOFTWARE\Fortinet\FortiClient\Sslvpn\Tunnels, build Configure-FortiVPN.ps1 to recreate those values, and deploy it as a platform script running in system context so it has permission to modify HKLM. Finally, you set app dependencies or a retry loop so the script waits for FortiClient to install, then monitor app and script status in Intune to confirm each device reports Success. This eliminates the need for Fortinet EMS Premium while keeping full control over how the VPN is configured.
Who this is for: Sysadmins, MSPs, and IT pros who already manage Windows endpoints with Microsoft Intune and need to roll out a pre-configured FortiClient VPN client. Comfort with PowerShell and the Windows registry is expected.
Before you start
- Access
- You need administrative access to the Microsoft Intune admin center (https://intune.microsoft.com) with permission to add apps and platform scripts, plus a Windows test machine and a valid Fortinet support account to download the FortiClient VPN online installer.
- Required roles
- Intune Administrator (or a custom role with Managed apps and Device configuration/Scripts read-write rights)
- Local administrator on the test/staging Windows machine used for MSI extraction and manual VPN configuration
- Intune Administrator
- Required licenses
- Microsoft Intune (standalone or included with a Microsoft 365 E3/E5 or Enterprise Mobility + Security plan)
- Vendor
- Microsoft
- Administrator permissions required
Steps target Windows 10 (1607+) and Windows 11 devices managed by Microsoft Intune. Registry paths and installer cache locations reflect current FortiClient VPN behavior and should be verified against your specific client version.
Plan for 1-2 hours for a pilot deployment, plus additional monitoring time as the rollout expands.
Warning: The PowerShell script modifies HKLM and runs as SYSTEM
The configuration script writes to HKLM\SOFTWARE\Fortinet\FortiClient\Sslvpn\Tunnels and must run in system context, which has full local machine privileges. A malformed or malicious script deployed to system context can affect every targeted device. Review the script line by line, keep VPN values under version control, and validate it locally with PowerShell -ExecutionPolicy Bypass -File before uploading to Intune.
Warning: Pilot before enterprise-wide rollout
Assign both the FortiClient VPN app and the configuration script to a small pilot device group first. Overly restrictive OS or architecture requirements, or a script that runs before FortiClient finishes installing, can cause failed deployments or an unusable VPN client across your fleet.
Note: This method does not use Fortinet EMS
Because configuration is applied through registry keys rather than Fortinet's Enterprise Management Server, connections are not centrally managed by EMS and future FortiClient updates could change the registry schema. Re-verify the exported registry structure after major FortiClient version changes.
1Extract the FortiClient VPN MSI from the online installer
Obtain a deployable MSI that Intune can package for distribution.
Fortinet does not publish a direct MSI download, so you must extract the MSI that the online installer caches locally.
1. Download FortiClientVPNOnlineInstaller.exe from the Fortinet support portal (a valid support account is required). 2. Run the installer and let it reach the welcome screen, but do not click through to complete the installation. Reaching the welcome screen is enough to trigger the MSI download to the local cache. 3. Open File Explorer and browse to the cache directory: C:\ProgramData\Applications\Cache\ 4. Look for a folder with a GUID name that contains a version-numbered subfolder. Sort by Date modified to find the most recent extraction. 5. Copy the extracted FortiClientVPN.msi to a working folder such as C:\Temp. 6. Cancel the online installer once the MSI has been copied.
copy "C:\ProgramData\Applications\Cache\{GUID}\{VERSION}\FortiClientVPN.msi" "C:\Temp\FortiClientVPN.msi"Expected result: A FortiClientVPN.msi file (typically 50-100 MB) exists in C:\Temp, and its Properties dialog reports the file type as "Windows Installer Package".
Note
Replace {GUID} and {VERSION} with the actual folder names on your machine - they are unique per download and version. Right-click the MSI and choose Properties to confirm the file type and that the version matches the FortiClient build you expect. If C:\ProgramData is hidden, enable Hidden items in File Explorer's View tab.
2Create the FortiClient VPN Line-of-Business app in Intune
Package and assign the extracted MSI so Intune can deploy it to managed devices.
Apps > All apps > Add > Line-of-business appPackage the extracted MSI as a Line-of-business (LOB) app.
1. Sign in to the Microsoft Intune admin center at https://intune.microsoft.com. 2. Go to Apps > All apps > Add, and choose Line-of-business app as the app type, then select Windows as the platform. 3. Under App package file, upload the extracted FortiClientVPN.msi. 4. On the App information page, set: - Name: FortiClient VPN - Description: FortiClient VPN client for secure remote access - Publisher: Fortinet - Command-line arguments: /quiet /norestart - Install behavior: System 5. Detection is normally handled automatically from the MSI product code. If you prefer a custom check, verify the presence of FortiClient.exe. 6. Under Requirements, set Operating system architecture to x64 and Minimum operating system to Windows 10 1607. 7. On Assignments, target a small pilot device group first.
# Optional custom detection reference
$AppPath = "C:\Program Files\Fortinet\FortiClient\FortiClient.exe"
if (Test-Path $AppPath) {
    $Version = (Get-ItemProperty $AppPath).VersionInfo.FileVersion
    Write-Output "FortiClient version: $Version"
}
Expected result: The app appears in All apps with status "Ready to install" (or upload complete), and the Assignments tab shows your pilot group.
Note
Do not set overly restrictive requirements that could exclude valid devices. Always validate against a pilot group before an enterprise-wide rollout. LOB MSI apps use the MSI product code for detection by default, so a custom rule is optional.
3Capture VPN settings manually to build a script template
Understand the FortiClient registry structure so you can replicate it in a script.
Manually configure a VPN connection on a test device to learn the exact registry values your script must write.
1. Install FortiClient on a test machine (you can use the MSI from step 1) and create your VPN connection through the FortiClient UI. 2. Export the tunnel registry key so you can inspect the structure: reg export "HKLM\SOFTWARE\Fortinet\FortiClient\Sslvpn\Tunnels" C:\Temp\FortiVPN_Config.reg 3. Open FortiVPN_Config.reg in a text editor and note the values under your tunnel name, for example server, port, description, and auth_method. 4. Document each value you will replicate: - server - VPN server FQDN or IP - port - connection port (usually 443) - description - friendly connection name - auth_method - authentication method (for example sslvpn) - certificate - client certificate path if used 5. Connect to the VPN manually to confirm the configuration works before scripting it.
reg export "HKLM\SOFTWARE\Fortinet\FortiClient\Sslvpn\Tunnels" C:\Temp\FortiVPN_Config.regExpected result: An exported .reg file shows the tunnel key with server, port, description, and auth_method values, and a manual VPN connection authenticates and reaches internal resources.
Note
The exact set of values can vary by FortiClient version and authentication type (for example, certificate-based auth adds a certificate value). Capture from a device configured exactly as your production users will need.
4Create the PowerShell VPN configuration script
Automate registry configuration of the VPN tunnel after FortiClient is installed.
Write Configure-FortiVPN.ps1 to create the tunnel registry key and populate the values you documented.
1. Create the script and set variables ($VPNName, $VPNServer, $VPNPort, $Description, $AuthMethod) for your environment. 2. Have the script confirm FortiClient is installed before touching the registry, create the Tunnels path if missing, write each value, then verify the result. 3. Test locally before deploying: PowerShell -ExecutionPolicy Bypass -File Configure-FortiVPN.ps1 4. If your organization enforces signed scripts, code-sign the file so Intune's signature check can pass.
# Configure-FortiVPN.ps1
$VPNName    = "CompanyVPN"
$VPNServer  = "vpn.yourcompany.com"
$VPNPort    = "443"
$Description = "Company VPN Connection"
$AuthMethod = "sslvpn"

$RegPath = "HKLM:\SOFTWARE\Fortinet\FortiClient\Sslvpn\Tunnels\$VPNName"

try {
    $FortiClientPath = "C:\Program Files\Fortinet\FortiClient\FortiClient.exe"
    if (-not (Test-Path $FortiClientPath)) {
        Write-Error "FortiClient not found. Ensure application is installed first."
        exit 1
    }
    if (-not (Test-Path $RegPath)) { New-Item -Path $RegPath -Force | Out-Null }

    New-ItemProperty -Path $RegPath -Name "server"        -Value $VPNServer  -PropertyType String -Force
    New-ItemProperty -Path $RegPath -Name "port"          -Value $VPNPort    -PropertyType String -Force
    New-ItemProperty -Path $RegPath -Name "description"   -Value $Description -PropertyType String -Force
    New-ItemProperty -Path $RegPath -Name "auth_method"   -Value $AuthMethod -PropertyType String -Force
    New-ItemProperty -Path $RegPath -Name "save_password" -Value 0           -PropertyType DWord  -Force
    New-ItemProperty -Path $RegPath -Name "auto_connect"  -Value 0           -PropertyType DWord  -Force

    $ServerValue = Get-ItemProperty -Path $RegPath -Name "server" -ErrorAction SilentlyContinue
    if ($ServerValue.server -eq $VPNServer) { exit 0 } else { Write-Error "Verification failed"; exit 1 }
}
catch {
    Write-Error "Script execution failed: $($_.Exception.Message)"
    exit 1
}
Expected result: Running the script locally returns exit code 0 and creates the tunnel values under HKLM\SOFTWARE\Fortinet\FortiClient\Sslvpn\Tunnels\CompanyVPN.
Note
$VPNName, $VPNServer, $VPNPort, $Description, and $AuthMethod are placeholders - replace them with your documented values from step 3. Self-signed certificates (via New-SelfSignedCertificate + Set-AuthenticodeSignature) are only appropriate for testing; use a trusted code-signing certificate for production if signature enforcement is enabled.
5Deploy the PowerShell script through Intune
Push the VPN configuration to managed devices in system context.
Devices > Scripts and remediations > Platform scripts > Add > Windows 10 and laterDeploy the script with Intune's platform scripts feature so it runs on target devices after FortiClient is installed.
1. In the Intune admin center go to Devices > Scripts and remediations > Platform scripts > Add > Windows 10 and later. 2. Upload Configure-FortiVPN.ps1 and set: - Name: Configure FortiClient VPN - Description: Automatically configures company VPN settings in FortiClient 3. Configure the script settings: - Run this script using the logged on credentials: No - Enforce script signature check: Yes (only if you signed the script) - Run script in 64 bit PowerShell Host: Yes 4. On Assignments, target the same device group as the FortiClient app. 5. Optionally add a detection/verification script to confirm the tunnel values were written.
# Detection script
$RegPath = "HKLM:\SOFTWARE\Fortinet\FortiClient\Sslvpn\Tunnels\CompanyVPN"
if (Test-Path $RegPath) {
    $server = Get-ItemProperty -Path $RegPath -Name "server" -ErrorAction SilentlyContinue
    if ($server.server -eq "vpn.yourcompany.com") {
        Write-Output "VPN configured correctly"
        exit 0
    }
}
Write-Output "VPN not configured"
exit 1
Expected result: The platform script appears under Platform scripts, and target devices report "Success" in the script's Device status view.
Note
Running as system (logged-on credentials = No) is required because the script writes to HKLM, which a standard user context cannot modify. Platform scripts run once per device on assignment; they are not re-run on a schedule the way remediations are, so plan configuration changes accordingly.
6Configure deployment order and monitor rollout
Ensure FortiClient installs before the script runs, then confirm the deployment succeeded.
Apps > All apps > FortiClient VPN > Properties > DependenciesSequence the deployment so the script never runs before FortiClient exists, then monitor the results.
1. Open the FortiClient VPN app and review Properties > Dependencies > Add if you have prerequisite software to enforce ordering for the app itself. 2. Because platform scripts do not honor app dependencies, add a retry loop in the script so it waits for FortiClient before writing the registry (see command). 3. Monitor rollout: - In Apps, open the FortiClient VPN app and review Device install status for Installed/Failed counts. - In Devices > Scripts and remediations, open the script and review Device status for Success/Error results. 4. On a target device, open FortiClient and confirm the pre-configured VPN connection is listed and connects successfully.
$MaxRetries = 5
$RetryDelay = 30
$FortiClientPath = "C:\Program Files\Fortinet\FortiClient\FortiClient.exe"

for ($i = 1; $i -le $MaxRetries; $i++) {
    if (Test-Path $FortiClientPath) {
        Write-Output "FortiClient found, proceeding with configuration..."
        # Run your configuration code here
        break
    } else {
        Write-Output "Attempt $i: FortiClient not found, waiting $RetryDelay seconds..."
        if ($i -eq $MaxRetries) {
            Write-Error "FortiClient installation not detected after $MaxRetries attempts"
            exit 1
        }
        Start-Sleep -Seconds $RetryDelay
    }
}
Expected result: Intune shows the app Installed and the script Success on target devices, and FortiClient displays the pre-configured VPN connection ready to use.
Note
Intune app install and script execution timing is not tightly synchronized, so the retry loop is the reliable way to prevent race conditions rather than depending on assignment order. Allow time for the next device check-in before status refreshes in the console.
Confirming the Rollout: What Success Looks Like in Intune and on the Device
Monitor deployment
A successful deployment has two independent signals that must both line up: Intune reports the app and script as delivered, and FortiClient on the endpoint shows the pre-configured VPN tunnel. Do not treat the Intune app status alone as proof - the app installing the client does not mean the registry configuration was written.
In the Intune admin center, check the FortiClient VPN app under its Device install status - targeted devices should move from Pending to Installed. Then check the Configure FortiClient VPN platform script under Devices > Scripts and remediations > Platform scripts, where each device reports a per-device result. Because Intune platform scripts run roughly once per hour after enrollment and do not enforce app-then-script ordering by themselves, expect a lag between the app installing and the script succeeding - this is where your retry loop or dependency configuration matters.
Finally, verify on an actual endpoint: open FortiClient and confirm the named connection (for example CompanyVPN) appears in the tunnel list with the correct server and port, and that a user can authenticate and reach internal resources. The registry key HKLM\SOFTWARE\Fortinet\FortiClient\Sslvpn\Tunnels\<VPNName> is the ground truth for whether the script applied.
Normal result: In Intune, the FortiClient VPN app shows Installed and the platform script shows a Success result for pilot devices within one to two script cycles. On the endpoint, the configured VPN connection is visible in FortiClient with the correct server FQDN and port 443, the Tunnels registry key exists with your values, and a test user can connect and reach internal resources.
Abnormal result: The app shows Installed but the script reports Failed or the VPN connection never appears in FortiClient - usually because the script ran before FortiClient finished installing (Test-Path on FortiClient.exe returned false), ran in logged-on-user context instead of system (no permission to write HKLM), or ran in the 32-bit host and hit registry redirection. A script status of Not applicable or Pending across all devices means the assignment or platform filter is wrong. If the registry key exists but connections still fail, revisit the exported values (server, port, auth_method) from the manual capture step.
Intune app install status (healthy pilot)
FortiClient VPN - Installed: 12 / Pending: 0 / Failed: 0 / Not installed: 0
Under the app's Device install status blade; all pilot devices received the MSI.
Intune platform script result
Configure FortiClient VPN - Success: 12 / Error: 0 / Pending: 0
Under Devices > Scripts and remediations; a per-device Success means the registry write and verification block completed with exit code 0.
Detection script output on a configured device
VPN configured correctly
Written by the detection script when HKLM\...\Sslvpn\Tunnels\CompanyVPN\server equals your VPN server FQDN; exit code 0.
Confirmed registry tunnel entry
HKLM\SOFTWARE\Fortinet\FortiClient\Sslvpn\Tunnels\CompanyVPN server=vpn.yourcompany.com port=443 auth_method=sslvpn
The registry values the PowerShell script created; this is the authoritative confirmation the configuration applied.
Troubleshooting
The extracted MSI is missing from the cache directory after running the online installer.
Warning
Cause: The online installer only downloads the MSI to C:\ProgramData\Applications\Cache once it reaches the welcome screen; closing it too early or an interrupted download leaves no package to copy.
Re-run FortiClientVPNOnlineInstaller.exe and leave it open at the welcome screen. Sort the subfolders under C:\ProgramData\Applications\Cache\ by date modified and open the newest GUID/version folder to find FortiClientVPN.msi. Copy it out before cancelling, then confirm the file properties show a Windows Installer Package.
The PowerShell configuration script fails with an access-denied or permission error when writing to the registry.
Critical
Cause: The script is running in the logged-on user context, which lacks write permission to HKLM\SOFTWARE\Fortinet.
In the Intune platform script settings, set Run this script using the logged on credentials to No so it executes in system context, and set Run script in 64 bit PowerShell Host to Yes. System context has the rights needed to modify keys under HKLM.
The configuration script runs but the VPN tunnel does not appear in FortiClient.
Warning
Cause: The script executed before FortiClient finished installing, so the Tunnels registry structure or client was not yet present.
Add an app dependency on the FortiClient VPN LOB app, or use the retry loop that checks for C:\Program Files\Fortinet\FortiClient\FortiClient.exe before applying configuration. Wait for the app to report installed, then let the script re-run on its next cycle.
Intune reports the script as failed because of a signature check.
Warning
Cause: Enforce script signature check is enabled, but the uploaded script is unsigned or signed with a certificate not trusted by target devices.
Either disable Enforce script signature check for an unsigned script, or sign the script with a code-signing certificate whose issuing authority is trusted on the endpoints. A self-signed certificate created with New-SelfSignedCertificate is only suitable for local testing, not production enforcement.
The detection rule always reports the app as not installed even though FortiClient is present.
Note
Cause: A custom detection path or MSI product code mismatch - for example the FortiClient binary path or version differs from what the rule expects.
Prefer the auto-detected MSI product code for detection. If using a custom rule, confirm C:\Program Files\Fortinet\FortiClient\FortiClient.exe exists on a test device and matches the expected version before relying on it in Intune.
Frequently asked questions
Why doesn't Fortinet provide a direct MSI download for FortiClient VPN?
Fortinet distributes FortiClient VPN through an online installer that downloads the MSI to a temporary cache rather than offering the MSI directly. To package it for Intune you run the installer to the welcome screen and copy the extracted MSI from C:\ProgramData\Applications\Cache\.
Can I deploy FortiClient VPN through Intune without Fortinet EMS Premium?
Yes. This method packages the extracted MSI as a Line-of-business app and pushes VPN settings with a PowerShell registry script, so you get centralized deployment and pre-configuration without the Fortinet Enterprise Management Server (EMS) Premium features.
Why must the PowerShell configuration script run in system context?
The VPN settings are written under HKLM\SOFTWARE\Fortinet\FortiClient\Sslvpn\Tunnels, and only the system account has write permission to that hive. Running the script as the logged-on user results in access-denied errors, so set 'Run this script using the logged on credentials' to No.
How do I ensure FortiClient installs before the configuration script runs?
Set an app dependency on the FortiClient VPN LOB app, or build a retry loop into the script that checks for C:\Program Files\Fortinet\FortiClient\FortiClient.exe and waits before applying configuration. This prevents the script from failing when the client isn't installed yet.
Which registry path stores FortiClient SSL VPN tunnel settings?
SSL VPN tunnel configurations are stored under HKLM\SOFTWARE\Fortinet\FortiClient\Sslvpn\Tunnels, with a subkey named for each tunnel holding values such as server, port, description, and auth_method.
How can I verify the FortiClient VPN deployment succeeded on target devices?
Monitor the app and script status in Intune and confirm devices report 'Success', then check that the tunnel exists under the Tunnels registry key using a detection script. Finally, open FortiClient on a target device to confirm the pre-configured VPN connection appears and connects.
Conclusion
You extracted the FortiClient VPN MSI from Fortinet's online installer, packaged it as a Line-of-business app in Microsoft Intune, and built a PowerShell script that writes the SSL VPN tunnel settings to the registry. By running that script in system context and sequencing it after the app install, you achieved automated, pre-configured VPN deployment across managed Windows devices without Fortinet EMS Premium.
You can deploy and pre-configure FortiClient VPN at scale through Intune by combining a Line-of-business MSI app with a system-context PowerShell registry script.
Apps > All apps > Add > Line-of-business app