How to Enable Core Isolation Memory Integrity in Windows 11
Learn how to enable Memory Integrity (HVCI) in Windows 11 via Windows Security, Group Policy, Registry, or Intune. Includes troubleshooting for incompatible drivers and BIOS virtualization requirements.

- Difficulty
- Beginner
- Time required
- 5 minutes
- Steps
- 4
- Platform
- Windows 11
- Last tested
- July 19, 2026
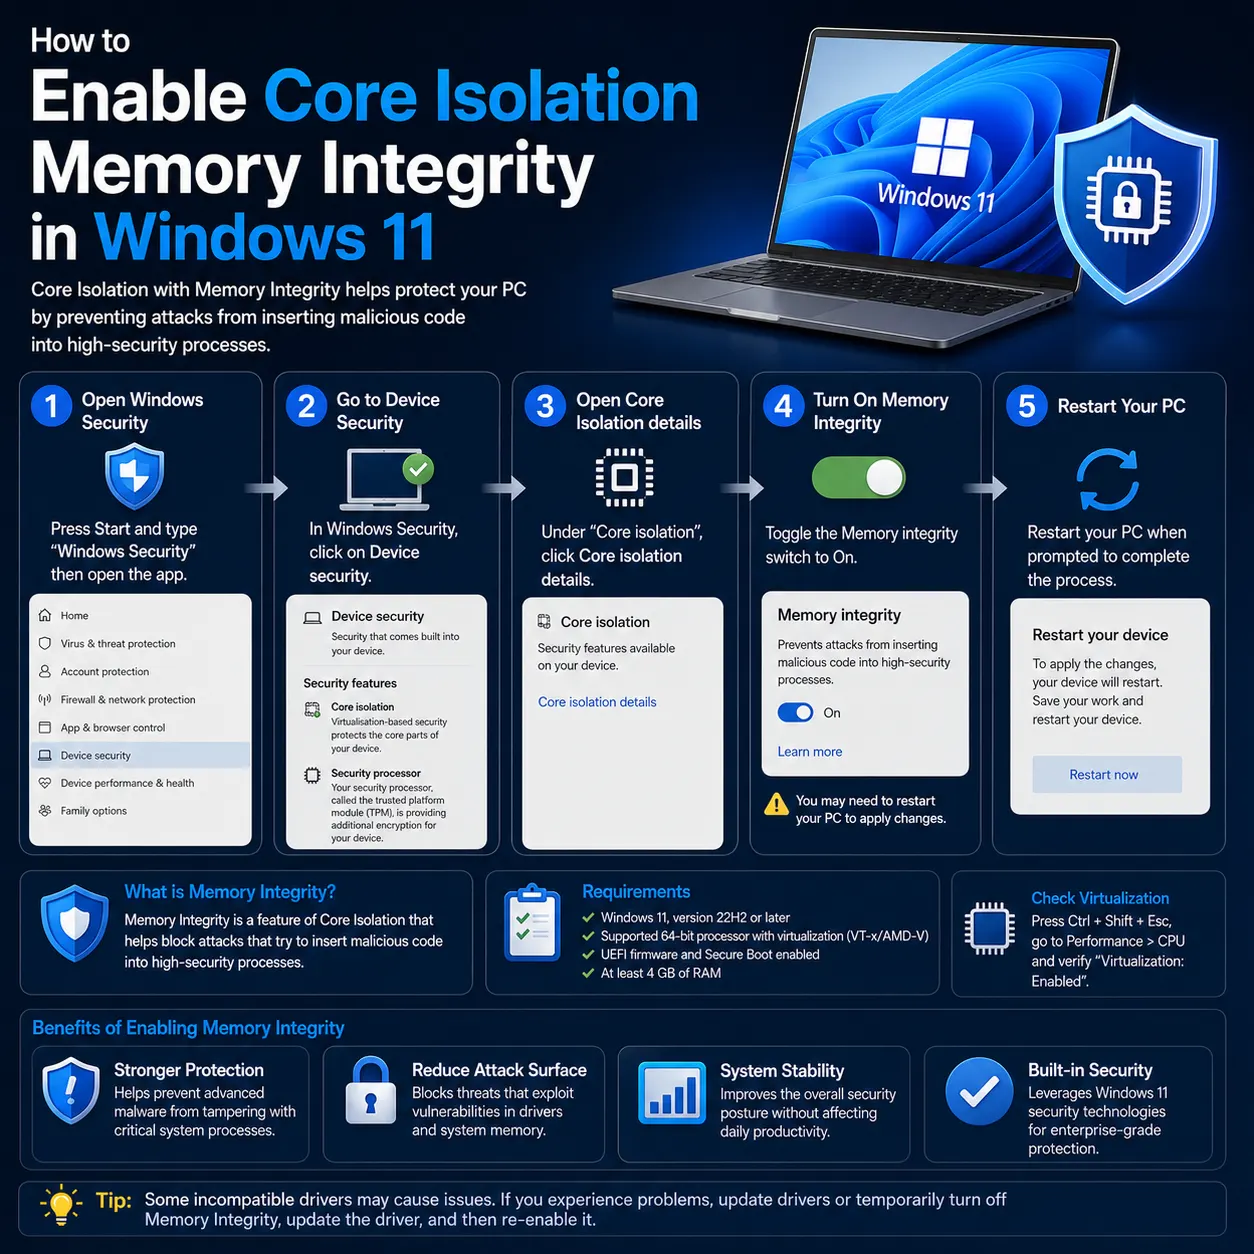
Table of contents
Quick Answer
Go to the stepsOpen Windows Security, go to Device Security, click Core isolation details, and toggle Memory Integrity to On. You need hardware virtualization (Intel VT-x or AMD-V) enabled in BIOS/UEFI. If the toggle fails, check for incompatible drivers.
- Open Windows Security from the Start menu or Settings > Privacy & security.
- Click Device security in the left sidebar.
- Click Core isolation details.
- Toggle Memory integrity to On.
- Restart your computer to apply the change.
Windows Security > Device security > Core isolation details > Memory integrityExpected result: Memory Integrity toggle shows On. After reboot, msinfo32 shows 'Hypervisor enforced Code Integrity' under VBS Services Running.
Key takeaways
- You'll learn how to enable Memory Integrity (also called Hypervisor-protected Code Integrity or HVCI) in Windows 11 using four methods: Windows Security, Group Policy, Registry, and Intune.
- Memory Integrity uses the Windows hypervisor to create an isolated virtual environment that protects the kernel from malware. Per Microsoft Learn, it prevents attackers from injecting malicious code into high-security processes.
- Enable Memory Integrity in Windows Security > Device security > Core isolation details and verify with msinfo32 after restart.
Introduction
Memory Integrity is a Virtualization-based Security (VBS) feature that isolates the code integrity verification process from the Windows kernel. Per Microsoft Learn, it uses the hypervisor to create a protected environment where only verified code can run in kernel mode.
Since Windows 11 22H2, Windows Security shows a warning if Memory Integrity is turned off. The warning appears in the system tray and Windows Notification Center. You can enable it through the Windows Security app, Group Policy, the Registry, or Intune for managed devices.
Some hardware drivers are incompatible with Memory Integrity. In rare cases, enabling it can cause a boot failure (blue screen). This tutorial covers all four methods and explains how to troubleshoot incompatible drivers.
Who this is for: IT admins, security teams, and home users who want to harden their Windows 11 devices against kernel-level attacks.
Before you start
- Access
- Local administrator access to the Windows 11 device. For Intune deployment, Intune Administrator or Endpoint Security Manager role.
- Required roles
- Local administrator
- Environment
- Windows 11 (any edition). Hardware virtualization (Intel VT-x / AMD-V) must be enabled in BIOS/UEFI. UEFI boot mode with Secure Boot enabled.
- Vendor
- Microsoft
- Tested environment
- Tested on Windows 11 24H2, July 2026.
- Last tested
- Administrator permissions required
Tested on Windows 11 24H2, July 2026.
5 minutes
Warning: Incompatible drivers may cause issues
Some third-party drivers are incompatible with Memory Integrity. Per Microsoft Learn, this can cause devices or software to malfunction and in rare cases may result in a blue screen. Review the incompatible drivers list before enabling.
Note: Verify virtualization in BIOS first
If virtualization is not enabled in BIOS/UEFI, the Memory Integrity option won't appear in Windows Security. Enable Intel VT-x (Intel) or SVM (AMD) in your BIOS before proceeding.
1Open Windows Security Device Security
Navigate to the Core Isolation settings in Windows Security.
Settings > Privacy & security > Windows Security > Device securityOpen Settings by pressing Win + I. Go to Privacy & security in the left sidebar. Click Windows Security, then click Open Windows Security. In the Windows Security app, click Device security in the left sidebar.
Expected result: The Device security page opens showing Core isolation and other security features.
Note
You can also search for 'Windows Security' in the Start menu to open it directly.
2Enable Memory Integrity in Core Isolation
Turn on Memory Integrity (HVCI) from the Core isolation settings.
Windows Security > Device security > Core isolation details > Memory integrityClick Core isolation details under the Core isolation section. Find the Memory integrity toggle and switch it to On. When prompted by UAC, click Yes to confirm. If the toggle fails, click Review incompatible drivers to see which drivers are blocking the feature.
Expected result: The Memory integrity toggle turns On. A message appears asking you to restart.
Note
If you see 'Resolve any driver incompatibilities, and try again,' you need to update or uninstall the incompatible drivers before Memory Integrity can be enabled. See the Troubleshooting section.
3Restart Your Computer
Apply the Memory Integrity setting by restarting Windows.
Click Restart when prompted, or restart your computer manually from the Start menu. Memory Integrity activates during the boot process.
Expected result: Windows restarts normally. After login, Memory Integrity shows as On in Core isolation details.
Note
If Windows fails to boot (blue screen), restart in Safe Mode and disable Memory Integrity via Registry: set Enabled to 0 at HKLM\SYSTEM\CurrentControlSet\Control\DeviceGuard\Scenarios\HypervisorEnforcedCodeIntegrity.
4Verify Memory Integrity is Active
Confirm that HVCI is running using System Information.
Press Win + R, type msinfo32, and press Enter. In System Information, scroll to Virtualization-based security section. Check Virtualization-based security Services Running for Hypervisor enforced Code Integrity.
msinfo32Expected result: System Information shows 'Hypervisor enforced Code Integrity' under VBS Services Running.
Note
If VBS shows as 'Not enabled', check that hardware virtualization is enabled in BIOS/UEFI and that Secure Boot is active.
Verify Memory Integrity Is Protecting Your Device
Confirm configuration
After enabling Memory Integrity and restarting, your device uses the hypervisor to isolate code integrity verification from the rest of the kernel. Per Microsoft Learn, this prevents attackers from injecting malicious code into high-security processes even if they compromise the kernel.
You can verify the status in two places: the Windows Security app (Device security > Core isolation details) shows Memory Integrity as On, and System Information (msinfo32) lists 'Hypervisor enforced Code Integrity' under VBS Services Running.
If the toggle shows Off after restart, an incompatible driver may have reverted the change. Check the Windows Event Log for DeviceGuard events.
Normal result: Memory Integrity toggle shows On. msinfo32 lists 'Hypervisor enforced Code Integrity' under VBS Services Running.
Abnormal result: Memory Integrity reverts to Off after restart, or Windows blue-screens during boot. This indicates an incompatible driver.
Healthy VBS status
VBS Services Running: Hypervisor enforced Code Integrity
Memory Integrity is active and protecting the kernel.
VBS not running
Virtualization-based security: Not enabled
Hardware virtualization may be disabled in BIOS/UEFI.
Troubleshooting
Memory Integrity toggle fails with 'Resolve any driver incompatibilities'
Warning
Cause: One or more installed drivers are not compatible with HVCI. Windows lists them when you click 'Review incompatible drivers.'
Click Review incompatible drivers to identify the blocking drivers. Open Device Manager, right-click the flagged driver, and select Update driver. If no update is available, check the hardware vendor's website. As a last resort, uninstall the incompatible driver if the hardware isn't critical.
Memory Integrity option is missing from Core isolation
Warning
Cause: Hardware virtualization (Intel VT-x / AMD SVM) is not enabled in BIOS/UEFI, or the device firmware doesn't support VBS.
Restart into BIOS/UEFI and enable Intel VT-x (Intel) or SVM/Secure Virtual Machine (AMD). The setting is typically under CPU Configuration, Advanced, or OC settings depending on the motherboard manufacturer. After enabling, restart and check Core isolation again.
Blue screen (BSOD) after enabling Memory Integrity
Critical
Cause: An incompatible kernel driver loaded during boot caused a system crash.
Boot into Safe Mode (hold Shift while clicking Restart, or interrupt boot 3 times). Open Registry Editor and navigate to HKLM\SYSTEM\CurrentControlSet\Control\DeviceGuard\Scenarios\HypervisorEnforcedCodeIntegrity. Set Enabled to 0. Restart normally and identify the incompatible driver before trying again.
Toggle shows 'This setting is managed by your administrator'
Note
Cause: Group Policy or Intune has configured Memory Integrity centrally. The local toggle is greyed out.
Contact your IT administrator. The setting is controlled via Group Policy (Computer Configuration > Administrative Templates > System > Device Guard) or Intune Settings Catalog (VirtualizationBasedTechnology CSP). Local users cannot override centrally managed settings.
Frequently asked questions
What is Memory Integrity in Windows 11?
Memory Integrity, also called Hypervisor-protected Code Integrity (HVCI), is a VBS feature that isolates the code integrity verification process from the Windows kernel. Per Microsoft Learn, it prevents malware from injecting code into high-security kernel processes.
Does Memory Integrity slow down my computer?
There is a small performance impact because Memory Integrity uses the hypervisor to isolate code verification. Most users won't notice the difference on modern hardware. Gaming performance may be slightly reduced in some titles.
Is Memory Integrity enabled by default in Windows 11?
Per Microsoft Q&A, Memory Integrity is disabled by default on most installations and must be enabled manually. Since Windows 11 22H2, Windows Security shows a warning if it's turned off.
Can I enable Memory Integrity via Group Policy?
Yes. Open gpedit.msc, navigate to Computer Configuration > Administrative Templates > System > Device Guard, and configure the 'Turn On Virtualization Based Security' policy with HVCI enabled.
What happens if I have incompatible drivers?
Windows will show a list of incompatible drivers and prevent Memory Integrity from turning on. You need to update or uninstall the incompatible drivers. In rare cases, enabling it with incompatible drivers can cause a blue screen.
Conclusion
Memory Integrity (HVCI) is a key Windows 11 security feature that isolates code integrity from the kernel using the hypervisor. You can enable it through Windows Security (Device security > Core isolation details), Group Policy, Registry, or Intune. Per Microsoft Learn, incompatible drivers are the most common blocker.
After enabling and restarting, verify the status using msinfo32 (look for 'Hypervisor enforced Code Integrity' under VBS Services Running). If Windows blue-screens, boot into Safe Mode and disable via the Registry.
Enable Memory Integrity in Windows Security > Device security > Core isolation details and verify with msinfo32 after restart.
Windows Security > Device security > Core isolation details > Memory integrity