How to Configure App Inventory for Windows Devices in Microsoft Intune
Learn how to configure Microsoft Intune's App Inventory feature using the Properties Catalog to collect application data from Windows devices, including install dates, versions, and publishers.

- Difficulty
- Intermediate
- Time required
- 10-15 minutes
- Steps
- 3
- Platform
- Intune
- Last tested
- July 18, 2026
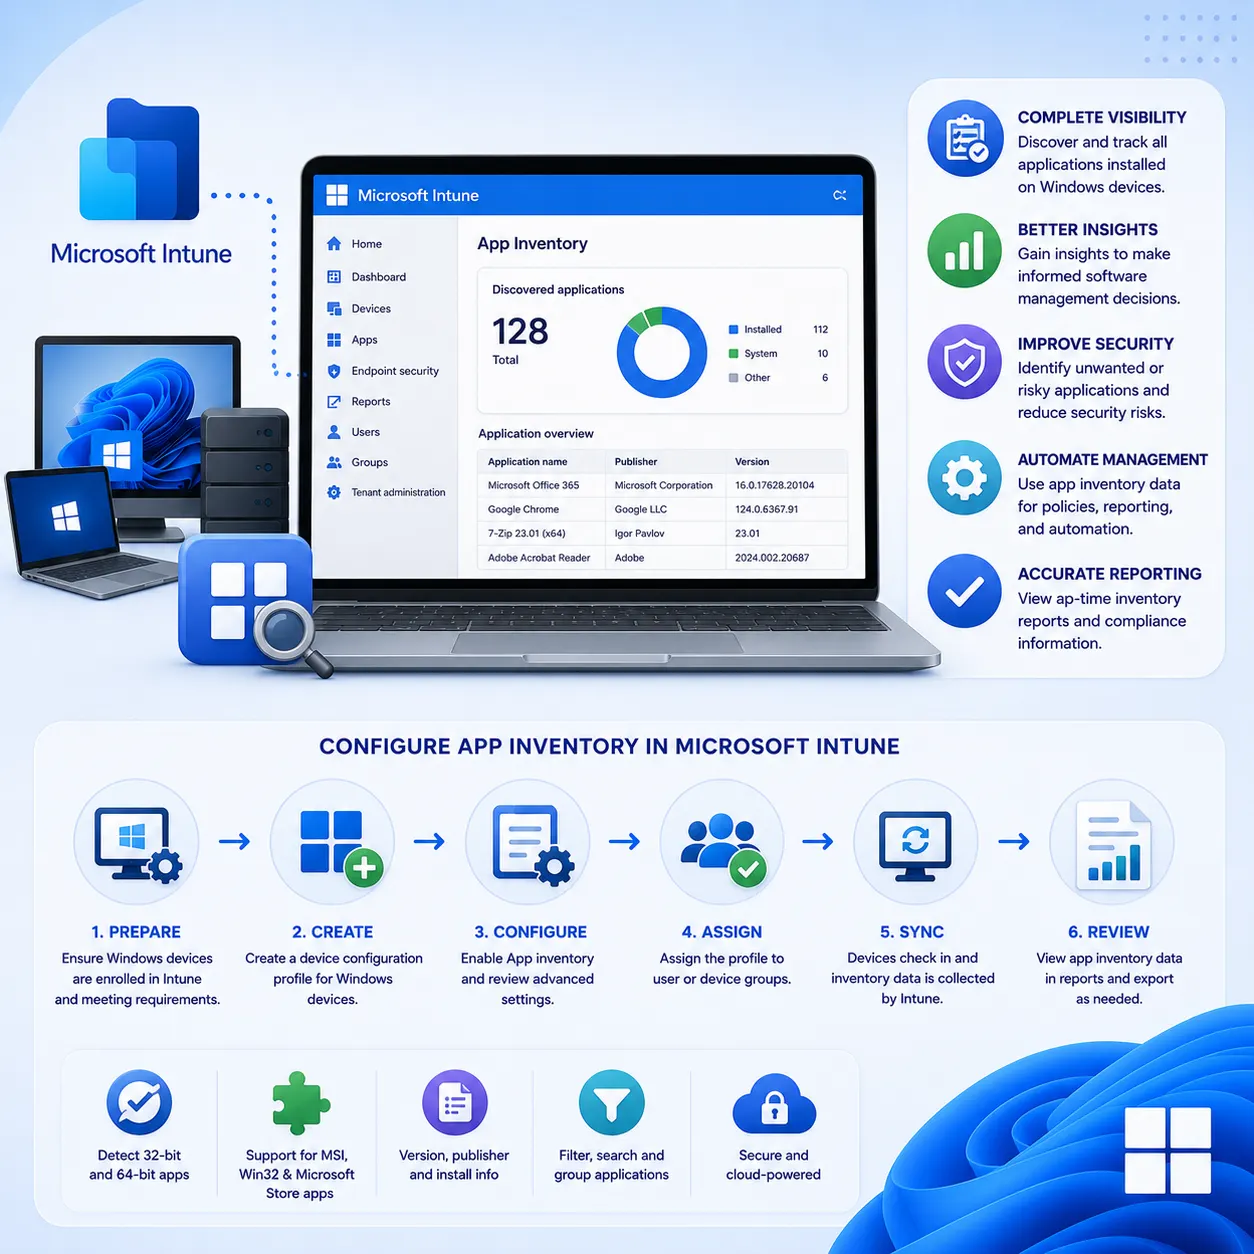
Table of contents
Quick Answer
Go to the stepsCreate a Properties Catalog configuration policy in Intune, enable ApplicationProperties, and assign it to your Windows device groups. Data appears within 24 hours.
- Sign in to intune.microsoft.com.
- Go to Devices > Manage devices > Configuration.
- Click Create > New Policy.
- Select Windows 10 and later, then Properties Catalog.
- Add ApplicationProperties and select desired properties.
- Assign to device groups and create the policy.
Devices > Manage devices > Configuration > Create > New Policy > Properties CatalogExpected result: Intune collects app data from target devices, visible under Devices > All devices > select device > All Apps > App Inventory tab.
Key takeaways
- How to create and deploy a Properties Catalog policy in Intune to collect detailed application inventory data from Windows devices.
- Full visibility into all installed applications is essential for compliance audits, shadow IT detection, vulnerability management, and software license tracking.
- The Properties Catalog gives you complete application visibility across all managed Windows devices with minimal ongoing effort.
Introduction
Microsoft Intune's Properties Catalog lets you collect detailed application inventory data from managed Windows devices. Unlike basic discovered apps lists, this feature gathers structured information about both Win32 applications (from registry uninstall keys) and modern Store apps (via Package Manager API). The Device Inventory Agent handles all collection automatically after you deploy the policy, using delta synchronization to minimize bandwidth after the first full upload.
Who this is for: IT administrators, MSPs, and endpoint management professionals managing Windows devices through Microsoft Intune.
Before you start
- Access
- Microsoft Intune admin center (intune.microsoft.com)
- Required roles
- Intune Administrator
- Global Administrator
- Required licenses
- Microsoft Intune Plan 1 or higher
- Environment
- Intune tenant with Windows 10/11 devices enrolled via Entra ID join or Hybrid join
- Vendor
- Microsoft
- Last tested
- Administrator permissions required
10-15 minutes
Note: Agent installs automatically
This deploys the Device Inventory Agent silently to target devices and begins collecting application data.
Warning: Pilot first
Start with a pilot group of 10-20 devices before deploying tenant-wide.
1Create a Properties Catalog policy in Intune
Create a new Properties Catalog policy for app inventory collection.
Devices > Manage devices > Configuration > Create > New PolicySign in to the Intune admin center at https://intune.microsoft.com with Intune Administrator or Global Administrator credentials.
In the left navigation, click Devices > Manage devices > Configuration. Click Create > New Policy.
Set the following:
- Platform: Windows 10 and later
- Profile type: Properties catalog
Click Create. On the Basics tab, name the policy (e.g. App Inventory - All Properties) and add a description. Click Next.
Expected result: The policy creation wizard opens with tabs for Basics, Configuration settings, and Assignments.
Note
Don't confuse Properties catalog with Custom profile type. Properties catalog is specifically designed for structured inventory collection.
2Select application properties for collection
Select which application properties the Device Inventory Agent will collect.
Configuration settings > Add Properties > ApplicationPropertiesOn the Configuration settings tab, click + Add Properties. Check the ApplicationProperties checkbox to expand all available properties.
Required properties (auto-selected): App Name, App Version, Publisher, Architectures, Install Scope, Install Scope Platform User Id, Install Scope User Id.
Recommended optional properties: Install location, Install date, Install Scope User Name, Platform Specific App Id.
Per Microsoft Learn's app inventory documentation, the Device Inventory Agent collects Win32 app data from uninstall registry keys and Store app data via the Package Manager API. The first sync is a full upload; subsequent syncs use delta uploads.
Click Next to reach the Assignments tab.
Expected result: The selected application properties appear in the configuration settings list with checkmarks.
Note
Not all properties return data for every application. Data availability depends on whether the information exists in the source (registry key or package manager API) on the device.
3Assign the policy and verify deployment
Assign the policy to device groups and deploy it.
Assignments > Add groups > Review + createOn the Assignments tab, click + Add groups under Include. Choose one of:
- All devices for tenant-wide coverage
- Specific device groups for targeted deployment
For initial testing, select a pilot group with 10-20 devices.
Click Next to skip Scope tags (unless your org uses them). On Review + create, verify your settings and click Create.
The policy deploys to assigned devices at their next check-in (up to 8 hours). Per Microsoft Learn, it can take up to 24 hours for the initial inventory data collection. View results at Devices > All devices > select a device > All Apps > App Inventory tab.
Expected result: The policy appears in Devices > Configuration with Deployed status and shows the number of targeted devices.
Note
If multiple Properties Catalog policies target the same device, the device merges settings. When there's a conflict, "collect" wins over "don't collect" for a given property, per Microsoft's documentation.
Troubleshooting
Win32 application data missing from inventory
Warning
Cause: Intune Management Extension or Device Inventory Agent not running, or co-managed device with Client Apps workload assigned to Configuration Manager.
Verify the InventoryService is running:
Get-Service -Name InventoryServiceFor co-managed devices, check the Client Apps workload assignment in Configuration Manager > Co-management > Workloads. Also review C:\Program Files\Microsoft Device Inventory Agent\Logs\InventoryAdaptor.log for errors.
Policy shows Pending status after deployment
Note
Cause: Device hasn't checked in yet (up to 8 hours for policy, up to 24 hours for initial data collection).
Force a device sync from the Intune admin center: Devices > All devices > select device > Sync. Alternatively, restart the Intune Management Extension on the device:
Restart-Service -Name IntuneManagementExtension -ForceProperties Catalog option not visible when creating a policy
Warning
Cause: The Properties Catalog profile type isn't available in the policy creation wizard.
Properties Catalog requires a recent Intune service release. Verify your tenant is on a supported version. The feature rolled out broadly in 2025-2026. If missing, check the Intune service health dashboard for pending updates.
Frequently asked questions
How often does Intune collect app inventory data?
Win32 application data refreshes every 24 hours. Modern Store apps refresh every 7 days. The first sync after policy deployment performs a full upload; subsequent syncs are delta-only, sending only changes since the last collection.
What's the difference between managed and discovered apps?
Managed apps are applications deployed through Intune policies. Discovered apps are all applications found on devices through inventory collection, including user-installed software and shadow IT. The Properties Catalog collects data about discovered apps from registry sources and the Package Manager API.
Why don't I see Win32 apps in app inventory?
Check that the Intune Management Extension service is running on the device. For co-managed devices with Configuration Manager, verify the Client Apps workload is switched to Intune. Review logs at C:\Program Files\Microsoft Device Inventory Agent\Logs\InventoryAdaptor.log.
Does app inventory collection impact network bandwidth?
The initial collection performs a full upload, which can consume bandwidth depending on installed app count. All subsequent collections use delta synchronization, transmitting only changes. Consider staggered deployment for large environments to manage the initial impact.
Can I choose which application properties to collect?
Yes. You can select individual properties or all properties in the ApplicationProperties category. Required properties (App Name, Version, Publisher, Architectures, Install Scope) are auto-selected. Optional properties like Install location and Install date can be added for richer data.
Conclusion
You've configured a Properties Catalog policy in Intune to collect detailed app inventory data from Windows devices. The Device Inventory Agent now automatically collects Win32 and Store app data using delta synchronization, and you can view results under each device's All Apps tab.
The Properties Catalog gives you complete application visibility across all managed Windows devices with minimal ongoing effort.
Devices > Manage devices > Configuration > Properties Catalog policySources2