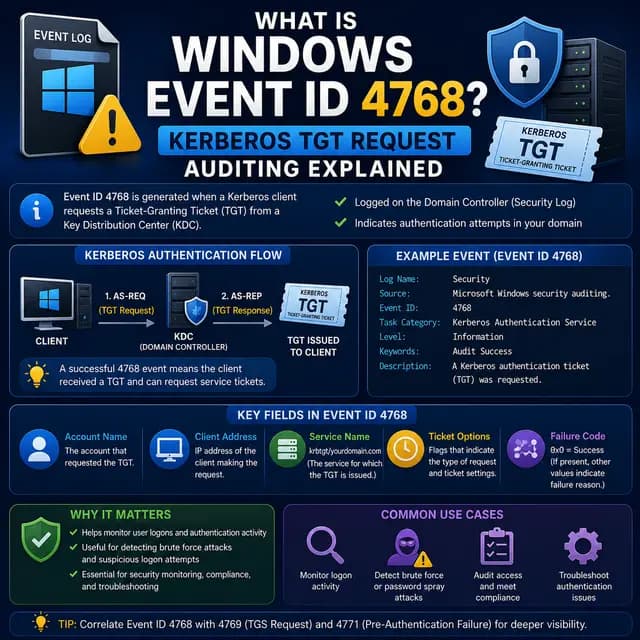
Cloud Kerberos trust is Microsoft's recommended model for Windows Hello for Business in hybrid environments. Instead of requiring complex PKI infrastructure (certificate authorities, templates, CRLs), it uses Entra ID as the Kerberos Key Distribution Center. Users authenticate with PIN, fingerprint, or face recognition, and Entra ID issues Kerberos tickets that on-premises resources accept. This tutorial covers the full setup: creating the Entra Kerberos server object in AD, configuring Intune policies via Account Protection and Settings Catalog, and verifying passwordless SSO to on-prem file shares and apps.
Before you start
What you will learn
- How to deploy Windows Hello for Business with cloud Kerberos trust using Microsoft Intune, from AD object creation to policy deployment and end-user verification.
- Cloud Kerberos trust eliminates PKI complexity while enabling passwordless authentication to both cloud and on-premises resources. It's Microsoft's recommended hybrid Hello model for new deployments.
Requirements
- Microsoft Intune admin center, on-premises AD domain controller, PowerShell
- Hybrid Entra ID environment: on-prem AD with Entra Connect, Entra ID joined or Hybrid joined Windows 10/11 devices with TPM 2.0
- Global Administrator (Entra ID)
- Domain Administrator (on-premises AD)
- Intune Administrator
Good to know
- 30-45 minutes
Quick answer
Create the Entra Kerberos server object in AD, then deploy two Intune policies: Account Protection (Hello enrollment settings for users) and Settings Catalog (cloud Kerberos trust for devices).
AD: New-AzureADKerberosServer > Intune: Account Protection + Settings Catalog policiesStep-by-step tutorial
3 stepsInstall module and create Entra Kerberos server object in AD
Create the Microsoft Entra Kerberos server object in on-premises AD, the bridge between cloud and on-prem Kerberos.
On a domain-joined machine with Domain Admin privileges, open PowerShell as Administrator.
Install and import the module:
Install-Module -Name AzureADHybridAuthenticationManagement -Force
Import-Module AzureADHybridAuthenticationManagementConnect to Entra ID and create the Kerberos server object:
Connect-AzureAD
New-AzureADKerberosServer -Domain "yourdomain.com"Replace yourdomain.com with your actual AD domain. The command creates an AzureADKerberos computer account and a krbtgt_AzureAD user account in your domain. These objects let on-premises resources accept Kerberos tickets issued by Entra ID.
Verify:
Get-AzureADKerberosServer -Domain "yourdomain.com"You need both Global Admin (Entra ID) and Domain Admin (on-prem AD) credentials. The command prompts for both.
Install-Module -Name AzureADHybridAuthenticationManagement -Force
New-AzureADKerberosServer -Domain "yourdomain.com"Run this on a domain controller or a machine with AD RSAT tools for the best experience. The AzureADKerberos object must replicate to all DCs before cloud Kerberos trust works reliably. Wait for AD replication to complete (or force it with repadmin /syncall).
Create Account Protection and Settings Catalog policies in Intune
Create and configure both Intune policies: Account Protection for Hello enrollment and Settings Catalog for cloud Kerberos trust.
Intune > Endpoint Security > Account Protection + Devices > Configuration > Settings CatalogPolicy 1: Account Protection (user-targeted)
In Intune, go to Endpoint Security > Account Protection > Create Policy. Select Windows 10 and later, profile Account Protection.
Configure:
- Use Windows Hello For Business (User): Enabled
- Require Security Device (User): Enabled
- Minimum PIN Length: 6
- Lowercase/Uppercase/Special Characters: Allow
Assign to a user security group. Click Create.
Policy 2: Settings Catalog (device-targeted)
Go to Devices > Configuration > Create > New Policy. Select Windows 10 and later, Settings Catalog.
Name it "Windows Hello Cloud Kerberos Trust". Click Add settings, search "Windows Hello for Business" and add:
- Use Cloud Trust For On Prem Auth: Enabled
- Cloud Kerberos Ticket Retrieval Enabled: Enabled
- Use Certificate For On Prem Auth: Disabled
Assign to a device security group. Click Create.
Account Protection policies go to users, Settings Catalog policies go to devices. Don't mix these assignments. If migrating from certificate-based Hello, the 'Use Certificate For On Prem Auth: Disabled' setting is critical to avoid conflicts.
Test Hello enrollment and verify cloud Kerberos trust SSO
Verify that Hello enrollment works and cloud Kerberos tickets grant access to on-premises resources.
Force a policy sync on a target device:
C:\Windows\System32\deviceenroller.exe /c /AutoEnrollMDMHave a test user sign in and set up Windows Hello: Settings > Accounts > Sign-in options > Windows Hello PIN > Set up. Complete MFA verification and create a PIN.
Test on-premises access:
net use Z: \\fileserver\share
klistThe klist output should show Kerberos tickets including a krbtgt entry from the cloud. File share access should succeed without any password prompt.
Check device registration:
dsregcmd /statusLook for AzureAdJoined: YES or DomainJoined: YES + AzureAdPrt: YES.
Check Hello events in Event Viewer:
Applications and Services Logs > Microsoft > Windows > HelloForBusiness > OperationalLook for Event ID 300-series entries confirming cloud Kerberos trust authentication.
dsregcmd /status
klistIf on-prem access fails, check that the AzureADKerberos object has replicated to the DC the device is authenticating against. Verify VPN or direct line-of-sight to a DC is available. Run klist purge and retry if tickets are stale.
Confirm the result
Troubleshooting
On-prem file share access fails after Hello enrollment
Cause: The AzureADKerberos computer object hasn't replicated to the DC the device is authenticating against, or the object wasn't created correctly.
Verify the AzureADKerberos object exists in AD:
Get-AzureADKerberosServer -Domain "yourdomain.com"Force AD replication:
repadmin /syncall /AdePOn the client, purge stale tickets and retry:
klist purge
net use Z: \\server\share
klistSet-AzureADKerberosServer or New-AzureADKerberosServer throws 'Failed to connect to domain'
Cause: Running New-AzureADKerberosServer without proper Global Admin credentials, or the -DomainCredential parameter is incorrectly formatted.
Run the command on a machine that is domain-joined and has line-of-sight to a DC. Use explicit credentials:
$cloudCred = Get-Credential # Global Admin
$domainCred = Get-Credential # Domain Admin (DOMAIN\user format)
New-AzureADKerberosServer -Domain "yourdomain.com" -CloudCredential $cloudCred -DomainCredential $domainCredDon't pass -DomainCredential if running as Domain Admin already. The dual-credential pattern often resolves authentication context conflicts.
Hello enrolls successfully but klist shows no cloud Kerberos tickets
Cause: The Settings Catalog policy with 'Use Cloud Trust For On Prem Auth' wasn't applied, or 'Use Certificate For On Prem Auth' is still enabled from a previous configuration.
In Intune, verify the Settings Catalog policy applied to the device: Devices > Configuration > select policy > Device status.
On the device, check the applied policy:
dsregcmd /statusLook for CloudTGT entries. If absent, force a sync and wait 15 minutes:
deviceenroller.exe /c /AutoEnrollMDMConfirm 'Use Certificate For On Prem Auth' is Disabled in the Settings Catalog policy.
Frequently asked questions
How does cloud Kerberos trust differ from certificate-based Hello?
Cloud Kerberos trust uses Entra ID as the KDC to issue Kerberos tickets, eliminating PKI infrastructure (no CA, certificate templates, or CRL management). Certificate-based Hello requires deploying and maintaining a full PKI stack. Microsoft recommends cloud Kerberos trust for new deployments.
What are the prerequisites for cloud Kerberos trust?
Windows 10/11 with TPM 2.0, Entra ID joined or Hybrid joined devices, on-prem AD with Windows Server 2016+ DCs, Entra Connect configured, Intune licensing, and MFA enabled for users. The AzureADHybridAuthenticationManagement PowerShell module is needed for the AD object creation.
Can I use both certificate and cloud Kerberos trust at the same time?
No. Per Microsoft's documentation, certificate-based and cloud Kerberos trust cannot run on the same device simultaneously. If migrating, disable 'Use Certificate For On Prem Auth' in the Settings Catalog policy before enabling cloud trust.
What if the device can't reach Entra ID?
The device needs to reach Entra ID to obtain cloud-issued Kerberos tickets. Without internet or VPN connectivity to Azure, cloud Kerberos trust won't work for on-prem access. Plan backup authentication methods for fully offline scenarios.
How do I troubleshoot cloud Kerberos trust failures?
Check Event Viewer under HelloForBusiness > Operational for Event 300-series. Run dsregcmd /status to verify device registration. Use klist to inspect Kerberos tickets. Confirm the AzureADKerberos object exists in AD and has replicated. Verify both Intune policies applied successfully.