How to Configure Maintenance Windows in Microsoft Intune for Update Control
Create an Intune Settings catalog policy to schedule Windows Update maintenance windows during off-hours, then assign, deploy, and verify it on your managed devices.

- Difficulty
- Intermediate
- Time required
- 30-45 minutes
- Steps
- 8
- Platform
- Microsoft Intune
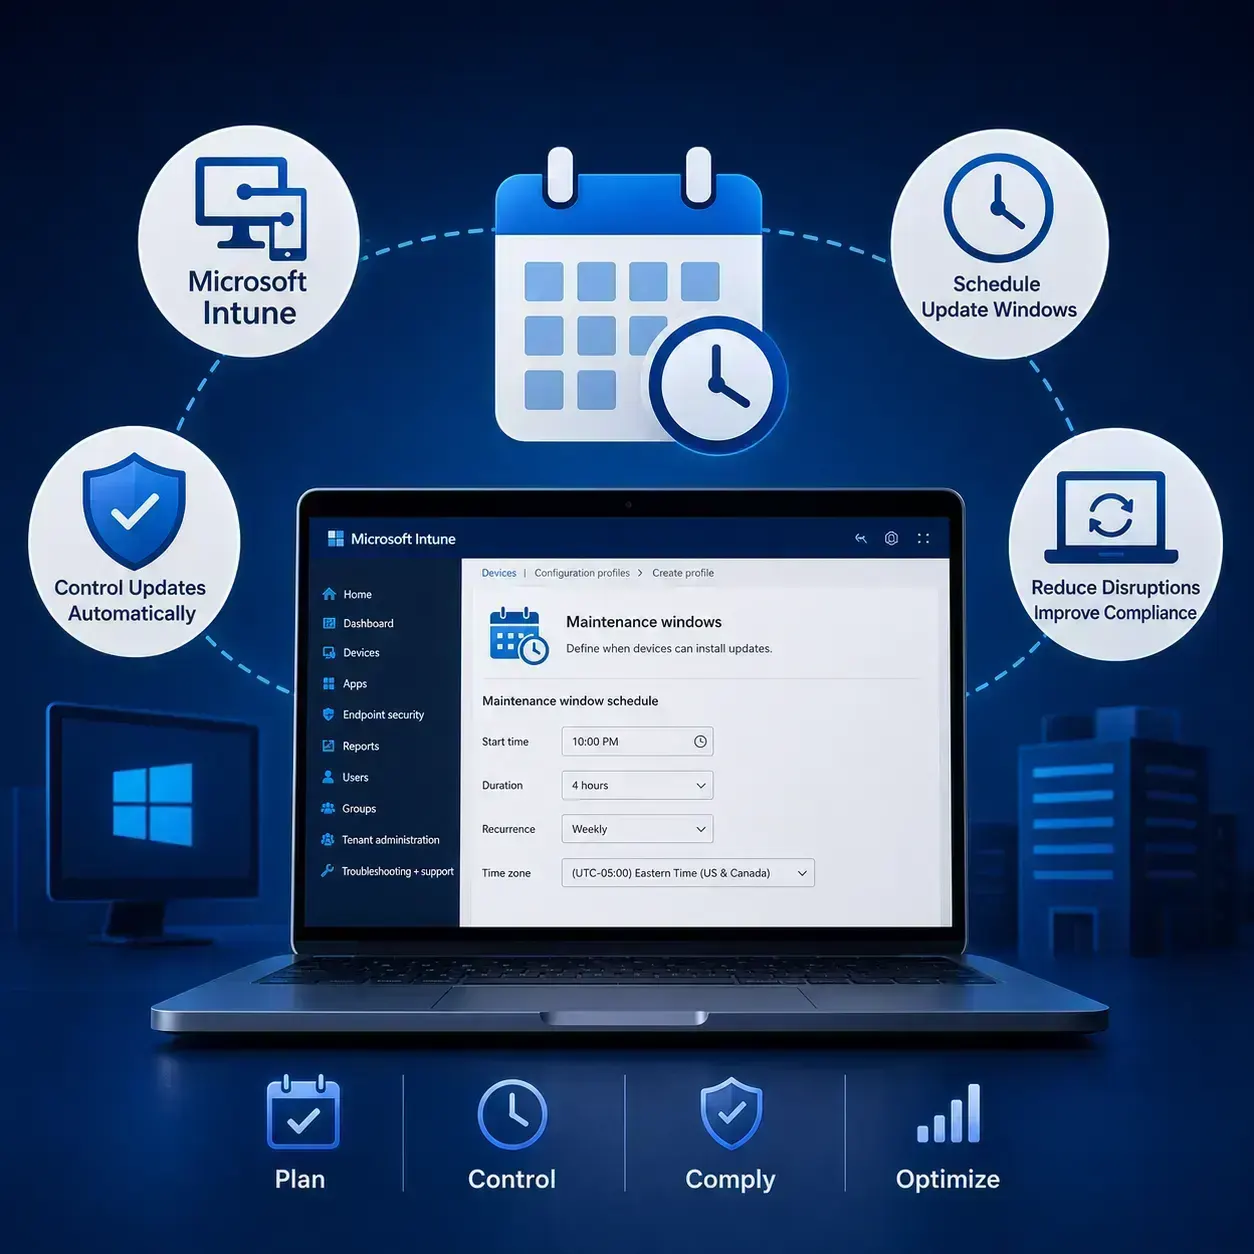
Table of contents
Quick Answer
Go to the stepsIn the Intune admin center, create a Settings catalog policy for Windows 10 and later, add the five Maintenance Window settings, set the start time (ISO 8601), duration in minutes, recurrence, and governed actions, then assign it to your device groups. Target devices must run Windows 11 24H2 or later, and windows are capped at 24 hours.
- Sign in at endpoint.microsoft.com and go to Devices > Manage devices > Configuration > Create > New policy.
- Choose Platform: Windows 10 and later and Profile type: Settings catalog, then name the policy.
- Search 'Maintenance Window' and add Enabled, Start Date Time, Duration, Recurrence Type, and Governed Actions.
- Set the schedule: ISO 8601 start time, duration in minutes (e.g., 300), recurrence (1-4), and governed actions bitmask (1 install, 2 restart, 3 both).
- Assign to the correct device groups, review, and click Create; force a Sync on test devices to apply immediately.
Devices > Manage devices > Configuration > Create > New policyExpected result: A deployed Settings catalog policy that schedules Windows update installs and restarts inside your defined off-hours window on assigned devices, verifiable in Devices > Monitor > Device configuration.
Key takeaways
- You will learn how to create, assign, and verify a Microsoft Intune Settings catalog policy that schedules Windows updates inside a controlled maintenance window during off-hours.
- Confining update installs and restarts to a defined window prevents mid-day reboots and productivity loss, while still keeping devices patched on a predictable schedule. It gives IT teams deterministic control over when update activity happens across managed fleets.
- A properly scoped Intune maintenance window policy schedules Windows updates during off-hours so patching happens without disrupting business operations.
Introduction
A maintenance window in Microsoft Intune tells the Windows Update client when it is allowed to install updates and restart devices, so those actions stay inside a scheduled off-hours block instead of interrupting users during the workday. You configure it as a Settings catalog configuration policy targeting Windows 10 and later, adding the five maintenance window settings — Enabled, Start Date Time, Duration, Recurrence Type, and Governed Actions — then assign it to device groups. This tutorial walks through building the policy from endpoint.microsoft.com, setting the schedule in ISO 8601 format with a duration in minutes, and choosing recurrence and governed-action values. It also covers optional advanced control through custom OMA-URI settings under ./Vendor/MSFT/Policy/Config/Update/MaintenanceWindow/, aligning the window with your existing update rings, and verifying enforcement on target devices. Note that the maintenance window feature requires Windows 11 24H2 or later on target devices, and windows are capped at a 24-hour maximum duration.
Who this is for: This guide is for sysadmins, MSP technicians, and IT pros who manage Windows update policy through Microsoft Intune and want to constrain update timing.
Before you start
- Access
- Sign in to the Microsoft Intune admin center at endpoint.microsoft.com with an account that can create and assign device configuration policies. Target devices must be enrolled in Intune and running Windows 11 24H2 or later for the maintenance window settings to take effect.
- Required roles
- Intune Administrator (or a custom role with Device configuration create/assign permissions)
- Intune Administrator
- Required licenses
- Microsoft Intune
- Vendor
- Microsoft
- Tested environment
- Microsoft Intune admin center; Windows 11 24H2 or later
- Administrator permissions required
Steps reference the Microsoft Intune admin center (endpoint.microsoft.com) with Settings catalog and Custom (OMA-URI) profiles; the maintenance window feature requires Windows 11 24H2 or later on target devices.
About 20-30 minutes to create and assign the policy; allow up to ~8 hours (or a forced sync) for it to reach devices.
Warning: Avoid conflicting maintenance window policies
Do not assign more than one maintenance window policy to the same devices. When policies conflict, the client prioritizes 'Software updates' windows over 'All deployments' windows, which can cause updates to install at unexpected times. Review existing assignments before adding a new policy.
Warning: Test custom OMA-URI before broad deployment
Custom OMA-URI policies under ./Vendor/MSFT/Policy/Config/Update/MaintenanceWindow/ require exact paths, data types, and values. A syntax error can misconfigure update behavior on every targeted device. Deploy to a small pilot group and verify before rolling out widely.
Note: Maintenance windows are capped at 24 hours
The Windows Update client automatically truncates any window longer than 24 hours. If you set Duration above 1440 minutes, updates may not behave as scheduled. Keep the duration within the 24-hour limit.
1Create a Settings catalog configuration policy
Start a new maintenance window policy in the Intune admin center.
Devices > Manage devices > Configuration > Create > New policyOpen your browser, go to endpoint.microsoft.com, and sign in with an account that has Intune policy authoring rights (for example Intune Administrator).
In the left navigation, go to Devices > Manage devices > Configuration. On the Configuration page, click Create, then select New policy.
In the create pane, set:
- Platform: Windows 10 and later
- Profile type: Settings catalog
Click Create to open the policy wizard.
Expected result: The Settings catalog policy wizard opens on the Basics tab, ready to be named and configured.
Note
Use a descriptive naming convention such as MW-Updates-NonBusinessHours so maintenance window policies are easy to identify later among other configuration profiles.
2Name the policy and add the maintenance window settings
Name the policy and add the five maintenance window settings from the Settings catalog.
Configuration policy > Basics / Configuration settingsOn the Basics tab, enter:
- Name:
Maintenance Window - Updates - Description:
Schedules Windows updates during off-hours to prevent business disruption
Click Next to reach the Configuration settings tab. Use the Add settings search box and type Maintenance Window. The results appear under the Windows Update category.
Select these five settings to add them to the policy:
- Maintenance Window Enabled
- Maintenance Window Start Date Time
- Maintenance Window Duration
- Maintenance Window Recurrence Type
- Maintenance Window Governed Actions
Close the settings picker to return to the configuration list.
Expected result: All five maintenance window settings appear in the Configuration settings list with their default values shown.
Note
If the maintenance window settings do not appear, confirm your target devices run Windows 11 24H2 or later — this feature depends on the Feature_Containment_UUS_Feature_MaintenanceWindow_59270588 flag and is not available on earlier builds.
3Configure the schedule, duration, recurrence, and governed actions
Set the timing, duration, recurrence, and allowed actions for off-hours updates.
Configuration policy > Configuration settingsSet each maintenance window setting to match your off-hours window:
- Maintenance Window Enabled: Enabled
- Maintenance Window Start Date Time: enter the start time in ISO 8601 format. For 10 PM on 28 April 2026, enter
2026-04-28T22:00:00.000Z. - Maintenance Window Duration: enter the length in minutes — for a 5-hour window enter
300. - Maintenance Window Recurrence Type: choose one of
1= no repeat (one-time),2= daily,3= weekly,4= monthly. Weekly (3) suits most regular maintenance schedules. - Maintenance Window Governed Actions: set the bitmask for allowed actions —
1= install updates,2= restart device,3= both install and restart.
Review each value before continuing.
Expected result: Each setting shows your intended value (enabled, start time, duration, recurrence, governed actions) ready to review.
Note
The Start Date Time uses UTC (Z suffix) in ISO 8601 — account for your time zone when picking the hour. Maintenance windows have a maximum duration of 24 hours; longer values are truncated by the Windows Update client. Schedule during your lowest-usage periods (many organizations use weekend nights or 2 AM–6 AM).
4Assign the policy to device groups
Target the correct devices and avoid conflicting assignments.
Configuration policy > AssignmentsClick Next to open the Assignments tab. Under Included groups, click Add groups and select the device groups that should receive this maintenance window. Common targeting options:
- An All Windows devices group for organization-wide windows
- Department-specific groups for different schedules per team
- Device-type groups to separate laptops from desktops
If certain machines must never be interrupted, use Excluded groups to add groups containing servers or always-on workstations.
Click Next to continue to the review screen.
Expected result: Your selected included groups appear in the Assignments summary, with any exclusions listed correctly.
Note
Avoid assigning conflicting maintenance window policies to the same devices. The client prioritizes "Software updates" windows over "All deployments" windows, which can produce unexpected behavior. Keep one clear window policy per device set.
5Review and deploy the policy
Confirm all settings and push the policy to targeted devices.
Configuration policy > Review + create; Devices > Monitor > Device configurationOn the Review + create tab, verify:
- Policy name and description
- Maintenance window schedule and duration
- Recurrence and governed actions
- Assigned device groups
When everything is correct, click Create to deploy the policy.
To watch deployment, go to Devices > Monitor > Device configuration and select your maintenance window policy to see per-device status and any errors.
Expected result: The policy is created and, in Device configuration monitoring, shows deployment progress across targeted devices.
Note
Device configuration policies typically apply within the next sync cycle (up to ~8 hours), though it is often faster. On test devices, use the Sync action in the Intune portal (or on the device) to force immediate policy application rather than waiting.
6Optionally set advanced options with a custom OMA-URI profile
Access Update CSP maintenance window settings beyond the Settings catalog UI.
Devices > Configuration > Create > New policy > CustomFor more granular control, go to Devices > Configuration > Create > New policy and choose Platform: Windows 10 and later, Profile type: Custom.
In the custom profile, click Add to create OMA-URI settings, then add each of the following:
./Vendor/MSFT/Policy/Config/Update/MaintenanceWindow/Enable— Data type Boolean — valuetrue./Vendor/MSFT/Policy/Config/Update/MaintenanceWindow/StartDateTime— Data type String — value2026-04-28T22:00:00.000Z./Vendor/MSFT/Policy/Config/Update/MaintenanceWindow/Duration— Data type Integer — value300./Vendor/MSFT/Policy/Config/Update/MaintenanceWindow/RecurrenceType— Data type Integer — value3(weekly)
Assign and create the profile as in the earlier steps.
./Vendor/MSFT/Policy/Config/Update/MaintenanceWindow/StartDateTimeExpected result: The custom profile lists each OMA-URI row with the correct data type and value, ready to assign and deploy.
Note
OMA-URI paths and data types must be exact — a wrong type (e.g., String vs Integer) causes the setting to fail silently or error. Deploy to a small test group before broad rollout. This is optional; use it only when the Settings catalog UI does not expose a value you need.
7Integrate with existing update rings
Align update ring deferrals and install behavior with the maintenance window.
Devices > Windows updates > Update rings for Windows 10 and laterGo to Devices > Windows updates > Update rings for Windows 10 and later. Select an existing ring or create a new one.
Configure the ring to work with the maintenance window:
- Quality update deferral period: 0–7 days (e.g., 3) so updates are available for the window
- Feature update deferral period: based on your testing needs (commonly 30–180 days)
- Installation behavior: auto install and restart at maintenance time
- Restart checks: skip all restart checks
Assign the update ring to the same device groups as the maintenance window policy so both configurations land on the same machines.
{
  "qualityUpdatesDeferralPeriodInDays": 3,
  "featureUpdatesDeferralPeriodInDays": 60,
  "installationBehavior": "autoInstallAtMaintenanceTime",
  "restartChecks": "skip"
}
Expected result: The update ring shows the deferral and installation-behavior values and is assigned to the same groups as the window policy.
Note
Pair short quality deferrals (3–7 days) with the maintenance window to balance security and stability — you get time to catch problematic updates while ensuring they install in the planned window. The JSON above illustrates the equivalent ring properties; set them via the ring UI fields.
8Monitor and troubleshoot the maintenance window
Confirm the window is enforced and resolve common issues.
Reports > Windows updatesMonitor effectiveness through several channels:
- Intune reporting: go to Reports > Windows updates to review installation patterns and compliance.
- Device-level checks: run the PowerShell below on a target device to inspect the applied registry values and update client events for maintenance activity.
Work through common issues:
- Updates installing outside the window: check for conflicting active hours or multiple maintenance window policies.
- Devices not receiving the policy: verify enrollment status and group membership.
- Window not enforced: confirm Windows 11 24H2+ and feature-flag availability.
- Devices powered off during the window: configure deadline enforcement in the update ring so updates eventually install.
# Check maintenance window registry settings
Get-ItemProperty -Path "HKLM:\SOFTWARE\Microsoft\WindowsUpdate\UX\Settings" -Name "MaintenanceWindow*"

# View Windows Update log for maintenance window activity
Get-WinEvent -LogName "Microsoft-Windows-WindowsUpdateClient/Operational" | Where-Object {$_.Message -like "*maintenance*"}
Expected result: The registry query returns the applied MaintenanceWindow values and the event query shows maintenance-related Windows Update client entries.
Note
Run the PowerShell in an elevated session on a device that has already synced the policy. If the registry values are missing, the device likely has not received the policy yet or does not meet the Windows 11 24H2 requirement. Remember the 24-hour maximum window — longer durations are truncated by the client.
Confirming the Maintenance Window Is Active
Confirm configuration
A successful configuration is not just a policy that shows up in the portal — it is a device that actually schedules and installs updates inside your defined window and stays quiet outside it. After the policy syncs, confirm the outcome at two levels: the Intune console and the target device itself.
In the Intune admin center, go to Devices > Monitor > Device configuration, open your maintenance window policy, and review the deployment status. Devices should report the policy as Succeeded rather than Error, Conflict, or Not applicable. A Conflict status usually means another maintenance window policy or update ring targets the same device with incompatible settings. A Not applicable result most often means the device is not on Windows 11 24H2 or later, where the setting is unsupported.
On a target device, the applied settings are written under the registry path HKLM:\SOFTWARE\Microsoft\WindowsUpdate\UX\Settings. Reading the MaintenanceWindow* values confirms the enabled state, start time, duration, and recurrence that Intune pushed down. The Microsoft-Windows-WindowsUpdateClient/Operational event log then shows whether update and restart activity actually occurred during the scheduled window rather than during business hours.
Interpret this as more than a checkbox: the goal is that governed actions (install, restart, or both) happen only inside the window, and that no conflicting active hours or second policy overrides the schedule.
Troubleshooting
Maintenance window settings do not appear in the Settings catalog search
Warning
Cause: The target devices are not running Windows 11 24H2 or later, which is required for the maintenance window feature (Feature_Containment_UUS_Feature_MaintenanceWindow_59270588).
Confirm your target devices are on Windows 11 24H2 or later. Filter or scope the policy to compliant devices, and if the catalog still doesn't surface the settings, use the Custom OMA-URI approach under ./Vendor/MSFT/Policy/Config/Update/MaintenanceWindow/ described in Step 6.
Updates are installing outside the configured maintenance window
Critical
Cause: Conflicting active hours settings or multiple maintenance window policies are assigned to the same devices, and the client prioritizes 'Software updates' windows over 'All deployments' windows.
Review the device for conflicting active hours and remove or reconcile any additional maintenance window policies targeting the same groups. Ensure only one maintenance window policy applies per device, and verify Governed Actions is set correctly (1 install, 2 restart, 3 both).
The maintenance window is longer than expected or gets cut short
Warning
Cause: The Windows Update client enforces a maximum maintenance window duration of 24 hours and automatically truncates anything longer.
Set Maintenance Window Duration to a value at or below 1440 minutes (24 hours). If you need broader coverage, use recurrence (daily/weekly) instead of a single oversized window.
Devices are not receiving the maintenance window policy
Warning
Cause: The device is not enrolled correctly, is missing from the assigned group, or has not completed a sync cycle yet.
Verify device enrollment status and group membership under Devices > Monitor > Device configuration. Trigger the Sync action from the Intune portal or the device to force policy application rather than waiting for the ~8-hour cycle.
Custom OMA-URI maintenance window policy fails to apply
Warning
Cause: OMA-URI paths, data types, or values were entered with incorrect syntax, which the Update CSP rejects.
Double-check each OMA-URI path (for example ./Vendor/MSFT/Policy/Config/Update/MaintenanceWindow/Enable), confirm the data type matches (Boolean, String, Integer), and validate the value format such as ISO 8601 for StartDateTime. Test on a small pilot group before broad deployment.
Devices powered off during the maintenance window never install updates
Note
Cause: The maintenance window only allows installs while the device is on and available; offline devices miss the scheduled window.
Configure deadline enforcement in your Windows Update rings so updates eventually install after the deadline even when the device misses the planned window. Pair this with quality update deferrals to balance stability and compliance.
Frequently asked questions
What Windows version is required for Intune maintenance windows?
The maintenance window settings require Windows 11 24H2 or later. On earlier versions the settings will not appear in the Settings catalog because the feature depends on the FeatureContainmentUUSFeatureMaintenanceWindow_59270588 flag.
What is the maximum duration for a Windows Update maintenance window?
The maximum maintenance window duration is 24 hours (1440 minutes). If you configure a longer duration, the Windows Update client automatically truncates it to 24 hours.
How do maintenance windows interact with active hours and update rings?
Maintenance windows can conflict with active hours settings, and the client prioritizes 'Software updates' windows over 'All deployments' windows. Align your update rings by setting installation behavior to auto install and restart at maintenance time and assigning them to the same device groups.
How long does it take for the maintenance window policy to apply to devices?
Device configuration policies typically apply within the next sync cycle, which is roughly 8 hours, though it can be faster. Use the Sync option in the Intune portal or on the device to force immediate application on test machines.
How do I verify the maintenance window is applied on a target device?
On a target device, check the registry with Get-ItemProperty -Path "HKLM:\SOFTWARE\Microsoft\WindowsUpdate\UX\Settings" -Name "MaintenanceWindow*" and review the Microsoft-Windows-WindowsUpdateClient/Operational event log for maintenance-related entries. You can also monitor deployment status under Devices > Monitor > Device configuration.
What happens if a device is powered off during the maintenance window?
If a device is off during the scheduled window, it misses that update opportunity. Configure deadline enforcement in your update rings so updates eventually install after the deadline even when a device was unavailable during the planned window.
Conclusion
You created a Settings catalog configuration policy in Microsoft Intune, added the five maintenance window settings, configured the start time, duration, recurrence, and governed actions, then assigned and deployed the policy to your target device groups. You also learned how to extend control with custom OMA-URI settings, align update rings with the window, and monitor enforcement through Intune reports and device-level checks.
A properly scoped Intune maintenance window policy schedules Windows updates during off-hours so patching happens without disrupting business operations.
Devices > Manage devices > Configuration > Create > New policy