How to Enable and Disable Remote Desktop Access Using Microsoft Intune
Learn how to enable and disable RDP access at scale with Microsoft Intune using custom OMA-URI policies, PowerShell remediation scripts, and the Remote Help alternative for secure enterprise remote access.

- Difficulty
- Intermediate
- Time required
- 45-60 minutes
- Steps
- 8
- Platform
- Microsoft Intune
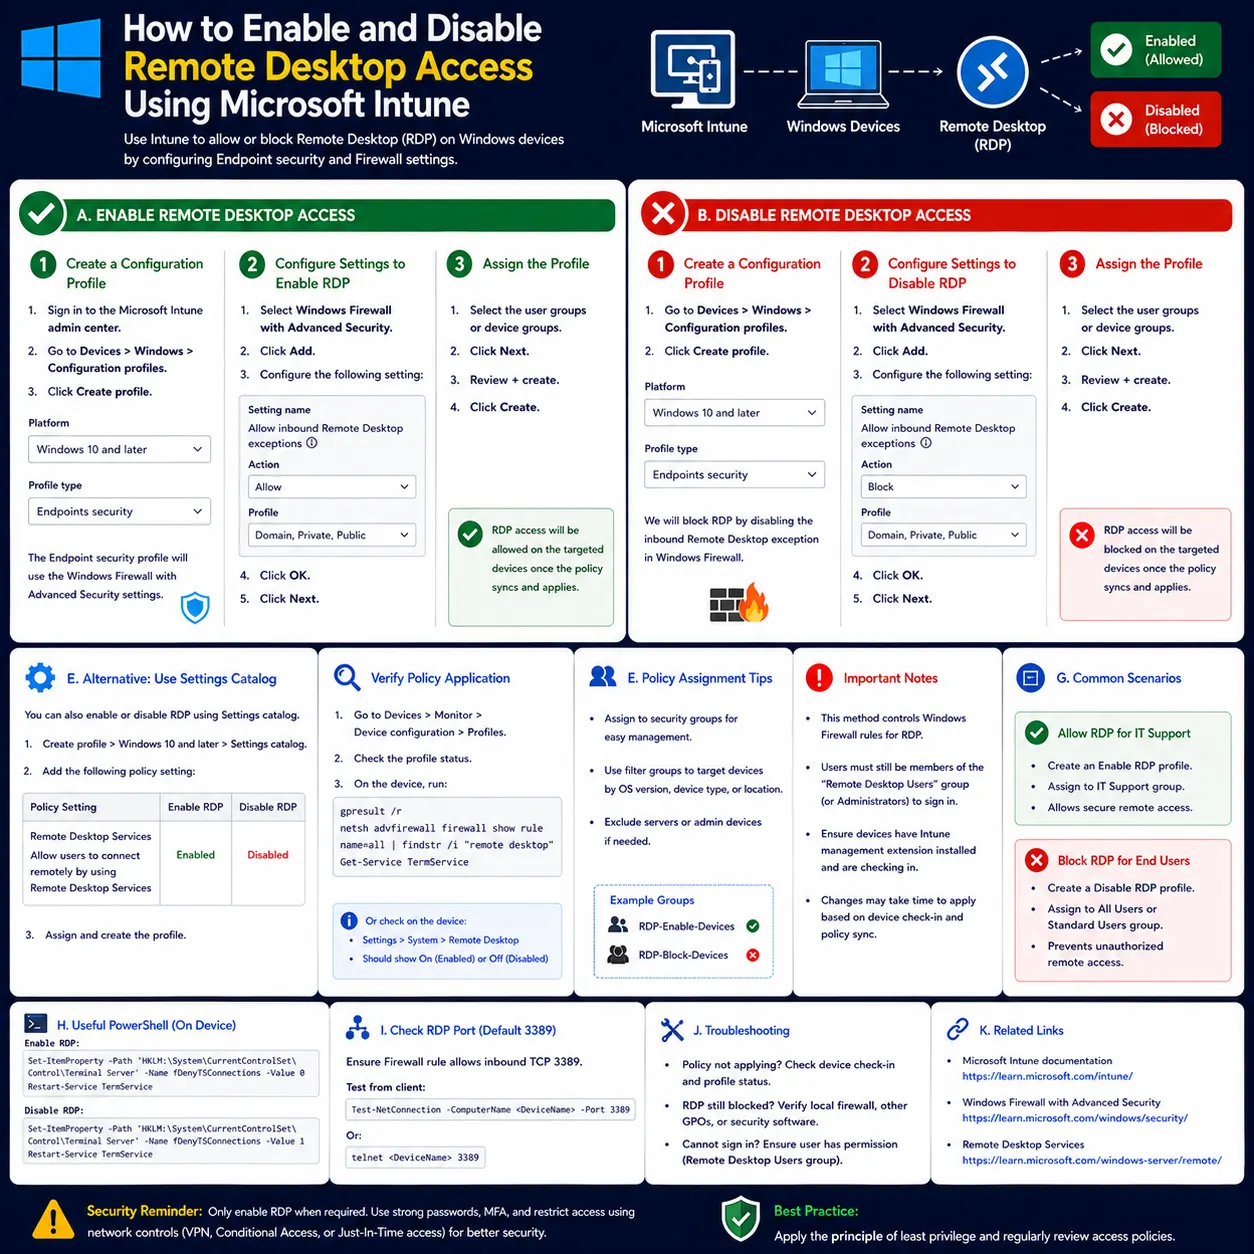
Table of contents
Quick Answer
Go to the stepsThere is no native Intune switch for RDP. Enable it by creating a Windows 10 and later Custom configuration profile with OMA-URI settings (AllowUsersToConnectRemotely and the Remote Desktop firewall rule set to <enabled/>), assign it to targeted device groups, and back it with a PowerShell script that sets fDenyTSConnections to 0 and enables the firewall group. To disable RDP, deploy the reverse policy and script. For IT support, use Intune Remote Help instead.
- In the Intune admin center, create a Windows 10 and later Custom profile with OMA-URI settings for RDP set to <enabled/>.
- Assign the policy to a targeted device group (for example IT Admin Devices), not All devices.
- Add a PowerShell script that sets fDenyTSConnections to 0, enables NLA, and enables the Remote Desktop firewall group.
- Test the connection with mstsc.exe using the hostname and Entra ID/UPN credentials, then verify service, registry, and port 3389.
- To disable RDP, deploy a reverse OMA-URI policy (<disabled/>) and a script that sets fDenyTSConnections to 1 and disables the firewall group.
Devices > Configuration > Create > New policyExpected result: RDP is enabled or disabled on the targeted Windows devices, the Intune policy reports Succeeded, and PowerShell verification returns exit code 0 confirming the registry and firewall state.
Key takeaways
- You will learn to centrally enable and disable Remote Desktop (RDP) access on managed Windows devices through Microsoft Intune using custom OMA-URI configuration profiles and PowerShell scripts. You will also learn to configure Entra ID authentication for RDP and set up Intune Remote Help as a more secure alternative.
- Manually configuring RDP on each machine or maintaining Group Policy for it does not scale and leaves gaps in a mobile, cloud-managed fleet. Centralizing RDP control in Intune lets you enable access only where needed, disable it cleanly for security, and monitor compliance across all devices.
- Enable or disable RDP at scale in Intune by pairing custom OMA-URI policies with PowerShell remediation scripts, and prefer Remote Help for secure remote assistance.
Introduction
Microsoft Intune does not expose a native toggle for Remote Desktop Protocol (RDP) in its standard configuration profiles, so enabling or disabling it centrally requires a combination of custom OMA-URI policies and PowerShell scripts. This tutorial walks through both the traditional RDP approach and Microsoft's recommended alternative, Intune Remote Help, so you can choose the right tool for each scenario.
On the RDP side, you will build custom profiles that set AllowUsersToConnectRemotely and the Remote Desktop firewall rule, then back them with a remediation script that sets fDenyTSConnections, enables Network Level Authentication (NLA), and enables the Remote Desktop firewall group. You will also configure Entra ID sign-in over RDP, test connectivity with mstsc.exe, create a matching disable policy, and set up monitoring.
One important caveat up front: the OMA-URI approach has known limitations. The Windows Settings app may still display Remote Desktop as Disabled even after a policy deploys successfully, which is why the accompanying PowerShell scripts are used to confirm and enforce the actual configuration. Where possible, prefer Remote Help for IT support scenarios, since it avoids firewall and VPN dependencies and fits zero-trust architectures.
Who this is for: This guide is for sysadmins, MSP technicians, and IT professionals who manage Windows devices with Microsoft Intune and need controlled remote access. It assumes intermediate familiarity with the Intune admin center, device groups, and basic PowerShell.
Before you start
- Access
- You need administrative access to the Microsoft Intune admin center (endpoint.microsoft.com) with permission to create configuration profiles, deploy platform scripts, and assign policies to device groups. Target devices must be enrolled in Intune and running Windows 10 or later.
- Required roles
- Intune Administrator (or a role with Device Configuration create/assign and Platform Scripts permissions)
- Help Desk Operator (assigned to support staff who will run Remote Help sessions)
- Intune Administrator
- Help Desk Operator
- Required licenses
- Microsoft Intune (device management)
- Remote Help add-on (required to use Intune Remote Help)
- Microsoft Intune
- Intune Remote Help (add-on)
- Vendor
- Microsoft
- Tested environment
- Microsoft Intune admin center (as of March 2026), Windows 10 and later
- Administrator permissions required
Based on Microsoft Intune behavior documented as of March 2026, targeting Windows 10 and later devices.
Plan roughly 1-2 hours, including policy deployment wait time (policies can take up to about 8 hours to fully apply).
Critical: Test disable policies before broad deployment
A misconfigured Disable RDP policy or PowerShell script can lock administrators out of remote systems, because it stops and disables the TermService service and disables the Remote Desktop firewall group. Deploy and validate disable policies on a small non-production device group first before assigning them to production devices.
Warning: PowerShell scripts run in System context with Bypass execution policy
The remediation scripts change the registry (fDenyTSConnections, UserAuthentication, EnableWebSignIn), toggle firewall rules, and restart or stop TermService with -Force. Review each script and confirm the target group scope before deployment, since these changes take effect silently and without user prompts.
Warning: Internet RDP to Entra ID joined devices requires VPN
Entra ID joined devices connecting over RDP from the internet require VPN connectivity. Direct internet RDP connections may fail due to certificate and name resolution issues, so do not expose RDP (TCP 3389) directly to the internet.
Note: Settings app may misreport RDP status
The Windows Settings app can display Remote Desktop as Disabled even when the OMA-URI policy and registry settings are correctly applied. Rely on the verification commands and Intune deployment reports rather than the Settings app to confirm the real state.
1Create a custom OMA-URI policy to enable RDP
Turn on Remote Desktop through an Intune custom configuration profile.
Microsoft Intune admin center > Devices > Configuration > Create > New policy > Windows 10 and later > Custom1. Sign in to the Microsoft Intune admin center at endpoint.microsoft.com. 2. Go to Devices > Configuration > Create > New policy. 3. For Platform, select Windows 10 and later; for Profile type, select Templates, then choose Custom. 4. Name the policy something clear, such as Enable RDP Access, and click Next. 5. On the Configuration settings tab, click Add and create two OMA-URI settings: - Name: AllowRemoteConnections - OMA-URI: ./Device/Vendor/MSFT/Policy/Config/RemoteDesktopServices/AllowUsersToConnectRemotely - Data type: String - Value: <enabled/> - Name: Firewall RDP Rule - OMA-URI: ./Vendor/MSFT/Policy/Config/Firewall/FirewallRules/RemoteDesktop-UserMode-In-TCP - Data type: String - Value: <enabled/> 6. Save each setting, then continue to the assignments step (covered next). Do not create the policy yet if you want to set assignments in the same wizard.
Expected result: The new custom profile lists both OMA-URI settings (AllowRemoteConnections and Firewall RDP Rule) with their values, and the wizard advances to the Assignments tab.
Note
Known limitation: This OMA-URI approach may not fully enable RDP on every device, and the Windows Settings app can still display Remote Desktop as Disabled even when the policy deploys successfully. That is why the PowerShell remediation script in a later step is required for reliable results. Copy the OMA-URI paths exactly - a single wrong character causes the setting to silently fail.
2Assign the policy to targeted device groups
Scope RDP enablement to the correct devices and avoid over-exposure.
Microsoft Intune admin center > Devices > Configuration > (Enable RDP Access) > Assignments- In the policy wizard, open the Assignments tab.
- Under Included groups, click Add groups and select the specific device groups that should have RDP enabled - for example IT Admin Devices or Remote Work Laptops.
- Optionally use filters (e.g., by OS version or device type) to further narrow the target.
- Avoid assigning to All devices unless your organization explicitly requires universal RDP access.
- Review the Review + create tab, then click Create to deploy the policy.
Expected result: The policy shows the selected groups under Included groups and, after Create, appears in the Configuration profiles list ready to deploy.
Note
Best practice: Create separate policies for enabling and disabling RDP (see the disable step later) rather than editing one policy back and forth. This lets you flip access by moving devices between groups or toggling assignments, and keeps an auditable history.
To track rollout, go to Devices > Monitor > Device configuration. The policy should report Succeeded on targeted devices, typically within about 8 hours depending on device check-in cycles.
3Deploy a PowerShell remediation script to enforce RDP settings
Guarantee the registry and firewall configuration where OMA-URI falls short.
Microsoft Intune admin center > Devices > Scripts and remediations > Platform scripts > Add > Windows 10 and later- Go to Devices > Scripts and remediations > Platform scripts > Add > Windows 10 and later (labeled Devices > Scripts in some tenants).
- Give the script a name such as Enable RDP - Remediation, then upload or paste the script below.
- Under Script settings, set Run this script using the logged on credentials to No (System context), Enforce script signature check to No, and Run script in 64 bit PowerShell Host to Yes.
- Assign the script to the same device groups used for the OMA-URI policy.
- Save to deploy.
# Enable Remote Desktop Registry Setting
Set-ItemProperty -Path 'HKLM:\System\CurrentControlSet\Control\Terminal Server' -Name "fDenyTSConnections" -Value 0 -Force
# Enable Network Level Authentication (recommended for security)
Set-ItemProperty -Path 'HKLM:\System\CurrentControlSet\Control\Terminal Server\WinStations\RDP-Tcp' -Name "UserAuthentication" -Value 1 -Force
# Enable Remote Desktop Firewall Rules
Enable-NetFirewallRule -DisplayGroup "Remote Desktop"
# Verify settings
$rdpEnabled = Get-ItemProperty -Path 'HKLM:\System\CurrentControlSet\Control\Terminal Server' -Name "fDenyTSConnections"
$firewallRules = Get-NetFirewallRule -DisplayGroup "Remote Desktop" | Where-Object {$_.Enabled -eq "True"}
if ($rdpEnabled.fDenyTSConnections -eq 0 -and $firewallRules.Count -gt 0) {
 Write-Output "RDP successfully enabled"
 exit 0
} else {
 Write-Output "RDP configuration failed"
 exit 1
}
Expected result: The script deploys and, on target devices, returns exit code 0 with the output "RDP successfully enabled"; execution status appears in Intune monitoring.
Note
Running in System context is required because the registry keys under HKLM and the firewall rules are machine-scoped. Check results under Devices > Monitor (or the script's own device status view) - successful execution returns exit code 0.
Setting UserAuthentication to 1 enforces Network Level Authentication (NLA), which is the more secure configuration.
4Configure Entra ID authentication for RDP
Allow Entra ID (web account) sign-in over RDP on joined devices.
Microsoft Intune admin center > Devices > Configuration > Create > New policy > Windows 10 and later > Custom1. Create a second Custom OMA-URI policy (same path as step 1) named RDP Web Sign-In. 2. Add these settings: - Name: EnableWebAuth - OMA-URI: ./Device/Vendor/MSFT/Policy/Config/CredentialProviders/AllowPINLogon - Data type: Integer - Value: 1 - Name: WebAccountProvider - OMA-URI: ./Device/Vendor/MSFT/Policy/Config/Authentication/EnableWebSignIn - Data type: Integer - Value: 1 3. Assign the policy to the same device groups. 4. Deploy the companion PowerShell script below (System context) to set the registry value and restart the RDP service.
# Enable web account sign-in for RDP
New-ItemProperty -Path "HKLM:\SOFTWARE\Microsoft\Windows\CurrentVersion\Policies\System" -Name "EnableWebSignIn" -Value 1 -PropertyType DWORD -Force
# Restart Remote Desktop Services
Restart-Service -Name "TermService" -Force
Write-Output "Web authentication enabled for RDP"
Expected result: On a target device, Settings > System > Remote Desktop > Advanced settings shows NLA required and a web account sign-in option becomes available.
Note
Warning: Entra ID joined devices reached via RDP over the internet require VPN connectivity. Direct internet-facing RDP to these devices commonly fails due to certificate and name-resolution issues, so plan for a VPN or a gateway.
Restarting TermService drops any active RDP sessions on the device - schedule this script for maintenance windows where possible.
5Test RDP connectivity and authentication
Confirm clients can reach and authenticate to the remote device.
1. From a client machine, open Remote Desktop Connection by running mstsc.exe. 2. Enter the target computer's hostname in FQDN form (not an IP address): computername.domain.com. 3. When prompted, enter Entra ID credentials in one of these formats: - AzureAD\user@yourdomain.com - or the UPN directly: user@yourdomain.com 4. Connect and confirm you reach the remote desktop. 5. On the target device, run the verification commands below to confirm the service, registry, firewall, and port are all correct.
# Check RDP service status
Get-Service -Name "TermService" | Select-Object Name, Status
# Verify RDP registry setting
Get-ItemProperty -Path 'HKLM:\System\CurrentControlSet\Control\Terminal Server' -Name "fDenyTSConnections"
# Check firewall rules
Get-NetFirewallRule -DisplayGroup "Remote Desktop" | Where-Object {$_.Enabled -eq "True"} | Select-Object DisplayName, Enabled
# Test RDP port accessibility
Test-NetConnection -ComputerName localhost -Port 3389
Expected result: The session connects and authenticates; TermService shows Running, fDenyTSConnections is 0, Remote Desktop rules show Enabled, and Test-NetConnection returns TcpTestSucceeded : True.
Note
Use the hostname/FQDN, not the IP address - Entra ID authentication relies on name resolution and certificate matching.
Pro tip: Consider deploying the Windows App (the successor to the classic Remote Desktop Connection client) through Intune for a more modern client experience.
6Set up Intune Remote Help as a secure alternative
Enable Microsoft's recommended remote assistance instead of raw RDP.
Microsoft Intune admin center > Tenant administration > Roles1. Go to Tenant administration > Roles and assign a built-in role such as Help Desk Operator to users who need remote access. 2. Configure the Remote Help permission level for each role: - View screen - read-only view of the user's screen - Full control - complete remote control - Elevation - ability to respond to UAC prompts - Unattended - connect without user interaction (Android fully managed devices only) 3. Enable Remote Help tenant-wide via Devices > Configuration > Create > New policy and choose Templates > Administrative Templates; search for Remote Help and enable the relevant settings. 4. Optionally deploy the verification script below to confirm the Remote Help app is present on devices.
# Check if Remote Help is available
$remoteHelpApp = Get-AppxPackage -Name "Microsoft.RemoteHelp" -AllUsers
if ($remoteHelpApp) {
 Write-Output "Remote Help app is installed: $($remoteHelpApp.Version)"
} else {
 Write-Output "Remote Help app not found - will auto-install after policy deployment"
}
# Check Intune enrollment status
$enrollmentStatus = Get-ItemProperty -Path "HKLM:\SOFTWARE\Microsoft\Enrollments\*" -Name "EnrollmentType" -ErrorAction SilentlyContinue
if ($enrollmentStatus) {
 Write-Output "Device is Intune enrolled"
} else {
 Write-Output "Device enrollment status unclear"
}
Expected result: Help desk operators can start a Remote Help session from Devices > All devices > (select device) > Remote Help, and the verification script reports the Remote Help app version.
Note
Microsoft recommends Remote Help as the primary remote access method for enterprise support: it uses Entra ID authentication, role-based access, and session logging, and it does not require firewall changes or VPN - a better fit for zero-trust environments than raw RDP.
Unattended access is limited to Android fully managed devices. Remote Help may also require a specific license/add-on in your tenant - confirm entitlement before rollout.
7Create a policy to disable RDP access
Cleanly turn RDP off when remote access is no longer needed.
Microsoft Intune admin center > Devices > Configuration > Create > New policy > Windows 10 and later > Custom1. Create a new Custom OMA-URI policy named Disable RDP Access with these settings: - Name: DisallowRemoteConnections - OMA-URI: ./Device/Vendor/MSFT/Policy/Config/RemoteDesktopServices/AllowUsersToConnectRemotely - Data type: String - Value: <disabled/> - Name: Disable Firewall RDP - OMA-URI: ./Vendor/MSFT/Policy/Config/Firewall/FirewallRules/RemoteDesktop-UserMode-In-TCP - Data type: String - Value: <disabled/> 2. Deploy the companion PowerShell script below (System context) to enforce the disabled state and stop the service. 3. Assign to the target device groups and create the policy.
# Disable Remote Desktop Registry Setting
Set-ItemProperty -Path 'HKLM:\System\CurrentControlSet\Control\Terminal Server' -Name "fDenyTSConnections" -Value 1 -Force
# Disable Remote Desktop Firewall Rules
Disable-NetFirewallRule -DisplayGroup "Remote Desktop"
# Stop Remote Desktop Services
Stop-Service -Name "TermService" -Force
Set-Service -Name "TermService" -StartupType Disabled
# Verify settings
$rdpDisabled = Get-ItemProperty -Path 'HKLM:\System\CurrentControlSet\Control\Terminal Server' -Name "fDenyTSConnections"
$firewallRules = Get-NetFirewallRule -DisplayGroup "Remote Desktop" | Where-Object {$_.Enabled -eq "False"}
if ($rdpDisabled.fDenyTSConnections -eq 1 -and $firewallRules.Count -gt 0) {
 Write-Output "RDP successfully disabled"
 exit 0
} else {
 Write-Output "RDP disable configuration failed"
 exit 1
}
Expected result: RDP connection attempts from a client fail or time out immediately, and the script returns exit code 0 with "RDP successfully disabled".
Note
Warning: Always test disable policies on non-production devices first. Stopping and disabling TermService plus closing the firewall can lock administrators out of remote systems if applied to the wrong group. Keep Remote Help configured so you retain a supported way back in.
Ensure a device is not simultaneously targeted by both the Enable and Disable policies, which causes conflicting settings.
8Monitor and troubleshoot RDP deployment
Verify compliance and diagnose failed deployments across the fleet.
Microsoft Intune admin center > Devices > Monitor > Device configuration- Go to Devices > Monitor > Device configuration to review per-device deployment status; confirm your RDP policies report Succeeded.
- For devices reporting Error or Conflict, open the device to see which setting failed and check for competing policies.
- For hands-on diagnosis, deploy the on-demand troubleshooting script below as a platform script (or run it locally) to report the service state, registry value, and firewall rule status.
- Correlate findings:
fDenyTSConnectionsshould be 0 (enabled) or 1 (disabled), and TermService plus the Remote Desktop firewall rules should match the intended state.
# RDP Troubleshooting and Status Check Script
# Check RDP service
$rdpService = Get-Service -Name "TermService"
Write-Output "RDP Service Status: $($rdpService.Status)"
# Check registry settings
$rdpRegistry = Get-ItemProperty -Path 'HKLM:\System\CurrentControlSet\Control\Terminal Server' -Name "fDenyTSConnections"
Write-Output "RDP Registry Setting (0=Enabled, 1=Disabled): $($rdpRegistry.fDenyTSConnections)"
# Check firewall rules
$firewallRules = Get-NetFirewallRule -DisplayGroup "Remote Desktop"
foreach ($rule in $firewallRules) {
 Write-Output "Firewall Rule: $($rule.DisplayName) - Enabled: $($rule.Enabled)"
}
Expected result: The Device configuration view shows policies as Succeeded, and the script prints the service status, the fDenyTSConnections value, and each Remote Desktop firewall rule's enabled state.
Note
Deployment status can lag by up to about 8 hours because it depends on device check-in intervals - a device that has not checked in recently may still show Pending even though it is healthy.
If the Windows Settings app shows Remote Desktop as Disabled but the troubleshooting script confirms fDenyTSConnections = 0 and RDP works, treat the script/registry output as the source of truth - this is the known Settings-app display quirk.
Confirming Remote Desktop Is Correctly Configured Through Intune
Confirm configuration
A successful configuration means two independent signals agree: Intune reports the policy and script as delivered, and the target device itself shows the expected registry, firewall, and service state. Because the Windows Settings app can misreport Remote Desktop status, do not treat the Settings screen as your source of truth - trust the Intune deployment reports and the on-device verification commands instead.
In the Intune admin center, open Devices > Monitor > Device configuration and confirm your enable (or disable) profile shows Succeeded for the targeted devices; policy delivery can take up to 8 hours. For the PowerShell remediation script, check the script's run results and confirm it returned exit code 0, which the scripts emit only after their own internal checks pass.
On the device, the enabled state is defined by fDenyTSConnections = 0, the Remote Desktop firewall group rules being Enabled, TermService Running, and TCP port 3389 reachable. For a disabled device, expect the mirror image: fDenyTSConnections = 1, the Remote Desktop firewall rules disabled, and TermService stopped and set to a Disabled startup type. When Entra ID authentication is configured, EnableWebSignIn should be 1 and clients should be able to sign in with the AzureAD\user@yourdomain.com or UPN format.
Normal result: Intune shows the profile as Succeeded and the script as exit code 0. On an RDP-enabled device: fDenyTSConnections is 0, the Remote Desktop firewall rules are Enabled, TermService is Running, and Test-NetConnection to port 3389 succeeds. A client can connect via mstsc.exe using the hostname and Entra ID/UPN credentials. On a disabled device, connections are rejected immediately or time out.
Abnormal result: The Settings app shows Disabled even though the policy applied - verify with the commands rather than the UI. If Intune shows Error/Conflict, or the script returns exit code 1, or fDenyTSConnections does not match the intended value, or port 3389 is unreachable when it should be open, the configuration did not fully apply. Run the on-demand troubleshooting script to capture service status, registry values, and firewall rule states before re-checking assignments and policy conflicts.
RDP registry setting (enabled device)
fDenyTSConnections : 0
0 means Remote Desktop connections are allowed; 1 means they are denied.
PowerShell remediation success
RDP successfully enabled (exit code 0)
The enable script emits this and exits 0 only after confirming fDenyTSConnections=0 and at least one enabled Remote Desktop firewall rule.
Firewall rule state (enabled)
Remote Desktop - User Mode (TCP-In) Enabled: True
The Remote Desktop firewall group must be enabled for inbound RDP to reach the device.
Port reachability check
TcpTestSucceeded : True (Test-NetConnection -Port 3389)
Confirms the listener is active and the firewall permits TCP 3389 on the target device.
Disabled-device expected state
fDenyTSConnections : 1 / TermService : Stopped (Disabled)
After the Disable RDP policy applies, connections should fail immediately or time out.
Intune deployment status
Devices > Monitor > Device configuration: Succeeded
Delivery can take up to 8 hours; verify per-device rather than relying on the tenant summary.
Troubleshooting
The Windows Settings app shows Remote Desktop as "Disabled" even after the OMA-URI policy reports success in Intune
Warning
Cause: The OMA-URI approach for RDP has known limitations, and the Settings app often reflects misleading status information that does not update to match the registry and firewall state applied by policy.
Do not rely on the Settings app to confirm status. On the target device, verify the actual configuration by running Get-ItemProperty -Path 'HKLM:\System\CurrentControlSet\Control\Terminal Server' -Name "fDenyTSConnections" (expect 0 when enabled) and Get-NetFirewallRule -DisplayGroup "Remote Desktop" | Where-Object {$_.Enabled -eq "True"}. Deploy the PowerShell remediation script from Step 3 to enforce the registry and firewall settings where OMA-URI falls short.
The RDP configuration policy is not showing as "Succeeded" on target devices
Note
Cause: Intune configuration profiles sync on a schedule and can take up to 8 hours to report deployment status, or the device may not be in the assigned group or matched by the filter.
Confirm the device is a member of the assigned group and matches any applied filters. Track deployment under Devices > Monitor > Device configuration. To speed things up, trigger a manual sync from the device (Settings sync) or wait for the standard check-in cycle; status should show "Succeeded" within 8 hours.
RDP connection to an Entra ID joined device fails when connecting over the internet
Warning
Cause: Entra ID joined devices connecting via RDP over the internet require VPN connectivity; direct internet RDP connections fail due to certificate and name resolution issues.
Establish VPN connectivity to the target network before connecting, and use the device hostname in computername.domain.com format rather than a public IP. Authenticate with the Entra ID credential format AzureAD\user@yourdomain.com or the UPN user@yourdomain.com.
Administrators are locked out of remote systems after applying the disable RDP policy
Critical
Cause: The disable script stops and disables TermService and turns off the Remote Desktop firewall group, which removes remote access entirely - including for admins who relied on it.
Always test disable policies on non-production devices first, and confirm you have an alternative access path (such as Intune Remote Help or physical/console access) before scoping the policy broadly. To restore access, reassign the enable policy and remediation script from Steps 1-3, which sets fDenyTSConnections to 0 and re-enables the firewall group.
The PowerShell remediation script returns exit code 1 (configuration failed)
Warning
Cause: The script's verification block did not find fDenyTSConnections equal to 0 and at least one enabled Remote Desktop firewall rule, often because it ran without sufficient privileges or the firewall group name did not match.
Configure the script to run in System context with execution policy set to Bypass under Devices > Scripts. Review results in Devices > Monitor and run the verification commands manually on a target device to confirm the registry value and Get-NetFirewallRule -DisplayGroup "Remote Desktop" output before re-deploying.
Frequently asked questions
Why does the Windows Settings app still show Remote Desktop as Disabled after my Intune policy deploys?
The OMA-URI approach for RDP has known limitations, and the Settings app frequently displays misleading status, showing "Disabled" even when RDP is correctly configured. Verify the real state on the device by checking that fDenyTSConnections equals 0 and that the Remote Desktop firewall rules are enabled, rather than trusting the Settings display.
Does Microsoft Intune have a native setting to enable RDP without OMA-URI?
No. As of March 2026, Intune does not provide a direct RDP toggle in standard configuration profiles, so you must use custom OMA-URI policies combined with PowerShell remediation scripts to reliably enable or disable RDP.
How long does an Intune RDP configuration policy take to apply to devices?
Assigned configuration policies typically report as "Succeeded" on target devices within 8 hours. You can track deployment progress under Devices > Monitor > Device configuration, and a manual device sync can apply the policy sooner.
Can I connect to an Entra ID joined device over RDP from the internet?
Not directly. Entra ID joined devices reached over RDP from the internet require VPN connectivity, because direct internet connections commonly fail due to certificate and name resolution issues. Connect through a VPN using the device's hostname in computername.domain.com format.
What is the difference between using RDP and Intune Remote Help?
Traditional RDP requires firewall changes, VPN connectivity for remote access, and custom Intune configuration, whereas Intune Remote Help is a cloud-based remote assistance tool with role-based access control, session logging, and Entra ID authentication. Microsoft recommends Remote Help as the primary remote access solution for modern zero-trust environments.
How do I disable RDP with Intune without locking myself out?
Create a dedicated "Disable RDP Access" OMA-URI policy plus a PowerShell script and test it on non-production devices first before broad deployment. Keep an alternative access path such as Intune Remote Help or console access available, since the disable script stops and disables TermService and turns off the Remote Desktop firewall group.
Conclusion
You now have a complete workflow for centrally managing Remote Desktop access with Microsoft Intune. Because Intune has no native RDP toggle, you combined custom OMA-URI configuration profiles with PowerShell remediation scripts to reliably enable RDP, configured Entra ID web sign-in, tested connectivity, and created a matching policy to disable RDP cleanly. You also set up Intune Remote Help as Microsoft's recommended, more secure alternative, and established monitoring to verify compliance across your fleet.
Enable or disable RDP at scale in Intune by pairing custom OMA-URI policies with PowerShell remediation scripts, and prefer Remote Help for secure remote assistance.
Devices > Configuration > Create > New policy