How to Configure Windows Recall Snapshot Storage Duration in Microsoft Intune
Use the Microsoft Intune Settings Catalog and Windows AI policies to enforce a maximum storage duration for Windows Recall snapshots on Copilot+ PCs, ensuring data retention compliance.

- Difficulty
- Intermediate
- Time required
- 45 minutes
- Steps
- 8
- Platform
- Microsoft Intune
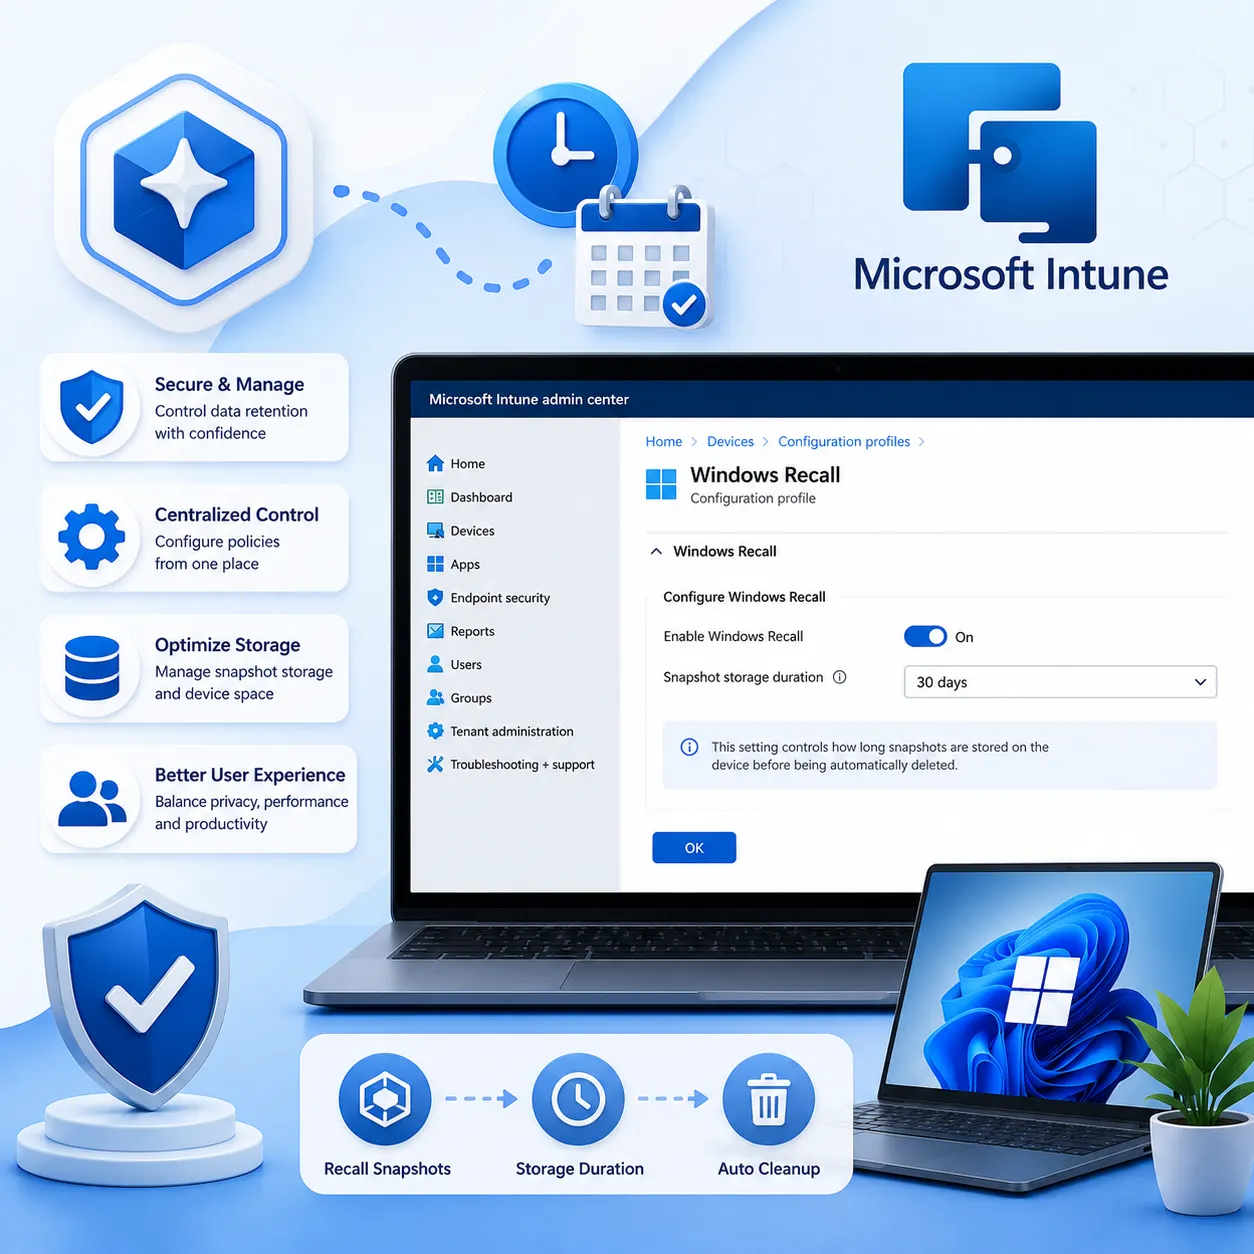
Table of contents
Quick Answer
Go to the stepsCreate a Windows Settings Catalog profile in Intune, add the Windows AI setting Set Maximum Storage Duration For Recall Snapshots, set it to your chosen retention period (for example 90 days), and assign it to a pilot group of Copilot+ PCs. After the next sync, the duration appears locked in Recall settings and old snapshots are cleaned up.
- In the Intune admin center, go to Devices > Configuration > Configuration profiles > Create > New policy.
- Choose platform Windows 10 and later and profile type Settings catalog, then name the profile.
- Add settings, search Windows AI, and select Set Maximum Storage Duration For Recall Snapshots (User) (Windows Insiders only).
- Enable the setting, choose a duration such as 90 days, and assign the profile to a pilot group.
- Create the profile, force a sync, and verify the duration is locked in Recall & snapshots settings.
Devices > Configuration > Configuration profiles > Create > New policyExpected result: The configured maximum storage duration (e.g. 90 days) appears and is locked in Windows Recall & snapshots settings on targeted devices, and the Intune profile reports Succeeded check-in status.
Key takeaways
- You will learn how to create and deploy a Microsoft Intune Settings Catalog profile that enforces a maximum storage duration for Windows Recall snapshots on Copilot+ PCs. This includes verifying the feature on a test device, selecting the correct Windows AI policy, setting a retention value, and validating enforcement.
- Without central management, users can leave Recall snapshots set to Unlimited retention, creating data-governance and privacy-compliance risks and consuming excessive disk space. Enforcing a retention limit through Intune brings Recall in line with your organization's data retention policies while keeping recent activity available to users.
- Use an Intune Settings Catalog profile with the Windows AI Recall storage duration setting to enforce a consistent snapshot retention period across your Copilot+ PCs.
Introduction
Windows Recall continuously captures snapshots of user activity to build a searchable timeline, which raises immediate questions about data retention and privacy for any organization. In an unmanaged state, each user can set their own storage duration — including Unlimited — so IT loses control over how much activity data accumulates on disk. Microsoft Intune addresses this through the Windows AI category in the Settings Catalog, where the Set Maximum Storage Duration For Recall Snapshots policies let you enforce retention limits of 30, 60, 90, or 180 days, or Unlimited. This tutorial walks through building that profile end to end: verifying the controls on a test device, choosing between the user-level and device-level variants, setting the duration value, assigning the policy to a pilot group, and confirming enforcement with MDM logs and the Settings UI. As of May 2026 these settings are marked (Windows Insiders only) and function on Windows 11 24H2 Insider builds running on NPU-enabled Copilot+ PCs, so plan validation accordingly before broad deployment.
Who this is for: This guide is for sysadmins, MSPs, and IT pros who manage Windows 11 Copilot+ PCs through Microsoft Intune and need to govern how long Recall snapshots are retained. Familiarity with the Intune admin center and Settings Catalog profiles is assumed.
Before you start
- Access
- You need administrative access to the Microsoft Intune admin center (https://intune.microsoft.com) with permission to create and assign device configuration profiles, plus access to at least one target Copilot+ PC for validation.
- Required roles
- Intune Administrator (or a custom Intune role with permission to create and assign Configuration Profiles)
- Local administrator on the test device (for Event Viewer, mdmdiagnosticstool, and forced sync validation)
- Intune Administrator
- Required licenses
- Microsoft Intune (device management) license assigned to targeted users/devices
- Microsoft Intune
- Environment
- Copilot+ PC with an NPU-enabled processor running a Windows 11 24H2 Insider build. As of May 2026 these Recall storage duration policies are marked "Windows Insiders only" and only apply on Insider builds.
- Vendor
- Microsoft
- Tested environment
- Windows 11 24H2 Insider build on Copilot+ PC with NPU
- Administrator permissions required
Based on the Intune Settings Catalog and Windows Recall behavior as of May 2026; policies are marked "Windows Insiders only" and apply to Windows 11 24H2 Insider builds on Copilot+ PCs with NPU-enabled processors.
Roughly 30-45 minutes for a pilot deployment, plus up to 24-48 hours to observe snapshot cleanup on target devices.
Warning: Users lose access to older snapshots when the policy applies
Setting a shorter maximum storage duration (for example 90 days) causes Windows to delete Recall snapshots older than that limit. Once the policy applies at device sync, those snapshots and the activity they captured cannot be recovered. Deploy to a small pilot group first and warn affected users before broad rollout.
Warning: Do not mix device-level and user-level Recall policies
Assigning both the device-level and user-level "Set Maximum Storage Duration For Recall Snapshots" settings can produce conflicting policy states and unpredictable enforcement. Choose one scope per device population unless you have a specific, tested reason to combine them.
Note: Feature is Windows Insiders only
These policies function only on Insider builds of Windows 11 24H2 on Copilot+ hardware. Devices that do not meet these requirements will report the policy as "Not applicable" in Intune rather than enforcing it.
1Verify Recall storage controls on a test device
Confirm Windows Recall and its storage duration options are available before creating policies.
Settings > Privacy & security > Recall & snapshots > StorageSign in to a Copilot+ PC running a Windows 11 24H2 Insider build (Recall storage duration policies function only on Insider builds on NPU-enabled Copilot+ PCs). Open the Recall settings directly by pasting ms-settings:privacy-recall into the Run dialog or address bar, or open Settings manually and go to Privacy & security > Recall & snapshots.
Expand the Storage section and locate Maximum storage duration for snapshots. Confirm the dropdown offers these options:
- 30 days
- 60 days
- 90 days
- 180 days
- Unlimited
If the Save snapshots toggle is off, enable it temporarily so all configuration options become visible. Record the current default value before you leave the page.
ms-settings:privacy-recallExpected result: The Recall & snapshots Storage section displays the Maximum storage duration for snapshots dropdown with the 30, 60, 90, 180-day, and Unlimited options.
Note
Recent Insider builds changed the default for new Copilot+ PCs from Unlimited to 90 days — document the actual default on your test device, since it affects what users experience before any policy applies. If the Storage section or duration options are missing, the build does not yet include the feature and the Intune policy will report Not applicable.
2Create a Settings Catalog configuration profile in Intune
Start a new Windows Settings Catalog profile scoped for Recall policies.
Devices > Configuration > Configuration profiles > Create > New policyOpen a browser, go to https://intune.microsoft.com, and sign in with an administrative account. Navigate to Devices > Configuration > Configuration profiles > Create > New policy.
On the Create a profile pane, set:
- Platform: Windows 10 and later
- Profile type: Settings catalog
Click Create. On the Basics tab, enter a descriptive name and description, for example:
- Name: Windows Recall - Max Snapshot Duration (90 days)
- Description: Configure maximum storage duration for Windows Recall snapshots via Windows AI settings. Enforces 90-day retention for privacy and disk management.
Click Next to continue.
Expected result: A new profile wizard opens showing Platform "Windows 10 and later" and Profile type "Settings catalog", with your name and description saved on the Basics tab.
Note
The Settings catalog profile type is required — the Windows AI Recall settings are not available in the older templated device configuration profiles. Use a naming convention that includes the enforced duration so the profile's intent is obvious in the profiles list.
3Add the Windows AI Recall storage duration setting
Select the correct Windows AI policy for snapshot retention.
Devices > Configuration > Configuration profiles > (profile) > Configuration settings > + Add settingsOn the Configuration settings page, click + Add settings to open the settings picker. In the search box type:
Windows AI
Expand the Windows AI category. Several Recall-related policies appear, each labeled (Windows Insiders only), including:
- Set Maximum Storage Duration For Recall Snapshots (User) (Windows Insiders only)
- Set Maximum Storage Duration For Recall Snapshots (Windows Insiders only)
- Set Maximum Storage Space For Recall Snapshots (User) (Windows Insiders only)
Select the checkbox for Set Maximum Storage Duration For Recall Snapshots (User) (Windows Insiders only) to apply the policy at user scope, which suits shared devices where users may need different retention. Click the X to close the settings picker.
Windows AIExpected result: The selected Windows AI setting "Set Maximum Storage Duration For Recall Snapshots (User)" appears in the Configuration settings list.
Note
The (User) variant applies per user on shared devices; the setting without "(User)" applies at the device level for all users. Choose one scope to match your deployment model — mixing both can cause conflicts (see the next step).
4Set the storage duration value
Configure and enable the specific retention period to enforce.
Devices > Configuration > Configuration profiles > (profile) > Configuration settingsOn the Configuration settings page, find the Set Maximum Storage Duration For Recall Snapshots (User) entry you just added.
- Set the setting toggle to Enabled.
- In the Maximum storage duration dropdown, select the retention period you want to enforce — 30, 60, 90, 180 days, or Unlimited.
For this example, select 90 days to align with a common data retention policy.
Optionally, to also cap disk usage, add Set Maximum Storage Space For Recall Snapshots (User) and set an appropriate size limit (typically 25–50 GB). Click Next when done.
Expected result: The setting shows Enabled status and displays your chosen duration (for example, 90 days) in the configuration summary.
Note
Do not configure conflicting device-level and user-level duration policies for the same devices — mixed scopes can produce unpredictable enforcement. Pick a single scope unless you have a specific, tested requirement for both.
6Review and deploy the profile
Validate all settings and push the policy to devices.
Devices > Configuration > Configuration profiles > (profile) > Review + createOn the Review + create page, confirm every detail:
- Platform: Windows 10 and later
- Profile type: Settings catalog
- Category: Windows AI
- Setting: Set Maximum Storage Duration For Recall Snapshots (User) = 90 days
- Assigned groups: your pilot or production group
Click Create to deploy the profile. To track delivery, go to Devices > Configuration > Configuration profiles, open the new profile, and review the Device and user check-in status section.
The policy reaches devices at their next Intune sync, typically within 15–60 minutes. To force a sync on a test device, use the Company Portal app (Settings > Sync) or run the scheduled task command below.
Get-ScheduledTask | Where-Object {$_.TaskName -eq "PushLaunch"} | Start-ScheduledTaskExpected result: The profile is created and appears in the profiles list, and the check-in status begins reporting device results with no error messages.
Note
Policy changes take effect immediately on sync — once applied, users lose access to snapshots older than the configured duration. The PushLaunch scheduled task triggers an MDM sync on the local device; run it on the test machine, not the admin console.
7Validate policy application on target devices
Confirm the retention setting is enforced on managed devices.
Settings > Privacy & security > Recall & snapshots > StorageOn a device that has completed its sync, open Settings > Privacy & security > Recall & snapshots, expand Storage, and check Maximum storage duration for snapshots. It should now show your configured value (90 days) and typically appears grayed out or locked, indicating policy enforcement.
For technical validation, open Event Viewer with eventvwr.msc and browse to Applications and Services Logs > Microsoft > Windows > DeviceManagement-Enterprise-Diagnostics-Provider, looking for events indicating Windows AI CSP policy processing.
To capture a full diagnostic report, run the mdmdiagnosticstool command below from an elevated prompt and review the resulting CAB for Windows AI or Recall policy errors.
mdmdiagnosticstool.exe -area DeviceEnrollment;DeviceConfiguration -cab c:\temp\MDMLogs.cabExpected result: The Maximum storage duration setting shows the configured value and is locked, and MDM logs show successful Windows AI policy processing.
Note
The c:\temp\MDMLogs.cab path is a placeholder — ensure the target folder exists and run the tool as Administrator. Existing snapshots older than the new limit may take up to 24–48 hours to be cleaned up, even though new snapshots follow the policy immediately.
8Monitor compliance and troubleshoot issues
Establish ongoing monitoring and resolve common errors.
Devices > Configuration > Configuration profiles > (profile) > Device and user check-in statusIn the Intune admin center, go to Devices > Configuration > Configuration profiles, open your Recall policy, and review the Device and user check-in status. Track these result categories:
- Succeeded — policy applied correctly.
- Error — application failed; open the device to inspect the error detail.
- Conflict — another policy (often a mixed user/device scope) targets the same setting; consolidate to one scope.
- Not applicable — the device does not support the feature (non-Copilot+ hardware or a non-Insider build).
For Error or Conflict devices, cross-check the MDM logs from the previous step and confirm the device meets the Insider-build and NPU-enabled Copilot+ PC requirements before re-syncing.
Expected result: The check-in status report lists devices under Succeeded, with any Error, Conflict, or Not applicable entries clearly identified for follow-up.
Note
Because these policies are still marked Windows Insiders only, expect Not applicable results on production (non-Insider) builds and non-Copilot+ hardware — this is expected, not a failure. Re-evaluate the policy scope as the feature moves out of Insider status in future Windows releases.
Confirming the Recall Storage Duration Policy Is Enforced
Confirm configuration
A successful configuration is more than a profile that says "Create" completed — it means the retention limit is actually locked on the endpoint. Verify success on two layers: the Intune admin center (deployment and check-in status) and the target device (the enforced setting plus MDM logs).
In Intune, open the profile under Devices > Configuration > Configuration profiles and review the Device and user check-in status. Each targeted device should progress to Succeeded after its next sync (typically 15–60 minutes, or immediately after a forced sync). On the device, open Settings > Privacy & security > Recall & snapshots, expand Storage, and confirm Maximum storage duration for snapshots shows the value you set (for example 90 days) and appears grayed out / locked, indicating it is managed rather than user-editable.
Remember the timing distinction: the retention limit applies to new snapshots immediately, but existing snapshots older than the limit may take up to roughly 24 hours to be cleaned up. So a device can report Succeeded while old snapshots are still being removed — that is expected, not a failure.
Normal result: The profile reports Succeeded in the Intune check-in status for targeted, supported devices; on the device the Maximum storage duration setting shows your configured value and is locked; and DeviceManagement-Enterprise-Diagnostics-Provider events show the Windows AI CSP policy applied without errors.
Abnormal result: The profile shows Error, Conflict, or Not applicable. Not applicable usually means the device is not a Copilot+ PC on a supported Windows 11 24H2 Insider build. Conflict typically means a device-level and user-level Recall policy (or a second profile) target the same device — remove the overlap. Error warrants collecting an MDM diagnostic report (mdmdiagnosticstool) to inspect Windows AI policy processing.
Intune check-in status (healthy)
Succeeded: 8 | Error: 0 | Conflict: 0 | Not applicable: 2
Two devices report Not applicable because they are not Copilot+ / not on a supported Insider build; the eight supported pilot devices applied the policy successfully.
Enforced device setting
Maximum storage duration for snapshots = 90 days (locked)
Shown under Settings > Privacy & security > Recall & snapshots > Storage, grayed out to indicate management by Intune.
MDM diagnostic collection
mdmdiagnosticstool.exe -area DeviceEnrollment;DeviceConfiguration -cab c:\temp\MDMLogs.cab
Run as Administrator on the device; extract the CAB and review for Windows AI / Recall policy application errors when troubleshooting an Error state.
Conflict signal
Conflict: 1
Indicates both a user-level and device-level Recall storage duration setting (or a duplicate profile) target the same device — resolve by keeping a single scope.
Troubleshooting
Policy shows "Not applicable" for targeted devices in the Intune check-in status
Warning
Cause: The device does not meet the feature requirements — Recall storage duration policies apply only to Copilot+ PCs with NPU-enabled processors running a Windows 11 24H2 Insider build. Standard hardware or non-Insider builds cannot process the Windows AI CSP setting.
Confirm the device is a Copilot+ PC with an NPU and is enrolled on a supported Windows 11 24H2 Insider build. On the device, open Privacy & security > Recall & snapshots and verify the storage duration options exist. Remove non-eligible devices from the assignment group so they do not clutter compliance reporting.
Policy check-in status returns "Conflict" on some devices
Critical
Cause: Both the user-level and device-level Recall storage duration settings are assigned to the same device with different values, so Windows cannot determine which retention period to enforce.
Pick a single scope for the policy. Edit the conflicting profiles so that only the Set Maximum Storage Duration For Recall Snapshots (User) setting or the device-level variant targets the device — not both. Re-sync the device and confirm the status changes to Succeeded.
The duration setting in Windows Settings is not locked or still shows the old value after sync
Warning
Cause: The device has not completed its Intune sync cycle, or the CSP policy has not finished processing.
Force a sync from the Company Portal app via Settings > Sync, or run the PushLaunch scheduled task in PowerShell: Get-ScheduledTask | Where-Object {$_.TaskName -eq "PushLaunch"} | Start-ScheduledTask. Wait 15-60 minutes, then recheck Privacy & security > Recall & snapshots.
Old Recall snapshots are still present after a shorter retention policy applies
Note
Cause: The retention policy governs new snapshots immediately, but cleanup of existing snapshots runs on a scheduled background process rather than instantly.
Allow up to 24-48 hours for the cleanup process to remove snapshots older than the configured duration. Verify progress by reopening the Recall storage settings and confirming that older entries have been deleted. Do not repeatedly re-deploy the policy expecting instant deletion.
The Windows AI settings do not appear in the Settings picker search results
Warning
Cause: You are searching in a traditional device configuration profile instead of a Settings catalog profile, or the tenant's Settings Catalog has not surfaced the Windows AI category.
Ensure the profile was created with Profile type: Settings catalog (not a template-based device configuration profile). Reopen the settings picker, search for Windows AI, and expand the category to reveal the Recall settings marked (Windows Insiders only).
Frequently asked questions
What Windows editions and hardware are required for Recall storage duration policies to apply?
As of May 2026 these policies apply only to Copilot+ PCs with NPU-enabled processors running a Windows 11 24H2 Insider build, and the settings are marked "Windows Insiders only." Devices that lack an NPU or run a non-Insider build will report the policy as Not applicable in Intune.
What is the difference between the user-level and device-level Recall storage duration settings?
The user-level setting (Set Maximum Storage Duration For Recall Snapshots (User)) applies per user, which is ideal for shared devices where different users may need different retention periods. The device-level variant enforces one duration uniformly for all users on the device. Applying both to the same device can cause a policy conflict.
Why does my Recall storage duration policy show as Not applicable in Intune?
"Not applicable" means the targeted device does not support the feature — typically because it is not a Copilot+ PC with an NPU, or it is not running a supported Windows 11 24H2 Insider build. Only eligible hardware and OS builds can process the Windows AI CSP setting.
What happens to existing Recall snapshots when a shorter retention policy is applied?
New snapshots follow the new duration immediately, but existing snapshots older than the configured limit are removed by a background cleanup process that can take up to 24-48 hours to run. Users will lose access to snapshots older than the enforced duration once cleanup completes.
How long does it take for the Recall storage duration policy to take effect on a device?
The policy is delivered during the device's next Intune sync cycle, typically within 15-60 minutes. You can force an immediate sync from the Company Portal app under Settings > Sync or by starting the PushLaunch scheduled task in PowerShell.
Can I still manage Recall storage duration if the policies are marked Windows Insiders only?
Yes, but only on Copilot+ PCs running supported Windows 11 24H2 Insider builds — the policies function correctly only in that context as of May 2026. On production (non-Insider) builds the settings will not be enforced, so treat these configurations as pilot deployments until the feature reaches general availability.
Conclusion
You verified that Windows Recall storage duration controls are available on a Copilot+ test device, created a Windows 10 and later Settings Catalog profile in Intune, added the Set Maximum Storage Duration For Recall Snapshots (User) Windows AI setting, chose a retention value such as 90 days, assigned it to a pilot group, and deployed it. You then validated enforcement in Windows Settings and through MDM diagnostics, and set up ongoing monitoring of the check-in status. This gives you centralized, policy-driven control over how long Recall snapshots are retained across your managed fleet.
Use an Intune Settings Catalog profile with the Windows AI Recall storage duration setting to enforce a consistent snapshot retention period across your Copilot+ PCs.
Devices > Configuration > Configuration profiles > Create > New policy