How to Sign RDP Files with rdpsign for Secure Remote Desktop Services
Learn how to digitally sign RDP files with rdpsign.exe to remove the Unknown Publisher warning in Remote Desktop Services. Covers certificate thumbprints, manual and automated RDS signing, and deploying trusted publisher thumbprints via Group Policy.

- Difficulty
- Advanced
- Time required
- 15 minutes
- Steps
- 5
- Platform
- Remote Desktop Services
- Last tested
- July 19, 2026
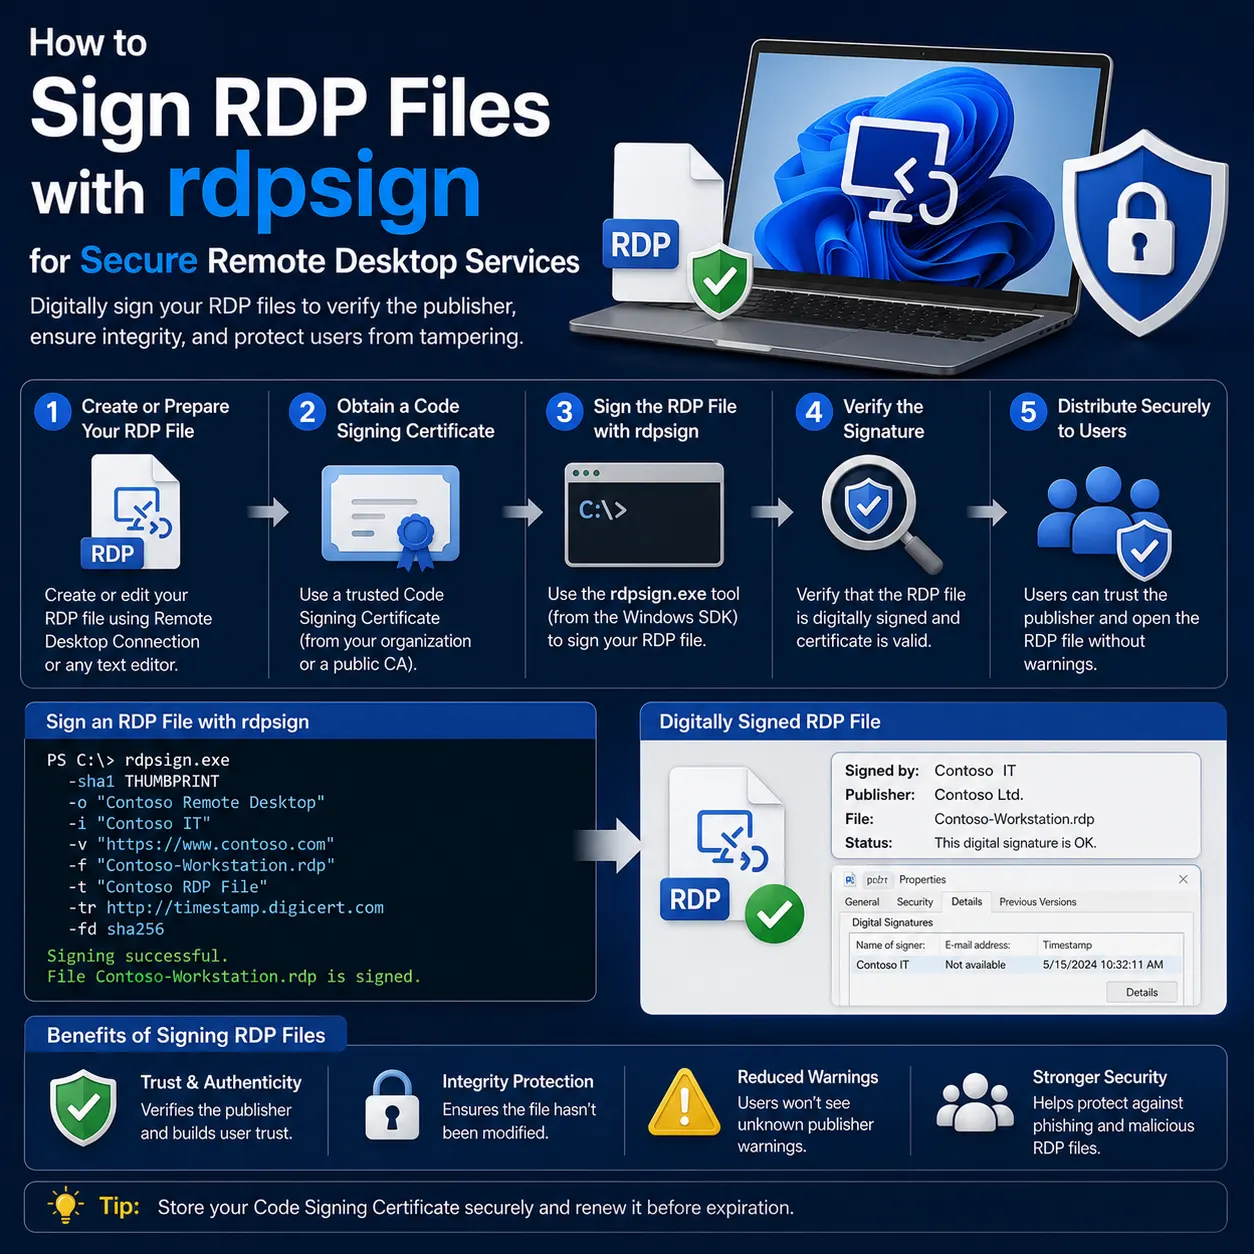
Table of contents
Quick Answer
Go to the stepsGet the signing certificate's thumbprint from the Certificates snap-in and remove all spaces. Run rdpsign /sha256 <thumbprint> file.rdp from an elevated command prompt to sign the file. Deploy the thumbprint to clients via the 'trusted .rdp publishers' Group Policy so they skip the warning.
- Obtain the signing certificate's thumbprint from the Certificates snap-in.
- Remove all spaces from the thumbprint.
- Run rdpsign /sha256 <thumbprint> file.rdp (use /l to test first).
- Deploy the thumbprint via the 'trusted .rdp publishers' Group Policy.
- Test opening the RDP file on a managed device.
Command prompt (admin) in the folder containing the RDP filerdpsign /sha256 82bf48cf5be3f8a2275d3c1b7cba18e501802eb3 file1.rdpExpected result: The RDP file is signed. Users on devices that trust the certificate open it without the Unknown Publisher warning.
Key takeaways
- You'll learn how to digitally sign RDP files with rdpsign.exe and configure Group Policy so users no longer see the Unknown Publisher warning.
- Unsigned RDP files trigger a security warning that users learn to ignore, weakening security awareness. Per Microsoft Learn, signing RDP files with a trusted certificate removes the warning and confirms authenticity.
- Sign RDP files with rdpsign.exe using the certificate thumbprint, then deploy the trusted publisher thumbprint via Group Policy to suppress the Unknown Publisher warning.
Introduction
When users open an RDP file, Windows shows a security warning if the file isn't digitally signed by a trusted publisher. Per Microsoft Learn, this 'Unknown Publisher' warning trains users to click through security prompts, which is a bad habit.
Digitally signing RDP files with a trusted certificate removes the warning. Per Microsoft, the rdpsign.exe tool signs individual files using a certificate's thumbprint, making it ideal for manually distributed files. For Remote Desktop Services, the RDPublishing role certificate automatically signs all published RemoteApp and desktop connections.
This tutorial covers manual signing with rdpsign.exe, automated RDS signing, and deploying the trusted publisher thumbprint via Group Policy so managed devices skip the warning entirely.
Who this is for: Windows Server and RDS administrators distributing RDP connection files to users.
Before you start
- Access
- Windows Server or client with rdpsign.exe. A code-signing certificate with an accessible private key. Group Policy access for deployment.
- Required roles
- Local administrator
- Domain administrator (for Group Policy)
- Domain administrator (for GPO)
- Environment
- Windows Server or Windows 10/11. Certificate installed in the local computer or personal certificate store.
- Vendor
- Microsoft
- Last tested
- Administrator permissions required
- Backup required
15 minutes
Warning: Thumbprint must have no spaces or hidden characters
Per Microsoft Q&A, the thumbprint must contain no spaces and no hidden Unicode characters (like the invisible LTR mark copied from MMC). Strip all spaces before use.
Note: backup the original RDP file
Per Microsoft Learn, rdpsign overwrites the input RDP file with the signed version. Keep a backup copy of the unsigned file before signing.
1Get the Certificate Thumbprint
Obtain the signing certificate's thumbprint.
Run > certlm.msc (local computer) or certmgr.msc (personal)Open the Certificates snap-in: run certlm.msc for the local computer store or certmgr.msc for your personal store. Navigate to the certificate you want to use for signing (it must be a code-signing or digital-signature certificate with an accessible private key).
Double-click the certificate, go to the Details tab, and select Thumbprint in the Field list. Copy the value shown.
Expected result: The certificate's Details tab shows the Thumbprint value.
Note
The certificate must have an accessible private key. If you see only the public key, signing will fail with error 0x80090016.
2Clean the Thumbprint
Clean the thumbprint for use with rdpsign.
Paste the thumbprint into a plain text editor. Per Microsoft Q&A:
- Remove all spaces between the hex pairs.
- Check the first character isn't a hidden question mark or Unicode mark (the invisible LTR character copied from MMC). Delete it if present.
- Lowercase is safest.
The result should be a continuous 40-character (SHA1) hex string.
Expected result: A clean thumbprint string with no spaces, e.g., 82bf48cf5be3f8a2275d3c1b7cba18e501802eb3.
Note
Hidden Unicode characters from copying in MMC are a common cause of silent validation failures. Retyping the thumbprint manually avoids this.
3Test Signing with the /l Flag
Test signing before modifying the file.
Open an elevated Command Prompt. Navigate to the folder containing the RDP file. Run rdpsign in test mode (/l) first:
rdpsign /l /sha256 82bf48cf5be3f8a2275d3c1b7cba18e501802eb3 file1.rdpPer Microsoft Q&A, use /sha256 for rdpsign v10+ (Windows 10/Server 2016 and later), even with a SHA-1 certificate. The /l flag tests without modifying the file.
rdpsign /l /sha256 82bf48cf5be3f8a2275d3c1b7cba18e501802eb3 file1.rdpExpected result: Test mode reports whether signing will succeed. No file is modified.
Note
The RDP file name must have no spaces and be the full file name. Wildcards are not accepted.
4Sign the RDP File
Sign the RDP file.
Once the test succeeds, sign the file for real by removing the /l flag:
rdpsign /sha256 82bf48cf5be3f8a2275d3c1b7cba18e501802eb3 file1.rdpPer Microsoft Learn, the signed output overwrites the input file. Keep a backup of the unsigned original. Use /q for quiet mode or /v for verbose output.
rdpsign /sha256 82bf48cf5be3f8a2275d3c1b7cba18e501802eb3 file1.rdpExpected result: The RDP file is signed. rdpsign reports success. The signed file overwrites the original.
Note
If you get error 0x80090016, the certificate's private key isn't accessible. Verify the private key is present in the certificate store.
5Deploy the Trusted Publisher Thumbprint via GPO
Deploy the trusted publisher thumbprint to clients.
GPMC > Computer Configuration > Administrative Templates > Windows Components > Remote Desktop Services > Remote Desktop Connection ClientIn the Group Policy Management Console, edit a GPO targeting your client devices. Navigate to:
Computer Configuration > Administrative Templates > Windows Components > Remote Desktop Services > Remote Desktop Connection Client
Open Specify SHA1 thumbprints of certificates representing trusted .rdp publishers. Set it to Enabled and enter the cleaned thumbprint. Click OK.
Expected result: The thumbprint is deployed to client devices, which now trust the signed RDP files.
Note
Per Microsoft, the client only skips the warning for certificates it trusts. The certificate's root CA must also be trusted on the endpoints. Run gpupdate /force on clients to apply.
Verify the RDP File Is Signed and Trusted
Verify fix
After signing, the RDP file contains a digital signature block. When a user on a device that trusts the signing certificate opens the file, Windows no longer shows the Unknown Publisher warning.
Per Microsoft Learn, the client only skips the warning if it trusts the signing certificate. Deploy the certificate's thumbprint to client devices via the 'trusted .rdp publishers' Group Policy. The certificate's root CA must also be trusted on the endpoints.
To verify a file is signed, check its properties or run rdpsign /l (test mode). If signing fails with error 0x80090016, the certificate's private key isn't accessible.
Normal result: The RDP file is signed. On trusting devices, it opens without the Unknown Publisher warning.
Abnormal result: Error 0x80090016 (private key not found) or the warning still appears. Check the certificate has a private key and the thumbprint is correct.
Signed and trusted
RDP opens with no publisher warning
The RDP file is signed and trusted.
Signing failed
Error Code: 0x80090016
The certificate lacks an accessible private key.
Troubleshooting
Error 0x80090016: The RDP file could not be signed
Warning
Cause: The certificate's private key isn't accessible in the certificate store.
Verify the certificate has an associated private key (a key icon appears in the Certificates snap-in). If the key is in Azure Key Vault HSM, rdpsign can't export it; use a certificate with a locally accessible private key.
rdpsign reports certificate not found
Warning
Cause: The thumbprint contains spaces or hidden Unicode characters copied from MMC.
Per Microsoft Q&A, remove all spaces and check for a hidden question mark or LTR mark at the start of the thumbprint. Retype the thumbprint manually to eliminate invisible characters.
Signed file still shows Unknown Publisher warning
Warning
Cause: The client doesn't trust the signing certificate, or the thumbprint wasn't deployed via Group Policy.
Deploy the certificate thumbprint via the 'trusted .rdp publishers' Group Policy. Ensure the certificate's root CA is trusted on the client. Run gpupdate /force and test again.
RDP file won't sign on Windows 10/Server 2016+
Note
Cause: Using /sha1 with rdpsign v10+ which requires /sha256.
Per Microsoft Q&A, use the /sha256 parameter for rdpsign v10 or greater, even when using a SHA-1 certificate thumbprint.
Frequently asked questions
Why do I see 'Unknown Publisher' when opening an RDP file?
The RDP file isn't digitally signed, or the signing certificate isn't trusted by the client. Signing the file with a trusted certificate and deploying its thumbprint via Group Policy removes the warning.
Should I use /sha1 or /sha256?
Per Microsoft Q&A, for rdpsign.exe v10 or greater (Windows 10/Server 2016+), use the /sha256 parameter even with a SHA-1 certificate thumbprint. Older versions used /sha1.
How do I find the certificate thumbprint?
Open the Certificates snap-in (certmgr.msc or certlm.msc), double-click the certificate, go to the Details tab, and click Thumbprint. Copy the value and remove all spaces.
Can RDS sign RemoteApp files automatically?
Per Microsoft Learn, in RDS the certificate associated with the RDPublishing role automatically signs all RemoteApp programs and desktop connections. Use Set-RDCertificate to assign a chained certificate.
What kind of certificate do I need?
The certificate must be a code-signing or digital-signature certificate with an accessible private key, and its root CA must be trusted on the client endpoints.
Conclusion
Signing RDP files removes the Unknown Publisher warning users see when opening a connection. Per Microsoft Learn, use rdpsign.exe with the certificate's thumbprint (spaces removed) to sign individual files.
For RDS deployments, the RDPublishing role certificate automatically signs all published RemoteApp and desktop connections. Deploy the signing certificate's thumbprint to client devices via the 'trusted .rdp publishers' Group Policy so managed devices skip the warning.
Sign RDP files with rdpsign.exe using the certificate thumbprint, then deploy the trusted publisher thumbprint via Group Policy to suppress the Unknown Publisher warning.
rdpsign /sha256 <thumbprint> file.rdp