What is API? Definition, How It Works & Use Cases

- Level
- Beginner
- Reading time
- 21 min
- Concept
- API (Application Programming Interface)
- Last reviewed
- July 5, 2026
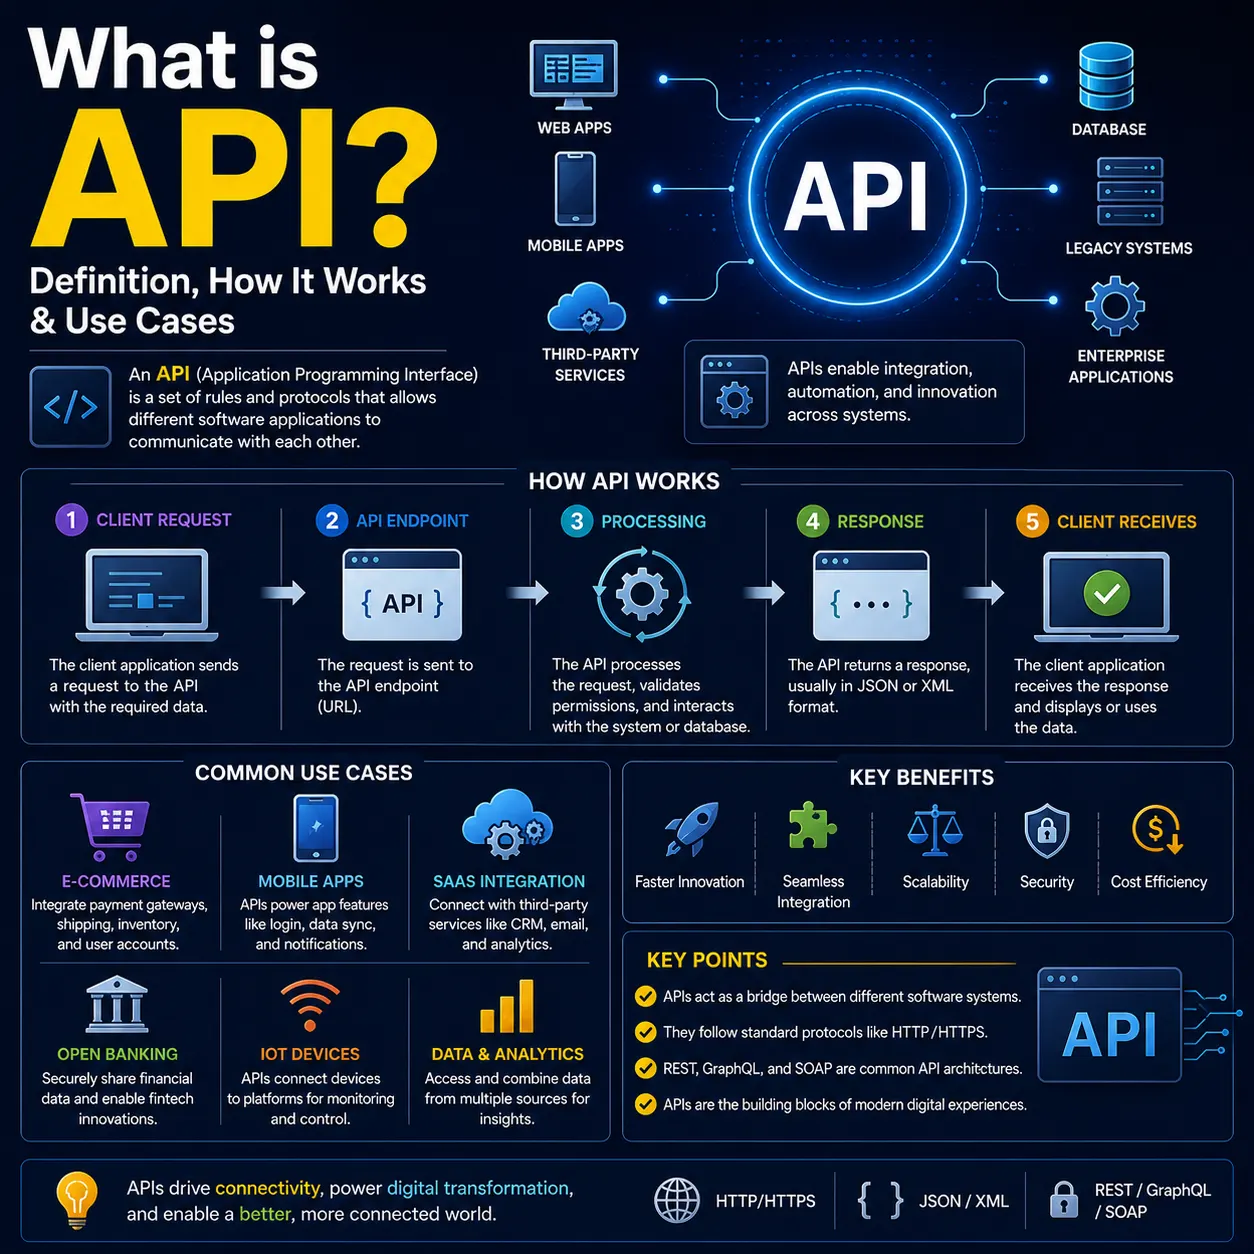
Table of contents
You order food, pay with a card, and track the delivery on a map - all inside one app that its makers never built end to end. Underneath, that app is stitching together other companies' services through APIs. An API is the contract that lets one piece of software ask another for data or an action without knowing how it works inside. It's one of the most fundamental ideas in software, and also one of the most misunderstood: people equate 'API' with a REST endpoint on the web, when APIs actually span libraries, operating systems, and several web styles. This explainer defines the concept precisely, shows how web APIs communicate, and maps the main types so the differences stop blurring together.
Key takeaways
- An API is a contract defining how software components interact, hiding each system's internal implementation.
- Not every API is a web API - libraries, operating systems, and hardware expose APIs too.
- REST is the dominant web-API style, but SOAP, GraphQL, and gRPC are all APIs with different trade-offs.
- Web APIs work through a request-response cycle over HTTP, usually exchanging JSON with status codes.
- APIs are secured with keys, OAuth, or tokens, and managed with gateways, rate limits, versioning, and OpenAPI docs.
Quick explanation
In simple terms
An API is like a waiter: you give it a request in an agreed format, it deals with the kitchen you can't see, and it brings back exactly what you asked for.
Technical definition
A defined interface contract specifying available operations, their parameters, and their return values - implemented as in-process library/OS calls or as network calls over HTTP using styles such as REST, GraphQL, SOAP, or gRPC, commonly serialized as JSON and secured via API keys or OAuth.
Analogy
A wall power socket is an API: a standard interface with a fixed contract (voltage, plug shape). Any compliant appliance can use it without knowing anything about the power station behind it - and the station can change without breaking your appliance.
Definition
An API is a defined set of rules - a contract - that lets one piece of software request data or actions from another without needing to know how it works internally. It specifies the operations available, the inputs they take, and the outputs they return.
An API (Application Programming Interface) is a contract that defines how software components interact. It exposes a set of operations, the inputs each expects, and the outputs each returns, so one program can use another's functionality without knowing its internal workings. That abstraction - hiding the implementation behind a stable interface - is the core idea.
A common misconception is that 'API' means a *web* API. In fact APIs exist at many levels: a library or framework API is the set of functions your code calls (for example, a Python library's methods); an operating-system API lets programs use OS features; a hardware API exposes device capabilities. Web APIs - the kind reached over HTTP across a network - are just the most visible modern case.
Within web APIs there are several architectural styles: REST (the dominant, resource- and HTTP-based style), GraphQL (a query language for flexible data fetching), SOAP (an older, contract-heavy XML protocol still common in enterprise and finance), and gRPC (a high-performance binary protocol for service-to-service calls). Keeping these distinctions straight is what separates understanding APIs from understanding one API style.
Why it matters
Core concepts
An API is a contract
An API defines what operations are available, what inputs they need, and what outputs they return - a stable agreement between components.
The essence of an API is abstraction through a contract. The consumer codes against the interface, not the implementation, so the provider can change internals freely as long as the contract holds. This is what makes software composable: you can rely on another system's capability without understanding - or being coupled to - how it does the work.
Example
A payment API exposes 'create a charge' with defined inputs and outputs; you never touch the provider's banking internals.
Why it matters — The contract is the whole value: it decouples consumer and provider so each can evolve independently.
Not all APIs are web APIs
APIs exist at many levels, not only as HTTP endpoints on the internet.
A library or framework API is the set of functions and classes your code calls in-process. An operating-system API lets programs use OS features like files and networking. A hardware/driver API exposes device capabilities. A web API is reached over a network via HTTP. They share the same idea - a defined interface - but only web APIs involve requests over the network. Equating 'API' with 'REST endpoint' is the most common conceptual error.
Example
Calling list.sort() in your language's standard library uses a library API; calling GET /users over HTTP uses a web API.
Why it matters — Understanding the broader definition prevents design mistakes, like adding a network hop where an in-process call would do.
Web API styles: REST, SOAP, GraphQL, gRPC
Web APIs can be built in several architectural styles, each with different trade-offs.
REST is the dominant style: resource-based, stateless, and built on standard HTTP methods, with great caching and tooling. SOAP is an older, strict XML protocol with strong contracts and built-in standards, still common in enterprise and finance. GraphQL is a query language exposing a single endpoint where clients request exactly the fields they need, avoiding over- and under-fetching. gRPC uses a compact binary format over HTTP/2 for high-performance service-to-service calls. WebSocket adds a persistent, two-way channel for real-time data.
Example
A public data service might use REST; a bank's legacy integration might use SOAP; a mobile app with variable data needs might use GraphQL; internal microservices might use gRPC.
Why it matters — Choosing the style to match the use case affects performance, caching, developer experience, and cost.
The request-response cycle
Web APIs communicate through a structured exchange of requests and responses over HTTP.
A client sends a request to an endpoint using an HTTP method - GET (read), POST (create), PUT/PATCH (update), DELETE (remove) - with headers, parameters, and sometimes a body. The server returns a response with a status code (200 OK, 201 Created, 400 Bad Request, 401/403 auth errors, 404 Not Found, 429 Too Many Requests, 500 Server Error) and a body, usually JSON. This predictable structure is why HTTP methods and status codes are worth learning once and reusing everywhere.
Example
GET /weather?city=Geneva returns 200 with a JSON body of current conditions.
Why it matters — The method-plus-status-code convention makes REST APIs consistent and self-describing across services.
API management, versioning, and webhooks
Running APIs at scale adds gateways, rate limits, versioning, documentation, and event-driven callbacks.
An API gateway centralizes authentication, rate limiting, routing, and monitoring. Versioning lets an API evolve without breaking existing consumers. OpenAPI (formerly Swagger) provides a machine-readable description that powers docs, client generation, and testing. Webhooks invert the model: instead of the client polling, the server pushes an HTTP call to the client when an event occurs - an efficient, event-driven complement to request-response APIs.
Example
A payment provider fires a webhook to your endpoint the moment a charge succeeds, instead of you polling for status.
Why it matters — These practices are what turn a working endpoint into a reliable, maintainable, secure API product.
How it works
The client sends a request
A client application calls an API endpoint with an HTTP method (GET, POST, PUT, DELETE), plus headers, parameters, and sometimes a body carrying data.
Client → Endpoint
Example — An app sends POST /charges with the amount and a payment token.
The server authenticates and authorizes
The API verifies the caller's identity (API key, OAuth token, or certificate) and checks whether it's permitted to perform the requested operation.
Auth check
Example — A bearer token is validated and its scopes checked before the request proceeds.
The server processes the request
The API executes the business logic - querying databases, calling other services, or performing calculations - to fulfill the request.
Process
Example — The service creates the charge record and calls the downstream banking system.
The server returns a response
The result is formatted, typically as JSON, with an HTTP status code indicating success or the type of error.
Response (JSON + status)
Example — The API returns 201 Created with the new charge's details.
The client uses the response - or gets a webhook
The client processes the returned data. For events it can't wait on, the server may instead push a webhook to the client when something happens later.
Use response / webhook callback
Example — The app shows a success screen, and a later webhook confirms the settled payment.
Use cases
Integrating third-party services
Developers / product teamsApps embed external capabilities - payments, maps, messaging, identity - through their providers' APIs instead of building them.
An e-commerce site uses a payment API so it never handles raw card data itself.
Benefit — Ship complex features quickly and offload specialized concerns.
Microservices communication
Architects / platform teamsApplications split into independent services that talk over well-defined APIs, enabling separate development, deployment, and scaling.
Separate user, inventory, payment, and notification services coordinated via APIs.
Benefit — Independent scaling and faster, isolated releases.
Cloud automation and infrastructure as code
DevOps / cloud engineersCloud platforms expose every service through APIs, so provisioning and configuration can be automated in code.
Scripts and IaC tools provision servers and networking via provider APIs.
Benefit — Repeatable, automated infrastructure and DevOps workflows.
Data access and open data
Data teams / integratorsOrganizations publish APIs to share datasets and functionality with controlled, authorized access.
A weather service or government portal offering a public data API.
Benefit — Controlled data sharing without exposing databases directly.
AI and agent tool use
AI / integration teamsAI applications call APIs to retrieve data and take actions, and increasingly are significant API consumers themselves.
An assistant calling a calendar or search API as a 'tool' to complete a task.
Benefit — Extends AI systems with real, live capabilities and data.
Benefits
Modularity and reuse
APIs let teams build on existing capabilities instead of rebuilding them, promoting modular design.
Reusing one internal auth API across every product.
Faster development
Leveraging existing APIs lets teams focus on their core logic rather than commodity functionality.
Adding maps or payments in days, not months.
Integration across technology stacks
A stable contract lets systems built on different languages and platforms interoperate.
A Python service and a .NET service exchanging JSON over REST.
Ecosystem and innovation
Public APIs let third parties build complementary products, extending a platform's reach.
A marketplace of integrations built on an open API.
Maintainability through decoupling
Providers can change internals without breaking consumers as long as the contract holds.
Rewriting a service's backend while keeping the same API.
Limitations
Dependency risk
HighRelying on external APIs creates points of failure if a provider has an outage, changes terms, or deprecates an endpoint.
Workaround — Design for graceful degradation, cache where possible, and monitor provider status and deprecation notices.
Security exposure
HighAPIs expose data and actions and are prime attack targets; broken authorization dominates the OWASP API Security Top 10.
Workaround — Enforce strong authentication and per-object authorization, validate inputs, rate-limit, and monitor for abuse.
Performance overhead
MediumNetwork calls and serialization add latency compared with in-process function calls.
Workaround — Batch requests, cache responses, use efficient formats (e.g. gRPC) for chatty service-to-service calls.
Versioning complexity
MediumEvolving an API without breaking existing consumers requires disciplined versioning and deprecation.
Workaround — Use clear versioning, maintain backward compatibility, and give consumers migration time and notice.
Rate limits and cost
MediumThird-party APIs impose usage limits and pricing tiers that can constrain functionality or raise costs.
Workaround — Design within quotas, cache aggressively, and model API costs into the product's economics.
Documentation dependency
LowPoor or outdated documentation slows integration and causes errors.
Workaround — Maintain accurate OpenAPI-driven docs with examples; treat docs as part of the product.
Architecture
A web API sits between a client and a provider's systems. Requests reach an endpoint, usually through an API gateway that handles authentication, rate limiting, and routing. The service applies business logic, exchanges a serialized format (typically JSON), and returns a response with a status code. An OpenAPI specification describes the contract, and webhooks provide an event-driven path back to clients.
Client
The application that consumes the API by sending requests.
A mobile app, web frontend, or another service.
Endpoint / API server
The addressable operation and the service that fulfills it.
GET /users/{id} served by a user service.
API gateway
Centralizes auth, rate limiting, routing, and monitoring across APIs.
A gateway enforcing 1,000 requests/min per key.
Authentication layer
Verifies identity and enforces authorization.
OAuth 2.0 token validation and scope checks.
Data format
The serialization used for requests and responses.
JSON (most web APIs) or XML (SOAP).
Specification / docs
The machine-readable contract that drives docs, clients, and tests.
An OpenAPI document.
Data flow
A client request travels to an endpoint, usually via a gateway that authenticates and rate-limits it. The service runs its logic, serializes a result (commonly JSON), and returns it with a status code. For later events, the provider can push a webhook to a client-registered URL rather than making the client poll.
Integrations: API gateways and management platforms, OpenAPI/Swagger tooling for docs and client generation, Identity providers for OAuth 2.0 / OIDC
Architecture limitations
Examples
Adding payments without touching card data
An online store needs to accept cards but doesn't want to handle sensitive data.
It integrates a payment provider's API: the client sends a tokenized request, the provider processes the charge, and returns a status - the store never stores raw card numbers.
A simple weather GET request
A dashboard shows current conditions for a city.
It calls GET /weather?city=Geneva on a weather API with an API key; the server returns 200 and a JSON body the dashboard renders.
Webhook instead of polling
An app needs to know the instant a payment settles.
Rather than repeatedly polling the payment API, the app registers a webhook URL; the provider pushes an HTTP call to it when the event occurs.
Comparisons
REST vs GraphQL vs GraphQL
REST exposes multiple resource endpoints with fixed responses; GraphQL exposes one endpoint where clients request exactly the fields they need.
| Criterion | REST vs GraphQL | GraphQL |
|---|---|---|
| Endpoints | Many, one per resource | Single endpoint |
| Data fetching | Fixed response shapes | Client specifies exact fields |
| Over/under-fetching | Common | Largely eliminated |
| Caching | Simple HTTP caching | More complex to cache |
When to choose — REST for simple, cacheable CRUD and public APIs; GraphQL for complex or client-variable data needs.
REST vs SOAP vs SOAP
REST is a lightweight, flexible HTTP style; SOAP is a strict, contract-heavy XML protocol still used where formal standards matter.
| Criterion | REST vs SOAP | SOAP |
|---|---|---|
| Format | Usually JSON | XML only |
| Contract | Convention plus OpenAPI docs | Formal WSDL contract |
| Weight | Lightweight, flexible | Heavier, more rigid |
| Typical use | Web and mobile, public APIs | Enterprise, finance, legacy integrations |
When to choose — REST for most modern web and mobile APIs; SOAP where strict contracts and built-in standards are required.
Myths, corrected
Myth
An API means a REST endpoint on the web.
Correction
An API is any interface contract between software components. Libraries, operating systems, and hardware all have APIs; web APIs are just the most visible kind, and REST is only one web style.
Why it happens: Web/REST APIs are what most developers interact with daily, so the general term gets narrowed to that case.
Myth
REST and API are the same thing.
Correction
REST is one architectural style for building APIs. APIs can also be SOAP, GraphQL, gRPC, or non-web library and OS interfaces.
Why it happens: REST's dominance makes it the default mental model for 'API.'
Myth
GraphQL has replaced REST.
Correction
They solve different problems and frequently coexist - REST for simple, cacheable operations and GraphQL for flexible, client-driven data needs. Neither is universally better.
Why it happens: GraphQL's benefits for complex data get generalized into 'REST is obsolete.'
Myth
SOAP is dead.
Correction
SOAP is legacy but still widely used in enterprise, banking, and government systems for its formal contracts and built-in standards. Plenty of critical integrations still rely on it.
Why it happens: SOAP rarely appears in new consumer web projects, so newer developers assume it's gone.
Myth
The API is the documentation (or just the URL).
Correction
The API is the interface contract - the operations, inputs, and outputs. Documentation and the endpoint URL describe and expose it, but they aren't the API itself.
Why it happens: Developers interact with docs and URLs, so those become shorthand for 'the API.'
Practical implications
For admins
Treat every consumed API as a dependency with an SLA, quota, and security posture: track keys and tokens, monitor rate limits and deprecations, and centralize control behind a gateway where possible.
For MSPs
Integrations across client stacks live and die on APIs; document which third-party APIs each client depends on, watch for breaking changes, and secure the credentials that access them.
For business
APIs are strategic - they enable partnerships and faster delivery but also create dependency and lock-in. Exposing an API can turn a capability into a product; consuming one trades build time for a vendor relationship.
For security
APIs are a top attack surface; broken authorization leads the OWASP API Security Top 10. Enforce strong auth, per-object authorization, input validation, rate limiting, and continuous monitoring.
For end users
APIs are invisible but shape the connected experiences users expect - single sign-on, embedded maps and payments, and real-time updates.
Cost impact
Third-party APIs carry usage-based pricing and rate limits; caching, batching, and efficient design directly affect the bill and the ceiling on scale.
Operational impact
Running APIs at scale means gateways, versioning, monitoring, and documentation as ongoing work, not one-time setup.
Decision guide
Use when
- Integrating external services or exposing your own capabilities to others
- Building microservices that must communicate over stable contracts
- Automating cloud infrastructure or sharing data with controlled access
Avoid when
- A simple in-process call would do - don't add a network boundary for its own sake
- Latency-critical paths where a chatty API design would hurt performance
- Bulk data movement better handled by streaming or ETL
Requirements
- A clear contract design (resources/operations, inputs, outputs, errors)
- Authentication and authorization appropriate to the exposure
- Versioning, rate limiting, and accurate (ideally OpenAPI) documentation
Alternatives
- Direct library/SDK calls when no network boundary is needed
- Message queues or event streaming for asynchronous, high-volume flows
- Webhooks for event-driven notifications instead of polling
Related terms
REST
A resource-based, stateless architectural style for web APIs built on HTTP.
GraphQL
A query language and runtime letting clients request exactly the data they need from one endpoint.
SOAP
An older, strict XML-based protocol with formal contracts, common in enterprise systems.
gRPC
A high-performance binary RPC framework over HTTP/2 for service-to-service calls.
Endpoint
A specific addressable operation or resource exposed by an API.
JSON
The lightweight text data format most web APIs use for requests and responses.
OAuth 2.0
A token-based standard for delegated, scoped API authorization without sharing credentials.
Webhook
An event-driven callback where a server pushes an HTTP request to a client when something happens.
OpenAPI (Swagger)
A machine-readable specification for describing REST APIs, powering docs and tooling.
Frequently asked questions
What is an API in simple terms?
An API is like a waiter: it takes a request from one application in an agreed format, deals with a system you can't see, and brings back the response. It lets different software talk to each other without knowing each other's internal workings.
Is REST the same as an API?
No. REST is one architectural style for building APIs. An API is the general concept of a software interface, and it can also be built with SOAP, GraphQL, or gRPC - or exist as a non-web library or operating-system interface.
Are all APIs web APIs?
No. Web APIs are reached over HTTP across a network, but libraries, frameworks, operating systems, and hardware all expose APIs too. Web APIs are simply the most visible modern type.
What's the difference between REST and GraphQL?
REST uses multiple endpoints with fixed response shapes and simple caching; GraphQL uses a single endpoint where clients request exactly the fields they need, avoiding over-fetching but with more complex caching. Many teams use both.
What is an API endpoint?
An endpoint is a specific address for one operation or resource an API exposes, such as GET /users/{id}. A single API typically has many endpoints, each mapping to a capability.
What is a webhook, and how is it different from an API call?
A webhook reverses the direction: instead of a client requesting data, the server pushes an HTTP call to a client-registered URL when an event happens. It's an efficient, event-driven complement to normal request-response API calls.
How are APIs secured?
Through authentication and authorization - API keys, OAuth 2.0 tokens, JWTs, or mutual TLS - plus HTTPS, input validation, and rate limiting. Broken authorization is the most common API security flaw, so getting access control right is critical.
How do I get started with APIs?
Learn HTTP basics and JSON, then experiment with a public API using a tool like Postman or curl. Add authentication (API keys, then OAuth), read the API's OpenAPI docs, and build a small integration end to end.
Conclusion
An API is a contract that lets software components interact without exposing their internals - an idea that spans libraries and operating systems as well as the web APIs most people picture. Web APIs communicate through a request-response cycle over HTTP, in styles like REST, GraphQL, SOAP, and gRPC, usually exchanging JSON, secured with keys or OAuth, and managed with gateways, versioning, and OpenAPI docs. The clearest sign you understand APIs is being able to separate the general concept from any single style.
Main takeaway
Next, read a deeper explainer on REST vs GraphQL, or a tutorial on calling and securing a real API with OAuth 2.0.