

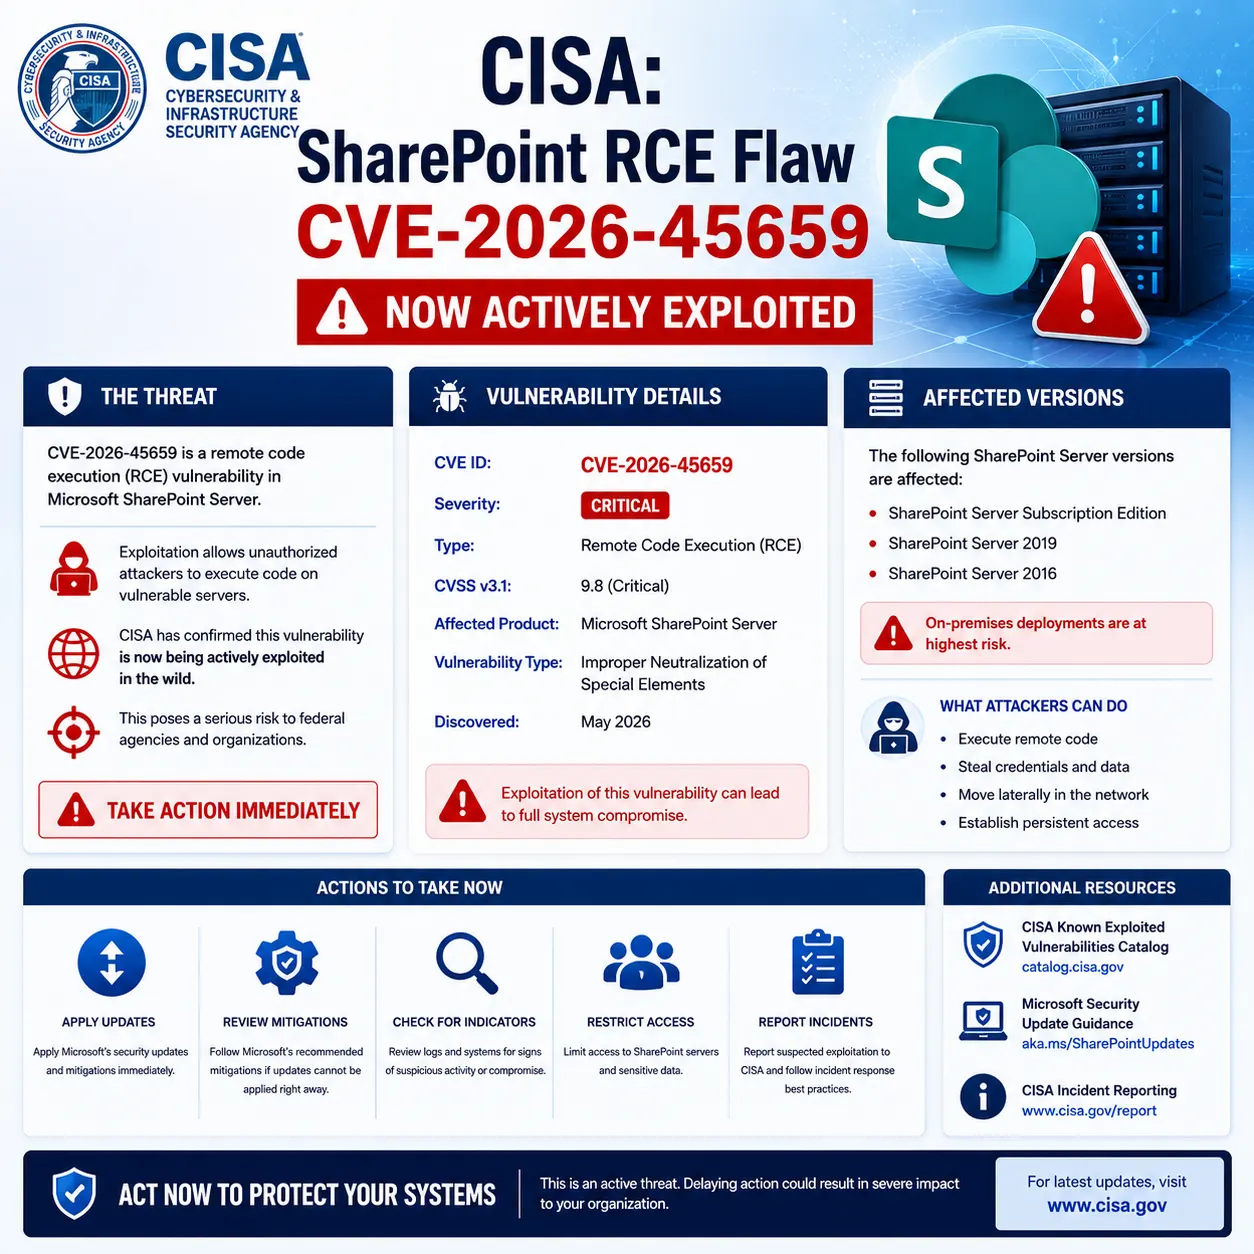
CISA: SharePoint RCE Flaw CVE-2026-45659 Now Actively Exploited
A deserialization bug in on-premises SharePoint Server, patched in May but omitted from that month's security update notes, is now being exploited by ransomware actors, CISA says.

On this page
Key takeaways
- CISA added CVE-2026-45659 to its KEV catalog on July 1, 2026, and gave federal agencies until July 4 to remediate under BOD 26-04.
- The flaw is a CWE-502 deserialization bug that requires only Site Member permissions and no user interaction to trigger.
- Microsoft shipped a fix in May 2026, after the CVE was accidentally left out of that month's Patch Tuesday notes.
- CISA has since confirmed ransomware gangs are abusing the flaw, and Shadowserver tracked thousands of exposed SharePoint servers still online.
- CISA's related alert lists five more actively exploited on-premises SharePoint CVEs added to KEV between April and August 2026.
What to do now
High urgency- Apply Microsoft's May 2026 security update for SharePoint Enterprise Server 2016, 2019, and Subscription Edition immediately
- Enable AMSI integration in Full Mode for every SharePoint web application and monitor for the named Exploit:Script and Backdoor:MSIL/LeakFang.A!dha detections
- Hunt for machine-key harvester artifacts before rotating IIS machine keys
- Assess internet exposure of SharePoint Central Administration and place servers behind an authenticated Layer 7 reverse proxy
- Review logs for anomalous SharePoint worker-process activity, webshells, and machine-key access predating patch deployment
CISA warned that attackers have begun exploiting CVE-2026-45659, a high-severity Microsoft SharePoint remote code execution vulnerability, and added it to its Known Exploited Vulnerabilities catalog on July 1, 2026. The agency later confirmed the flaw is also being abused in ransomware attacks against on-premises SharePoint Server instances.
The vulnerability lets an authenticated attacker with only low-level Site Member permissions run arbitrary code over the network without user interaction, putting internet-exposed, unpatched SharePoint farms at immediate risk.
CISA confirms active exploitation, including ransomware use, of SharePoint deserialization flaw CVE-2026-45659 on unpatched on-premises servers.
Patch on-premises SharePoint Server now: CVE-2026-45659 is in CISA's KEV catalog and is being used in ransomware attacks against internet-exposed, unpatched instances.
Affected & context
CISA added CVE-2026-45659, a deserialization-of-untrusted-data flaw in on-premises Microsoft SharePoint Server, to its Known Exploited Vulnerabilities catalog on July 1, 2026, and later confirmed the flaw is being abused in ransomware attacks.
The bug lets an authenticated attacker with only Site Member permissions run arbitrary code remotely on unpatched, internet-exposed SharePoint servers, and it now sits among a growing cluster of actively exploited on-premises SharePoint CVEs.
Organizations running on-premises SharePoint Enterprise Server 2016, SharePoint Server 2019, or SharePoint Server Subscription Edition, particularly internet-facing deployments.
- Vendors
- Microsoft
- Products
- SharePoint Enterprise Server 2016SharePoint Server 2019SharePoint Server Subscription Edition
- Geography
- United StatesGlobal
- Industry
- GovernmentEnterprise IT
- CVEs
- CVE-2026-45659CVE-2026-32201CVE-2026-56164CVE-2026-58644CVE-2026-50522CVE-2026-55040
What is CVE-2026-45659 and why is CISA warning about it?
CVE-2026-45659 is a deserialization-of-untrusted-data vulnerability in on-premises Microsoft SharePoint Server, classified under CWE-502, per Cyberpress's report. An authenticated attacker holding only Site Member permissions (PR:L) can send crafted serialized objects to a vulnerable SharePoint component and trigger remote code execution over the network (AV:N), Microsoft said in its advisory cited by BleepingComputer.
Microsoft rated the attack complexity as low, noting an attacker does not need detailed prior knowledge of the target system and can repeat the exploit reliably. No user interaction is required, which makes the flaw attractive for automated, large-scale scanning against internet-facing SharePoint farms.
- CWE-502 deserialization flaw in on-premises SharePoint Server
- Requires only Site Member permissions, no admin rights
- Network attack vector, low complexity, no user interaction
How did the patch timeline unfold?
Microsoft released the fix for CVE-2026-45659 on May 21 for SharePoint Enterprise Server 2016, SharePoint Server 2019, and SharePoint Server Subscription Edition. The company acknowledged the CVE had been accidentally omitted from the May 2026 Security Updates, according to BleepingComputer.
CISA added the flaw to its Known Exploited Vulnerabilities catalog on July 1, 2026, roughly six weeks after the fix shipped, and set a three-day remediation deadline of July 4 for federal civilian agencies under Binding Operational Directive 26-04. BOD 26-04 requires agencies to prioritize patching based on factors including KEV catalog inclusion, whether exploitation can be automated, and internet exposure, per CISA's own guidance cited in the source reporting.
- Fix shipped in May 2026, after a missed May Patch Tuesday listing
- Added to KEV on July 1, 2026, with a July 4 federal deadline
Who is affected and what does BOD 26-04 require?
The vulnerability affects all supported on-premises SharePoint Server versions: Subscription Edition, 2019, and 2016, according to CISA's alert. Shadowserver, an internet-scanning watchdog group, tracked over 10,000 SharePoint servers exposed online in early reporting, later refining that figure to over 8,500 exposed servers with more than 200 still unpatched against CVE-2026-45659, per BleepingComputer's follow-up coverage.
BOD 26-04, issued shortly before the KEV addition, requires Federal Civilian Executive Branch agencies to prioritize patching based on KEV inclusion, whether exploitation can be automated at scale, whether the asset is exposed to the internet, and whether successful exploitation grants attackers partial or full device control. CISA has stated stakeholders bear responsibility for assessing their own exposure and meeting the directive's timelines.
- Affects SharePoint Server 2016, 2019, and Subscription Edition
- Over 8,500 SharePoint servers exposed online; 200+ unpatched, per Shadowserver
Why does this matter for enterprise IT and MSPs?
CISA has now confirmed CVE-2026-45659 is being used in ransomware attacks, not just isolated intrusion attempts, a shift that raises the operational stakes for any organization still running unpatched, internet-facing SharePoint Server instances. Since November 2021, CISA has flagged 14 actively exploited Microsoft SharePoint vulnerabilities, with eight also tied to ransomware campaigns, based on BleepingComputer's reporting.
- On-premises SharePoint farms remain a repeated ransomware entry point across multiple CVEs since 2021.
- CISA's SharePoint hardening alert, originally published July 14, 2026 and updated through August 2026, lists six related actively exploited SharePoint CVEs, showing attackers are chaining multiple bugs.
- Post-exploitation activity includes IIS machine-key theft, which can let attackers regain access even after a server is patched if keys are not rotated.
- 14 actively exploited SharePoint CVEs flagged by CISA since 2021, 8 tied to ransomware
- Post-exploitation includes IIS machine-key theft for persistence
CISA's forensic triage guidance suggests affected systems may need examination even after patching, since stolen IIS machine keys can allow re-entry.
What mitigations and detections has CISA recommended?
CISA's alert directs organizations to apply Microsoft's patches, verify successful installation, and shorten patch cycles going forward. It also recommends enabling Antimalware Scan Interface (AMSI) integration for every SharePoint web application in Full Mode where feasible, and watching for specific AMSI and Microsoft Defender Antivirus detections named in the alert, including Exploit:Script/ToolPaneAuthBypass.C for RCE coverage and Backdoor:MSIL/LeakFang.A!dha for post-exploitation activity involving IIS-protected secrets.
- Apply Microsoft's SharePoint security updates and confirm successful installation.
- Enable AMSI integration in Full Mode for each SharePoint web application.
- Hunt for machine-key harvesters before rotating IIS machine keys to prevent re-theft.
- Restrict SharePoint Central Administration access and place internet-facing farms behind a Layer 7 reverse proxy.
- CISA names specific AMSI and MDAV detection signatures for this exploitation cluster
- IIS machine keys should be rotated only after hunting for harvester artifacts
What should administrators watch for next?
Microsoft has not updated its own CVE-2026-45659 advisory to formally tag it as exploited, even though CISA's KEV catalog and alert updates describe confirmed exploitation and ransomware abuse, according to BleepingComputer. That gap between vendor and government agency labeling is worth tracking, since it can affect how internal risk-scoring tools prioritize the patch.
CISA's related alert has been updated multiple times as new SharePoint CVEs were added to KEV, most recently CVE-2026-55040 on August 18, 2026, suggesting the on-premises SharePoint exploitation cluster is still active rather than closed. Administrators running any of the six listed CVEs should expect further updates and treat unpatched, internet-exposed SharePoint servers as a standing risk until confirmed otherwise.
- Microsoft advisory has not been updated to tag CVE-2026-45659 as exploited, per BleepingComputer
- CISA's alert was updated as recently as August 18, 2026 with a sixth related CVE
Timeline
Microsoft ships fix after May update omission
Microsoft released security updates for SharePoint Enterprise Server 2016, SharePoint Server 2019, and SharePoint Server Subscription Edition, saying the CVE-2026-45659 fix had been accidentally left out of the May 2026 Patch Tuesday release.
Source: BleepingComputer
Confidence: High
CISA adds CVE-2026-45659 to KEV catalog
CISA confirmed active exploitation and ordered Federal Civilian Executive Branch agencies to remediate by July 4, 2026 under BOD 26-04.
Source: CISA / Cyberpress
Confidence: High
CISA alert expands to cover related SharePoint CVEs
CISA published a broader alert covering CVE-2026-32201, CVE-2026-45659, and CVE-2026-56164 tied to on-premises SharePoint exploitation and post-exploitation IIS machine-key theft.
Source: CISA
Confidence: High
CISA adds sixth related CVE to KEV alert
CISA updated the same alert to add CVE-2026-55040, bringing the total number of actively exploited on-premises SharePoint CVEs referenced in the alert to six.
Source: CISA
Confidence: High
CISA confirms ransomware exploitation of CVE-2026-45659
CISA confirmed ransomware gangs had begun abusing CVE-2026-45659, while Shadowserver tracked thousands of exposed SharePoint servers, including hundreds still unpatched.
Source: BleepingComputer
Confidence: High
Impact
Unpatched, internet-exposed on-premises SharePoint servers can be remotely compromised by any authenticated user with only Site Member permissions, and CISA has confirmed the flaw is now also used to deploy ransomware.
Business impact
Compromised SharePoint farms can lead to ransomware deployment, service outages, and forced forensic investigations under CISA's triage requirements, disrupting document collaboration and internal workflows.
Technical impact
Successful exploitation grants remote code execution on the SharePoint Server and enables post-exploitation theft of IIS machine keys, allowing attackers to forge authentication tokens and persist even after a patch is applied.
Security impact
CVE-2026-45659 is one of six actively exploited on-premises SharePoint CVEs CISA has added to its KEV catalog since April 2026, and one of 14 SharePoint flaws flagged as exploited since 2021, eight tied to ransomware.
Privacy impact
Data stored in compromised SharePoint document libraries and sites is exposed to unauthorized access once an attacker achieves code execution on the server.
Affected audience: Enterprise IT administrators, MSPs managing on-premises SharePoint farms, Federal Civilian Executive Branch agencies, Government and enterprise security teams
Action required.
Technical details
- CVEs
- CVE-2026-45659, CVE-2026-32201, CVE-2026-56164, CVE-2026-58644, CVE-2026-50522, CVE-2026-55040
- Exploitation
- Exploited in the wild
- Attack vector
- Network (AV:N); low attack complexity (AC:L); requires only authenticated Site Member privileges (PR:L) and no user interaction
- Affected versions
- SharePoint Enterprise Server 2016, SharePoint Server 2019, SharePoint Server Subscription Edition
- Patched versions
- SharePoint Enterprise Server 2016 (May 2026 update), SharePoint Server 2019 (May 2026 update), SharePoint Server Subscription Edition (May 2026 update)
- CWEs
- CWE-502
Detection methods
- AMSI detection Exploit:Script/SuspSignoutReqBody.A (request body scanning, SharePoint Server Subscription Edition only)
- AMSI detection Exploit:Script/ToolPaneAuthBypass.A (request header scanning, all supported versions)
- AMSI detection Exploit:Script/ToolPaneAuthBypass.C (RCE coverage, all supported versions)
- Microsoft Defender Antivirus detection Backdoor:MSIL/LeakFang.A!dha for post-exploitation IIS secret theft
Mitigations
- Apply Microsoft's May 2026 patch for CVE-2026-45659 and verify successful installation
- Enable AMSI integration with Full Mode Request Body Scan for each SharePoint web application
- Avoid exposing SharePoint Servers directly to the internet; place them behind an authenticated Layer 7 reverse proxy where exposure is necessary
- Block external access to SharePoint Central Administration and restrict farm/database communications
Workarounds
- Hunt for and remediate machine-key harvester artifacts before rotating IIS machine keys, per Microsoft's ASP.NET view state security guidance
Technical references
Response
Vendor statement
Microsoft said any authenticated attacker with a minimum of Site Member permissions could trigger the flaw remotely, without needing admin rights, and that the attack complexity is low because it does not require prior knowledge of the target system.
Authorities
CISA warned that this type of vulnerability is a frequent attack vector for malicious cyber actors and poses significant risks to the federal enterprise, and it ordered FCEB agencies to remediate under BOD 26-04.
Customer guidance
CISA tells organizations to apply Microsoft's patch immediately, enable AMSI Full Mode scanning on SharePoint web applications, hunt for intrusion artifacts before rotating IIS machine keys, and restrict internet exposure of SharePoint Central Administration.
Response status: Patched
Patch available: Yes
Workaround available: Yes
Updates
CVE-2026-45659 added to CISA KEV catalog
Major updateCISA added the flaw to its Known Exploited Vulnerabilities catalog and set a July 4, 2026 remediation deadline for federal agencies.
CISA alert expanded with CVE-2026-58644
CISA updated its SharePoint hardening alert to add CVE-2026-58644 to the KEV catalog.
CVE-2026-50522 added to KEV
CISA updated the alert again to reflect the addition of CVE-2026-50522.
CVE-2026-55040 added, sixth CVE in cluster
Major updateCISA updated the alert to add a sixth actively exploited on-premises SharePoint CVE, CVE-2026-55040.
CISA confirms ransomware use of CVE-2026-45659
Major updateCISA confirmed ransomware gangs are now abusing CVE-2026-45659 in a Tuesday update to the KEV catalog, and Shadowserver reported over 8,500 exposed servers, more than 200 still unpatched.
FAQ
What is CVE-2026-45659?
CVE-2026-45659 is a CWE-502 deserialization-of-untrusted-data vulnerability in on-premises Microsoft SharePoint Server that lets an authenticated attacker with only Site Member permissions execute arbitrary code remotely over the network.
Which SharePoint versions are affected?
The flaw affects on-premises SharePoint Enterprise Server 2016, SharePoint Server 2019, and SharePoint Server Subscription Edition; SharePoint Online is not affected.
Is CVE-2026-45659 being exploited in ransomware attacks?
Yes. CISA confirmed that ransomware gangs are now abusing CVE-2026-45659, in addition to earlier active exploitation flagged when the flaw was added to the KEV catalog on July 1, 2026.
Is a patch available for CVE-2026-45659?
Yes. Microsoft released security updates for SharePoint Enterprise Server 2016, SharePoint Server 2019, and SharePoint Server Subscription Edition in May 2026, after the CVE was accidentally omitted from that month's Patch Tuesday release.
How many SharePoint servers are still exposed?
Shadowserver tracked over 8,500 SharePoint servers exposed to the internet, with more than 200 of them still unpatched against CVE-2026-45659, according to CISA's ransomware update.
What other SharePoint CVEs is CISA tracking in this cluster?
CISA's alert covers six actively exploited on-premises SharePoint CVEs added to KEV between April and August 2026: CVE-2026-32201, CVE-2026-45659, CVE-2026-56164, CVE-2026-58644, CVE-2026-50522, and CVE-2026-55040.
The bottom line
CISA confirmed active exploitation and ransomware abuse of SharePoint flaw CVE-2026-45659, one of six related on-premises SharePoint CVEs added to its KEV catalog since April 2026.
Organizations running on-premises SharePoint Server should apply the May 2026 patch, enable AMSI Full Mode scanning, and hunt for intrusion artifacts before rotating IIS machine keys.
What happens next
CISA may continue updating its SharePoint hardening alert as additional exploited CVEs surface, and Microsoft has not yet updated its own advisory to tag CVE-2026-45659 as exploited.
Related on Anavem: CISA Adds Actively Exploited SharePoint RCE CVE-2026-45659 to KEV Catalog · Max-Severity Adobe ColdFusion Flaw CVE-2026-48282 Now Exploited in Attacks · Microsoft Ships KB5082417 .NET Framework Update Fixing CLR Privilege Escalation · Microsoft Patches Dozen-Plus Flaws, Apple Fixes Screen Sharing Bug CVE-2026-6540 · Microsoft Ships KB5078938 for Windows Server 2016 and Windows 10 1607 · Microsoft Ships KB5082123 for Windows 10 1809 and Server 2019, Patching Five Vul.
What to do
Patch on-premises SharePoint Server now and check exposed instances against CISA's detection signatures for signs of compromise.
Sources
BleepingComputer · Jul 2, 2026
Claims supported
- CVE-2026-45659 added to KEV catalog on July 1, 2026 with a July 4 remediation deadline
- Microsoft's May 2026 patch and CVSS vector details
- Shadowserver tracked over 10,000 exposed SharePoint servers
CISA · Jul 14, 2026 · Primary source
Claims supported
- Six actively exploited on-premises SharePoint CVEs and their KEV addition dates
- AMSI and MDAV detection signatures for exploitation cluster
- Hardening recommendations including IIS machine-key rotation guidance
BleepingComputer · Aug 19, 2026
Claims supported
- CISA confirmed ransomware exploitation of CVE-2026-45659
- Shadowserver tracked over 8,500 exposed servers, 200+ unpatched
- 14 SharePoint CVEs flagged exploited since 2021, eight tied to ransomware
Cyberpress · Jul 1, 2026
Claims supported
- CWE-502 classification and forensic triage guidance under BOD 26-04