How to Enable Remote Desktop on Windows Server Using PowerShell
Enable Remote Desktop on Windows Server using PowerShell. Covers the registry change, firewall rules, NLA configuration, connectivity testing, and a reusable script for multi-server deployment.

- Difficulty
- Intermediate
- Time required
- 5-10 minutes
- Steps
- 3
- Platform
- Windows Server
- Version
- 2016 / 2019 / 2022 / 2025
- Last tested
- July 18, 2026
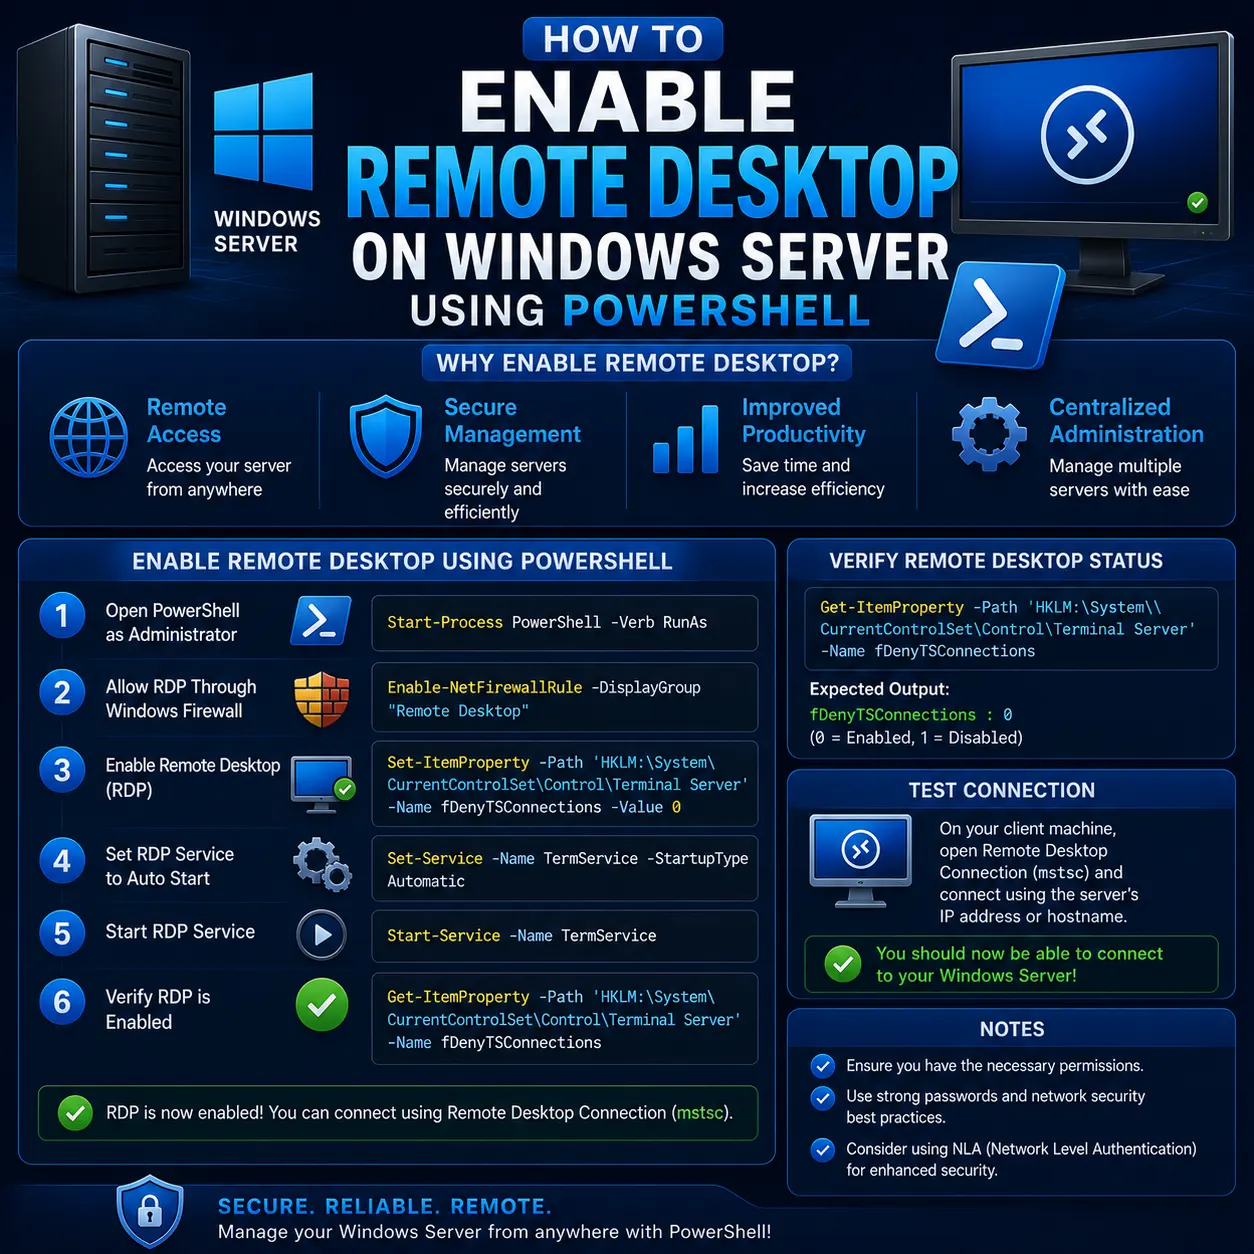
Table of contents
Quick Answer
Go to the stepsSet fDenyTSConnections to 0, enable the Remote Desktop firewall rules, enable NLA, and restart TermService. Three PowerShell commands and RDP is live.
- Open PowerShell as Administrator.
- Set fDenyTSConnections to 0 in the registry.
- Enable the Remote Desktop firewall rule group.
- Enable NLA (UserAuthentication = 1).
- Restart TermService.
- Test with Test-NetConnection on port 3389.
Set-ItemProperty -Path 'HKLM:\System\CurrentControlSet\Control\Terminal Server' -Name 'fDenyTSConnections' -Value 0; Enable-NetFirewallRule -DisplayGroup 'Remote Desktop'; Restart-Service TermService -ForceExpected result: Port 3389 is listening. Test-NetConnection to the server on port 3389 returns TcpTestSucceeded: True.
Key takeaways
- How to enable RDP on Windows Server using PowerShell, configure firewall rules and NLA, verify connectivity, and deploy the configuration to multiple servers.
- PowerShell is the only option on Server Core and the most efficient method for scripting RDP enablement across multiple servers in enterprise environments.
- Three PowerShell commands enable RDP on any Windows Server: set fDenyTSConnections to 0, enable the Remote Desktop firewall group, and restart TermService. Always enable NLA for security.
Introduction
Remote Desktop Protocol (RDP) is disabled by default on Windows Server for security reasons. Enabling it via PowerShell is faster, scriptable, and works on Server Core installations where no GUI is available. The process involves three things: setting the fDenyTSConnections registry value to 0, enabling the Remote Desktop firewall rules for port 3389, and enabling Network Level Authentication (NLA) for security. This tutorial covers all three plus connectivity testing and a reusable deployment script.
Who this is for: Windows Server administrators, MSPs, and DevOps engineers who need to enable and secure RDP access for remote management.
Before you start
- Access
- Local or remote PowerShell with Administrator privileges
- Required roles
- Local Administrator on the target server
- Required licenses
- None (RDP is built into Windows Server)
- Environment
- Windows Server 2016, 2019, 2022, or 2025 (Standard or Datacenter, including Server Core)
- Vendor
- Microsoft
- Tested environment
- Windows Server 2025 Datacenter, Server Core
- Last tested
- Administrator permissions required
5-10 minutes
Warning: Security risk: port 3389 exposure
Enabling RDP opens TCP port 3389 and creates a potential attack surface. Always enable Network Level Authentication and restrict access via firewall rules or VPN.
Note: Active sessions will be dropped during service restart
Using Restart-Service -Force on TermService will disconnect any active RDP sessions on the server.
1Enable RDP in registry and configure firewall rules
Enable Remote Desktop by modifying the core registry setting and enabling firewall rules.
Open PowerShell as Administrator (right-click Start > Terminal (Admin) or PowerShell (Admin)).
Enable RDP in the registry:
Set-ItemProperty -Path 'HKLM:\System\CurrentControlSet\Control\Terminal Server' -Name 'fDenyTSConnections' -Value 0Enable the Windows Firewall rules for port 3389:
Enable-NetFirewallRule -DisplayGroup "Remote Desktop"This activates both TCP and UDP rules for RDP. Verify:
Get-NetFirewallRule -DisplayGroup "Remote Desktop" | Where-Object Enabled -eq True | Select-Object DisplayName, EnabledYou should see at least "Remote Desktop - User Mode (TCP-In)" listed as True.
Set-ItemProperty -Path 'HKLM:\System\CurrentControlSet\Control\Terminal Server' -Name 'fDenyTSConnections' -Value 0Expected result: fDenyTSConnections is set to 0. RDP is enabled at the registry level.
Note
The fDenyTSConnections value controls whether Terminal Services accepts incoming connections. Setting it to 0 enables RDP. The firewall rules are pre-defined but disabled by default.
2Enable Network Level Authentication and restart TermService
Enable Network Level Authentication for security and restart the RDP service.
Enable NLA to require authentication before establishing an RDP session:
Set-ItemProperty -Path 'HKLM:\System\CurrentControlSet\Control\Terminal Server\WinStations\RDP-Tcp' -Name 'UserAuthentication' -Value 1Restart Terminal Services to apply all changes:
Restart-Service -Name TermService -Force
Start-Sleep -Seconds 5
Get-Service TermService | Select-Object Name, StatusNLA prevents unauthenticated connections from consuming server resources. This protects against DoS attacks and brute-force attempts that target the RDP login screen. Only disable NLA (value 0) if you have legacy clients that don't support it.
Set-ItemProperty -Path 'HKLM:\System\CurrentControlSet\Control\Terminal Server\WinStations\RDP-Tcp' -Name 'UserAuthentication' -Value 1Expected result: NLA is enabled. TermService is running. Port 3389 is listening.
Note
The -Force flag on Restart-Service will drop any active RDP sessions. Plan accordingly if the server has active users. The service restart takes a few seconds.
3Verify RDP configuration and test connectivity
Verify that RDP is fully functional and test connectivity.
Run a complete configuration check:
# Registry check
$rdp = (Get-ItemProperty 'HKLM:\System\CurrentControlSet\Control\Terminal Server').fDenyTSConnections
Write-Host "RDP Enabled: $($rdp -eq 0)"
# Firewall check
$fw = (Get-NetFirewallRule -DisplayGroup 'Remote Desktop' | Where-Object Enabled -eq True).Count
Write-Host "Firewall Rules Active: $fw"
# NLA check
$nla = (Get-ItemProperty 'HKLM:\System\CurrentControlSet\Control\Terminal Server\WinStations\RDP-Tcp').UserAuthentication
Write-Host "NLA Enabled: $($nla -eq 1)"
# Service check
Write-Host "TermService: $((Get-Service TermService).Status)"
# Port check
$port = Get-NetTCPConnection -LocalPort 3389 -State Listen -ErrorAction SilentlyContinue
Write-Host "Port 3389 Listening: $($null -ne $port)"
# Server IP
$ip = (Get-NetIPAddress -AddressFamily IPv4 | Where-Object {$_.IPAddress -notlike '127.*'} | Select-Object -First 1).IPAddress
Write-Host "Connect with: mstsc /v:$ip"From a remote machine, test connectivity:
Test-NetConnection -ComputerName SERVER_IP -Port 3389Then connect with: mstsc /v:SERVER_IP
Test-NetConnection -ComputerName localhost -Port 3389Expected result: All checks return True/Green. Test-NetConnection returns TcpTestSucceeded: True.
Note
For multi-server deployment, wrap these commands in Invoke-Command -ComputerName with credentials. The same PowerShell commands work identically on Server 2016 through 2025, including Server Core.
Troubleshooting
RDP connection refused after enabling via PowerShell
Warning
Cause: Firewall rules not enabled, port 3389 blocked by network firewall or security group, or TermService not running.
Verify all three components:
# Check registry
(Get-ItemProperty 'HKLM:\System\CurrentControlSet\Control\Terminal Server').fDenyTSConnections
# Check firewall
Get-NetFirewallRule -DisplayGroup 'Remote Desktop' | Select DisplayName, Enabled
# Check service
Get-Service TermService
# Check port
Get-NetTCPConnection -LocalPort 3389 -State ListenIf all local checks pass, the issue is likely a network-level firewall (Azure NSG, AWS Security Group, or physical firewall) blocking port 3389.
NLA error: 'The remote computer requires Network Level Authentication'
Note
Cause: The client doesn't support NLA, or the server's NLA configuration requires credentials that the client can't provide (e.g. expired password, untrusted certificate).
On the client, enable NLA support in the RDP client settings (Show Options > Advanced > Server authentication). If the client is too old to support NLA, temporarily disable NLA on the server:
Set-ItemProperty -Path 'HKLM:\System\CurrentControlSet\Control\Terminal Server\WinStations\RDP-Tcp' -Name 'UserAuthentication' -Value 0
Restart-Service TermService -ForceRe-enable NLA after testing and plan client upgrades.
Access denied when connecting via RDP despite correct credentials
Warning
Cause: The user account doesn't have RDP access permissions. By default, only Administrators can connect via RDP on Windows Server.
Add the user to the Remote Desktop Users group:
Add-LocalGroupMember -Group 'Remote Desktop Users' -Member 'DOMAIN\username'Verify current members:
Get-LocalGroupMember -Group 'Remote Desktop Users'Frequently asked questions
Do the PowerShell commands differ between Server 2022 and 2025?
No. The PowerShell commands (Set-ItemProperty, Enable-NetFirewallRule, Restart-Service) are identical across Windows Server 2016, 2019, 2022, and 2025. The registry paths, firewall rule names, and service names haven't changed.
Can I enable RDP on Server Core with PowerShell?
Yes, and it's often the only way since Server Core has no GUI. Use the same PowerShell commands directly at the console or via PowerShell remoting (Invoke-Command). If PowerShell remoting isn't enabled yet, use sconfig (option 7) at the Server Core console.
What happens if I disable NLA?
Disabling NLA allows unauthenticated connections to reach the RDP login screen, consuming server resources. This exposes the server to brute-force and DoS attacks. Only disable NLA if legacy clients can't connect with it enabled, and add compensating controls like VPN or IP-based firewall rules.
Why might TermService fail to restart?
Common causes: port 3389 conflict with another service, corrupted registry entries, or active RDP sessions blocking the restart. Use -Force with Restart-Service, check for port conflicts with Get-NetTCPConnection -LocalPort 3389, and review Event Viewer (System log, TermService source) for errors.
How do I enable RDP on multiple servers at once?
Wrap the commands in Invoke-Command -ComputerName with credentials. PowerShell remoting must be enabled on target servers. For domain-joined servers, use domain admin credentials. For workgroup servers, configure TrustedHosts first.
Conclusion
You've enabled Remote Desktop on Windows Server via PowerShell by modifying the fDenyTSConnections registry value, enabling the Remote Desktop firewall rules for port 3389, configuring NLA for secure authentication, and verifying connectivity. The same commands work across Server 2016 through 2025, including Server Core.
Three PowerShell commands enable RDP on any Windows Server: set fDenyTSConnections to 0, enable the Remote Desktop firewall group, and restart TermService. Always enable NLA for security.
Set-ItemProperty fDenyTSConnections 0 > Enable-NetFirewallRule Remote Desktop > Restart-Service TermService