How to Install and Configure Microsoft Entra Connect for Directory Sync
Install and configure Microsoft Entra Connect to synchronize your on-premises Active Directory with Microsoft Entra ID, enabling hybrid identity with password hash sync, OU filtering, and SSO.

- Difficulty
- Intermediate
- Time required
- 30-60 minutes
- Steps
- 3
- Platform
- Microsoft Entra Connect
- Last tested
- July 18, 2026
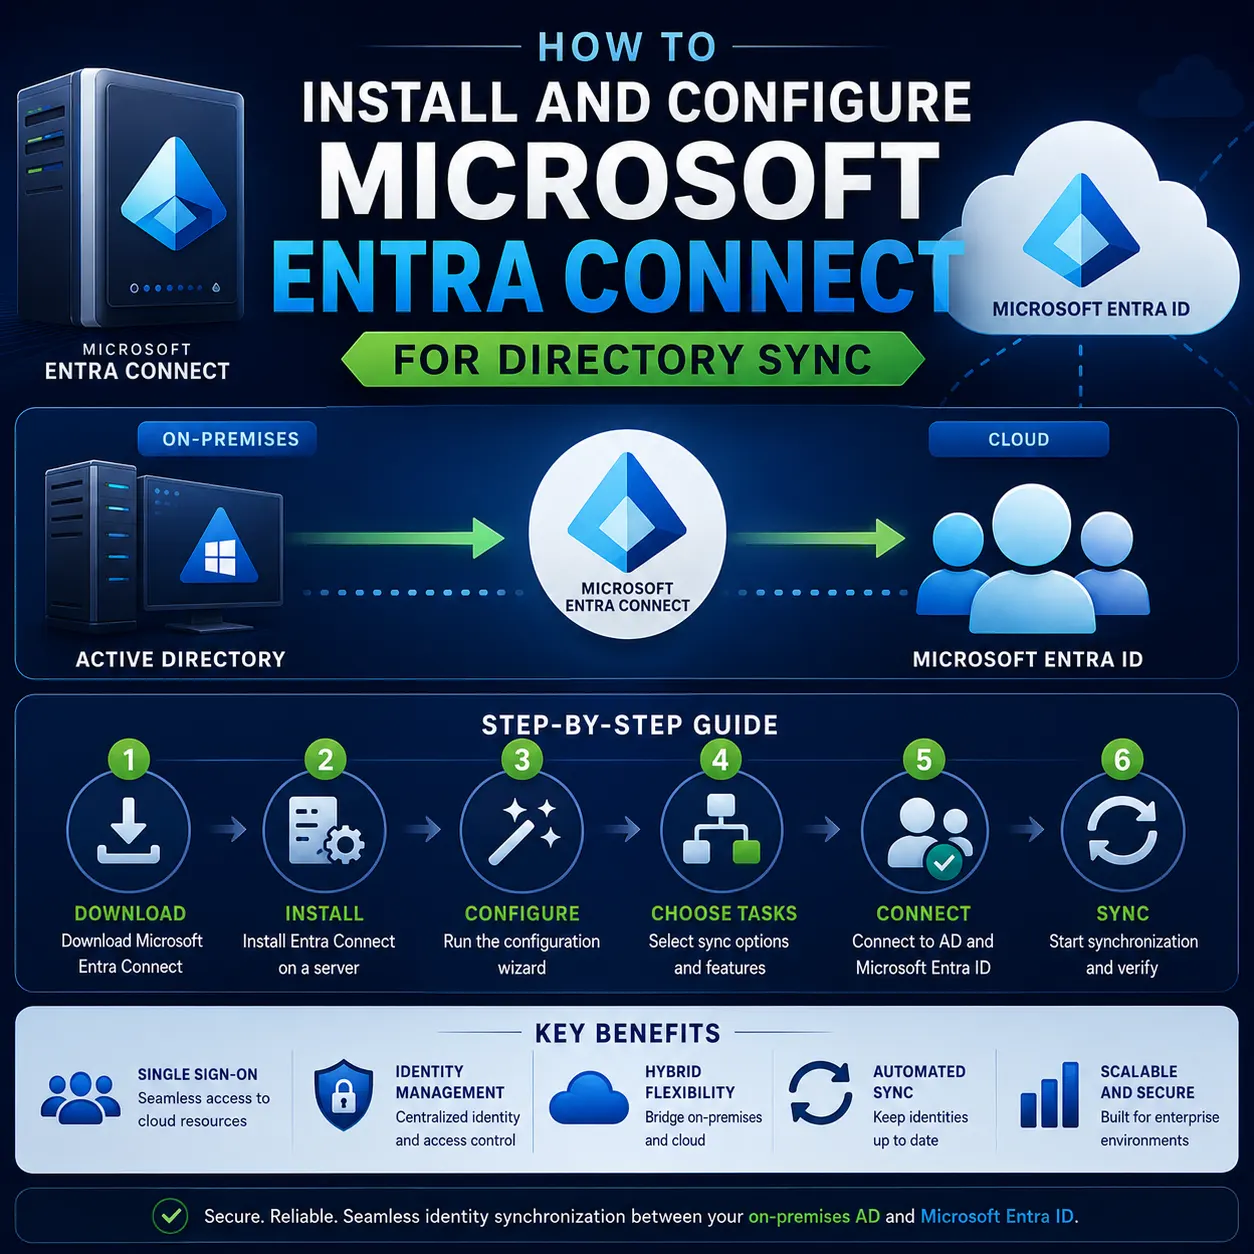
Table of contents
Quick Answer
Go to the stepsDownload Entra Connect from entra.microsoft.com, install with Custom settings, choose Password Hash Synchronization, connect your AD forest, filter OUs, and verify the initial sync in both admin centers.
- Run IdFix to clean AD errors.
- Enable TLS 1.2 on the server.
- Download Entra Connect from entra.microsoft.com.
- Install with Custom settings, select Password Hash Sync.
- Connect to Entra ID with Global Admin credentials.
- Add your AD forest with Enterprise Admin credentials.
- Select OUs to sync and complete the wizard.
entra.microsoft.com > Identity > Hybrid management > Microsoft Entra Connect > DownloadExpected result: Users from selected OUs appear in Microsoft 365 admin center with a sync icon. Get-ADSyncScheduler shows NextSyncCyclePolicyType as Delta.
Key takeaways
- How to install Microsoft Entra Connect on a dedicated server and configure custom synchronization with password hash sync, OU filtering, and initial sync verification.
- Without Entra Connect, organizations must maintain separate user accounts in AD and the cloud. Synchronization eliminates this overhead and enables SSO across on-premises and cloud resources.
- Entra Connect with Password Hash Sync is the most straightforward path to hybrid identity. Run IdFix first, install with Custom settings for OU control, and verify sync in both admin centers.
Introduction
Microsoft Entra Connect (formerly Azure AD Connect) synchronizes users, groups, and passwords from your on-premises Active Directory to Microsoft Entra ID. This enables hybrid identity: users sign into Microsoft 365 and Azure with the same credentials they use on-premises. This tutorial covers the custom installation method, which gives you control over sign-in method, OU filtering, and optional features like password writeback.
Who this is for: IT administrators, MSPs, and hybrid identity architects setting up directory synchronization between on-premises AD and Microsoft Entra ID.
Before you start
- Access
- Microsoft Entra admin center (entra.microsoft.com) and on-premises Active Directory
- Required roles
- Global Administrator (Entra ID)
- Enterprise Administrator (on-premises AD)
- Required licenses
- Microsoft 365 (any plan with Entra ID)
- Or standalone Microsoft Entra ID P1/P2
- Environment
- Domain-joined Windows Server 2016+ with 4 GB RAM, 70 GB disk, .NET 4.7.1+, TLS 1.2 enabled
- Vendor
- Microsoft
- Tested environment
- Windows Server 2022, AD DS 2016 functional level, Entra Connect 2.x
- Last tested
- Administrator permissions required
- Backup required
30-60 minutes
Warning: Clean up Active Directory first
Run IdFix to clean up AD errors before installing Entra Connect. Duplicate proxyAddresses and invalid UPNs will cause sync failures.
Warning: Use a dedicated server
Don't install on a domain controller in production. Use a dedicated member server for performance and security isolation.
Critical: TLS 1.2 required
TLS 1.2 is mandatory. Entra Connect will fail to connect to Azure without it.
1Prepare Active Directory and server prerequisites
Clean up Active Directory and verify server prerequisites before installation.
Run IdFix to find and fix AD errors that block synchronization. Download IdFix from the Microsoft Download Center, run it on a domain-joined machine, and click Query. Fix issues like duplicate proxyAddresses, invalid UPN characters, and missing mail attributes. Re-run until clean.
Verify TLS 1.2 on the Entra Connect server:
# Check TLS 1.2 status
$path = 'HKLM:\SYSTEM\CurrentControlSet\Control\SecurityProviders\SCHANNEL\Protocols\TLS 1.2'
Get-ItemProperty "$path\Client" -Name Enabled -ErrorAction SilentlyContinue
Get-ItemProperty "$path\Server" -Name Enabled -ErrorAction SilentlyContinueIf not enabled, set it via registry and reboot. Also confirm the server can reach login.microsoftonline.com on port 443:
Test-NetConnection login.microsoftonline.com -Port 443Server requirements: Windows Server 2016+, 4 GB RAM, 70 GB disk, .NET 4.7.1+, domain-joined, not a DC in production.
Expected result: IdFix reports zero errors (or only documented acceptable exceptions). TLS 1.2 is confirmed enabled.
Note
Back up AD before applying IdFix changes. The MSOL service account created during installation never expires and uses a randomly generated complex password.
2Install Entra Connect and connect to Entra ID and AD
Download, install Entra Connect with custom settings, and connect to both Entra ID and on-premises AD.
entra.microsoft.com > Identity > Hybrid management > Microsoft Entra Connect > DownloadDownload AzureADConnect.msi from entra.microsoft.com > Identity > Hybrid management > Microsoft Entra Connect > Connect Sync > Download.
Run the installer as Administrator. On the Welcome page, accept the license terms. Click Customize (not Express settings).
On Install required components, leave defaults and click Install. This installs SQL Express LocalDB, .NET components, and PowerShell modules (2-3 minutes).
On User sign-in, select Password Hash Synchronization (most common, simplest to maintain). Click Next.
On Connect to Azure AD, enter your Global Administrator credentials (e.g. admin@tenant.onmicrosoft.com). Complete MFA if prompted.
On Connect your directories, click Add Directory. Select Create new AD account and enter Enterprise Admin credentials for your domain. Entra Connect creates a service account (MSOL_xxxx) with replication permissions.
Expected result: The wizard connects to your Entra ID tenant and your AD forest. Both show green checkmarks.
Note
Use a dedicated Global Admin account for Entra Connect, not a personal admin account. The credentials are stored encrypted on the server. For Pass-through Authentication or ADFS, select the appropriate option instead of Password Hash Sync.
3Configure OU filtering and verify initial sync
Select OUs, complete the wizard, and verify the initial synchronization.
On Domain and OU filtering, expand your domain and check only the OUs you want to sync (Users, Groups, Contacts). Exclude OUs for service accounts, disabled users, and test accounts.
On Uniquely identifying your users, select Let Azure manage the source anchor (recommended).
On Filter users and devices, select Synchronize all users and devices unless you need group-based filtering.
On Optional features, enable only what you need. Common choices for initial setup: leave all unchecked. Enable Password writeback or Group writeback later once basic sync is confirmed working.
On Ready to configure, check Start the synchronization process when configuration completes and click Install.
After installation (5-10 minutes), verify sync:
Import-Module ADSync
Get-ADSyncScheduler
Get-ADSyncConnectorRunStatusAlso check admin.microsoft.com > Users > Active users for synced users, and entra.microsoft.com > Identity > Hybrid management for sync health.
Import-Module ADSync; Get-ADSyncSchedulerExpected result: Synced users appear in Microsoft 365 admin center with a sync icon. Get-ADSyncScheduler shows SyncCycleEnabled = True.
Note
Initial sync can take 30 minutes to several hours for large directories (100k+ objects). Delta syncs run every 30 minutes by default. You can force a sync with Start-ADSyncSyncCycle -PolicyType Delta.
Troubleshooting
Entra Connect fails to connect to Azure AD during setup
Critical
Cause: TLS 1.2 not enabled, firewall blocking outbound 443, or proxy not configured for Entra Connect.
Verify TLS 1.2 is enabled in the registry. Test connectivity:
Test-NetConnection login.microsoftonline.com -Port 443
Test-NetConnection aadcdn.msftauth.net -Port 443If behind a proxy, configure it in Entra Connect's machine.config or use the /ProxyAddress parameter during installation.
Cannot add Active Directory forest during installation
Warning
Cause: Enterprise Admin credentials wrong, or the AD forest isn't reachable from the Entra Connect server.
Verify the Entra Connect server is domain-joined and can resolve the forest's DNS. Use nltest /dsgetdc:yourdomain.com to confirm DC reachability. Ensure the Enterprise Admin account isn't locked or password-expired. Try using DOMAIN\username format instead of UPN.
Synchronization errors after initial sync completes
Warning
Cause: Duplicate proxyAddresses, invalid UPN characters, or missing attributes in on-premises AD.
Open Synchronization Service Manager (miisclient.exe in the Entra Connect install directory). Check the Connectors tab for export errors. Common fixes:
# Find sync errors
Get-ADSyncConnectorRunStatus
Get-ADSyncRunStepResult -RunHistoryId (Get-ADSyncRunProfileResult | Select -First 1).RunHistoryIdRe-run IdFix to catch any new AD errors. Fix the affected objects in AD and force a delta sync with Start-ADSyncSyncCycle -PolicyType Delta.
Frequently asked questions
What's the difference between Entra Connect and Azure AD Connect?
Microsoft Entra Connect is the rebranded version of Azure AD Connect (renamed in 2023-2024). The functionality is the same. The rebrand aligns it with Microsoft's broader Entra identity platform.
Can I install Entra Connect on a domain controller?
Yes, but Microsoft doesn't recommend it for production. A dedicated member server provides better performance and security isolation. If you must use a DC, ensure it has adequate resources.
How long does the initial sync take?
Small environments (under 10,000 objects): 30 minutes or less. Large directories (100,000+ objects): several hours. Delta syncs after that run every 30 minutes and take seconds to minutes.
What happens if the Entra Connect server goes down?
Existing cloud users keep working. Sync stops, so new changes won't propagate. Set up a staging mode server as a standby. If the server is lost, install on a new server and run the wizard again.
Can I change OU filtering after installation?
Yes. Re-run the configuration wizard (AzureADConnect.exe in the install directory), select 'Customize synchronization options,' and add or remove OUs. Removing an OU deletes those objects from Entra ID on the next sync cycle.
Conclusion
You've installed Microsoft Entra Connect with custom settings, configured Password Hash Synchronization, connected your AD forest, filtered OUs, and verified the initial sync. Users from selected OUs now appear in Microsoft 365 with synced credentials.
Entra Connect with Password Hash Sync is the most straightforward path to hybrid identity. Run IdFix first, install with Custom settings for OU control, and verify sync in both admin centers.
entra.microsoft.com > Identity > Hybrid management > Microsoft Entra ConnectSources2