How to Configure NTP Time Synchronization on Windows Server
Configure the Windows Time service (W32Time) on Windows Server to sync with reliable external NTP sources, so your domain controllers and member servers keep accurate, consistent time.

- Difficulty
- Intermediate
- Steps
- 5
- Platform
- Windows Server
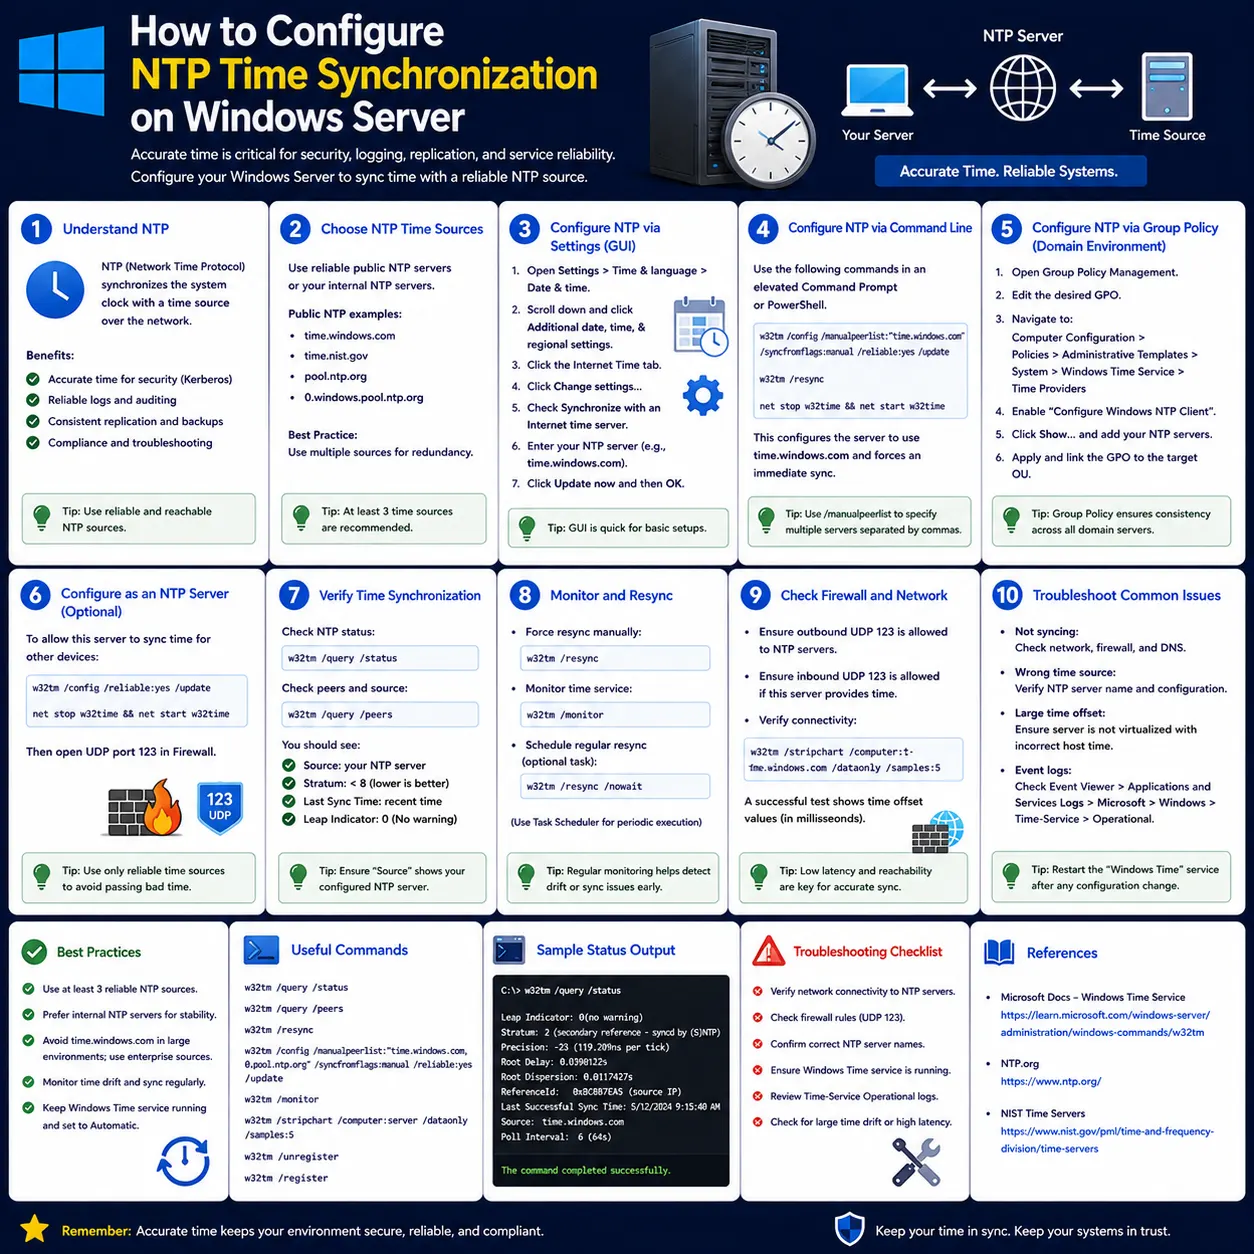
Table of contents
Quick Answer
Go to the stepsOn the forest root PDC emulator, configure W32Time to sync from external NTP servers with a single w32tm /config command, restart the Windows Time service, then force a resync and confirm the source and stratum. Other domain machines should keep syncing from the domain (NT5DS), not from external NTP directly.
- Confirm you are on the PDC emulator with netdom query fsmo (external NTP config belongs here).
- From an elevated prompt, run the w32tm /config command with your chosen NTP peer list.
- Restart the service: net stop w32time && net start w32time.
- Force a sync with w32tm /resync.
- Verify with w32tm /query /status and w32tm /query /source.
w32tm /config /manualpeerlist:"time.windows.com,0x8" /syncfromflags:manual /reliable:yes /updateExpected result: The Windows Time service synchronizes with the configured external NTP peers; w32tm /query /source returns your NTP peer(s) and w32tm /query /status shows a valid stratum and a recent last successful sync time.
Key takeaways
- You will learn how to configure the Windows Time service (W32Time) to synchronize with reliable external NTP servers, and how to verify that your Windows Server is holding accurate time. This includes identifying the correct server in your time hierarchy, setting the manual peer list, and confirming the sync source and stratum.
- Accurate time is a prerequisite for Kerberos authentication, log correlation, certificate validation, and scheduled tasks across an Active Directory environment. Even small clock drift on a domain controller can cause authentication failures and hard-to-diagnose issues.
- Configure only the forest root PDC emulator (or a standalone server) to sync from external NTP peers, and let the rest of the domain sync from the AD hierarchy.
Introduction
In an Active Directory forest, time flows down a hierarchy: domain members sync from domain controllers, DCs sync from the PDC emulator, and the forest root PDC emulator is the one machine that should point to an authoritative external NTP source. Getting that hierarchy wrong - for example, pointing every server at time.windows.com - leads to conflicting time sources and drift.
This tutorial walks through configuring the Windows Time service (W32Time) end to end using the built-in w32tm command-line tool. You will identify the server's role, choose reliable NTP sources such as pool.ntp.org or time.windows.com, apply the configuration with w32tm /config, restart the service, and then force a resync to verify the source, stratum, and last successful sync. All commands run from an elevated Command Prompt or PowerShell session.
Who this is for: This guide is for sysadmins, MSPs, and IT pros who manage Windows Server domain controllers, member servers, or standalone hosts and need reliable, correctly sourced time synchronization.
Before you start
- Access
- You need local administrator rights on the target Windows Server and the ability to open an elevated Command Prompt or PowerShell session. In an Active Directory environment, make these changes on the forest root PDC emulator using a Domain Admins account.
- Required roles
- Local Administrator on the target server
- Domain Admins (when configuring the PDC emulator in an AD forest)
- Administrator (local or domain)
- Environment
- A supported Windows Server installation running the Windows Time service (W32Time), with outbound UDP port 123 open to the external NTP sources you select.
- Vendor
- Microsoft
- Tested environment
- Windows Server 2019/2022
- Administrator permissions required
About 15-20 minutes.
Warning: Time changes can disrupt authentication and logging
Kerberos tolerates only a small clock skew (5 minutes by default). Applying an incorrect NTP source, an unreachable peer list, or a large time correction can break domain logons, break scheduled tasks, and desynchronize event log timestamps across the environment. Configure and verify on the PDC emulator first, and confirm the external sources are reachable on UDP 123 before restarting the service.
Critical: Do not point multiple machines at external NTP in a domain
In an Active Directory domain, only the forest root PDC emulator should sync from an external NTP source. Applying the /syncfromflags:manual configuration to other domain controllers or member servers overrides the domain hierarchy and can create conflicting time sources. Leave those machines on the default domain synchronization (NT5DS).
1Identify the server's role in the time hierarchy
Determine whether the server is the PDC emulator, another domain controller, a member server, or standalone so you configure the correct time source.
Start menu → right-click Command Prompt → Run as administratorBefore changing anything, establish where this server sits in the Active Directory time hierarchy. By default, domain-joined machines synchronize their clock up the domain hierarchy: member servers and workstations sync from a domain controller, domain controllers sync from the PDC emulator, and the PDC emulator in the forest root domain is the single machine that should point to an external NTP source. This keeps the whole forest anchored to one authoritative clock.
Only configure an external NTP peer list on the forest root PDC emulator (or on a standalone/workgroup server). Leaving every domain member syncing from the domain avoids clock conflicts that break Kerberos authentication.
To find which domain controller currently holds the PDC emulator role, open an elevated Command Prompt and run the command below.
netdom query fsmoExpected result: A list of the five FSMO role holders is printed, including a line such as "PDC ... your-dc.contoso.com" identifying the server that owns the PDC emulator role.
Note
netdom ships with the AD DS role and RSAT AD tools. If it is unavailable, you can also find the PDC emulator with PowerShell: Get-ADDomain | Select-Object PDCEmulator. For a standalone or workgroup server there is no hierarchy - treat it like a PDC emulator and point it directly at an external NTP source.
2Choose reliable external NTP time sources
Select trustworthy NTP servers to use as the authoritative external time source.
Pick reliable, low-latency NTP sources for the PDC emulator (or standalone server) to synchronize with. Good options include:
- pool.ntp.org - a large rotating pool of community NTP servers (e.g.
0.pool.ntp.org,1.pool.ntp.org). - time.windows.com - Microsoft's public NTP service, the default on Windows.
- An internal hardware time source (such as a GPS/atomic reference clock or an appliance) if your environment requires it.
List multiple peers so W32Time has redundancy if one source is unreachable. Each peer is followed by a flag; for standard NTP client synchronization, append ,0x8, which requests time using client mode. Separate multiple peers with spaces inside the quoted list, for example:
"0.pool.ntp.org,0x8 1.pool.ntp.org,0x8 time.windows.com,0x8"
Confirm outbound UDP port 123 is permitted through any firewall between this server and the chosen sources before continuing.
Expected result: You have a written list of two or more external NTP hostnames, each with the ,0x8 flag, ready to paste into the w32tm command in the next step.
Note
The 0x8 flag means "send request as a client" (SpecialInterval is not set). Using at least two or three peers is recommended so a single unreachable server does not stop synchronization. In high-security or air-gapped environments, use an internal reference clock instead of public pools.
3Configure W32Time with the external NTP peers
Set the manual peer list and synchronization flags on the Windows Time service.
Start menu → right-click Command Prompt → Run as administratorOn the PDC emulator (or standalone server), open an elevated Command Prompt and configure the Windows Time service to use your chosen peers. Run the main command below, substituting your own peer list if you selected different servers in the previous step.
Each parameter does the following:
- /manualpeerlist:"..." - sets the space-separated list of external NTP peers to synchronize with. The
0x8flag requests time in client mode. - /syncfromflags:manual - tells W32Time to sync only from the peers in the manual peer list (rather than from the AD domain hierarchy).
- /reliable:yes - marks this machine as a reliable time source, appropriate for the PDC emulator that the rest of the domain trusts.
- /update - notifies the running time service that its configuration has changed so it re-reads the settings.
w32tm /config /manualpeerlist:"time.windows.com,0x8" /syncfromflags:manual /reliable:yes /updateExpected result: The command returns "The command completed successfully." indicating the new peer list and flags were written to the Windows Time service configuration.
Note
Replace time.windows.com,0x8 with your full multi-peer list (e.g. "0.pool.ntp.org,0x8 1.pool.ntp.org,0x8") for redundancy. On a member server or non-PDC domain controller you would normally leave the default /syncfromflags:domhier (NT5DS) instead, so it keeps syncing from the domain hierarchy. Use /reliable:yes only on the PDC emulator or an authoritative standalone server.
4Restart the Windows Time service
Apply the new configuration by restarting W32Time and confirm it is set to start automatically.
Command Prompt (elevated) → net stop/start, or services.msc → Windows TimeThe /update switch signals the service, but restarting W32Time ensures the new peer list and flags are fully applied. From the same elevated Command Prompt, stop and start the service:
Run net stop w32time followed by net start w32time. On PowerShell you can instead use a single command, Restart-Service w32time.
Also confirm the service is configured to run and start automatically. You can check its state with sc query w32time and its start type in Services (services.msc). The Windows Time service must be running for synchronization to occur.
net stop w32time && net start w32timeExpected result: The service reports "The Windows Time service was stopped successfully." then "The Windows Time service was started successfully." and is running again.
Note
PowerShell equivalent: Restart-Service w32time. On domain controllers the Windows Time service start type is typically managed automatically; if it is disabled, set it with sc config w32time start= auto (note the space after start=).
5Force a resync and verify the configuration
Trigger an immediate synchronization and confirm the source, stratum, and last successful sync time.
Command Prompt (elevated)Force W32Time to synchronize now instead of waiting for its next poll interval, then confirm it is pulling time from your configured NTP peers.
- Run
w32tm /resyncto trigger an immediate synchronization. - Run
w32tm /query /statusto review the current status - check the Stratum, Source, Last Successful Sync Time, and Leap Indicator values. - Run
w32tm /query /sourceto confirm the active time source is one of the external NTP peers you configured (not "Local CMOS Clock" or "Free-running System Clock").
w32tm /resync
w32tm /query /status
w32tm /query /source
Expected result: w32tm /resync reports "The command completed successfully."; /query /status shows a recent Last Successful Sync Time and a low stratum number; and /query /source returns one of your configured NTP servers (e.g. time.windows.com).
Note
If /query /source shows "Local CMOS Clock" or /resync reports "The computer did not resync because no time data was available," synchronization has not succeeded - verify outbound UDP 123 is open, the peer names resolve, and re-run the config. Allow a minute or two after restart before the first successful sync appears. You can also inspect peer detail with w32tm /query /peers.
Confirming Your NTP Configuration Is Working
Confirm configuration
After forcing a resync, the output of w32tm /query /status and w32tm /query /source tells you whether the server is actually pulling time from the peers you configured - not just whether the command ran without error. A successful configuration means the reported Source is one of the external NTP servers from your manual peer list (for example time.windows.com), the Stratum is a low single-digit value (typically 2-4 when syncing from a public source), and the Last Successful Sync Time is recent (within the last poll interval). On the PDC emulator you should also see /query /status report that the server is running with a manual/NTP source rather than the local CMOS clock.
Interpret the values together. A Source of Local CMOS Clock or Free-running System Clock means synchronization is not happening, even if the service is running. A stratum of 0 or an unusually high stratum, or a Last Successful Sync Time that never advances, indicates the peer is unreachable (usually blocked UDP 123) or the peer list was not applied. Members and non-PDC domain controllers should instead report a domain source such as the PDC emulator's hostname - that is the correct, healthy state for those machines.
Normal result: w32tm /query /source returns an external NTP server from your manual peer list (e.g. time.windows.com); w32tm /query /status shows a low stratum (2-4), Leap Indicator 0 (no warning), and a Last Successful Sync Time within the last poll interval.
Abnormal result: /query /source returns Local CMOS Clock or Free-running System Clock, stratum is 0 or missing, or Last Successful Sync Time does not advance - indicating the peers are unreachable (check UDP 123), the config was not applied, or the service did not restart cleanly.
Healthy source output (PDC emulator)
Source: time.windows.com,0x8
w32tm /query /source confirms the server is synchronizing from the configured external NTP peer rather than the local clock.
Healthy status excerpt
Stratum: 3 (secondary reference - syncd by (S)NTP)\nLeap Indicator: 0(no warning)\nLast Successful Sync Time: 3/14/2024 10:42:07 AM
A low stratum, clean leap indicator, and a recent successful sync time indicate accurate, active synchronization.
Failed synchronization
Source: Local CMOS Clock
The server fell back to its hardware clock - the external peers are unreachable or the manual peer list did not take effect.
Correct source on a member/non-PDC machine
Source: PDC01.corp.example.com
Domain members and non-PDC DCs should sync from the domain hierarchy (NT5DS), not directly from an external NTP source.
Troubleshooting
w32tm /resync returns "The computer did not resync because no time data was available."
Warning
Cause: The Windows Time service cannot reach the configured NTP peers, usually because outbound UDP port 123 is blocked by a firewall or the peer names are unreachable.
Confirm outbound UDP 123 is open to your NTP peers, then test reachability with w32tm /stripchart /computer:time.windows.com /samples:5 /dataonly. If the stripchart shows no responses, correct the firewall rule or switch to a reachable peer and re-run w32tm /resync.
w32tm /query /source reports "Local CMOS Clock" instead of the external NTP peers
Warning
Cause: The manual peer list or /syncfromflags:manual setting was not applied, or the service was not restarted after configuration.
Re-run the config command, ensuring /syncfromflags:manual and the correct /manualpeerlist are set, then restart the service with net stop w32time && net start w32time and query the source again with w32tm /query /source.
The Windows Time service will not start or is disabled
Critical
Cause: The W32Time service startup type is set to Manual or Disabled, or the service has stopped after a previous configuration error.
Set the service to start automatically and start it: sc config w32time start= auto followed by net start w32time. Verify with w32tm /query /status that the service is running and reporting a valid source.
Domain members show a large time offset even after the PDC emulator is fixed
Note
Cause: Member machines still hold a stale configuration or were manually pointed at an external source instead of using domain hierarchy (NT5DS).
On affected members reset the client to domain sync with w32tm /config /syncfromflags:domhier /update, then restart the service and run w32tm /resync. They should then report the domain hierarchy as their source.
w32tm /query /status shows a high stratum or "unspecified" reference ID
Note
Cause: The upstream NTP peer is itself unsynchronized or the server has not yet completed a successful sync since the last configuration change.
Wait for a sync cycle and force one with w32tm /resync /rediscover, then re-check w32tm /query /status. If the stratum stays high, choose a lower-stratum, more reliable peer such as pool.ntp.org and reconfigure.
Frequently asked questions
How do I set the NTP server on a Windows Server domain controller?
On the forest root PDC emulator, run w32tm /config /manualpeerlist:"time.windows.com,0x8" /syncfromflags:manual /reliable:yes /update from an elevated prompt, then restart the Windows Time service. Other domain controllers and members should keep syncing from the domain hierarchy rather than an external source.
What does the 0x8 flag mean in the w32tm manual peer list?
The 0x8 flag tells W32Time to send requests in client mode (SNTP/NTP client) rather than symmetric active mode. It is the recommended flag when polling a standard external NTP server such as pool.ntp.org or time.windows.com.
Why should only the PDC emulator sync with an external NTP source?
In an Active Directory forest all machines sync time down the domain hierarchy, and the forest root PDC emulator sits at the top of that hierarchy. Pointing only the PDC emulator at an external source keeps the whole forest on a single consistent, authoritative clock and avoids conflicting time sources.
How can I check which time source my Windows Server is using?
Run w32tm /query /source to see the current time source, and w32tm /query /status for details such as stratum, last successful sync time, and offset. A correctly configured server shows your NTP peers as the source, not "Local CMOS Clock."
What is the difference between NT5DS and NTP in syncfromflags?
NT5DS (used with /syncfromflags:domhier) means the server synchronizes from the Active Directory domain hierarchy, which is the correct setting for domain members and non-PDC domain controllers. NTP (used with /syncfromflags:manual) means the server synchronizes from the manually configured peer list, which is appropriate for the forest root PDC emulator or standalone servers.
How do I fix the Windows Time service when it is not synchronizing?
Confirm the W32Time service is running and set to automatic, verify outbound UDP port 123 is open to your NTP peers, then force a sync with w32tm /resync /rediscover. If it still fails, re-check the peer list and flags with w32tm /query /configuration and correct any invalid source.
Conclusion
You identified the server's place in the Active Directory time hierarchy, selected reliable external NTP sources, configured the Windows Time service with a manual peer list and the correct sync flags, restarted the service, and verified synchronization. With the forest root PDC emulator pointed at trustworthy peers, the rest of the domain inherits accurate time down the hierarchy.
Configure only the forest root PDC emulator (or a standalone server) to sync from external NTP peers, and let the rest of the domain sync from the AD hierarchy.
w32tm /config /manualpeerlist:"time.windows.com,0x8" /syncfromflags:manual /reliable:yes /update