

N-able Patches N-central Auth Bypass Again After CVE-2026-18577 Exploited
A remote monitoring platform used by MSPs let attackers gain admin access, pivot into managed endpoints via Take Control, and hide behind Cloudflare Tunnels, twice, after the first patch missed an alternate exploitation path.

On this page
Key takeaways
- N-able began investigating on July 31, 2026 after unusual licensing errors from on-premises customers.
- CVE-2026-18556 was patched in version 2026.2, but attackers found an alternate bypass path that became CVE-2026-18577.
- Attackers used the Take Control feature to reach managed endpoints and installed persistent Cloudflare Tunnel services.
- CISA added CVE-2026-18577 to its Known Exploited Vulnerabilities catalog on August 4, 2026.
- N-able shipped Hotfix 2 (build 2026.3.1.10) on August 8, 2026, superseding the earlier 2026.3.1.7 fix.
What to do now
High urgency- Upgrade self-hosted N-central to build 2026.3.1.10 (Hotfix 2), not just the earlier 2026.3.1.7 or 2026.3 fix
- Run N-able's custom service template to check Windows endpoints for known indicators of compromise
- Check for svchost.exe in users' Documents folders and a service named Cloudflared on managed endpoints
- Review ui_access_control.log and BASupSrvc_*.log.gz for unauthorized Take Control sessions, including ones tied to MSP Support
- Scan logs for connections from the published attacker IP addresses
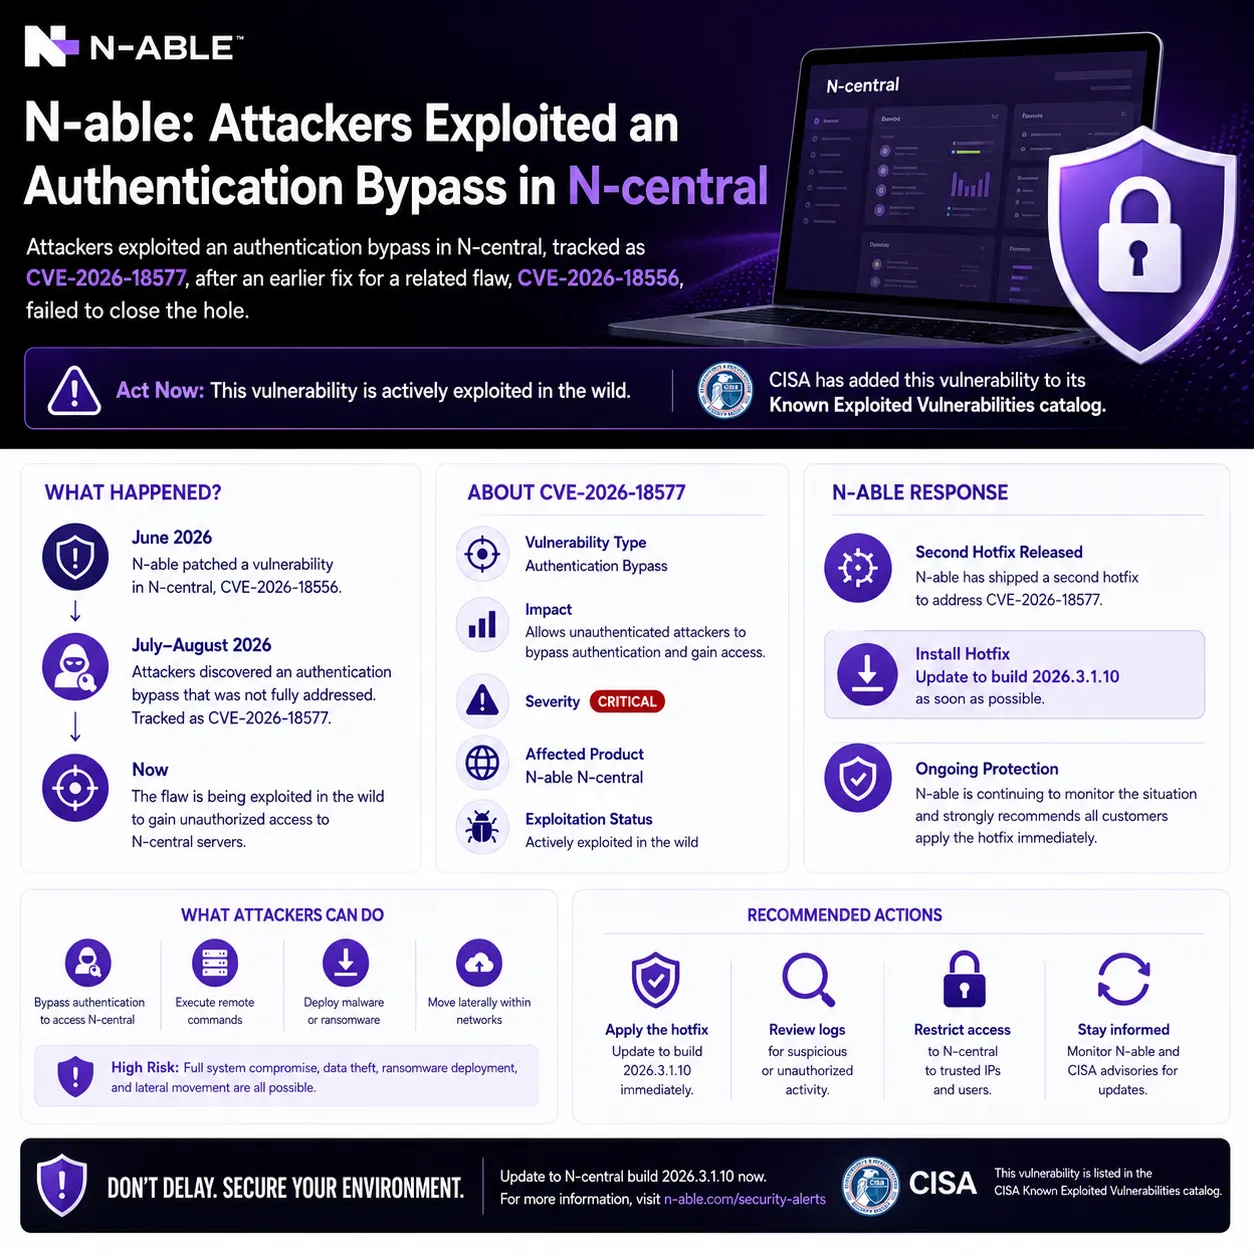
N-able says attackers exploited an authentication bypass in its N-central remote monitoring and management platform, gaining administrative access to servers and reaching customer systems managed through them. The company's first patch, meant to close CVE-2026-18556, was incomplete: attackers found an alternate path that N-able tracked as a new flaw, CVE-2026-18577, and kept exploiting it until a second hotfix shipped on August 8, 2026.
Because N-central manages endpoints for many downstream customers at once, a single compromised server gave attackers a foothold that persisted through Cloudflare Tunnels even after access to the RMM server itself was cut off.
N-able's first patch for an N-central authentication bypass failed to stop attackers, who reached managed endpoints via Take Control and Cloudflare Tunnels before a second hotfix shipped.
Upgrade self-hosted N-central to build 2026.3.1.10, check for Cloudflared services and svchost.exe in Documents folders, and review Take Control session logs for unauthorized MSP Support activity.
Affected & context
N-able confirmed attackers exploited an authentication bypass in its N-central RMM platform starting around July 31, 2026; a first patch for CVE-2026-18556 was bypassed via an alternate path tracked as CVE-2026-18577, prompting a second hotfix and a CISA KEV listing.
N-central is used by managed service providers to administer many customer networks at once, so a single compromised server can give attackers a path into numerous downstream organizations.
On-premises N-central customers running builds prior to 2026.3.1.10, and any managed endpoints reached via Take Control from a compromised server.
- Vendors
- N-ableCloudflare
- Products
- N-centralTake Control
- Geography
- FinlandUnited StatesGlobal
- Industry
- Managed IT ServicesInformation Technology
- CVEs
- CVE-2026-18556CVE-2026-18577
What happened to N-able N-central?
N-able N-central is a remote monitoring and management (RMM) platform that managed service providers and internal IT teams use to administer customer endpoints from a single console. N-able says attackers exploited an authentication bypass in the product to gain remote administrative access to N-central servers, then used that access to reach the customer systems those servers managed.
The investigation started on July 31, 2026, after N-able noticed an unusual volume of licensing errors coming from on-premises customers. That anomaly led the company to discover that unknown attackers had remotely gained administrative access to servers running version 2026.1 and earlier, exploiting what N-able's own CVE record calls an unauthenticated administrative account takeover, CWE-288, an authentication bypass through an alternate path.
Why did the first N-central patch fail?
N-able says it fixed the original flaw, CVE-2026-18556, in version 2026.2. Attackers then found an alternate way to exploit the same underlying weakness that the 2026.2 fix did not block. N-able tracked that gap as a new vulnerability, CVE-2026-18577, expanding the affected range to every N-central build before 2026.3.1.7. Both CVEs carry a CVSS 4.0 score of 8.2, but neither N-able record names the vulnerable endpoint or request sequence, and the company has not published code-level root-cause detail.
N-able's first instruction to customers, upgrading to build 2026.3.1.7 on August 2, 2026, proved insufficient once exploitation continued. On August 8, 2026, N-able shipped Hotfix 2, build 2026.3.1.10, stating it supersedes Hotfix 1 with additional hardening even for customers who had already patched. The company framed the change as a response to attackers evolving their techniques rather than as a fix for a newly found flaw.
How did attackers persist inside managed endpoints?
After compromising an N-central server, attackers used the platform's built-in Take Control feature to reach managed endpoints. On those endpoints, they registered Cloudflare Tunnel as a Windows service, giving them a persistent outbound connection to Cloudflare's edge network that required no inbound firewall rule or open listening port. Running the tunnel as a service let it survive a reboot, and N-able confirmed the tunnels kept working even after the compromised route through the N-central server itself was revoked.
Nothing in the disclosures suggests Cloudflare's infrastructure was itself compromised; the attackers simply abused a legitimate tunneling service the way many intrusions now do, to disguise outbound traffic as ordinary web activity. CISA's advisory adds that attackers conducted reconnaissance against key servers such as domain controllers, enumerated running processes, and in some cases moved laterally to other hosts after gaining initial access.
Who is affected and what does CISA say?
N-able has acknowledged only a limited number of affected customers and has not disclosed how many downstream endpoints were reached, when exploitation began, or who is behind it. Huntress, an MSP-focused security vendor, said in a rapid response that it observed exploitation at a self-hosted N-central instance tied to one partner account, where attackers reached nine downstream organizations, touching one endpoint in each before disconnecting.
- CISA added CVE-2026-18577 to its Known Exploited Vulnerabilities catalog on August 4, 2026, and recommended federal civilian agencies apply fixes by August 6, 2026.
- Finland's national cyber security centre said in an August 2 advisory that all N-central versions available before the emergency hotfix were vulnerable.
- Huntress said it did not observe the Cloudflare tunnel installation activity that N-able described in its original customer notification, suggesting attacker behavior varied by target.
What indicators of compromise should defenders check?
N-able published IP addresses tied to the intrusion, and Huntress traced four of the original addresses to Mullvad and NordVPN exit nodes, meaning IP matching alone will not reliably distinguish an attacker from unrelated VPN traffic. N-able also told customers to check for a file called svchost.exe placed in a user's Documents folder and for a service named Cloudflared registered on endpoints, and to review traffic against the published addresses.
- Correlate ui_access_control.log with C:\ProgramData\GetSupportService_N-Central\Logs\BASupSrvc_*.log.gz on Windows endpoints, as Huntress recommends, since both appear during legitimate Take Control use so their presence alone is not proof of compromise.
- Review sessions tied to apparent N-able support identities, such as mspsupport@n-able.com, for activity the account owner did not initiate.
- CISA and Huntress flagged a malicious connection using the default "MSP Support" username from IP 173.249.252[.]200 in at least one confirmed case.
What should N-central customers do now?
Every N-central customer should be running build 2026.3.1.10; upgrading only to the earlier 2026.3.1.7 is no longer sufficient given the August 8 hotfix. N-able says hosted NCOD instances will be upgraded automatically on a schedule communicated directly to partners, while self-hosted servers must be patched by the customer. N-able has also released a custom service template that automates a check for known indicators of compromise against Windows device endpoints in N-central.
A clean scan is not proof of safety
N-able itself warns that a clean scan result from its IoC-checking template is not a guarantee that an environment was not impacted, since the investigation is ongoing and additional indicators may surface.
Customers who find evidence of compromise must also hunt for and remove malicious tunnel services from managed endpoints directly, because patching N-central does not remove persistence already installed on another machine. N-able has advised anyone who finds these indicators to contact its support team and engage their own security teams for a broader investigation.
Timeline
N-able detects unusual activity
N-able noticed an unusual volume of licensing errors from on-premises customers and began investigating, later finding attackers had gained administrative access to servers running version 2026.1 and earlier.
Source: N-able / The Hacker News
Confidence: High
First hotfix ships as build 2026.3.1.7
N-able released build 2026.3.1.7, its first instruction to customers, alongside disclosure of CVE-2026-18577; Finland's national cyber security centre warned all prior versions were vulnerable.
Source: N-able / Traficom
Confidence: High
Huntress confirms exploitation at a partner account
Huntress published a rapid response confirming exploitation of a self-hosted N-central instance, with attackers reaching one endpoint in each of nine organizations under a single partner account.
Source: Huntress
Confidence: High
CISA adds CVE-2026-18577 to KEV
CISA added CVE-2026-18577 to its Known Exploited Vulnerabilities catalog and recommended federal agencies apply fixes by August 6, 2026.
Source: CISA
Confidence: High
N-able ships Hotfix 2
N-able released Hotfix 2, build 2026.3.1.10, describing additional hardening measures and stating it supersedes the earlier hotfix even for customers who already applied it.
Source: N-able
Confidence: High
Impact
MSPs running vulnerable N-central builds faced administrative takeover of their RMM server and, in some cases, attacker pivoting into managed customer endpoints via Take Control.
Business impact
MSPs must audit both their N-central server and every downstream customer endpoint reachable via Take Control, which multiplies incident-response effort across many client networks at once.
Technical impact
Attackers who gained administrative access used Take Control to reach managed endpoints and registered Cloudflare Tunnel services that survive reboots and persist even after N-central server access is revoked.
Security impact
Two chained authentication bypass flaws (CWE-288) let unauthenticated attackers take over N-central admin accounts; CISA confirmed active exploitation and added CVE-2026-18577 to its KEV catalog.
Affected audience: Managed service providers, IT administrators running self-hosted N-central, Downstream customers of MSPs using N-central for endpoint management
Action required.
Technical details
- CVEs
- CVE-2026-18556, CVE-2026-18577
- CVSS
- 8.2
- Exploitation
- Exploited in the wild
- Attack vector
- Remote, unauthenticated authentication bypass using an alternate path or channel (CWE-288), giving attackers administrative access to N-central servers.
- Affected versions
- N-central through 2026.1 (CVE-2026-18556), N-central prior to 2026.3.1.7 (CVE-2026-18577)
- Patched versions
- 2026.2 (fixed CVE-2026-18556, later found incomplete), 2026.3.1.7 (Hotfix 1), 2026.3.1.10 (Hotfix 2, supersedes Hotfix 1)
- CWEs
- CWE-288
Indicators of compromise
- File
svchost.exe in users' Documents folderMalicious binary placed outside its normal system path on managed endpoints
Source: N-able
Confidence: Medium
- Other
CloudflaredRegistered service name for a Cloudflare Tunnel used to maintain outbound persistence
Source: N-able
Confidence: Medium
- Ip
173.249.252.200IP address seen in N-central exploitation attempts
Source: N-able
Confidence: Medium
- Ip
87.249.138.34NordVPN exit node observed in attack traffic
Source: Huntress
Confidence: Medium
- Ip
37.19.210.32Mullvad VPN exit node previously linked to bruteforcing and spam abuse
Source: Huntress
Confidence: Medium
- Ip
68.235.46.214IP address seen in N-central exploitation attempts
Source: N-able
Confidence: Medium
- Ip
37.153.90.88IP address included in N-able's expanded IoC list
Source: N-able
Confidence: Low
- Ip
92.118.112.181IP address included in N-able's expanded IoC list
Source: N-able
Confidence: Low
- Domain
mousears.synology.meAttacker domain published by Huntress in its rapid response
Source: Huntress
Confidence: Low
- Domain
wagoosh.direct.quickconnect.toAttacker domain published by Huntress in its rapid response
Source: Huntress
Confidence: Low
Detection methods
- Review ui_access_control.log correlated with C:\ProgramData\GetSupportService_N-Central\Logs\BASupSrvc_*.log.gz on Windows endpoints for unauthorized Take Control sessions
- Run N-able's custom service template against Windows endpoints to check for known IoCs
- Scan for a registered service named Cloudflared and for svchost.exe located in a user's Documents folder
Mitigations
- Upgrade self-hosted N-central to build 2026.3.1.10 immediately, since Hotfix 1 (2026.3.1.7) alone is no longer sufficient
- Remove any malicious Cloudflare Tunnel services found on managed endpoints, since patching N-central does not clear persistence installed elsewhere
Technical references
Response
Vendor statement
N-able said, "We are proactively expanding protections in response to ongoing monitoring of threat actors as they evolve their attack techniques," adding that Hotfix 2 is required even for customers who already applied the first hotfix.
Authorities
CISA said N-central "contains an authentication bypass using an alternate path or channel [that] allows for authentication bypass and account takeover," and directed federal civilian agencies to apply the fix by August 6, 2026.
Customer guidance
N-able told customers to upgrade self-hosted N-central to build 2026.3.1.10, run its custom IoC-check service template, and search endpoints for svchost.exe in Documents folders, a Cloudflared service, or traffic from the published attacker IP addresses, contacting support if any indicator is found.
Response status: Mitigated
Patch available: Yes
Workaround available: No
Updates
CISA adds CVE-2026-18577 to KEV catalog
Major updateCISA confirmed active exploitation and ordered federal civilian agencies to patch by August 6, 2026.
N-able ships Hotfix 2 (build 2026.3.1.10)
Major updateN-able said Hotfix 2 supersedes Hotfix 1 with additional hardening and is required even for customers who already applied the first fix.
FAQ
What is CVE-2026-18577?
CVE-2026-18577 is an authentication bypass in N-able N-central, scored 8.2 on CVSS, that resulted from an incomplete fix for the earlier flaw CVE-2026-18556. It affects builds prior to 2026.3.1.7 and lets remote attackers gain administrative access without credentials.
Is CVE-2026-18577 being exploited in the wild?
Yes. N-able confirmed active exploitation starting around July 31, 2026, and CISA added the flaw to its Known Exploited Vulnerabilities catalog on August 4, 2026.
Is upgrading to build 2026.3.1.7 enough?
No. N-able says Hotfix 1 (2026.3.1.7) is superseded by Hotfix 2 (2026.3.1.10), which adds further hardening; customers who already applied Hotfix 1 still need Hotfix 2.
How did attackers persist after N-able revoked server access?
Attackers used the Take Control feature to reach managed endpoints and registered Cloudflare Tunnel services on those devices, which survive reboots and keep working even after the compromised N-central server is cut off.
What should N-central customers check for compromise?
N-able advises checking for svchost.exe in users' Documents folders, a service named Cloudflared, and traffic from its published attacker IP addresses, plus reviewing Take Control logs such as ui_access_control.log for unauthorized MSP Support sessions.
Are hosted N-central customers affected the same way as self-hosted ones?
N-able said hosted NCOD instances are upgraded automatically on a schedule communicated to partners, while self-hosted servers must be upgraded by the customer directly.
The bottom line
A second N-able hotfix, build 2026.3.1.10, was needed after attackers exploited CVE-2026-18577 to bypass the first patch for CVE-2026-18556 and reach managed endpoints via Take Control.
Applying only the first N-central hotfix left MSPs exposed; customers must confirm they are on build 2026.3.1.10 and separately check managed endpoints for Cloudflare Tunnel persistence.
What happens next
N-able says its investigation is ongoing and may surface additional indicators of compromise; affected customers should keep monitoring for updated guidance.
What to do
Upgrade self-hosted N-central to build 2026.3.1.10 and run N-able's IoC service template against managed endpoints now.
Sources
The Hacker News · Aug 3, 2026 · Primary source
Claims supported
- N-able began investigating on July 31, 2026 after unusual licensing errors
- Attackers used Take Control and registered Cloudflare Tunnel services on managed endpoints
- CVE-2026-18577 affects builds prior to 2026.3.1.7, patched August 2, 2026
- Huntress observed exploitation at one self-hosted partner account reaching nine downstream organizations
The Hacker News · Aug 8, 2026 · Primary source
Claims supported
- N-able shipped Hotfix 2, build 2026.3.1.10, superseding Hotfix 1
- N-able vendor statement on expanding protections
- Expanded list of ten indicator IP addresses
The Hacker News · Aug 4, 2026 · Primary source
Claims supported
- CISA added CVE-2026-18577 to its KEV catalog on August 4, 2026
- CISA directed federal civilian agencies to patch by August 6, 2026
- Attackers connected via a default MSP Support username tied to Take Control sessions
- Prior N-central flaws CVE-2025-8875 and CVE-2025-8876 were exploited about a year earlier