

VMware vCenter Flaw CVE-2026-59310 Exploited for Persistent Access
A five-day gap between Broadcom's emergency patch and mass exploitation left hundreds of vCenter appliances backdoored with an open-source reverse shell tool.

On this page
Key takeaways
- CVE-2026-59310 carries a CVSS score of 9.8 and allows unauthenticated remote code execution via directory traversal in vCenter's Syslog server.
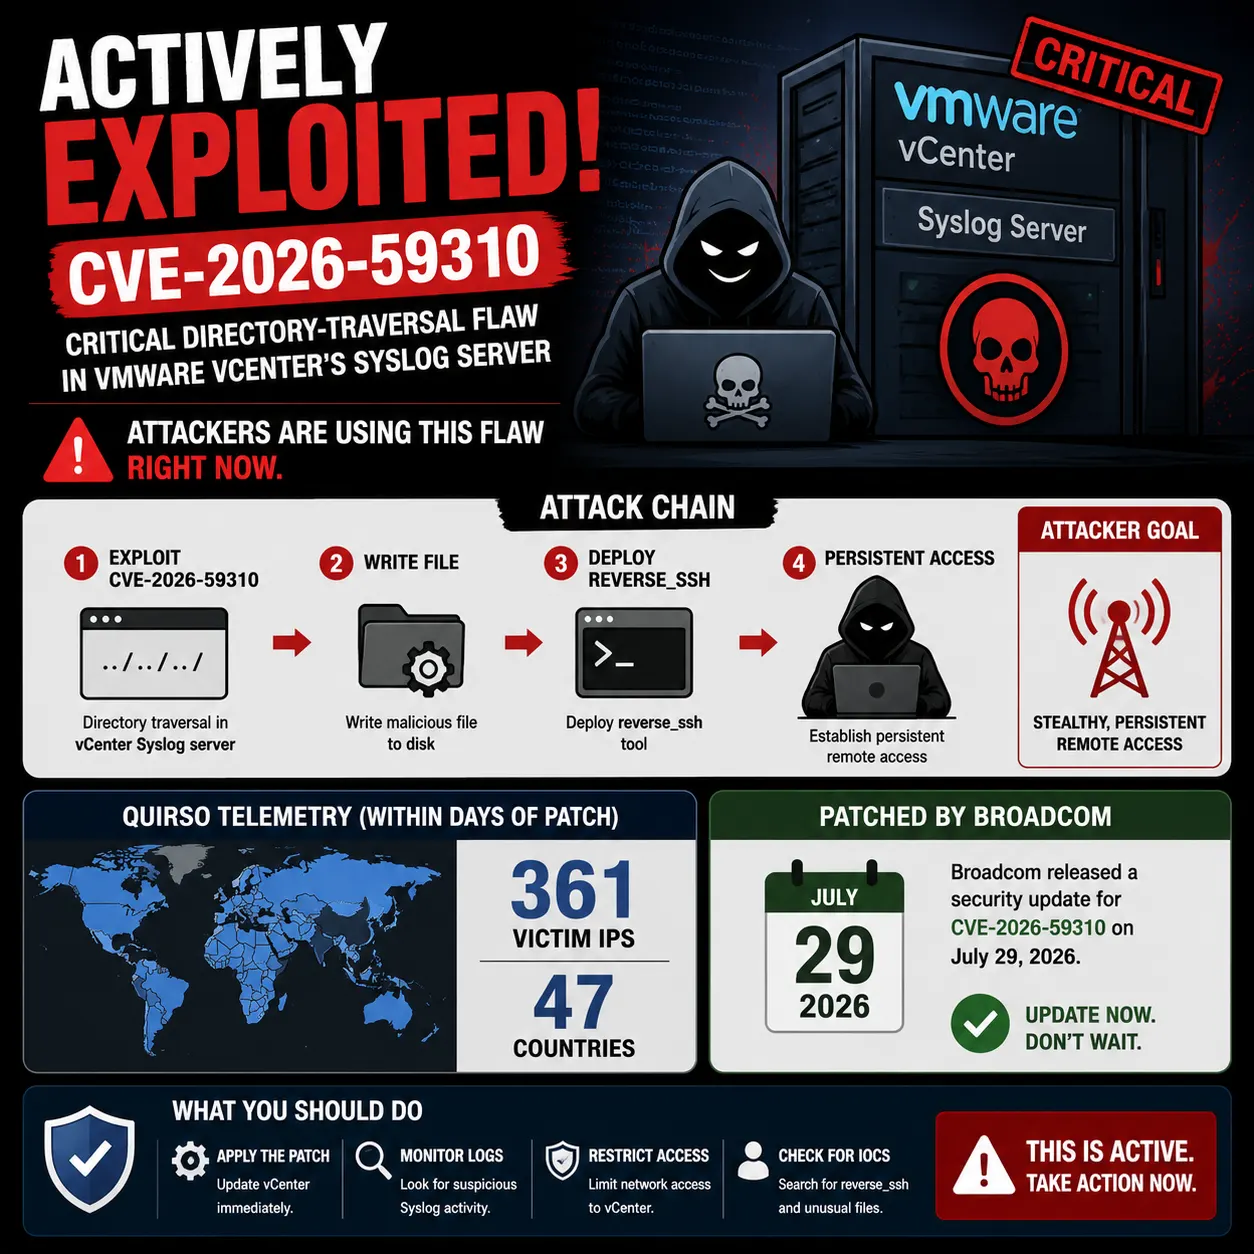
- QUIRSO identified 361 victim IP addresses across 47 countries, with compromises starting five days after Broadcom's patch.
- Attackers deploy reverse_ssh via a malicious cron job to establish outbound C2 channels that bypass inbound firewall rules.
- Broadcom confirmed there are no workarounds; patched builds are vCenter 9.1.0.0300, 9.0.2.0100, 8.0 U3k, or 8.0 U2f.
- A second flaw, CVE-2026-59309, is seeing a separate spike in scanning activity that has not been confirmed as linked exploitation.
What to do now
Immediate urgency- Patch vCenter to 9.1.0.0300, 9.0.2.0100, 8.0 U3k, or 8.0 U2f as specified in VMSA-2026-0006
- Remove vCenter management interfaces from direct internet exposure and require MFA-backed VPN access
- Hunt for reverse_ssh artifacts using QUIRSO's published YARA rule and inspect vCenter binaries and temp directories
- Audit egress network logs for unusual, persistent outbound SSH sessions originating from vCenter IP addresses
Attackers are actively exploiting a critical VMware vCenter vulnerability, CVE-2026-59310, to deploy the open-source reverse_ssh tool and maintain persistent remote access to compromised appliances, according to findings from German incident-response firm QUIRSO.
The directory-traversal flaw sits in vCenter's Syslog server component and lets an attacker with network access execute arbitrary code without authentication, turning the central management plane for VMware virtual infrastructure into an entry point for broader compromise.
Researchers believe, though without disclosed evidence, that a suspected APT actor is exploiting patched VMware vCenter flaw CVE-2026-59310 to backdoor at least 361 systems worldwide with the reverse_ssh persistence tool.
Patch vCenter to the fixed builds immediately, hunt for reverse_ssh artifacts and unusual outbound SSH connections, and treat any unpatched internet- or network-reachable vCenter instance as likely compromised.
Affected & context
QUIRSO found that a suspected APT actor is exploiting CVE-2026-59310, a critical directory-traversal flaw in VMware vCenter's Syslog server, to gain code execution and deploy the reverse_ssh tool for persistent remote access; 361 victim IPs across 47 countries were identified, with compromises beginning five days after Broadcom's July 29 patch.
vCenter is the central control plane for VMware virtual infrastructure, so a successful compromise can give attackers broad access to ESXi hosts, virtual machines, and stored data across an entire virtualized environment.
Organizations running unpatched, internet-exposed or internally reachable VMware vCenter 8.0, 9.0, or 9.1 appliances.
- Vendors
- BroadcomVMware
- Products
- VMware vCenter Server 9.1VMware vCenter Server 9.0VMware vCenter Server 8.0VMware Cloud FoundationVMware vSphere Foundation
- Malware
- reverse_ssh
- Geography
- GermanyUnited StatesTurkeyIranFranceGlobal
- CVEs
- CVE-2026-59310CVE-2026-59309
What happened to VMware vCenter?
CVE-2026-59310 is a directory-traversal vulnerability in the Syslog server component of VMware vCenter, Broadcom's centralized management console for vSphere virtual infrastructure. An attacker with network access to a vulnerable appliance can exploit the flaw without authentication to execute arbitrary code, according to VMSA-2026-0006, published by Broadcom on July 29, 2026. QUIRSO, a German digital forensics and incident response firm, said it uncovered the exploitation while working an incident response engagement and later confirmed a broader pattern across dozens of countries.
After gaining code execution, the attacker installs a malicious cron job on the vCenter host to run reverse_ssh, an open-source Go-based reverse-shell framework, on a recurring schedule. This gives the intruder a durable, self-reestablishing channel back into the environment rather than a one-time foothold.
- CVE-2026-59310 has a CVSS score of 9.8 and requires no authentication to exploit.
- The flaw resides in the vCenter Syslog server component.
Why the timing of this campaign matters
QUIRSO's telemetry shows compromised systems first reaching out to attacker infrastructure just five days after Broadcom's public disclosure and patch release. QUIRSO said this close correlation suggests the disclosure itself, rather than earlier undisclosed knowledge, marked the starting point of the campaign, though it noted the attacker might have had prior awareness of the flaw. The compressed window between patch and mass exploitation leaves defenders with very little margin to apply updates before automated or targeted scanning finds exposed appliances.
Rapid7 had earlier noted that vCenter Server has appeared on CISA's Known Exploited Vulnerabilities list ten times for prior flaws, underscoring that the product is a recurring target for attackers seeking control over virtualized infrastructure.
- Compromises began five days after Broadcom's July 29 patch.
Who is affected, and how widespread is it?
- 361 unique victim IP addresses identified across 47 countries.
- Germany leads with 55 unique IPs, followed by the United States (41), Turkey (38), Iran (26), and France (25).
- 151 new victim IPs appeared in a single day on August 4, and 343 of the 361 total were compromised by August 5.
Affected products include vCenter Server 9.1, 9.0, and 8.0, along with VMware Cloud Foundation and vSphere Foundation deployments that bundle vCenter. Organizations exposing vCenter management interfaces directly to the internet face the highest risk, but QUIRSO and Rapid7 both note that internal network access is sufficient for exploitation, so unsegmented internal networks are also exposed.
- 361 victim IPs across 47 countries were identified by QUIRSO.
How does reverse_ssh give attackers persistent access?
reverse_ssh is a dual-use, open-source tool that initiates outbound SSH connections from the compromised host to infrastructure controlled by the attacker, rather than waiting for inbound connections. Cyber Security News reported that the tool provides automated connect-backs, local and remote port forwarding for lateral movement, and built-in SCP/SFTP support for staging or exfiltrating virtual machine files. Because the connection is outbound and typically uses standard ports, it routinely evades inbound perimeter firewall rules designed to block unsolicited external access.
Presence alone is not proof
QUIRSO cautioned that reverse_ssh's presence should not, by itself, be treated as evidence of malicious activity, since it has legitimate penetration-testing uses. Combined with unauthorized installation, unexpected outbound connections, or execution on a vulnerable vCenter appliance, however, it becomes a high-priority indicator requiring investigation.
- reverse_ssh establishes outbound SSH connections that bypass inbound firewall controls.
What is Broadcom's guidance for admins?
Broadcom confirmed there are no workarounds or temporary mitigations for CVE-2026-59310, making the vendor-supplied patch the only remediation. Fixed releases are vCenter 9.1.0.0300, vCenter 9.0.2.0100, and vCenter 8.0 U3k or 8.0 U2f depending on branch, with a separate async patch path to 8.0 U3k for VMware Cloud Foundation 5.x deployments.
- Apply the patched vCenter build matching your deployed version without delay.
- Remove vCenter management interfaces from direct internet exposure and require VPN access with multi-factor authentication.
- Deploy QUIRSO's published generic YARA rule to scan for reverse_ssh client binaries on vCenter hosts and temporary directories.
- Audit egress logs for unusual, persistent outbound SSH sessions originating from vCenter management IP addresses.
- No workaround exists; patching to 9.1.0.0300, 9.0.2.0100, 8.0 U3k, or 8.0 U2f is the only fix.
Is a second vCenter flaw also under attack?
Separately from the CVE-2026-59310 campaign, threat-hunting group Defused Cyber reported a spike in scanning activity consistent with attempts to identify systems vulnerable to CVE-2026-59309, an unauthenticated authentication-bypass flaw in vCenter's Directory Service (vmdir), also rated CVSS 9.8 under VMSA-2026-0006. Honeypot telemetry showed increased version-fingerprinting probes against the vCenter API and walks of the SAML single sign-on flow.
QUIRSO co-founder Denis Szadkowski told The Hacker News there is not yet enough evidence to link the CVE-2026-59309 scanning with the CVE-2026-59310 intrusion set or infrastructure, but said forensic evidence from the incidents it investigated strongly points to CVE-2026-59310 as the confirmed initial access vector behind the reverse_ssh compromises. QUIRSO said it plans a follow-up report detailing the attacker's infrastructure and post-exploitation techniques.
- CVE-2026-59309 is a separate vmdir authentication-bypass flaw seeing scanning activity not yet confirmed as linked exploitation.
Timeline
Broadcom discloses VMSA-2026-0006
Broadcom publishes security advisory VMSA-2026-0006 covering CVE-2026-59309 and CVE-2026-59310, two critical vCenter flaws rated CVSS 9.8, along with patched builds.
Source: Rapid7
Confidence: High
First compromised systems phone home
QUIRSO observes the earliest compromised vCenter systems contacting attacker-controlled infrastructure, five days after the patch was released.
Source: The Hacker News / QUIRSO
Confidence: High
Exploitation accelerates
151 additional victim IP addresses are observed connecting to attacker infrastructure in a single day.
Source: Cyber Security News
Confidence: Medium
95 percent of victims already compromised
The victim count reaches 343 of the eventual 361 total identified IPs, showing most exploitation happened within 48 hours of the campaign's start.
Source: Cyber Security News
Confidence: Medium
Victim count finalized at 361 IPs
QUIRSO's tracked total reaches 361 unique victim IP addresses across 47 countries.
Source: BleepingComputer
Confidence: High
Findings published publicly
The Hacker News and other outlets publish QUIRSO's findings on the active exploitation campaign.
Source: The Hacker News
Confidence: High
Impact
Unpatched vCenter appliances reachable on a network can be silently backdoored with an outbound SSH channel, giving attackers durable control over an organization's entire virtualized infrastructure.
Business impact
A compromised vCenter appliance can expose ESXi hosts, virtual machines, and stored configuration or credential data across an entire virtualized estate, risking downtime and data theft.
Technical impact
Exploitation of the Syslog server directory-traversal flaw yields arbitrary code execution with system privileges, followed by a malicious cron job that installs reverse_ssh for outbound, firewall-evading command-and-control access.
Security impact
The attack establishes an outbound C2 channel that bypasses inbound perimeter firewall rules and enables port forwarding and file transfer for lateral movement and data staging.
Affected audience: IT admins and sysadmins running VMware vSphere environments, MSPs managing virtualization infrastructure for clients, Security operations and incident response teams
Action required.
Technical details
- CVEs
- CVE-2026-59310, CVE-2026-59309
- CVSS
- 9.8
- Exploitation
- Exploited in the wild
- Attack vector
- Unauthenticated, network-based exploitation of a directory-traversal flaw in the vCenter Syslog server, requiring only network reachability to the appliance and no prior credentials.
- Affected versions
- VMware vCenter 9.1.x, VMware vCenter 9.0.x, VMware vCenter 8.0.x
- Patched versions
- vCenter 9.1.0.0300, vCenter 9.0.2.0100, vCenter 8.0 U3k, vCenter 8.0 U2f
Detection methods
- QUIRSO's published generic YARA rule for detecting reverse_ssh client binaries (also flags legitimate use of the tool)
- Monitoring egress logs for unexpected, persistent outbound SSH connections from vCenter management IPs
Mitigations
- Apply Broadcom's vendor patches for CVE-2026-59310 and CVE-2026-59309 without delay, as no workarounds exist
- Restrict vCenter management interfaces from direct internet exposure and unsegmented internal networks
Technical references
Response
Vendor statement
Broadcom's advisory VMSA-2026-0006, published July 29, 2026, confirms both CVE-2026-59309 and CVE-2026-59310 as critical, unauthenticated, network-exploitable vulnerabilities and states no workarounds or mitigations exist beyond patching.
Customer guidance
Broadcom and researchers urge administrators to apply the emergency patches immediately, restrict vCenter management interfaces from direct internet or unsegmented internal network exposure, and hunt for reverse_ssh indicators on any vCenter appliance that was reachable before patching.
Response status: Patched
Patch available: Yes
Workaround available: No
Updates
QUIRSO discloses active exploitation
Major updateQUIRSO published findings confirming 361 victim IPs across 47 countries and reverse_ssh deployment tied to CVE-2026-59310.
FAQ
What is CVE-2026-59310?
CVE-2026-59310 is a critical (CVSS 9.8) directory-traversal vulnerability in the VMware vCenter Syslog server that lets an unauthenticated attacker with network access execute arbitrary code, per Broadcom's VMSA-2026-0006 advisory.
How many systems have been compromised?
QUIRSO identified 361 unique victim IP addresses across 47 countries, with Germany, the U.S., Turkey, Iran, and France accounting for more than half.
What does reverse_ssh do once installed?
reverse_ssh is an open-source Go-based tool that establishes outbound SSH connect-back sessions, supports port forwarding and file transfer, and bypasses inbound firewall rules that would otherwise block attacker access.
Is there a workaround if I can't patch immediately?
No. Broadcom states there are no workarounds or mitigations for CVE-2026-59310; applying the vendor patch is the only remediation.
Which vCenter versions fix the flaw?
Broadcom's fixed builds are vCenter 9.1.0.0300, vCenter 9.0.2.0100, and vCenter 8.0 U3k or 8.0 U2f depending on the branch, as listed in VMSA-2026-0006.
Is CVE-2026-59309 also being exploited?
Defused Cyber reported a spike in scanning activity against vCenter's vmdir authentication-bypass flaw CVE-2026-59309, but QUIRSO says there is not yet enough evidence to link it to the CVE-2026-59310 intrusion set or infrastructure.
The bottom line
QUIRSO found active exploitation of VMware vCenter flaw CVE-2026-59310 backdooring 361 systems worldwide with reverse_ssh, beginning five days after Broadcom's patch release.
Any vCenter appliance that was network-reachable and unpatched between July 29 and now should be treated as potentially compromised and checked for reverse_ssh artifacts.
What happens next
QUIRSO says it plans a follow-up report detailing the attacker's infrastructure, techniques, and post-exploitation activity, while researchers continue monitoring separate scanning tied to CVE-2026-59309.
Related on Anavem: CISA: SharePoint RCE Flaw CVE-2026-45659 Now Actively Exploited · Max-Severity Adobe ColdFusion Flaw CVE-2026-48282 Now Exploited in Attacks · N-able Patches N-central Auth Bypass Again After CVE-2026-18577 Exploited · CVE-2026-62873: Critical Microsoft 365 Admin Center EoP Flaw Patched · CISA Adds Actively Exploited SharePoint RCE CVE-2026-45659 to KEV Catalog · Microsoft Ships KB5082417 .NET Framework Update Fixing CLR Privilege Escalation .
What to do
Patch vCenter to the fixed builds and hunt for reverse_ssh indicators immediately.
Sources
The Hacker News · Aug 12, 2026 · Primary source
Claims supported
- 361 victim IPs across 47 countries, with compromises beginning five days after Broadcom's patch release
- reverse_ssh deployed via malicious cron job for persistence
- CVE-2026-59309 scanning spike observed by Defused Cyber
Cyber Security News · Aug 12, 2026
Claims supported
- Country-level victim IP breakdown
- reverse_ssh capabilities including port forwarding and firewall evasion
- Recommended defensive measures for admins
BleepingComputer · Aug 12, 2026
Claims supported
- Victim expansion timeline: 151 new IPs on August 4, 343 by August 5
- QUIRSO plans a follow-up report on attacker infrastructure
Rapid7 · Jul 30, 2026 · Primary source
Claims supported
- CVSSv3.1 base scores of 9.8 for both CVE-2026-59309 and CVE-2026-59310
- Fixed version table for vCenter 9.1, 9.0, and 8.0 branches
- vCenter has appeared on CISA's KEV list ten times previously