

CriticalGitLab Community Edition
CISA confirms exploitation of GitLab's CVSS 10 file read flaw CVE-2026-85706
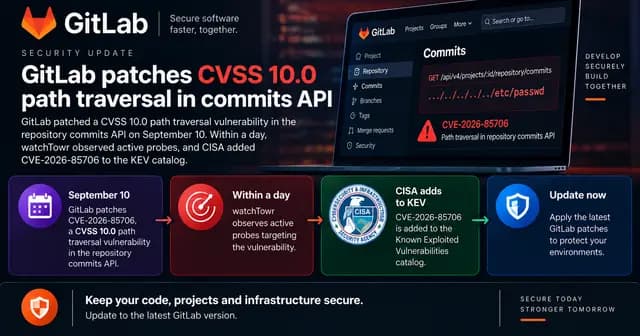
GitLab patched a CVSS 10.0 path traversal bug in the repository commits API on September 10. Within a day, watchTowr saw probes and CISA added CVE-2026-85706 to the KEV catalog.