

14 of 100 stories tagged “Vulnerability”
More 129
SonicWall confirms two SMA1000 zero-days chained in active attacks
SonicWall says attackers are chaining CVE-2026-83548 and CVE-2026-83549 to run code on SMA1000 remote access appliances. A hotfix is out, there's no workaround, and no IoCs have been published yet.
wp2shell: WordPress Core Pre-Auth RCE Fixed in 6.9.5 and 7.0.2
WordPress shipped forced updates 6.9.5 and 7.0.2 on July 17, 2026, closing a pre-auth remote code execution flaw named wp2shell that an anonymous HTTP request can trigger against a default core install with no plugins. The bug affects 6.9.0-6.9.4 and 7.0.0-7.0.1.

Certighost CVE-2026-54121: Public Exploit Turns a Domain User Into a Domain Controller
Researchers H0j3n and Aniq Fakhrul have released a working exploit for Certighost, an Active Directory Certificate Services flaw patched in July 2026 that let any low-privileged domain user impersonate a domain controller and reach full domain compromise.
BeyondTrust Patches Critical Auth Bypass Vulnerability in Remote Support and PRA
BeyondTrust has patched a critical auth bypass vulnerability set in Remote Support (RS) and Privileged Remote Access (PRA). Two of the four flaws are critical pre-authentication bypasses (CVE-2026-40138 and CVE-2026-40139, CVSS 9.2). Under a specific authentication configuration, they let unauthenticated attackers reach affected appliances.
CISA Orders Federal Agencies to Patch Exploited Langflow Auth Bypass by Friday
CISA has added an actively exploited Langflow authorization bypass flaw (CVE-2026-55255) to its Known Exploited Vulnerabilities Catalog, ordering U.S. federal civilian agencies to patch it by Friday under BOD 26-04. The IDOR bug lets authenticated attackers access other users' AI flows and the sensitive data they process.
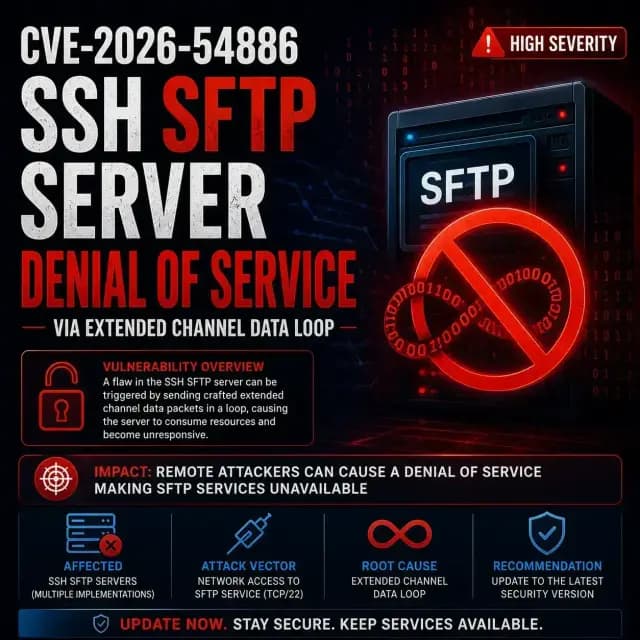
CVE-2026-54886: SSH SFTP Server Denial of Service via Extended Channel Data Loop
A newly disclosed vulnerability, tracked as CVE-2026-54886, can trigger a denial-of-service condition in an affected SSH/SFTP server implementation through an infinite loop in the handling of extended channel data. Administrators should watch for vendor advisories and patch details as they become available.
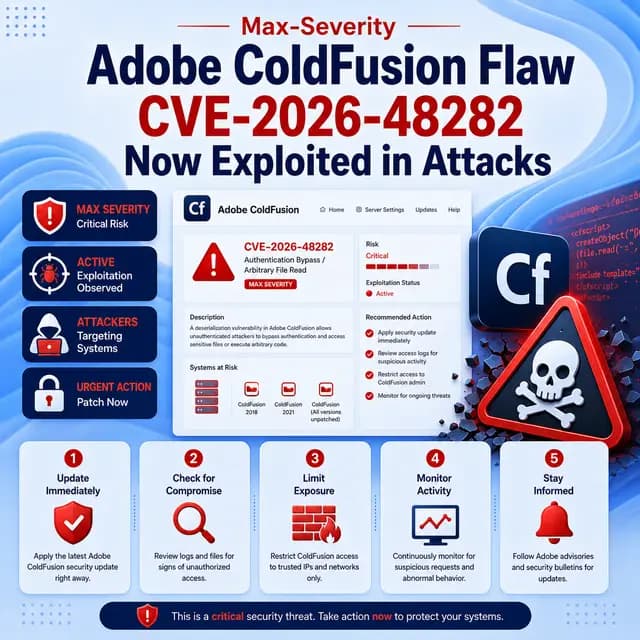
Max-Severity Adobe ColdFusion Flaw CVE-2026-48282 Now Exploited in Attacks
Canada's Cyber Centre warns that attackers are exploiting CVE-2026-48282, a maximum-severity Adobe ColdFusion vulnerability that allows unauthenticated remote code execution. Adobe patched the flaw days earlier and urged admins to update within 72 hours.
CISA Adds Actively Exploited SharePoint RCE CVE-2026-45659 to KEV Catalog
CISA added Microsoft SharePoint Server flaw CVE-2026-45659 (CVSS 8.8) to its Known Exploited Vulnerabilities catalog, citing active exploitation and setting a July 4, 2026 remediation deadline for U.S. federal agencies.
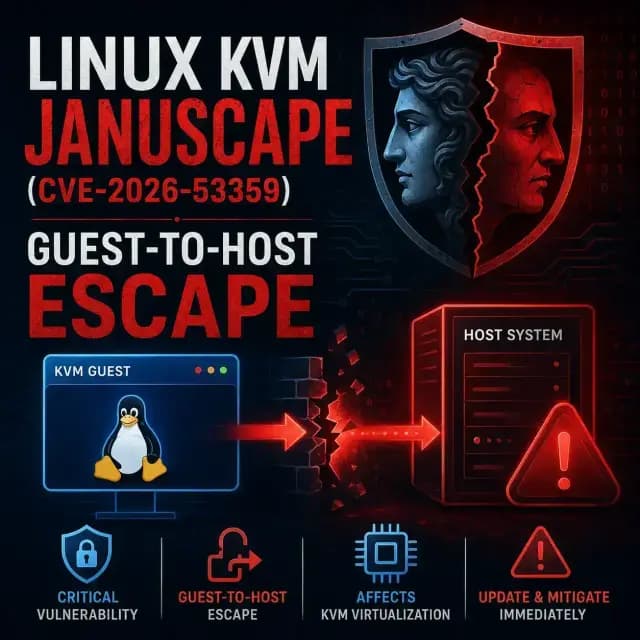
Linux KVM Januscape (CVE-2026-53359): Guest-to-Host Escape
Linux KVM Januscape (CVE-2026-53359) is a use-after-free in KVM's shadow MMU. A guest VM can trigger it to crash or take over its x86 host on both Intel and AMD. This 16-year-old flaw was fixed in mainline on June 19, 2026.

Microsoft Ships KB5094125 to Patch Five Windows Server 2025 Flaws
Microsoft's June 2026 security update KB5094125 patches five vulnerabilities in Windows Server 2025, including a critical unauthenticated Remote Desktop Services RCE (CVE-2026-0235) and a Hyper-V guest-to-host escape (CVE-2026-0237). The update raises the OS build to 26100.32995 and applies to all editions across full GUI and Server Core installations.
Microsoft Ships KB5094122 for Windows Server 2016 and Windows 10 1607, Patching Kernel and CLFS Flaws
Microsoft released KB5094122, the June 2026 cumulative security update for Windows 10 Version 1607 and Windows Server 2016, addressing critical remote code execution and privilege escalation vulnerabilities. The update moves the build to 14393.9234 and fixes flaws in the Windows Kernel, CLFS Driver, Graphics Component and Print Spooler.
Microsoft Ships KB5094128 for Windows Server 2022, Patching Four Critical Flaws
Microsoft's June 2026 security update KB5094128 patches multiple critical vulnerabilities in Windows Server 2022, including an unauthenticated NFS remote code execution flaw (CVE-2026-26001, CVSS 9.8), a Task Scheduler privilege escalation bug, an AD CS authentication bypass, and a Windows kernel memory corruption issue. The update raises the OS build to 20348.5256 and requires a restart.
Microsoft Ships KB5087051 to Patch Four .NET Framework CVEs on Windows 11 25H2
Microsoft's KB5087051 cumulative update for .NET Framework 3.5 and 4.8.1 on Windows 11 Version 25H2 addresses four CVE-tracked vulnerabilities, including remote code execution, an ASP.NET Core authentication bypass, and a serialization denial-of-service flaw, alongside WCF stability and Entity Framework performance fixes.
Microsoft Ships KB5087545, Fixing Five Critical Windows Server 2022 Flaws
Microsoft released KB5087545 for Windows Server 2022 on May 12, 2026, patching five critical vulnerabilities including an unauthenticated RDP remote code execution flaw (CVE-2026-0145, CVSS 9.8) and a Hyper-V guest-to-host escape. The cumulative update raises the OS build to 20348.5139 and carries several known post-install issues.